Audit operations inside containers
Audit commands that organization members or applications run inside containers to detect threats before they escalate.kubectl exec or shell access to detect threats before they escalate.
Enable the feature, view audit reports and logs, configure alerts, and disable the feature when no longer needed.
This is a whitelist feature. Submit a ticket to enable access before proceeding.
Billing
The feature itself is free. After enablement, Simple Log Service (SLS) usage fees apply. For pricing details, see Billing overview.
Limitations
Cluster types: ACK managed Pro cluster, ACK managed Basic cluster, and ACK dedicated cluster.
Operating system and kernel: Alibaba Cloud Linux, Ubuntu, or ContainerOS with a kernel version later than 4.19.
OS | Minimum cluster version | Additional requirements |
Alibaba Cloud Linux | 1.18 | — |
ContainerOS | 1.24 | — |
Ubuntu | 1.30 (see Manually upgrade a cluster) | Automatic OS upgrades must be disabled during node initialization. The |
Step 1: Enable the feature
Enabling the feature installs two add-ons:
Log collection add-on — collects audit logs, sends them to SLS, and creates a default audit report. See Log collection component.
ack-advanced-audit add-on — audits operations within containers.
A Logstore named advaudit-${cluster_id} is created in the log collection project. Audit logs are retained for 180 days by default. To adjust the retention period, see Manage a Logstore.
To enable the feature:
Log in to the ACK console and click Clusters in the left navigation pane.
Click the name of your cluster. In the left navigation pane, choose Security > Audit.
On the Audit page, click the Container Audit tab and then click Install.
Step 2: View audit reports
On the Audit page, click the Container Audit tab and then click the Container Audit Overview tab.
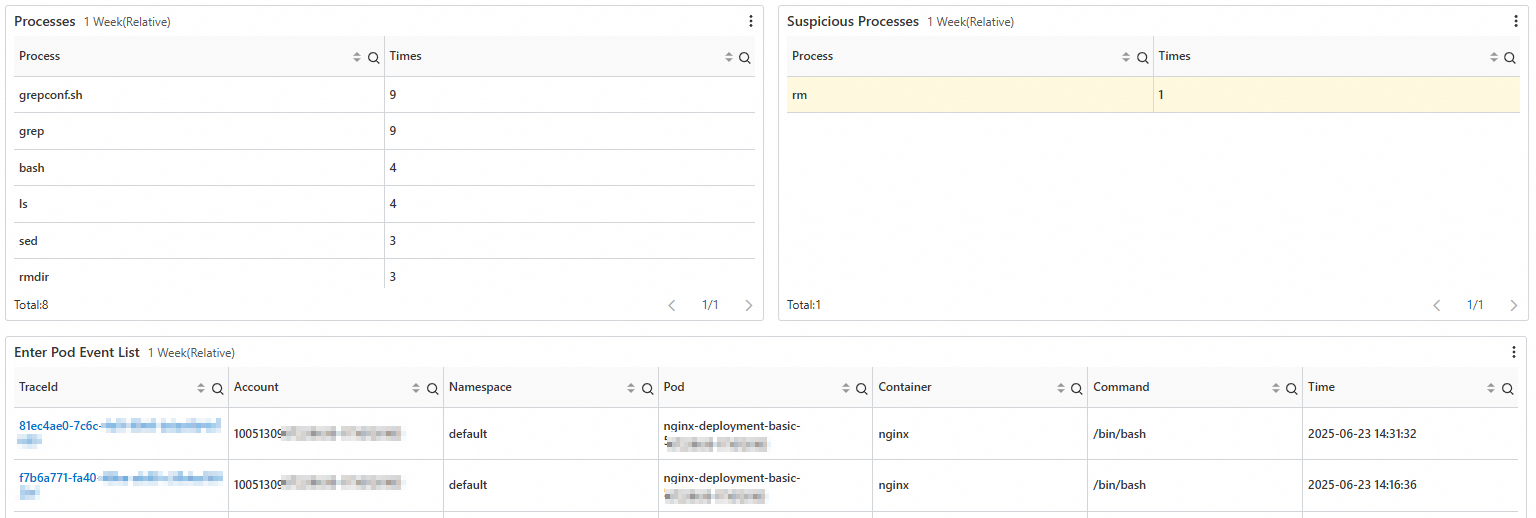
The overview report shows:
Pod access frequency and pod details.
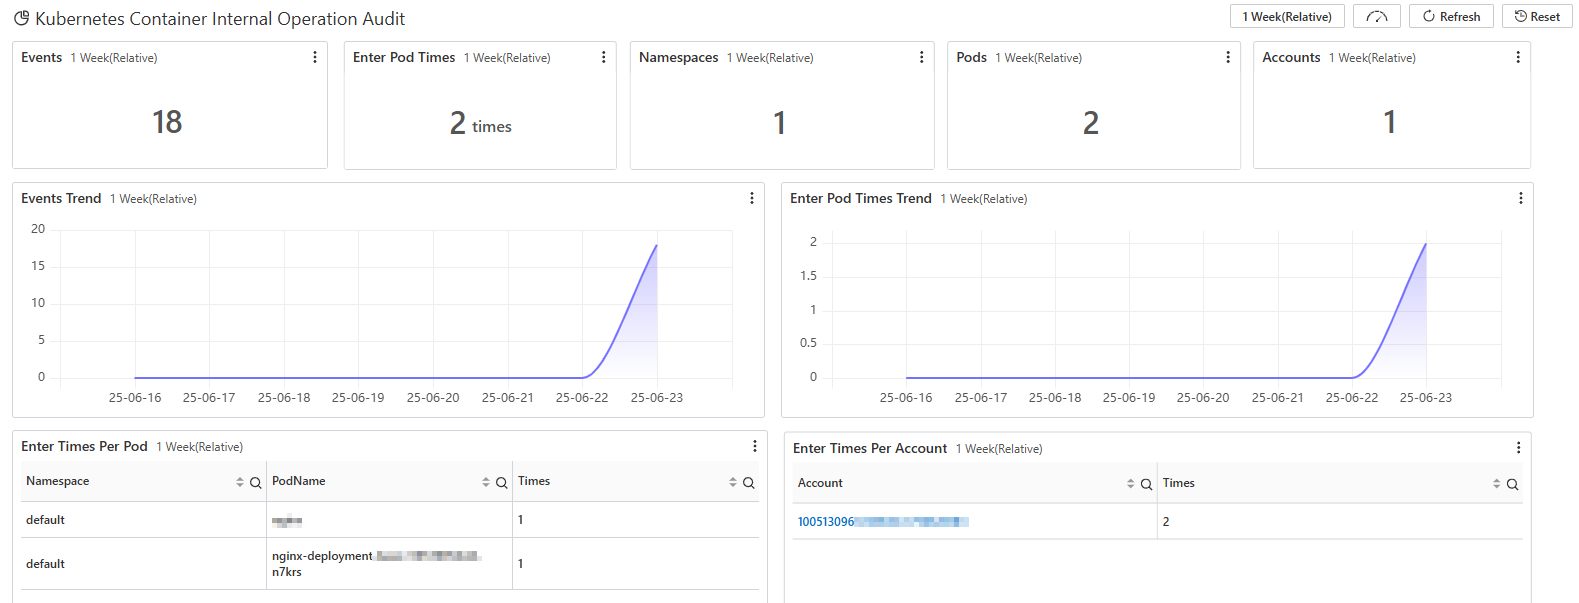
Kubernetes accounts, commands run after access, and common threats.
Step 3: View detailed log records
Two methods are available depending on your goal:
Method | Best for |
Audit report page | Quickly reviewing a recent individual event |
Logstore page with search statements | Historical queries and complex filters |
View logs from the audit report page
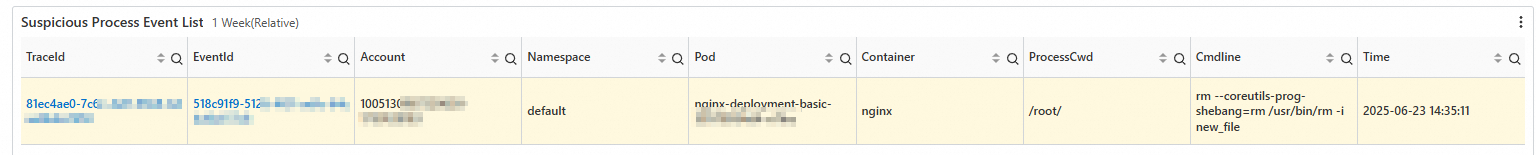
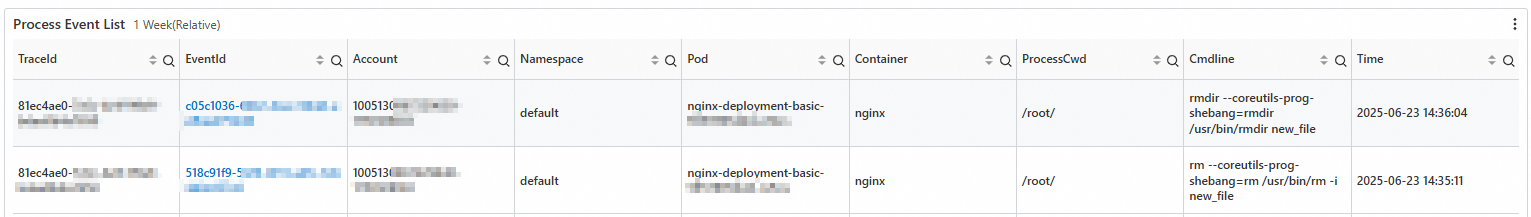
On the Container Audit Overview tab, scroll to the Suspicious Process Event List section. Click a link in the traceId or eventId column:
traceId — shows all commands run after a container was accessed.
eventId — shows the details of one specific command.
View logs from the Logstore page
Log in to the ACK console and click Clusters in the left navigation pane.
Click your cluster name. In the left navigation pane, choose Security > Audit.
On the Audit page, click the Container Audit tab and then click the Query Container Audit Logs tab.
Enter a search statement in the search box. Query by pod — replace
<namespace>and<pod_name>with actual values:Category
Field
Description
Pod
k8s.pod.namespaceNamespace of the pod
Pod
k8s.pod.nameName of the pod
Process
process.nameName of the process that was executed
* and k8s.pod.namespace: <namespace> and k8s.pod.name: <pod_name>Query by process name — replace
<name>with the program name:* and process.name: <name>The table above lists key query fields. For all supported methods, see Log search and analysis.
Set a time range and click Search & Analyze.
(Optional) Step 4: Configure alerts
Use the SLS alerting feature to monitor container operations in real time. Supported alert channels include SMS messages, DingTalk chatbot, emails, custom webhooks, and the notification center.
This topic uses DingTalk alerts as an example to describe how to configure container internal operation audit alerts. For other alert configuration methods, see Alerting.
Log on to the Simple Log Service console.
Go to the Webhook Integration page.
In the Projects section, click the project you want.
In the left-side navigation pane, click Alerts.
On the Alert Center page, click the Notification Objects tab and then click Webhook Integration.
Create a webhook.
On the Webhook Integration page, click Create.
In the Create Webhook dialog box, configure the following parameters and click OK.
Parameter
Description
ID
The webhook ID. Must be unique. This example uses ack-container-operation-audit-alert.
Name
The name of the webhook. This example uses Kubernetes intra-container operation audit alert.
Type
The webhook type. This example selects DingTalk.
Request URL
The webhook URL.
Create a custom chatbot in DingTalk and obtain its webhook URL. See Custom robot access.
Create an alert template.
On the Alert Center page, click the Notification Management tab and then click Alert Template.
On the Alert Template page, click Create.
Configure the ID and name for the alert template. Then, configure the title and content for the DingTalk alert notification.
See Create an alert template. Configure two templates as follows.
ID
Name
Title
Content
ack-container-operation-audit-alert-enter
Kubernetes container access alert
Kubernetes intra-container operation audit alert
- Alert Rule: ${alert_name}
- Trigger Time: ${alert_time}
- Severity: ${severity}
- Cluster ID: {{ alert.results[0].fire_result['clusterid'] }}

An account accessed a container by using kubectl exec or the terminal feature. Check for any abnormal activities.
Number of operations: {{ alert.fire_results_count }}. The following provides details about one of the operations:

- Operation Time: {{ alert.results[0].fire_result['time'] }}
{% if alert.results[0].fire_result['k8s.user.aliuid'] -%}
- Account: {{ alert.results[0].fire_result['k8s.user.aliuid'] }}
{% else -%}
- Account: {{ alert.results[0].fire_result['k8s.user.username'] }}
{% endif -%}
- Namespace: {{ alert.results[0].fire_result['k8s.pod.namespace'] }}
- Pod: {{ alert.results[0].fire_result['k8s.pod.name'] }}
- Container: {{ alert.results[0].fire_result['kubeobject.operation.podexecoptions.container'] }}
- Command: {{ alert.results[0].fire_result['kubeobject.operation.podexecoptions.commandstr'] }}

[[Details](${query_url})]
[[Settings](${alert_url})]
ack-container-operation-audit-alert-run-danger-cmd
Kubernetes alert for running risky programs after container access
Kubernetes intra-container operation audit alert
- Alert Rule: ${alert_name}
- Trigger Time: ${alert_time}
- Severity: ${severity}
- Cluster ID: {{ alert.results[0].fire_result['clusterid'] }}

An account ran a risky program after accessing a container by using kubectl exec or the terminal feature. Check for any abnormal activities.
Number of operations: {{ alert.fire_results_count }}. The following provides details about one of the operations:

- Operation Time: {{ alert.results[0].fire_result['time'] }}
{% if alert.results[0].fire_result['k8s.user.aliuid'] -%}
- Account: {{ alert.results[0].fire_result['k8s.user.aliuid'] }}
{% else -%}
- Account: {{ alert.results[0].fire_result['k8s.user.username'] }}
{% endif -%}
- Namespace: {{ alert.results[0].fire_result['k8s.pod.namespace'] }}
- Pod: {{ alert.results[0].fire_result['k8s.pod.name'] }}
- Container: {{ alert.results[0].fire_result['k8s.container.name'] }}
- Working Directory: {{ alert.results[0].fire_result['process.cwd'] }}
- Command: {{ alert.results[0].fire_result['process.cmdline'] }}

[[Details](${query_url})]
[[Settings](${alert_url})]
Configure alerts.
Log on to the Simple Log Service console.
In the project list, find the project that the cluster uses (k8s-log-${cluster_id}) and click the project name.
In the left-side navigation pane, click the
 icon, select Dashboards, and then click Kubernetes Container Internal Operation Audit.
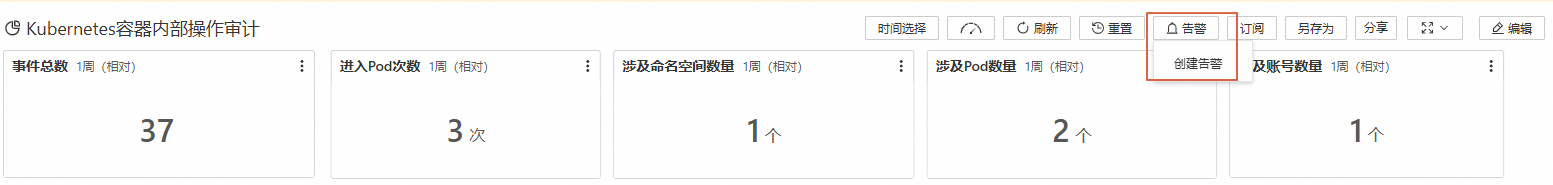
On the Kubernetes Container Internal Operation Audit report page, choose .

On the Alert Monitoring Rule page, configure the alert rules for
Kubernetes container access alertandKubernetes alert for running risky programs after container access, and then click OK.The following values are for reference. Adjust based on your requirements.
Kubernetes container access alertParameter
Description
Rule Name
Kubernetes container access alertCheck Frequency
Fixed Interval: 1 minute.
Query Statistics
Click Add, open the Advanced Settings tab, configure the parameters, and click OK.
Logstore: Search for and select
advaudit-${cluster_id}, for example,advaudit-c76da730c08ca45adb90fad86fb******.Query Time Range: Select 1 Minute (Relative).
Search: Displayed after you specify the Logstore. Enter the following query:
kind: Kubernetes and kubeObject.operation.kind: PodExec | select "clusterid", "time", "traceId", "eventId", "k8s.user.aliuid", "k8s.user.username", json_extract(k8s, '$.user.groups') as "k8s.user.groups", "host.hostip", "host.nodename", "k8s.pod.namespace", "k8s.pod.name", json_extract(k8s, '$.pod.labels') as "k8s.pod.labels", "kubeobject.operation.podexecoptions.container", json_extract(kubeobject, '$.operation.podExecOptions.command') as "kubeobject.operation.podexecoptions.command", "kubeobject.operation.podexecoptions.commandstr" from log
Trigger Condition
Select Data is returned. Then, set Severity to Report.
Destination
Select Simple Log Service Notification.
Enable
Turn on the switch.
Alert Policy
Select Simple Mode and configure the following parameters.
Notification Method: Select DingTalk.
Select Webhook: Select
Kubernetes intra-container operation audit alert.Notified Contacts: Select No Reminder.
Alert Template: Search for and select
Kubernetes container access alert.Period: Select Any Time.
Kubernetes alert for running risky programs after container accessParameter
Description
Rule Name
Kubernetes alert for running risky programs after container accessCheck Frequency
Fixed Interval: 1 minute.
Query Statistics
Click Add, open the Advanced Settings tab, configure the parameters, and click OK.
Logstore: Search for and select
advaudit-${cluster_id}, for example,advaudit-c76da730c08ca45adb90fad86fb74****.Query Time Range: Select 1 Minute (Relative).
Search: Displayed after you specify the Logstore. Enter the following query:
kind: Command | select "clusterid", "time", "traceId", "eventId", "k8s.user.aliuid", "k8s.user.username", json_extract(k8s, '$.user.groups') as "k8s.user.groups", "host.hostip", "host.nodename", "k8s.pod.namespace", "k8s.pod.name", json_extract(k8s, '$.pod.labels') as "k8s.pod.labels", "k8s.container.name", "k8s.container.image", "process.cwd", "process.name", "process.cmdline", json_extract(process, '$.pid') as "process.pid", "process.user.uid", json_extract(process, '$.parentPid') as "process.parentpid", "process.parentname" from log where "process.name" in ('rm', 'sudo', 'su', 'nsenter', 'curl', 'wget', 'yum', 'apt-get', 'apt', 'apk', 'dpkg', 'nc', 'ncat', 'ssh', 'scp', 'nmap', 'docker', 'crictl', 'nerdctl', 'podman', 'kubectl', 'helm', 'mysql', 'redis', 'psql', 'redis-cli', 'pip', 'npm', 'gem')
Trigger Condition
When Data is returned, set Severity to medium.
Destination
Select Simple Log Service Notification.
Enable
Turn on the switch.
Alert Policy
Select Simple Mode and configure the following parameters.
Notification Method: Select DingTalk.
Select Webhook: Select
Kubernetes intra-container operation audit alert.Notified Contacts: Select No Reminder.
Alert Template: Select
Kubernetes alert for running risky programs after container access.Period: Select Any Time.
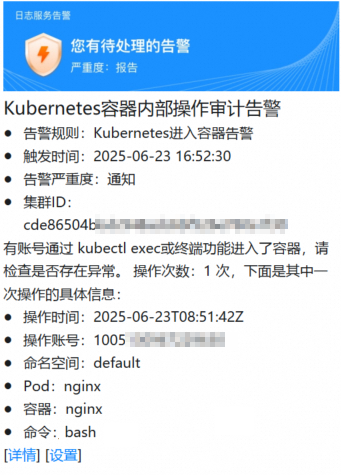
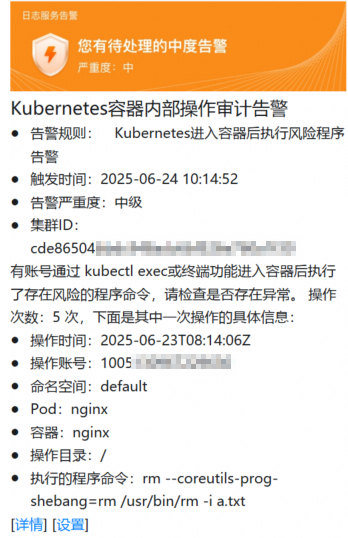
Test the alert rules.
Run
kubectl exec -it <pod_name> -- bashto enter a container. This triggers theKubernetes container access alertrule.In the container, run
touch a.txt && rm a.txt. This triggers theKubernetes alert for running risky programs after container accessrule.
Disable the feature
Uninstalling the ack-advanced-audit add-on disables the feature.
Disabling the feature does not delete the advaudit-${cluster_id} Logstore. If you leave it in place, SLS storage charges continue to accrue. To stop billing, log in to the SLS console and manually delete the Logstore. See Stop billing for or delete a Logstore.
To uninstall the add-on:
Log in to the ACK console and click Clusters in the left navigation pane.
Click your cluster name. In the left navigation pane, click Add-ons.
On the Add-ons page, find ack-advanced-audit and click Uninstall.
Next steps
See ack-advanced-audit for release notes and details.
To audit API Server operations (who did what to which resource and when), see Use the cluster API Server audit feature.