Configure local rate limiting for an ingress gateway
During high-traffic events such as flash sales, sudden traffic spikes can overwhelm your system, causing request backlogs and service failures. ASM provides a local rate limiting feature to control traffic at the ingress gateway and protect your backend services. This topic shows you how to configure this feature.
Prerequisites
-
You have an ASM instance that meets the following requirements:
-
ASM Enterprise Edition or Ultimate Edition: version 1.11.5.30 or later. For more information about how to upgrade an ASM instance, see Upgrade an ASM instance.
-
ASM Standard Edition: version 1.9 or later. This edition supports local rate limiting only through the native Istio method. For different Istio versions, refer to the corresponding version's documentation. For the latest Istio version, see Enabling Rate Limits using Envoy.
-
An ingress gateway is deployed. For more information, see Create an ingress gateway.
-
You have created the bookinfo and nginx services. In this topic, the bookinfo service is deployed in the default namespace, and the nginx service is deployed in the foo namespace. For more information about how to create the bookinfo service, see Deploy an application in a cluster associated with an ASM instance.
-
You have created a gateway and a virtual service. For more information, see Manage gateways and Manage virtual services.
-
You have installed a load testing tool. For more information, see hey.
Applicability
The local rate limiting feature in ASM applies to ASM gateways and application services with an injected sidecar.
Use cases
This topic uses the bookinfo and nginx services to demonstrate how to use rate limiting for gateways and services. The nginx service is deployed in the foo namespace to verify the scope of rate limiting.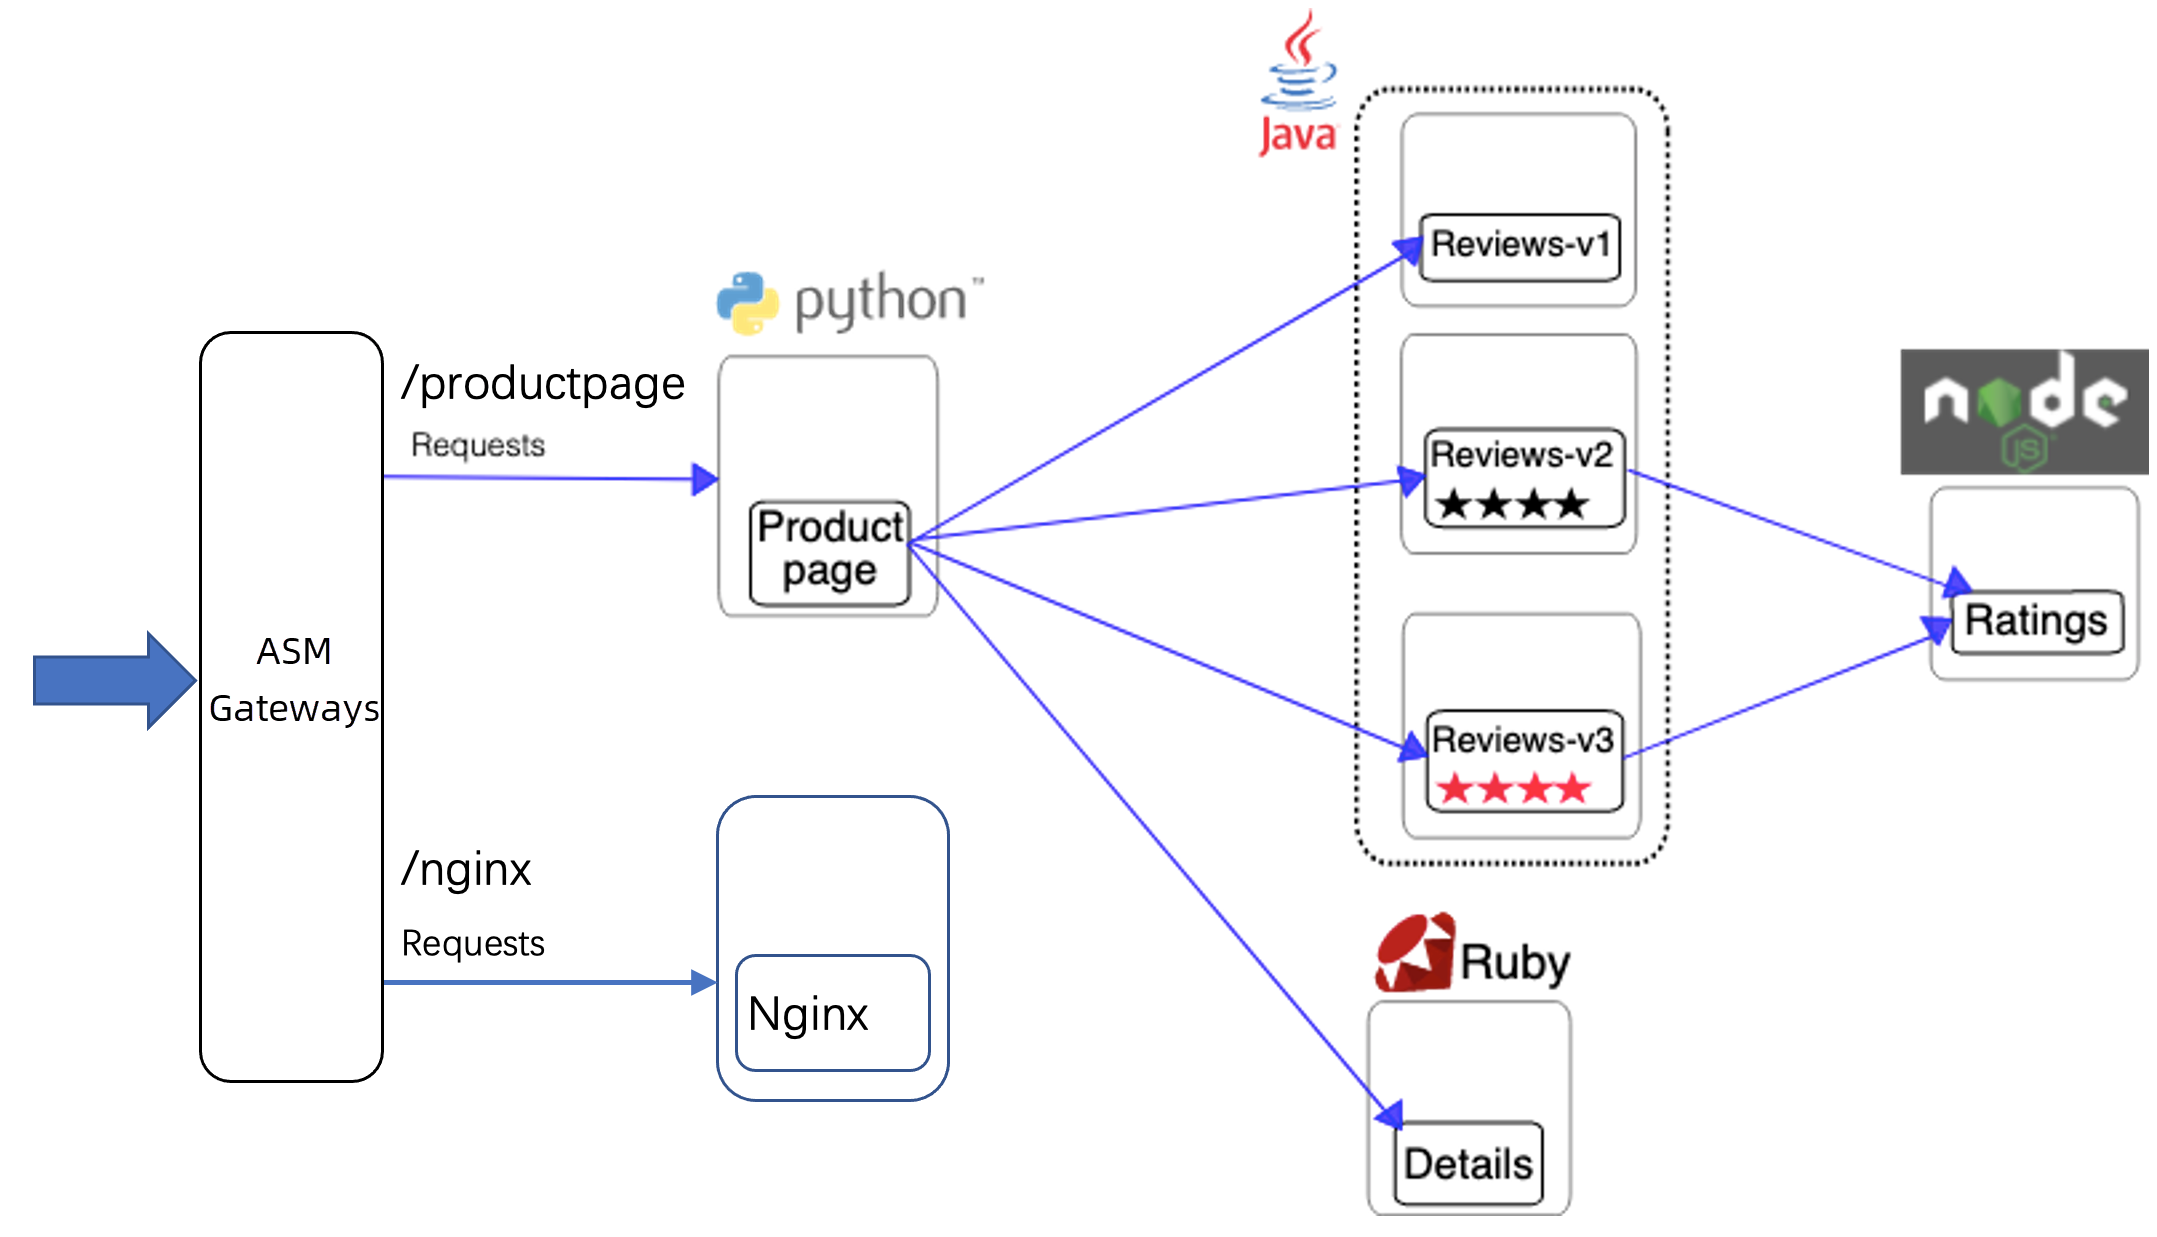
Scenario 1: Rate limit a virtual service route
Configure a rate limiting rule for the productpage-route-name1 route on the bf2.example.com:80 domain and port combination. productpage-route-name1 is a route in the bookinfo virtual service created in the Prerequisites section. It matches requests for paths like /productpage, /static, /login, and /logout, and forwards them to the productpage service. After you configure the rate limiting rule, it limits the traffic rate for requests to these paths.
-
Create a local rate limiting rule.
-
Log on to the ASM console. In the left-side navigation pane, choose .
-
On the Mesh Management page, click the name of the ASM instance. In the left-side navigation pane, choose . On the page that appears, click Create.
-
On the Create page, configure the parameters as described below and click OK.
For more information about the parameters, see ASMLocalRateLimiter CRD reference.
Section
Parameter
Description
Basic Information About Throttling
Namespaces
The namespace for the local rate limiting rule. This must be the same namespace as the rate-limited workload. In this example, you must select istio-system because all ASM gateways are deployed in the istio-system namespace.
Name
A custom name for the local rate limiting configuration. This example uses ingressgateway.
Type of Effective Workload
The type of workload to which rate limiting applies. Supported values are Applicable Service and Applicable Gateway. This example uses Applicable Gateway.
Relevant Workload
If you select Applicable Gateway, you must also select a Select Istio Gateway. The rule applies to the workload associated with the selected gateway. This example uses bookinfo-gateway.
List of Throttling Rules
Gateway Domain Name
Select a domain declared in the gateway. The rate limiting rule takes effect for the specified port and domain combination. This example uses bf2.example.com.
Gateway Port
Select a port declared in the gateway. The rate limiting rule takes effect for the specified port and domain combination. This example uses 80.
Match Routes of Virtual Service
Select a route declared in the virtual service that is associated with the gateway. The rate limiting rule takes effect for the specified virtual service route. This example uses productpage-route-name1.
Throttling Configuration
Specify the detection window and the number of allowed requests for the local rate limiting token bucket algorithm. Requests that exceed the limit within the detection window are throttled. In this example, use the following configurations:
-
Set Time Window for Throttling Detection to 1s.
-
Set Number of Requests Allowed in Time Window to 10.
These settings limit requests to the service workload to 10 per second.
advanced config
Click Show Advanced Settings to specify advanced behaviors for when rate limiting occurs. You can configure the advanced settings as required. In this example, set Custom Throttling Response Body to
{"ret_code": xxx,"message": "Your request be limited"}.The following code shows the YAML file for the local rate limiting configuration.
-
If you do not configure advanced settings, the system returns the default response when rate limiting is triggered.
-
If you configure advanced settings, the system returns a custom response when rate limiting is triggered.
-
-
-
Run the following commands in the hey tool to continuously generate stress traffic.
hey -host bf2.example.com -c 10 -n 100000 http://${ASM_GATEWAY_IP}/productpagehey -host bf2.example.com -c 10 -n 100000 http://${ASM_GATEWAY_IP}/nginx -
Run the following command to access the /productpage path of the gateway.
curl -H 'host: bf2.example.com' http://${ASM_GATEWAY_IP}/productpage -vExpected output:
< HTTP/1.1 429 Too Many Requests
< Content-Length: 18
< Content-Type: text/plain
< Date: Thu, 13 Jan 2022 03:03:09 GMT
< Server: istio-envoy
<
local_rate_limited
The output indicates that access to the bookinfo service is limited.
-
Run the following command to access the /nginx path of the gateway.
curl -H 'host: bf2.example.com' http://${ASM_GATEWAY_IP}/nginx -vThe response does not include a 429 status code, which indicates that access is not limited.
Scenario 2: Rate limit a gateway domain and port
Configure a rate limiting rule for the bf2.example.com:80 domain and port combination to limit traffic to all paths on that combination.
-
Configure a rate limiting rule.
-
Log on to the ASM console. In the left-side navigation pane, choose .
-
On the Mesh Management page, click the name of the ASM instance. In the left-side navigation pane, choose . On the page that appears, click Create.
-
On the Create page, configure the parameters as described below and click OK.
For more information about the parameters, see ASMLocalRateLimiter CRD reference.
Section
Parameter
Description
Basic Information About Throttling
Namespaces
The namespace for the local rate limiting rule. This must be the same namespace as the rate-limited workload. In this example, you must select istio-system because all ASM gateways are deployed in the istio-system namespace.
Name
A custom name for the local rate limiting configuration. This example uses ingressgateway.
Type of Effective Workload
The type of workload to which rate limiting applies. Supported values are Applicable Service and Applicable Gateway. This example uses Applicable Gateway.
Relevant Workload
If you select Applicable Gateway, you must also select a Select Istio Gateway. The rule applies to the workload associated with the selected gateway. This example uses bookinfo-gateway.
List of Throttling Rules
Gateway Domain Name
Select a domain declared in the gateway. The rate limiting rule takes effect for the specified port and domain combination. This example uses bf2.example.com.
Gateway Port
Select a port declared in the gateway. The rate limiting rule takes effect for the specified port and domain combination. This example uses 80.
Match Routes of Virtual Service
Do not select a route in this example. This applies the rate limiting rule to all routes for the specified domain and port.
Throttling Configuration
Specify the detection window and the number of allowed requests for the local rate limiting token bucket algorithm. Requests that exceed the limit within the detection window are throttled. In this example, use the following configurations:
-
Set Time Window for Throttling Detection to 1s.
-
Set Number of Requests Allowed in Time Window to 10.
These settings limit requests to the service workload to 10 per second.
The following code shows the YAML file for the local rate limiting configuration.
-
-
-
Run the following command in the hey tool to continuously generate stress traffic.
hey -host bf2.example.com -c 10 -n 100000 http://${ASM_GATEWAY_IP}/nginx -
Run the following command to access the /nginx path of the gateway.
curl -H 'host: bf2.example.com' http://${ASM_GATEWAY_IP}/nginx -vThe response returns
HTTP/1.1 429 Too Many Requests, which indicates that access to the /nginx path on the gateway is limited.
Scenario 3: Rate limit by request header
Configure a rate limiting rule for the nginx-route-name1 route on the bf2.example.com:80 domain and port combination. You can specify that the rate limiting rule takes effect only for requests with the ratelimit: "true" request header. This rule does not affect other requests to the route. nginx-route-name1 is a route in the bookinfo virtual service created in the Prerequisites section. It matches requests for the /nginx path and forwards them to the nginx service.
-
Configure a rate limiting rule.
-
Log on to the ASM console. In the left-side navigation pane, choose .
-
On the Mesh Management page, click the name of the ASM instance. In the left-side navigation pane, choose . On the page that appears, click Create.
-
On the Create page, configure the parameters as described below and click OK.
For more information about the parameters, see ASMLocalRateLimiter CRD reference.
Section
Parameter
Description
Basic Information About Throttling
Namespaces
The namespace for the local rate limiting rule. This must be the same namespace as the rate-limited workload. In this example, you must select istio-system because all ASM gateways are deployed in the istio-system namespace.
Name
A custom name for the local rate limiting configuration. This example uses ingressgateway.
Type of Effective Workload
The type of workload to which rate limiting applies. Supported values are Applicable Service and Applicable Gateway. This example uses Applicable Gateway.
Relevant Workload
If you select Applicable Gateway, you must also select a Select Istio Gateway. The rule applies to the workload associated with the selected gateway. This example uses bookinfo-gateway.
List of Throttling Rules
Gateway Domain Name
Select a domain declared in the gateway. The rate limiting rule takes effect for the specified port and domain combination. This example uses bf2.example.com.
Gateway Port
Select a port declared in the gateway. The rate limiting rule takes effect for the specified port and domain combination. This example uses 80.
Match Routes of Virtual Service
Select a route declared in the virtual service that is associated with the gateway. The rate limiting rule takes effect for the specified virtual service route. This example uses nginx-route-name1.
Match Request Attributes
Specify a request matching condition to trigger the rate limiting rule. In this example, use the following configurations:
-
Set Matched Attributes to Specific Request Header.
-
Set Request Header to ratelimit.
-
Set Matching Method to Exact Match.
-
Set Matched Content to true.
Throttling Configuration
Specify the detection window and the number of allowed requests for the local rate limiting token bucket algorithm. Requests that exceed the limit within the detection window are throttled. In this example, use the following configurations:
-
Set Time Window for Throttling Detection to 1s.
-
Set Number of Requests Allowed in Time Window to 10.
These settings limit requests to the service workload to 10 per second.
The following code shows the YAML file for the local rate limiting configuration.
-
-
-
Run the following command in the hey tool to continuously generate stress traffic. The requests all carry the
ratelimit: truerequest header to trigger rate limiting.hey -host bf2.example.com -H 'ratelimit: true' -c 10 -n 10000 http://${ASM_GATEWAY_IP}/nginx -
Run the following command to access the
/nginxpath of the gateway.curl -H 'host: bf2.example.com' -H 'ratelimit: true' http://${ASM_GATEWAY_IP}/nginx -vThe response returns
HTTP/1.1 429 Too Many Requests, which indicates that requests to the/nginxpath of the gateway with theratelimit: truerequest header are limited. -
Run the following command to access the
/nginxpath of the gateway, but without theratelimit: truerequest header.curl -H 'host: bf2.example.com' http://${ASM_GATEWAY_IP}/nginx -vThe response does not include a 429 status code, which indicates that requests without the
ratelimit: truerequest header are not limited.
Related operations
Delete the rate limiting rule
-
Delete the rate limiting rule.
-
Log on to the ASM console. In the left-side navigation pane, choose .
-
On the Mesh Management page, click the name of the ASM instance. In the left-side navigation pane, choose .
-
On the Rate Limiting page, find the target rate limiting rule, click Delete in the Actions column, and then click OK in the Submit dialog box.
-
-
Run the following command to access the
/nginxpath of the gateway.curl -H 'host: bf2.example.com' http://${ASM_GATEWAY_IP}/nginx -vThe response does not include a 429 status code, which indicates that access is not limited.