Features
This topic describes the features of different Bastionhost editions and compares them.
Feature list
Edition | Document |
Bastionhost (Basic, Enterprise Dual-Engine, and SM-compliant editions) | |
Bastionhost (Developer and Lightweight editions) |
Scenarios
Edition | Scenario | |
Bastionhost (Basic, Enterprise Dual-Engine, and SM-compliant editions) | Basic Edition | Designed for small and medium-sized enterprises (SMEs) with 50 to 500 hybrid assets that need a professional O&M experience. It offers granular controls, such as client-based O&M, detailed user access and behavior authorization, automatic blocking of risky commands, and approval for high-risk commands. You can also monitor and interrupt O&M sessions in real time. It supports user management with Resource Access Management (RAM), Active Directory (AD), or self-managed Lightweight Directory Access Protocol (LDAP) users. This edition covers the basic O&M security needs for SMEs. |
Enterprise Dual-Engine Edition | Designed for enterprises with high O&M security requirements or large-scale operations, such as those in government, finance, gaming, online education, and information technology. The Enterprise Dual-Engine Edition includes all features of the Basic Edition but with better performance and configurations to meet advanced security needs. Its advantages include the following:
| |
SM-compliant Edition | Builds on the O&M control capabilities of the enterprise-grade Bastionhost. It uses Chinese cryptographic algorithms to encrypt critical data, meeting advanced information security and compliance requirements. | |
Bastionhost (Developer and Lightweight editions) | Developer Edition | Designed for individual developers or micro-enterprises that are fully on the cloud with 5 to 20 Elastic Compute Service (ECS) or Kubernetes (K8s) assets. It provides basic capabilities, such as unified O&M for administrators, access authorization control for O&M users, and full video recording for O&M auditing. It also offers a deeper cloud experience with lightweight deployment, seamless connectivity across multiple Virtual Private Clouds (VPCs), and automatic detection of asset accounts. |
Lightweight Edition | Designed for small, cloud-native enterprises with 5 to 20 ECS or K8s assets. In addition to the basic O&M capabilities of the Developer Edition, this edition adds more enterprise-level O&M and control features. These features include file transfer and auditing, administrator control over user commands, and automatic blocking of high-risk commands to ensure security. It also offers higher performance and specifications, such as 365-day log storage. | |
Feature comparison
In the following table, 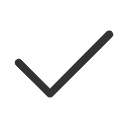 indicates that the feature is supported, and
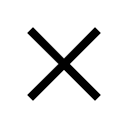 indicates that the feature is not supported.
Feature | Description | Free Edition | Developer Edition | Lightweight Edition | Basic Edition | Enterprise Dual-Engine Edition | SM-compliant Edition |
Architecture | Uses a stable architecture to ensure stable business operations and monitoring. | Software as a Service (SaaS) | SaaS | SaaS | Cloud-based single-engine architecture | Cloud-based dual-engine architecture | Cloud-based dual-engine architecture |
Cross-domain O&M | Manage assets across multiple VPCs in different regions from a unified console. |
| Supports one-click private network connection | Supports one-click private network connection | Supports self-managed network mode | Supports self-managed network mode and network domain proxy mode | Supports self-managed network mode and network domain proxy mode |
Privileged access management | Divides system accounts into privileged and standard accounts. Supports quick authorization and management by category. |
|
|
|
|
|
|
Elastic scaling | Supports elastic scaling of asset specifications, storage, and bandwidth. |
|
|
|
|
|
|
Chinese cryptographic algorithm | Supports encryption using Chinese cryptographic algorithms. |
|
|
|
|
|
|
Internationalization | Supports multiple languages. You can switch between Simplified Chinese, Traditional Chinese, and English in real time. |
|
|
|
|
|
|
Can be deployed outside China. Compatible with two-factor authentication using various international mobile numbers. |
|
|
|
|
|
| |
Multiple accounts | Supports unified O&M for assets across multiple accounts in a resource directory. |
|
|
|
|
|
|
User management | Supports multiple user roles, such as administrator, O&M engineer, and auditor. |
|
|
|
|
|
|
Supports automatic synchronization of RAM users and self-managed local users. |
|
|
|
|
|
| |
Supports integration with third-party identity sources such as AD/LDAP users. |
|
|
|
|
|
| |
Supports integration with IDaaS users. You can sync users from various identity sources, such as DingTalk and Azure AD, to Bastionhost. |
|
|
|
|
|
| |
Asset management | Supports O&M for Windows and Linux systems. |
|
|
|
|
|
|
Supports O&M for the following databases: RDS for MySQL, SQL Server, and PostgreSQL; PolarDB for MySQL, PostgreSQL, and PostgreSQL (Oracle-compatible); and self-managed databases of MySQL, SQL Server, PostgreSQL, and Oracle types. |
|
|
|
|
|
| |
Supports O&M for web applications and client applications. Common O&M protocols include HTTPS and HTTP. |
|
|
|
|
|
| |
Supports manual creation and one-click import of assets from Alibaba Cloud and third-party clouds. | Elastic Compute Service | Elastic Compute Service | Elastic Compute Service |
|
|
| |
Supports hosting of asset credentials (passwords/keys). O&M engineers can access assets without knowing the passwords. |
|
|
|
|
|
| |
Supports unified O&M for hybrid environments, including multicloud, cloud, and on-premises IDC servers. |
|
|
|
|
|
| |
Integrates with Security Center to monitor asset risks. It provides timely alerts on threats, vulnerabilities, and baseline risks, and lets you quickly navigate to Security Center to resolve them. |
|
|
|
|
|
| |
Asset password change | Supports manual or scheduled password changes for Linux and Windows servers. |
|
|
|
|
|
|
Supports integration with KMS for password and key rotation of ECS instances. |
|
|
|
|
|
| |
O&M control | Supports granular one-to-one authorization from users to asset accounts. |
|
|
|
|
|
|
Supports two-factor authentication using text messages, email, mobile TOTP tokens, and DingTalk. |
| DingTalk not supported | DingTalk not supported |
|
|
| |
Supports logging on to Bastionhost to access hosts using clients such as Mstsc, Xshell, SecureCRT, and PuTTY. |
|
|
|
|
| Single sign-on mode | |
Supports logging on to Bastionhost for file transfer using SFTP clients such as WinSCP, Xftp, and SecureFX. |
|
|
|
|
| Single sign-on mode | |
You can log on to ECS Workbench to perform O&M on ECS instances. |
|
|
|
|
|
| |
Supports single sign-on (SSO) for asset O&M in Browser/Server (B/S) mode. |
|
|
|
|
|
| |
Supports a separate O&M portal. |
|
|
|
|
|
| |
Supports asset access through a web page. |
|
|
|
|
|
| |
Supports creating O&M tasks to run scripts in batches on host accounts. |
|
|
|
|
|
| |
Supports real-time monitoring of ongoing sessions and lets you interrupt them at any time. |
| Supports real-time monitoring | Supports real-time monitoring |
|
|
| |
Supports control over operations such as clipboard uploads/downloads and disk mapping during Remote Desktop Protocol (RDP) O&M. |
|
|
|
|
|
| |
Supports setting command blacklists, whitelists, blocking, and approval policies to control the execution of high-risk and sensitive commands during Secure Shell (SSH) O&M. |
|
| Supports command blocking |
|
|
| |
Supports control over file operations (upload, download, delete, rename) and folder operations (create, delete) during O&M. |
|
|
|
|
|
| |
Supports enabling secondary approval for O&M. O&M engineers can access assets only after an administrator grants approval. |
|
|
|
|
|
| |
Supports restricting user and asset logons to Bastionhost based on source IP addresses and logon time windows. |
|
|
|
|
|
| |
Supports setting limits on idle time and total duration for O&M sessions. |
|
|
|
|
|
| |
Log auditing | Supports full logging and video recording of O&M operations for auditing. You can use the recordings to clearly review and trace the O&M process. |
|
|
|
|
|
|
Supports auditing of file transfers. |
|
|
|
|
|
| |
Supports generating O&M reports. Reports can be exported in PDF, HTML, and Word formats. |
|
|
|
|
|
| |
Supports storing session audit logs in Simple Log Service (SLS). |
|
|
|
|
|
| |
API | Supports OpenAPI calls. |
|
|
|
|
|
|