High bill risk warning
Malicious attacks or traffic theft can cause sudden spikes in bandwidth or traffic, leading to unexpectedly high bills. You are responsible for any resulting charges. This topic explains how to mitigate these risks and control your costs.
Potential risk: High bills from malicious access
-
During an attack, CDN bandwidth resources are consumed. Therefore, you are responsible for the resulting traffic and bandwidth fees.
-
A sudden increase in your bandwidth caused by malicious traffic consumption is similar to an attack. Because this activity consumes the bandwidth resources of CDN or , you are responsible for the resulting traffic and bandwidth fees.
Associated risk: Bills may exceed your account balance
Malicious attacks or traffic theft can easily lead to high bills, which often exceed your account balance.
CDN and are pay-as-you-go services. Bill amounts are affected by factors such as the billing cycle (for example, hourly, daily, or monthly) and bill processing delays. For Alibaba Cloud CDN and , bills are generated with a 3- to 4-hour delay. Therefore, services cannot be immediately suspended when your account balance reaches zero. This may result in an overdue amount, or the overdue amount of a single bill may exceed your service suspension credit limit.
Alibaba Cloud offers a service suspension protection feature. If you enable this service and your account has an overdue payment, Alibaba Cloud provides a credit or grace period based on factors such as your customer level and spending history. This allows you to continue using cloud services for a limited time. The credit limit is automatically calculated and updated each month. For more information, see Overdue payments and service suspension.
-
For new users, service suspension protection is disabled by default. The following shows the process for overdue payments and service suspension when the feature is disabled:
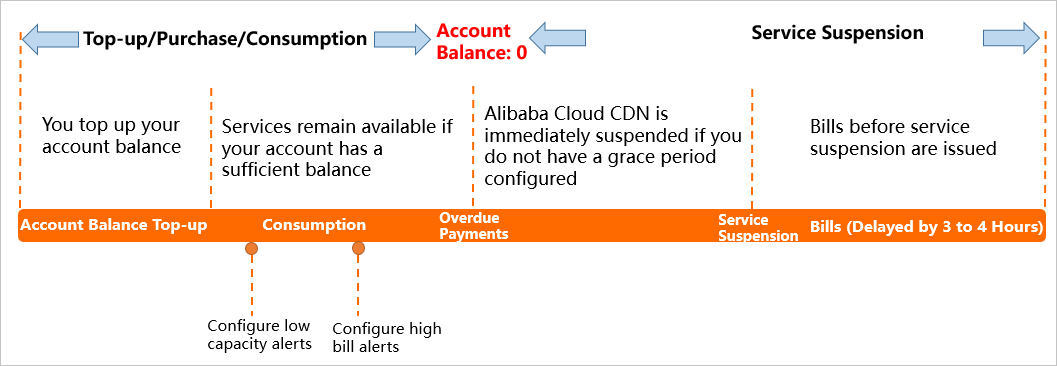
Example: Customer A uses the pay-by-traffic (billed hourly) CDN service, has disabled service suspension protection, and has an account balance of CNY 1,000. Between 15:00 and 16:00 on February 1, the customer's traffic spikes. Around 19:00 on February 1, the hourly bill for the 15:00–16:00 period is generated with an amount of CNY 5,000. After settlement, the account has an overdue balance of CNY 4,000. The CDN service is then suspended. However, bills for the 16:00–17:00, 17:00–18:00, and 18:00–19:00 periods will still be generated. The final overdue amount is likely to be greater than CNY 4,000.
-
You can manually enable service suspension protection. The following shows the process for overdue payments and service suspension when the feature is enabled:
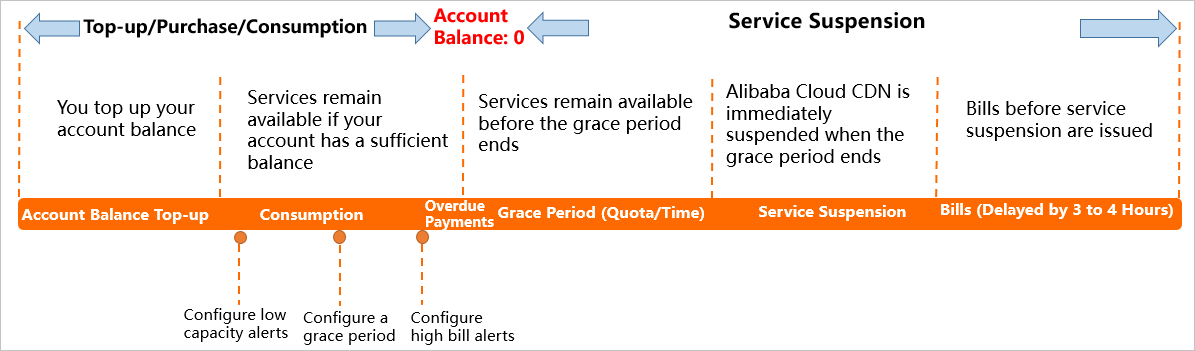
Example: If Customer A from the previous example has enabled service suspension protection with a credit limit of CNY 500. When the bill for the 15:00–16:00 period is generated around 19:00 on February 1, the CDN service will still be suspended because the overdue amount (CNY 4,000) is greater than the service suspension protection limit (CNY 500).
Mitigation strategies
-
Alibaba Cloud CDN products do not provide access control or security protection capabilities by default. Alibaba Cloud CDN detects sudden increases in customer bandwidth. If abnormal traffic is detected, Alibaba Cloud evaluates whether to apply measures such as traffic throttling or sandboxing to the traffic spike based on the customer's normal business traffic volume and the overall load of the abnormal traffic to ensure network stability for all users. (Traffic throttling or sandboxing is not always triggered. For more information, see "Burst bandwidth/QPS throttling rules" in Usage limits.) Alibaba Cloud is not responsible for any availability issues that result from these measures.
-
To ensure the stable operation of your services and avoid high bills, we recommend that you enable the protection features and access control configurations described in this topic.
Enable access control
If you experience a sudden spike in traffic, first analyze your real-time logs to determine the cause. For information, see Configure real-time log delivery for CDN and for DCDN. Based on your findings, configure the appropriate access control features in the console to prevent unnecessary traffic and bandwidth consumption.
|
Access control feature |
Description |
|
Configure a referer blacklist or whitelist |
This feature prevents hotlinking by allowing or blocking requests based on their Referer header. You can configure a whitelist to allow only requests from matching referers or a blacklist to block them. For configuration instructions, see Configure a referer blacklist or whitelist for CDN and for DCDN. |
|
Configure URL signing |
The URL signing feature provides a secure and reliable way to prevent resource hotlinking by coordinating Alibaba Cloud CDN POPs with your origin server. You can refer to Configure URL signing to configure rules that meet your business requirements. |
|
Configure remote authentication |
The remote authentication feature forwards user requests to your specified authentication server through Alibaba Cloud CDN / points of presence (POPs). The authentication server then validates the requests to strictly prevent unauthorized users from accessing your resources. You can configure rules that are specific to your business needs by following the instructions in Configure remote authentication. |
|
Configure an IP address blacklist or whitelist |
After a malicious attack or traffic spike, analyze your real-time logs, which are configured via , to identify IP addresses with high access frequency. If you identify malicious IP addresses, you can use the IP address blacklist or whitelist feature to block them. For more information, see Configure an IP address blacklist or whitelist for CDN and for DCDN. |
|
Configure a User-Agent blacklist or whitelist |
After a malicious attack or traffic spike, analyze your real-time logs, configured via , to check if the malicious activity originates from specific User-Agents. If you identify a malicious User-Agent, you can use the User-Agent blacklist or whitelist feature to block these requests. For more information, see Configure a User-Agent blacklist or whitelist for CDN and for DCDN. |
Enable traffic management
Use CloudMonitor to set product-level or domain-level bandwidth monitoring rules to track your traffic and bandwidth usage and receive alerts for anomalies. For more information, see Configure alert rules. If you experience unexpected bandwidth spikes, you can also configure policies like bandwidth throttling and traffic throttling for your domain.
|
Traffic management feature |
Description |
|
Set bandwidth cap |
If you want to limit the maximum bandwidth for a domain name, you can use the Bandwidth Cap feature. After the configured bandwidth threshold is reached, CDN stops providing acceleration services for the domain name and resolves it to an invalid address to help you avoid high bills. For more information, see Bandwidth Cap. |
|
Set traffic throttling for individual requests |
The traffic throttling for individual requests feature limits the downstream speed at which CDN POPs serve content to users. This feature is often used to manage traffic during promotional events, such as a new game release, by controlling the peak bandwidth of the accelerated domain across the entire network. For more information, see Configure traffic throttling for individual requests. |
|
Set bandwidth throttling |
If you need to limit the bandwidth for a domain name that uses Alibaba Cloud CDN/, and your daily peak bandwidth is greater than 10 Gbps, you can fill in your information to request a backend configuration. Important
|
|
Set up real-time monitoring |
If you want to monitor the peak bandwidth of a domain name in real time, you can use the Cloud Product Monitoring feature of CloudMonitor to set up monitoring for the peak bandwidth of a specified domain name for CDN or . When the configured peak bandwidth is reached, an alert (SMS, email, or DingTalk) is sent to the administrator, which helps you detect potential risks in a more timely manner. For more information, see the CloudMonitor product details page. |
|
Set up spending and cost alerts |
In the top navigation bar of the console, choose Expenses > Expenses and Costs. Configure the following features to better control your account spending and avoid high bills.
Note
To ensure the completeness of metering data and the accuracy of bills, CDN and products require approximately 3 hours after a billing cycle ends to generate a final bill. Therefore, there is a delay between the resource consumption time and the actual payment deduction, and bills cannot provide real-time feedback on resource usage. This is determined by the distributed nature of CDN and points of presence (POPs). All CDN and service providers use a similar method. |
Enable protection features
If the access control and traffic management features do not meet your security needs, we recommend that you activate Edge Security Acceleration (ESA). ESA provides comprehensive security capabilities, including native DDoS protection and a native web application firewall (WAF). It uses Alibaba Cloud's proprietary machine learning algorithms to detect threats in every request, offering end-to-end protection for your services. For more information, see ESA Security Protection and Feature comparison of CDN, DCDN, and ESA.
|
Attack type |
Overview |
Protective measures |
|
DDoS attacks |
Application-layer attacks include HTTP GET floods, HTTP POST floods, and Challenge Collapsar (CC) attacks. These attacks mimic legitimate user requests, such as those from search engines and web crawlers, which makes them difficult to distinguish from normal traffic. These attacks often target resource-intensive operations on a web server, such as database queries or page rendering. By making a high volume of concurrent requests for these operations, attackers can overwhelm web services. Modern attacks are often hybrid. Any frequent, simulated user action, such as those from automated voting scripts, can be considered a CC attack. CC attacks target the backend of web applications, leading not only to denial of service but also degrading performance, including web response times, database services, and disk I/O. |
Edge Security Acceleration (ESA) integrates DDoS protection capabilities by default, using a layered defense system to quickly mitigate the impact of attacks, significantly reduce business downtime, and ensure your website remains available during an attack. ESA provides DDoS protection by default. Depending on your subscription plan, ESA offers different levels of DDoS protection to reduce service downtime and ensure that your website can resume normal operations as soon as possible. |
|
Traffic theft |
|
|
Related topics
For more information about security-related issues and solutions, see Security protection FAQ.