AWS ELB migration
Migrate AWS Elastic Load Balancing (ELB) resources — CLB, ALB, and NLB — to Alibaba Cloud SLB using Cloud Migration Hub (CMH).
Prerequisites
-
To migrate an ALB, associate the AliyunServiceRoleForAlb service-linked role with your Alibaba Cloud account.
-
To migrate an NLB, associate the AliyunServiceRoleForNlb service-linked role with your Alibaba Cloud account.
-
CMH supports only CLB, ALB, and NLB migration.
-
CMH only migrates listeners that forward to ECS instances. Migrate EC2 instances to ECS in the CMH migration plan first. Configure other listener types manually in the SLB console.
If you do not migrate EC2 instances through CMH, CMH cannot associate destination ECS instances during ELB migration. The related listeners are skipped. Configure them manually in the SLB console.
Resource discovery
Complete ELB resource discovery on the Resource Discovery page before you start the migration.
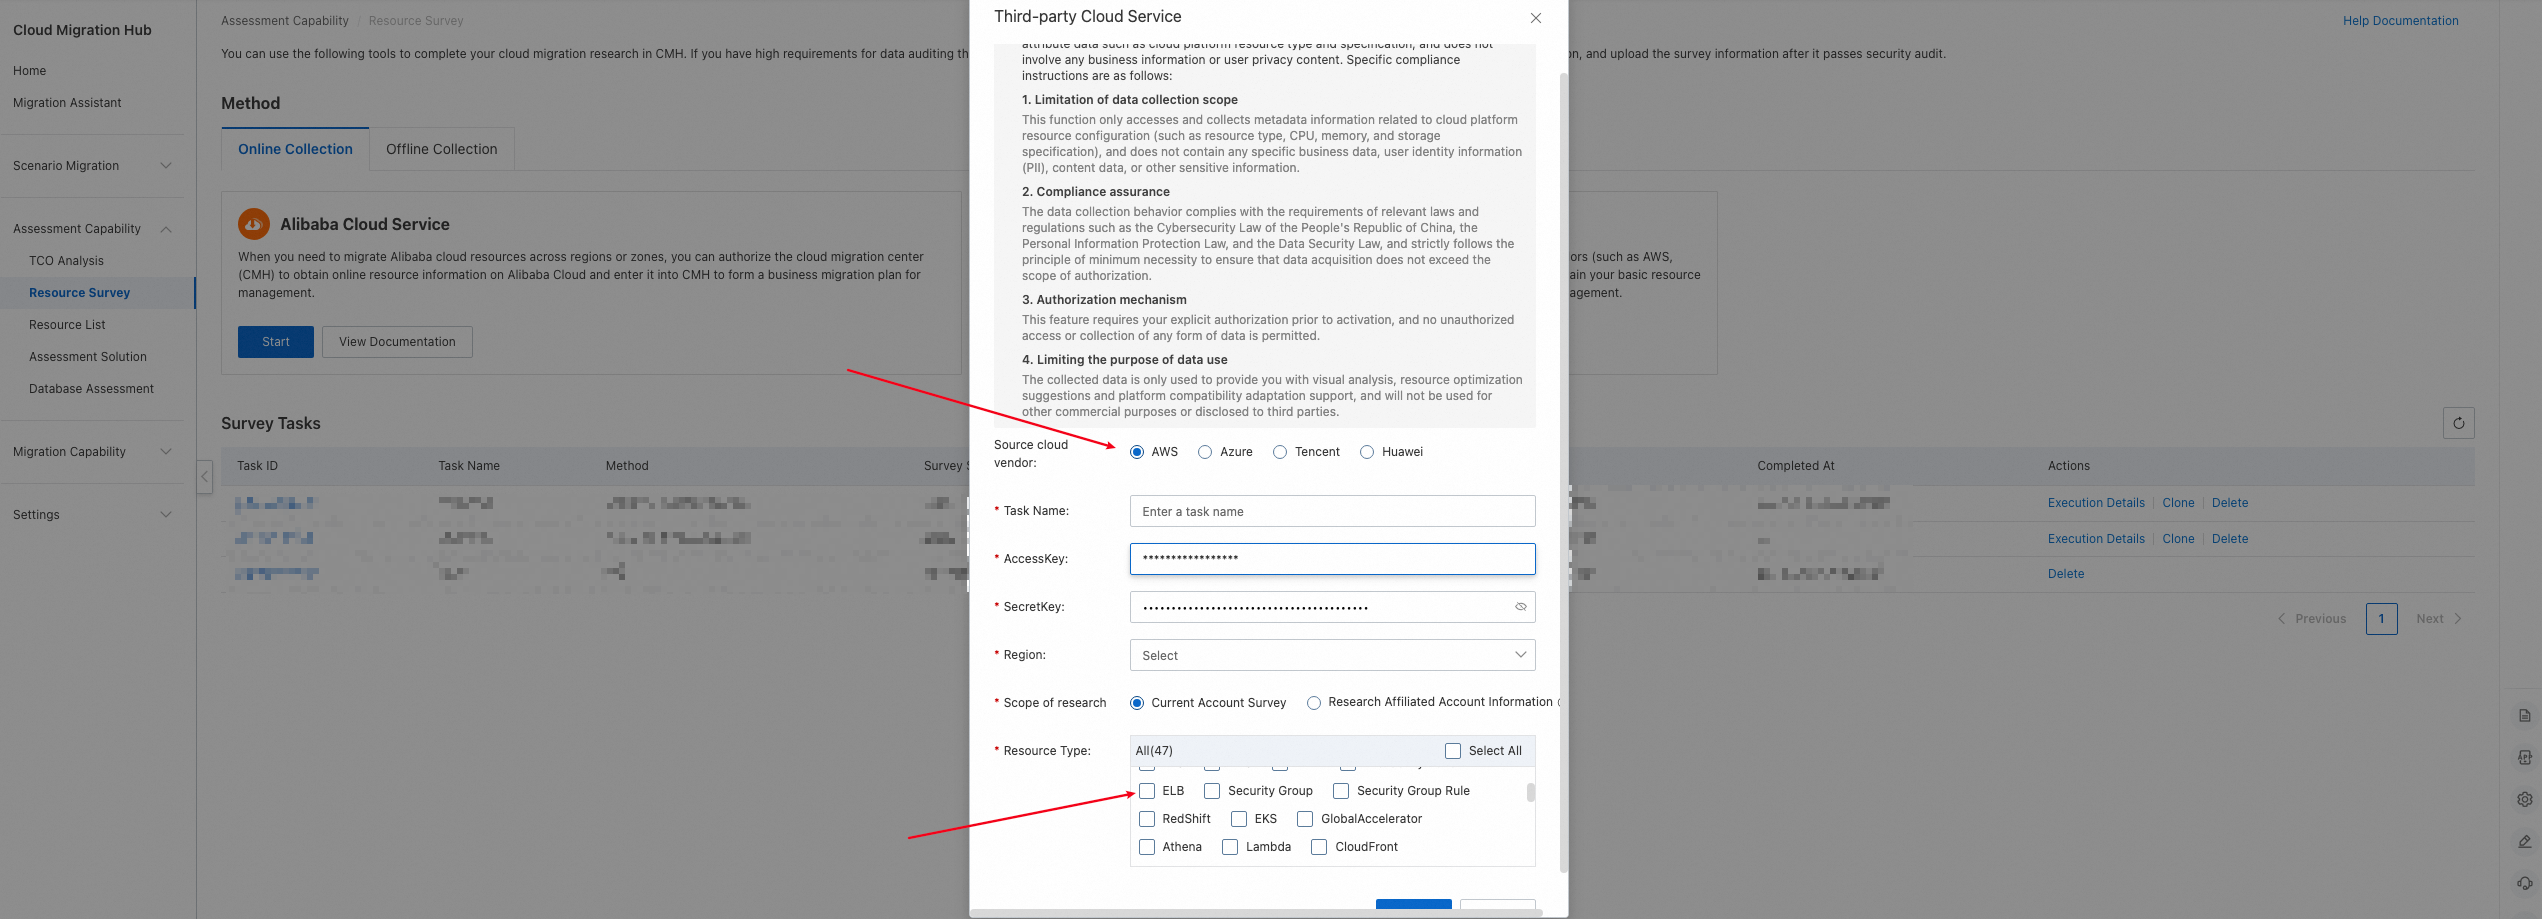
1. Go to . Set Source Cloud Vendor to AWS and include ELB in Resource Type.
2. After the discovery task completes, click Details to view the results.
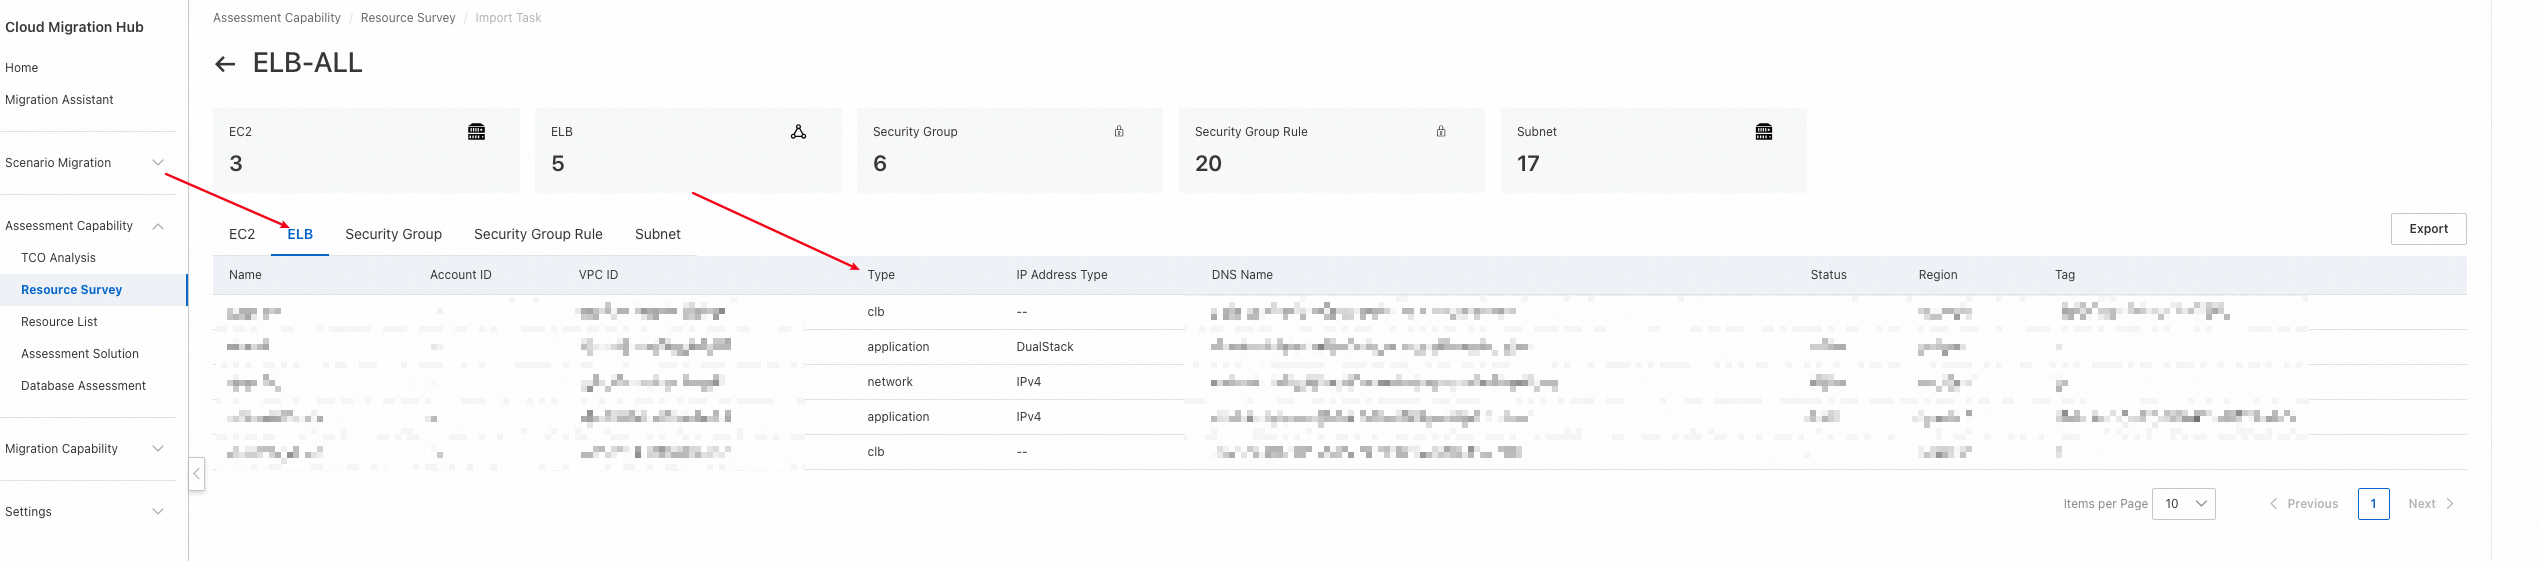
ELB types:
|
Type |
Meaning |
|
clb |
Classic Load Balancer |
|
application |
Application Load Balancer |
|
network |
Network Load Balancer |
3. Click a resource to view its details.
|
Information |
Type |
Description |
|
Basic information |
|
Load balancer basic information, such as name and network type. |
|
Listener List |
|
Source listener details. |
|
Health Check List |
|
Source health check configuration. |
|
Target Instance List |
|
Source target instance details. |
|
Target Group List |
|
Source target group details. |
Cross-cloud migration
Migrate AWS ELB to Alibaba Cloud SLB from the Migration Plan page.
Prerequisite: Migrate EC2 instances to ECS before migrating ELB. Otherwise, CMH creates only the SLB instance without listeners or server group configuration.
EC2 and ELB migrations can be in different plans, but EC2 migration must complete first.
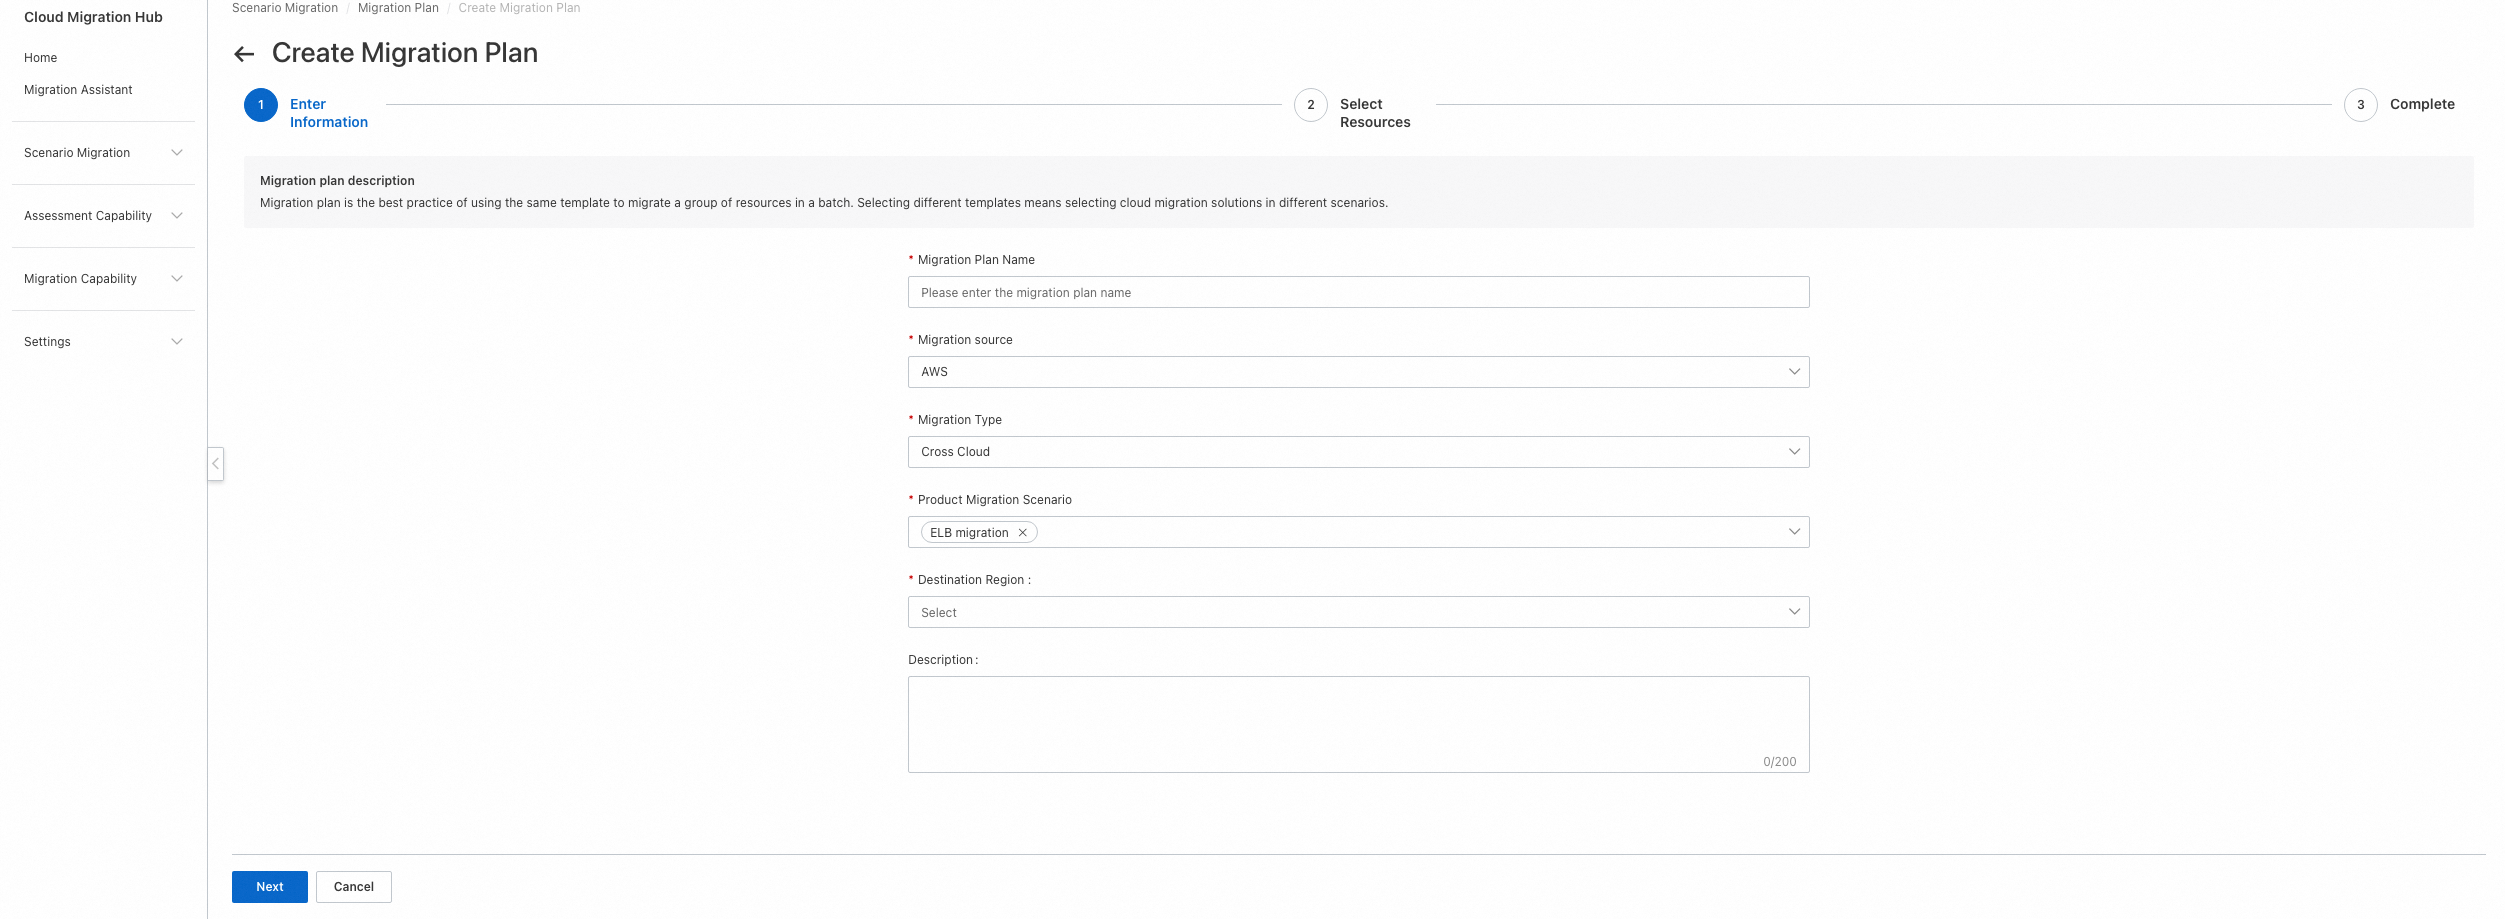
1. Go to and create a new migration plan.
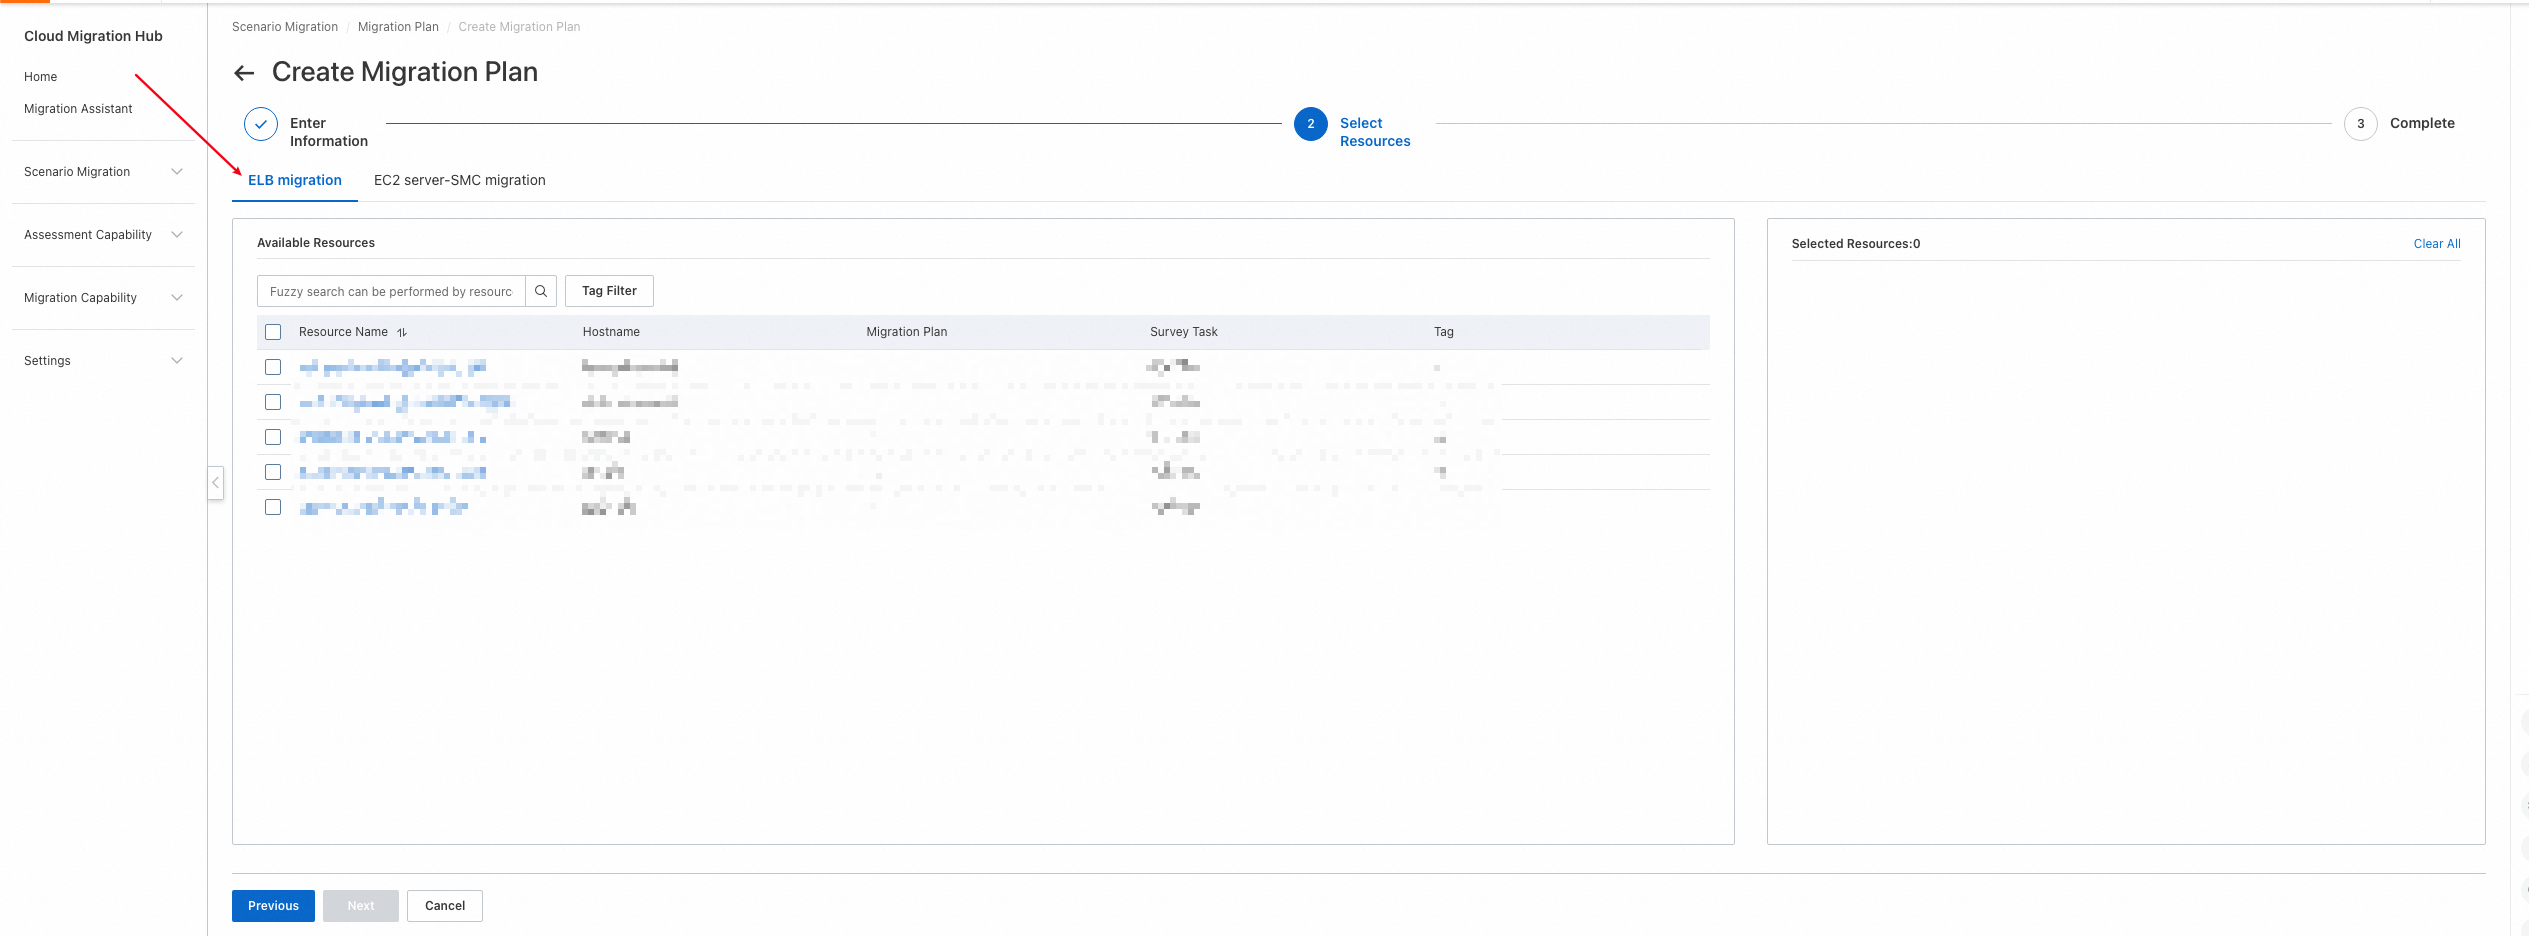
2. Confirm that destination ECS instances are created before mapping source listeners.
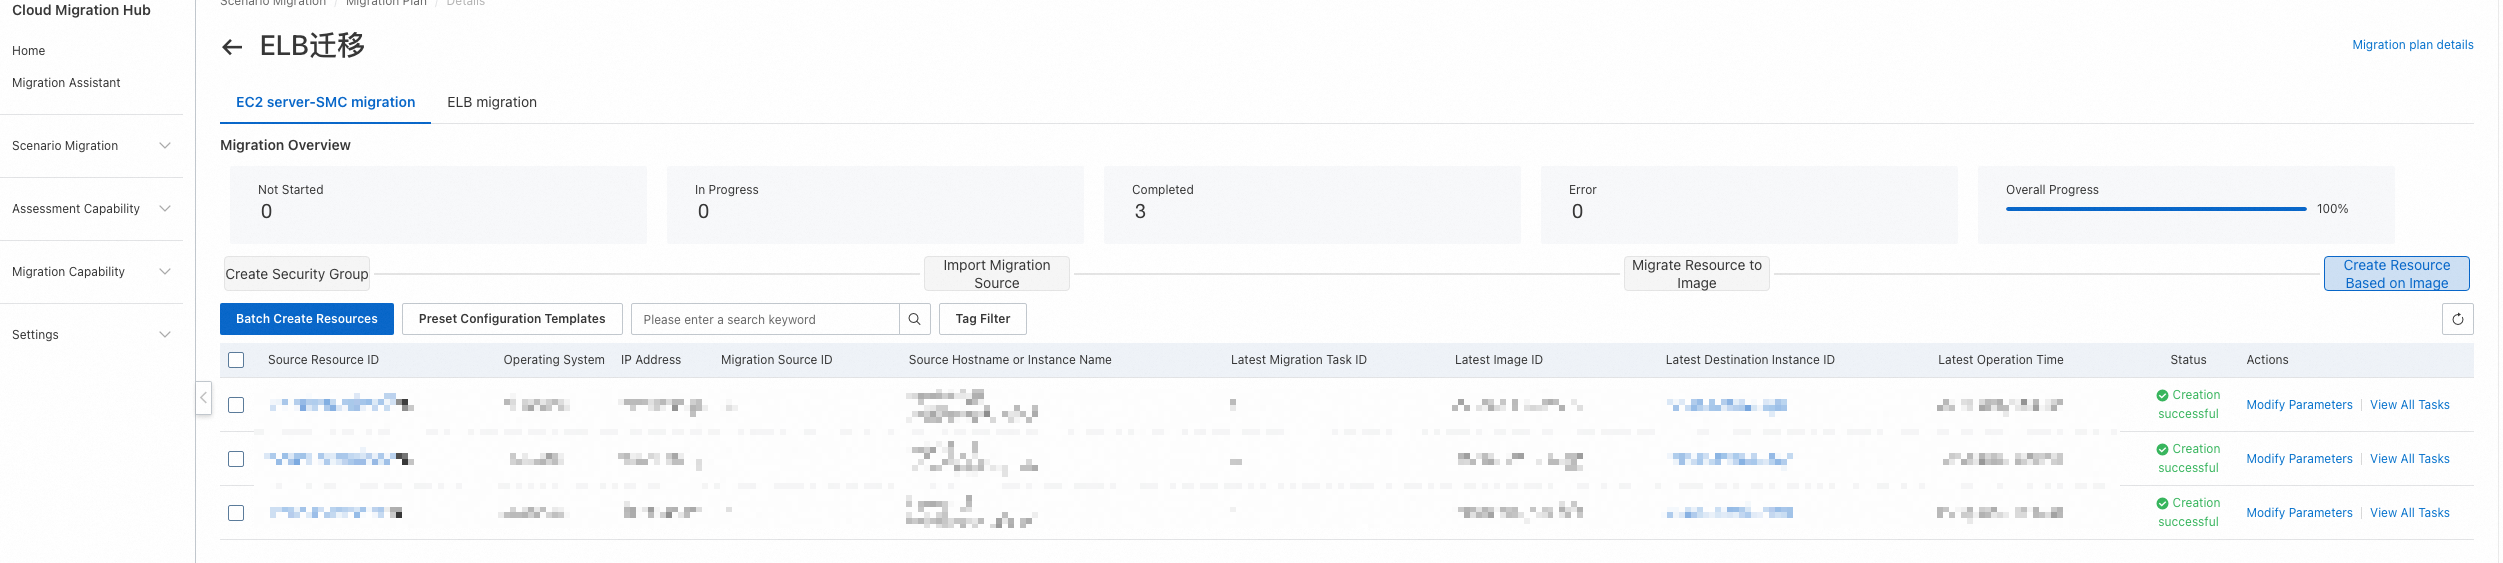
3. Configure load balancer parameters. Expand the mapped listeners and target groups, then click Modify Parameters to configure instance, listener, and target group settings. Select the resources to create and click Batch Create Resources.
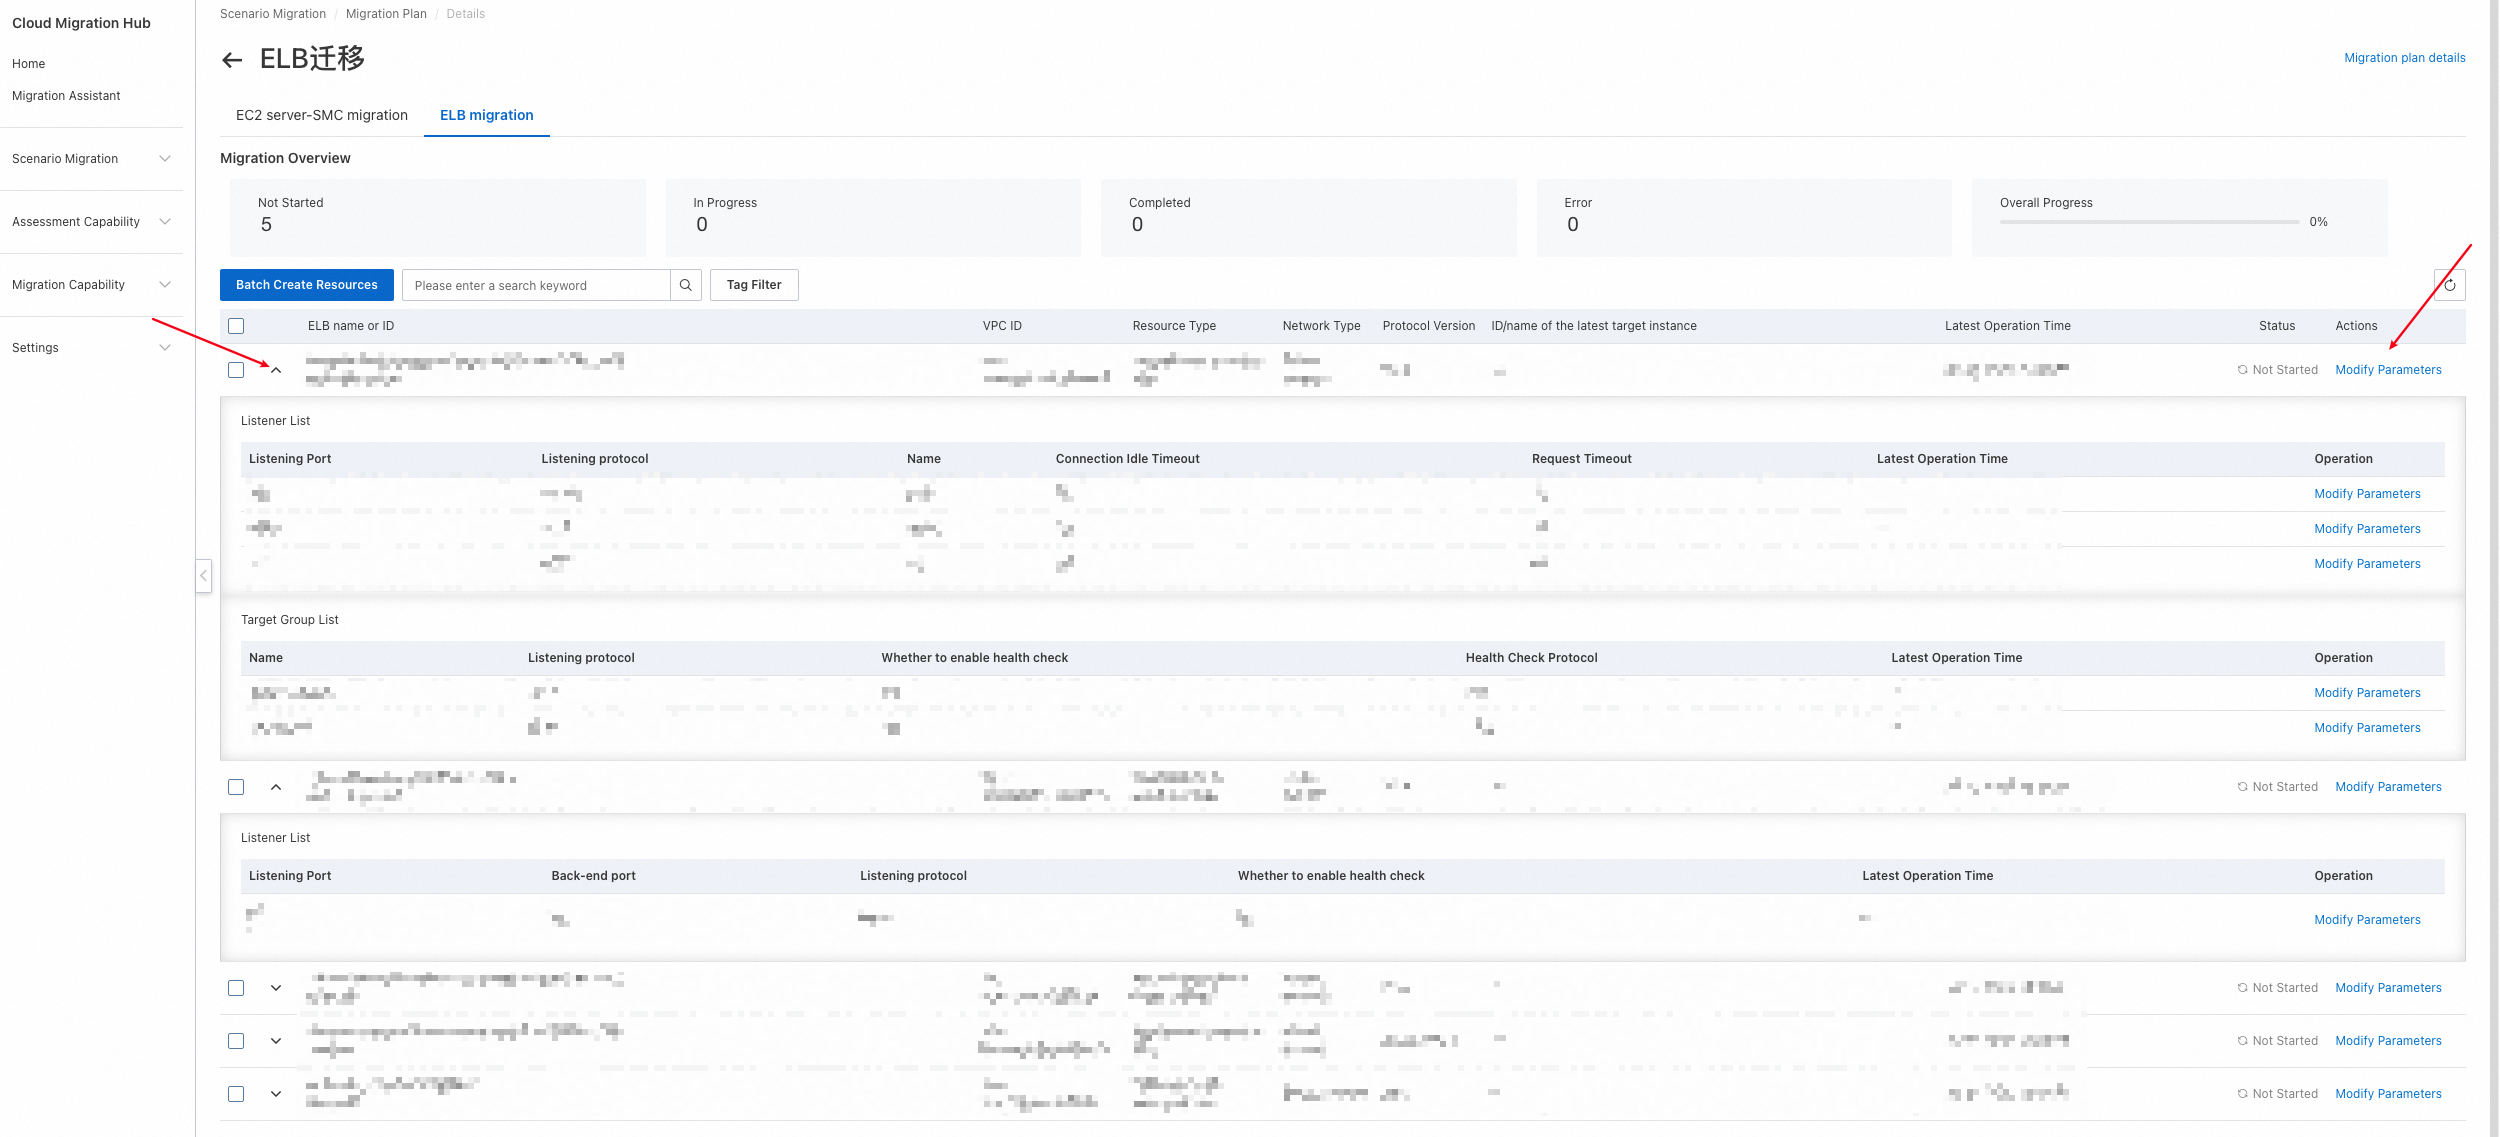
CLB parameter descriptions
Instance
|
Parameter |
Description |
|
Zone |
CLB uses multi-zone mode by default. Select the primary zone; the backend automatically assigns a secondary zone. |
|
Network Type |
|
|
Name |
Name of the CLB instance. |
|
VPC ID |
Required only for the internal network type. VPC ID |
|
vSwitch |
Required only for the internal network type. ID of the vSwitch in the primary zone. |
|
Metering method for Internet-facing instance |
Required only for the Internet network type. Important
Pay-by-traffic metering requires the pay-as-you-go billing method.
|
|
Billing method |
|
|
IP Version |
|
|
Specify private IP address for the instance |
Leave this empty to use a randomly assigned IP address. |
Listener
|
Parameter |
Description |
|
Listener Protocol |
Mapped from the source. Read-only. |
|
Listener Port |
|
|
Backend Port |
|
|
Listener bandwidth peak |
Peak listener bandwidth in Mbps. Valid values:
|
|
Scheduling Algorithm |
|
|
Access Control Type |
Important
Leave empty to auto-map the access control policy from the source. Otherwise, the mapping is overwritten. |
|
Access Control Policy Group ID |
Important
Leave empty to auto-map the access control policy from the source. Otherwise, the mapping is overwritten. |
|
Enable Health Check |
|
|
Health Check Type |
|
|
Health Check Port |
|
|
Health Check Timeout |
Maximum wait time for a health check response. The check fails if the backend server does not respond within this period. |
|
Health Check Interval |
|
|
Consecutive Successes |
Consecutive successful checks required to change a backend server's status from fail to success. |
|
Consecutive Failures |
Consecutive failed checks required to change a backend server's status from success to fail. |
|
Health Check Status |
HTTP status codes that indicate a successful health check. |
|
Health Check Domain Name |
Important
Leave empty to use the target server's IP address as the health check domain name. |
|
Health Check URI |
|
|
HTTP Health Check Method |
|
|
Custom Listener Name |
|
|
Enable getting the client IP address through the X-Forwarded-For header |
|
|
Enable Session Persistence |
|
|
Cookie Handling Method |
|
|
Cookie Timeout |
|
|
Cookie configured on the server |
|
|
Get the virtual IP address (VIP) of the client request through the SLB-IP header |
|
|
Get the SLB instance ID through the SLB-ID header |
|
|
Get the listener protocol of the SLB instance through the X-Forwarded-Proto header |
|
|
Enable Gzip compression for specific file types |
|
|
Enable HTTP to HTTPS forwarding |
|
|
Connection Idle Timeout |
SLB closes the connection after this idle period. A new connection is established on the next request. |
|
Request Timeout |
SLB returns an |
|
Get the listener port of the SLB instance through the XForwardedFor_SLBPORT header |
|
|
Get the client port for accessing the SLB instance through the XForwardedFor_ClientSrcPort header |
|
|
Server Certificate ID |
|
|
CA Certificate ID |
|
|
Enable HTTP/2 |
|
|
TLS Protocol |
|
|
Request string for UDP listener health check |
|
|
Response string for UDP listener health check |
Application Load Balancer parameter descriptions
Instance
|
Parameter |
Description |
|
Name |
|
|
VPC ID |
|
|
Zone |
Select at least two zones and their vSwitches. |
|
Address Mode |
|
|
Instance Edition |
ALB edition. Each edition has different feature limits and billing policies. |
|
IP Version |
Important
When you select Dual-stack, the VPC must support IPv6. |
|
Network Type |
|
|
Billing Method |
|
|
Enable Deletion Protection |
Listener
|
Parameter |
Description |
|
Protocol |
|
|
Listener Port |
|
|
Listener Name |
|
|
Access Control Type |
Important
Leave empty to auto-map the access control policy from the source. Otherwise, the mapping is overwritten. |
|
Access Control Policy Group ID |
Important
Leave empty to auto-map the access control policy from the source. Otherwise, the mapping is overwritten. |
|
Enable Gzip compression for specific file types |
|
|
Connection Idle Timeout |
SLB closes the connection after this idle period. A new connection is established on the next request. |
|
Request Timeout |
SLB returns an |
|
Server Certificate ID |
|
|
CA Certificate ID |
|
|
Enable HTTP/2 |
|
|
Enable Mutual Authentication |
Target Group
|
Parameter |
Description |
|
Name |
Listener protocol type, mapped from the source. Read-only. |
|
Listener Protocol |
|
|
Enable Connection Draining |
|
|
Connection Draining Timeout |
|
|
Scheduling Algorithm |
|
|
Enable Health Check |
|
|
Health Check Protocol |
|
|
Health Check Port |
|
|
Health Check Timeout |
Maximum wait time for a health check response. The check fails if the backend server does not respond within this period. |
|
Health Check Interval |
|
|
Consecutive Successes |
Consecutive successful checks required to change a backend server's status from fail to success. |
|
Consecutive Failures |
Consecutive failed checks required to change a backend server's status from success to fail. |
|
Health Check Status |
HTTP status codes that indicate a successful health check. |
|
HTTP Health Check Method |
|
|
Enable getting the client IP address through the X-Forwarded-For header |
|
|
Enable Session Persistence |
|
|
Cookie Handling Method |
|
|
Cookie Timeout |
|
|
Cookie configured on the server |
|
|
Enable IPv6 |
|
|
Enable backend keep-alive |
|
|
Enable cross-zone load balancing for the server group |
Enabled by default. |
NLB parameter descriptions
Instance
|
Parameter |
Description |
|
Name |
|
|
VPC ID |
|
|
Zone |
Select at least two zones and their vSwitches. |
|
Protocol Version |
Important
When you select Dual-stack, the VPC must support IPv6. |
|
Network Type |
|
|
Billing Method |
|
|
Enable Deletion Protection |
|
|
Security Group |
Listener
|
Parameter |
Description |
|
Protocol |
|
|
Listener Port |
|
|
Listener Name |
|
|
Connection Idle Timeout |
SLB closes the connection after this idle period. A new connection is established on the next request. |
|
TLS Protocol |
|
|
Support carrying the client source address to backend servers through the Proxy Protocol |
|
|
Enable Mutual Authentication |
Target Group
|
Parameter |
Description |
|
Name |
Listener protocol type, mapped from the source. Read-only. |
|
Protocol Version |
|
|
Listener Protocol |
|
|
Enable full-port forwarding |
|
|
Enable Connection Draining |
|
|
Connection Draining Timeout |
|
|
Enable client IP address persistence |
|
|
Scheduling Algorithm |
|
|
Enable Health Check |
|
|
Health Check Type |
|
|
Health Check Port |
|
|
Health Check Timeout |
Maximum wait time for a health check response. The check fails if the backend server does not respond within this period. |
|
Health Check Interval |
|
|
Consecutive Successes |
Consecutive successful checks required to change a backend server's status from fail to success. |
|
Consecutive Failures |
Consecutive failed checks required to change a backend server's status from success to fail. |
|
Health Check Status |
HTTP status codes that indicate a successful health check. |
|
HTTP Health Check Method |
|
|
Health Check URI |
|
|
Request string for UDP listener health check |
|
|
Response string for UDP listener health check |