Configure an associated role by using STS
Traditionally, DataWorks nodes relied on configuring plaintext AccessKeys to access external services like OSS. This approach poses security risks and management challenges. Hard-coding a permanent AccessKey creates a risk of exposure, potentially compromising your entire data assets if the key is leaked. Additionally, because managing keys for each task is complex, they are often granted coarse-grained permissions. This practice makes it difficult to implement fine-grained access control based on the least-privilege principle. To address these issues, use RAM role authorization. This approach uses Security Token Service (STS) to dynamically obtain temporary credentials, which eliminates the risk of key leakage and enables on-demand, task-specific, fine-grained permission management.
Solution overview
The configuration process has three main steps: Create a RAM role, Create a permissions policy, and Grant permissions to a RAM user.

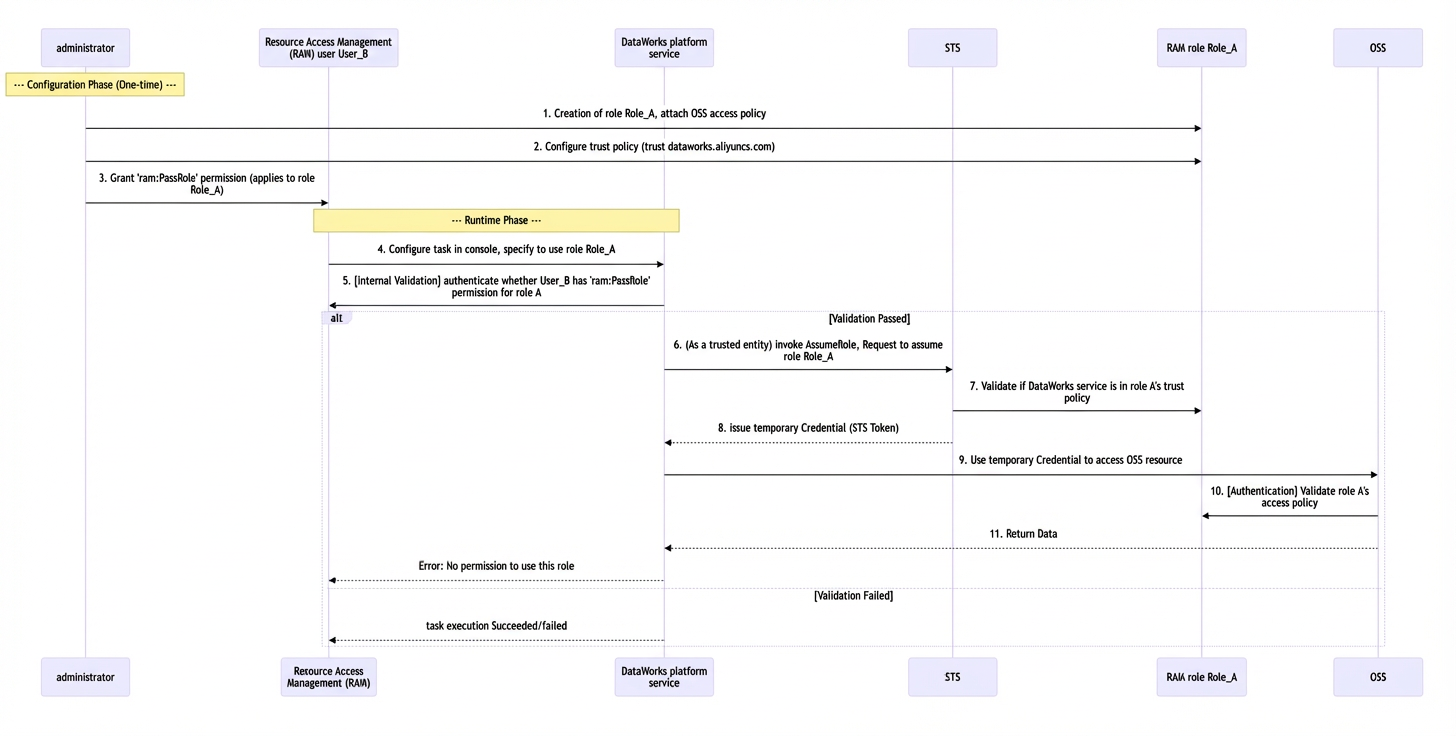
For a detailed explanation, see Appendix: STS invocation flow.
Prerequisites
You have an Alibaba Cloud account or a RAM administrator with AliyunRAMFullAccess permissions.
Step 1: Create a RAM role
This role is the identity credential that DataWorks assumes when accessing other cloud resources.
Create a RAM role: Log on to the Roles page of the RAM console and click Create Role. Keep the default selections, click Confirm, and enter a descriptive role name, such as
DataWorksRAMROLEforDataStudio.Modify the trust policy: After the role is created, go to its details page. On the Trust Policy tab, edit the policy to allow only the
dataworks.aliyuncs.comandengine.dataworks.aliyuncs.comservices to assume this role. The policy is as follows:For more information, see Modify the trust policy of a RAM role.
{
  "Version": "1",
  "Statement": [
    {
      "Action": "sts:AssumeRole",
      "Effect": "Allow",
      "Principal": {
        "Service": [
          "dataworks.aliyuncs.com",
          "engine.dataworks.aliyuncs.com"
        ]
      }
    }
  ]
}
Grant permissions to the RAM role: On the role's details page, go to the Manage Permissions tab and click Add Permissions. Grant the necessary permissions to the
DataWorksRAMROLEforDataStudiorole.For example, to access OSS, you can grant the
AliyunOSSReadOnlyAccess(read-only) orAliyunOSSFullAccess(full access) permissions.For more information, see Manage RAM role permissions.
In the Add Permissions panel, set the resource scope to account level, search for and select the required policy, and then click OK.
Step 2: Create a permissions policy
This policy allows a RAM user to pass the RAM role created in Step 1 to the DataWorks service.
Log on to the Policies page of the RAM console, click Create Policy, and switch to the JSON tab to edit the policy content.
Replace
<role-name>with the name of the RAM role for DataWorks, for example,DataWorksRAMROLEforDataStudio.{ "Version": "1", "Statement": [ { "Effect": "Allow", "Action": [ "ram:ListRoles" ], "Resource": "*" }, { "Effect": "Allow", "Action": "ram:PassRole", "Resource": "acs:ram::<account-id>:role/<role-name>" } ] }
Action | Description |
| Allows the user to view the list of roles in the account. This permission is required to select a role in the UI. |
| Allows the user to pass the specified role to a cloud service. Replace the
|
For more information, see Create a custom policy.
Click Determine and save the Permission Policy as
DataWorksRAMPolicyforDataStudio.
Step 3: Authorize a RAM user
In this final step, you grant the end user permission to pass the role.
Log on to the Users page of the RAM console. Find the RAM user that you want to authorize, for example,
new_ram_user@.... In the Operation column, click Add Permissions.In the Add Authorization panel, search for and select the permissions policy created in Step 2 (
DataWorksRAMPolicyforDataStudio), and confirm the authorization.
To authorize multiple RAM users, repeat this step for each user who needs this permission.
Next steps
After the authorization is complete, log on with the new_ram_user@... account and go to the Data Studio page. You can then use the associated role to run tasks on supported nodes. For more information, see Configure an associated role for a node in scheduling.
For a list of supported nodes, refer to the user interface.
Appendix: STS invocation flow
Alibaba Cloud RAM provides two core authorization models for roles: direct assumption (AssumeRole) and delegated authorization (PassRole).
Model 1: Direct assumption (sts:AssumeRole)
Core action: A trusted entity, such as a RAM user or an application, calls the STS
AssumeRoleAPI to obtain temporary credentials for a RAM role. This allows the entity to "become" that role.Authorization chain:
Entity A→Calls sts:AssumeRole→Assumes Role R→Gains permissions of Role R.Permission requirement: Entity A requires the
sts:AssumeRolepermission.Typical scenario: An application running on an ECS instance or a local server needs temporary access to OSS. The application uses its own AccessKey to call
AssumeRole, obtains temporary credentials, and then uses those credentials to access OSS. In this scenario, Entity A is the active executor.
Model 2: Delegated authorization (ram:PassRole)
Core action: An entity, such as a RAM user, "passes" a RAM role to a cloud service like DataWorks or ECS, authorizing that service to assume the role. The user does not assume the role.
Authorization chain: User_B → Passes Role_A → To a cloud service → Cloud service calls sts:AssumeRole to assume Role_A → Cloud service gains permissions of Role_A.
Permission requirement: User_B requires the
ram:PassRolepermission.Typical scenario: The scenario described in this document. A developer (User_B) configures a task in the DataWorks console and specifies a role, Role_A. To allow the DataWorks service to access OSS on the user's behalf, the user must have permission to "pass" Role_A to the DataWorks service. In this scenario, the user is the authorizer, and the cloud service is the delegated executor.
The interaction flow for the delegated authorization (PassRole) model has two stages: configuration and runtime.
Configuration stage: An administrator completes the initial setup, which includes creating the role, configuring its permissions and trust relationships, and granting the
PassRolepermission to the end user.Runtime stage:
User action and permission passing: The user specifies a role in DataWorks, which triggers the permission passing. The DataWorks platform verifies that the user has permission to "hand over" this role.
Service assumes the role: After verification, the DataWorks backend service (
dataworks.aliyuncs.com), acting as the principal, sends anAssumeRolerequest to STS.STS authorization and service execution: STS confirms that DataWorks is a trusted service for Role_A and issues temporary credentials to it. The DataWorks service then uses these credentials to access OSS and complete the task delegated by the user.