What is DKIM and how to add a record
This article explains DomainKeys Identified Mail (DKIM) and shows how to add a DKIM record.
Prerequisites
Before you begin, familiarize yourself with the concepts in What is DNS?
What is DKIM?
DomainKeys Identified Mail (DKIM) is an email authentication method that detects email spoofing and tampering, improving email security and trust. It lets a sender use a digital signature to prove an email originated from the claimed domain and was not altered in transit.
How to obtain the record value
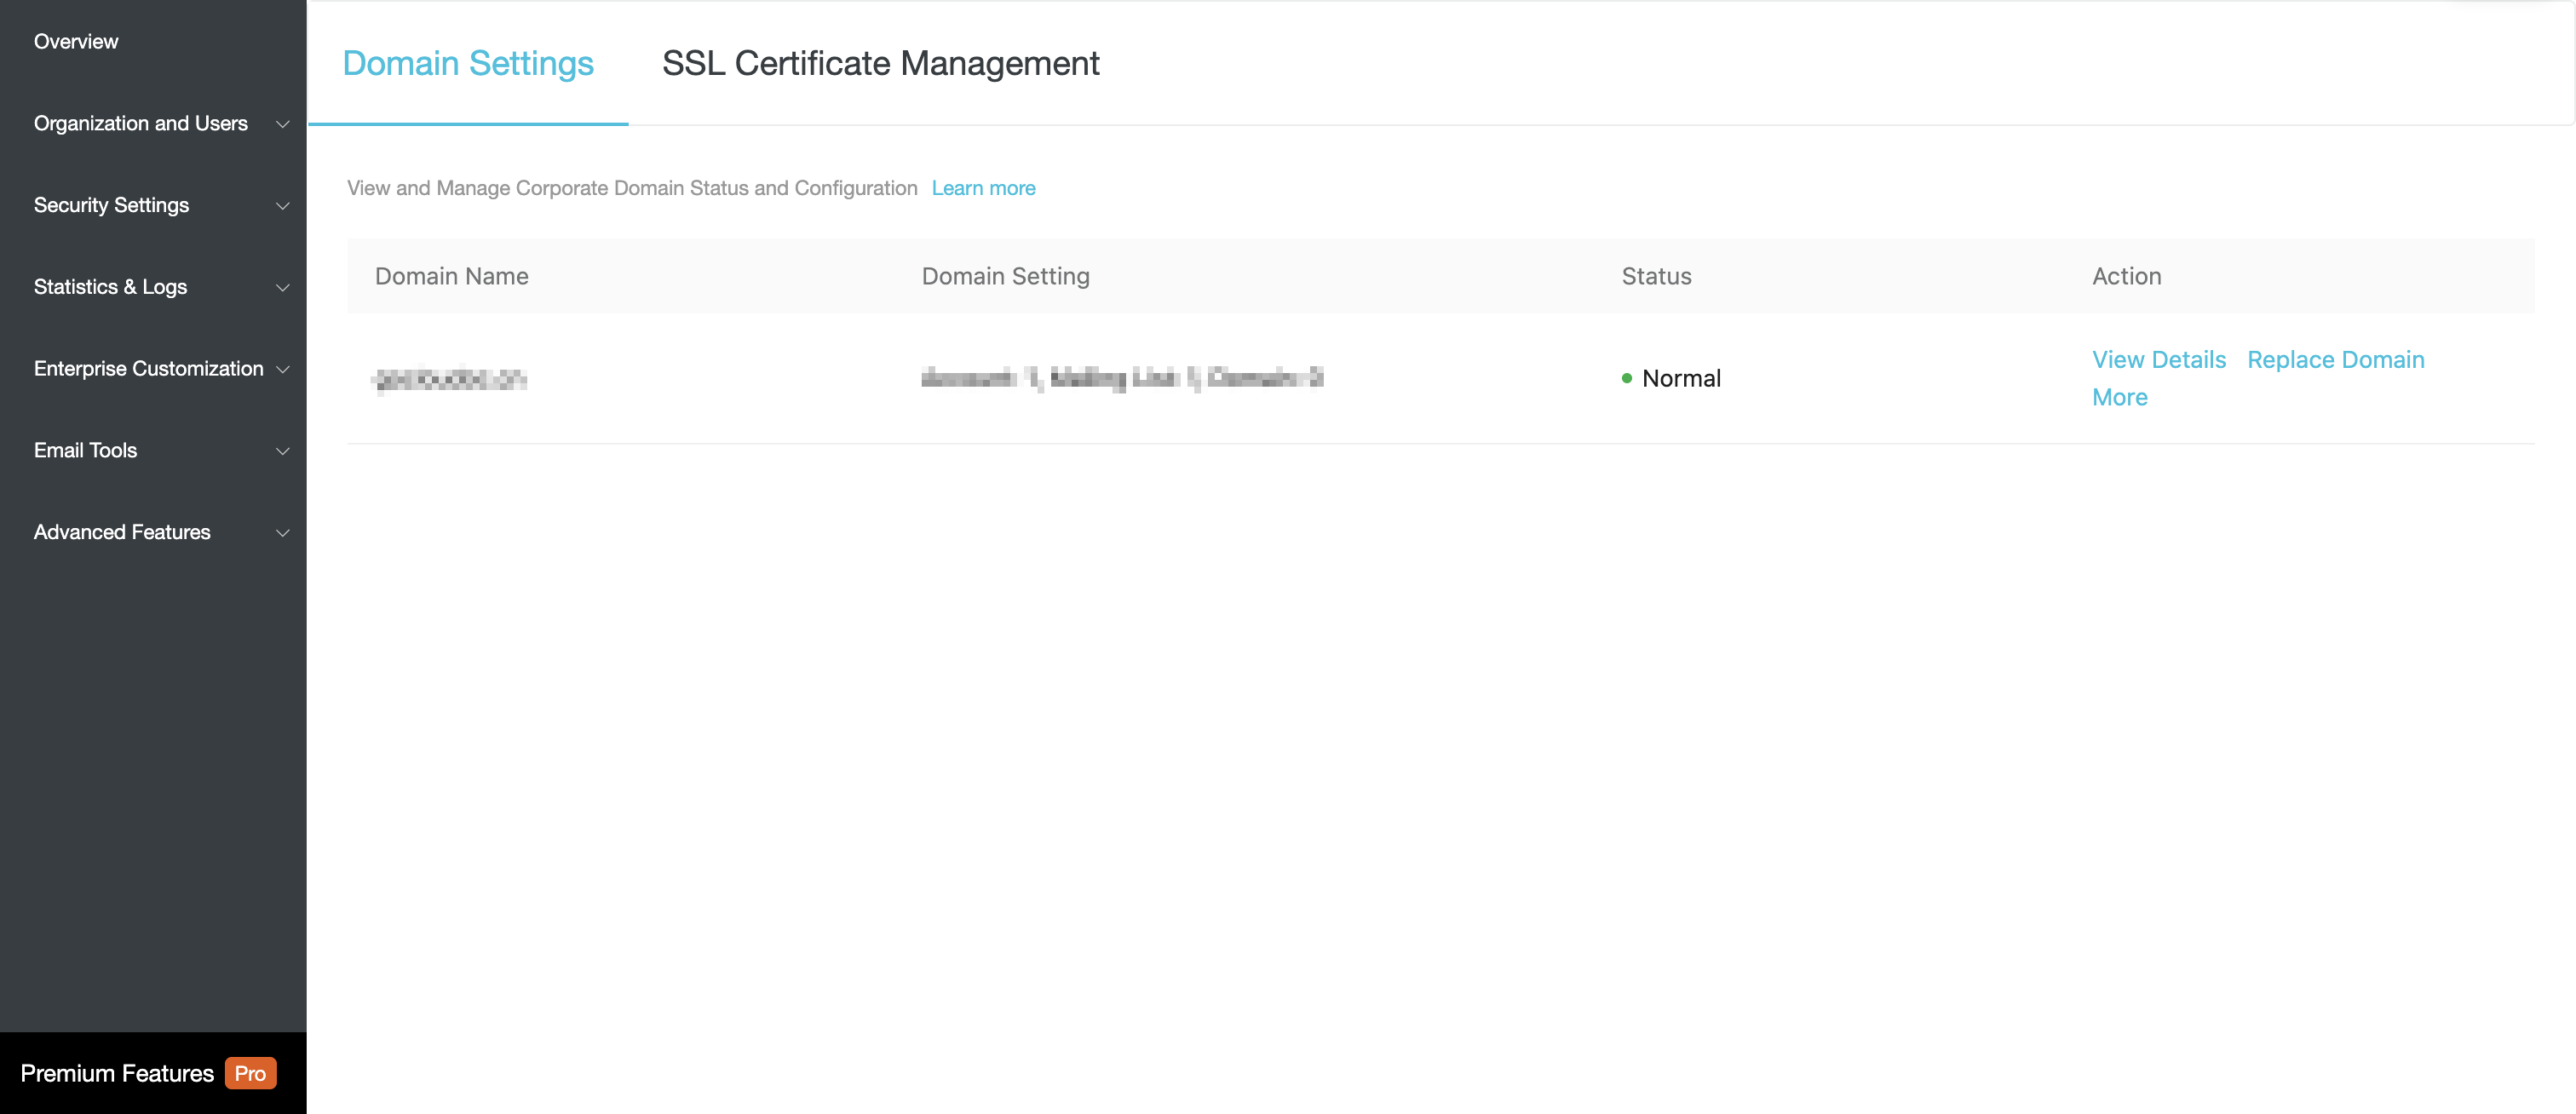
Log on to the management console as the email administrator. Navigate to Enterprise Customization > Domain Management > Domain Settings, and then click View Details.
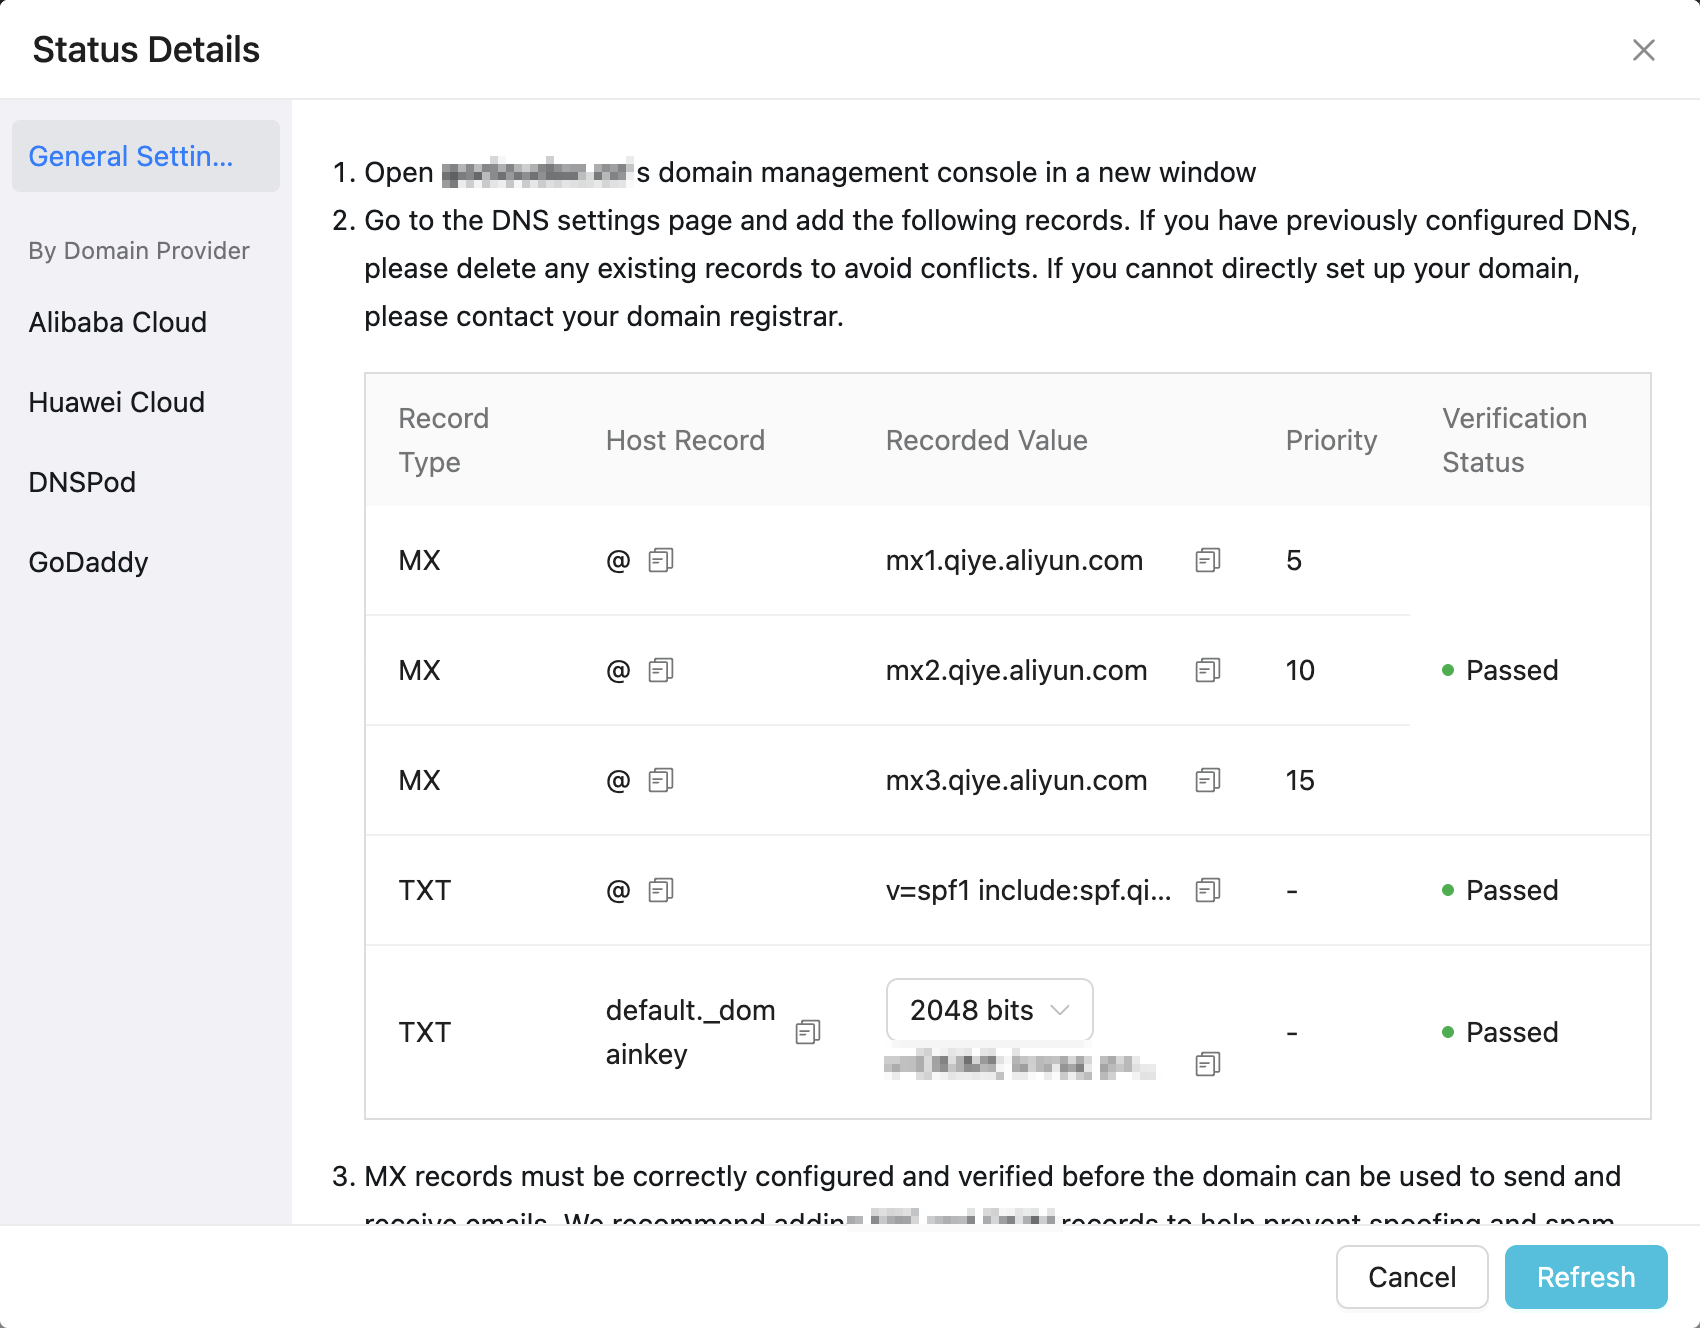
Click Copy to get the DKIM record value.
 Note
Obtain this information for your domain from your email management console.
The encryption bit length can be 1024 or 2048. Select the appropriate value based on the requirements of your domain management platform. Most platforms support both. If you change the encryption bit length, the previous record value becomes invalid. Update your domain's DNS settings with the latest record.
To apply the changes, navigate to another feature and then return to the Domain Management page. This action triggers server-side DKIM signing.
How to add the record
The following steps use the Alibaba Cloud DNS console as an example. If you use a different DNS provider, log on to its console to apply the required changes.
1. Log on to the Alibaba Cloud DNS console.
2. Click your domain name to go to the DNS Settings page.
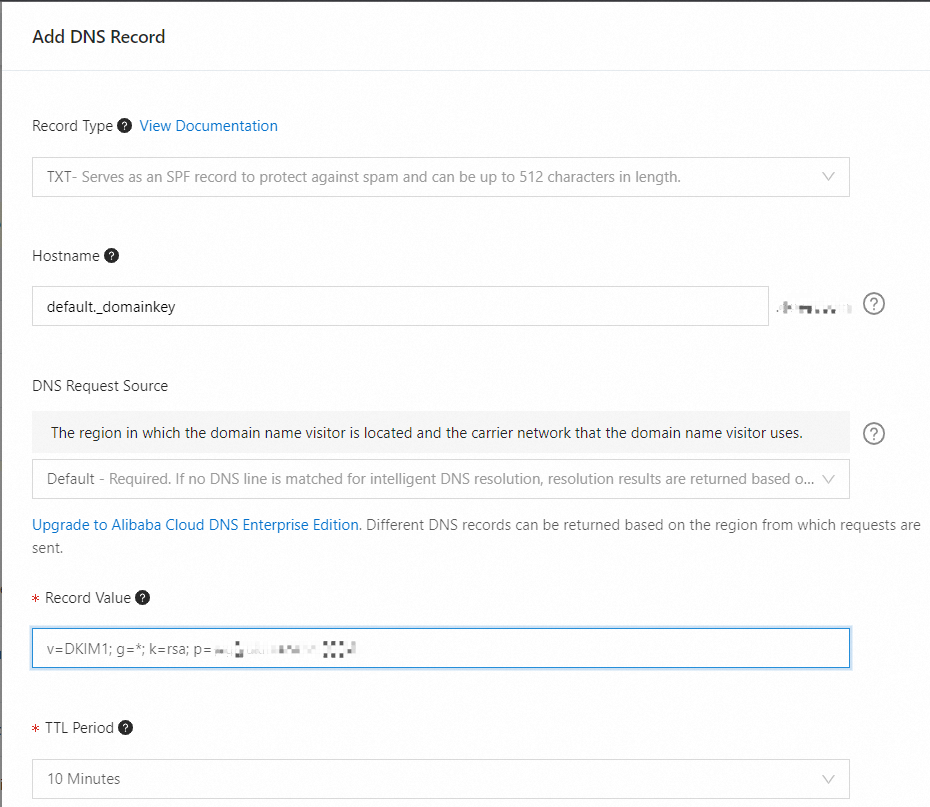
3. On the DNS Settings page, click the Add Record button to create a TXT record.
4. When adding a TXT record, set the host record to default._domainkey.
5. TXT record value: v=DKIM1; g=*; k=rsa; p=... (Note: The record is a single line).  The following figure shows an example of adding a DKIM record:
DKIM Signature Syntax
When an email is sent, if DKIM is enabled, the sending server adds a DKIM signature header to the email. This DKIM signature includes information to verify the email, and its key parts include the signature (generated by using a private key) and the selector. A selector is a unique string identifier that is used to identify a specific DKIM public key record.
When an email is sent with DKIM enabled, the sending server adds a DKIM-Signature header to the message. This header contains the information required to verify the email, including a digital signature generated with a private key and a selector. The selector is a unique string that identifies the specific public key record in DNS.
DKIM-Signature: v=1; a=rsa-sha256; d=example.com; s=default; c=relaxed/relaxed;
h=from:to:subject:date:message-id; i=@example.com;
bh=...; b=...;
In this header:
v=1indicates the DKIM version.a=rsa-sha256indicates the signing algorithm.d=example.comindicates the sending domain.s=defaultindicates the selector used for the signature.c=relaxed/relaxedindicates the canonicalization algorithm.h=from:to:subject:date:message-idindicates the signed header fields.i=@example.comindicates the signing identity.The part after
bh=is the hash of the message body.The part after
b=is the signature itself.
When a receiving server receives the email, it inspects the DKIM-Signature header to find the values for d= (domain) and s= (selector). These two values tell the receiving server which DNS record to query to find the corresponding public key.
The receiving server constructs a DNS query based on the sending domain (d=example.com) and the selector (for example, default), in the following format:
default._domainkey.example.comThe receiving server then queries this DNS record, obtains the public key, and uses this public key to verify the validity of the signature b=. If the signature verification is successful, it confirms that the email is from the claimed domain and was not tampered with in transit.
If a domain has multiple sending sources, each source should use a different selector so that recipients can find the correct public key from the selector in the DKIM-Signature header of each email.