Grant permissions to a RAM user by using an Alibaba Cloud account
Resource Access Management (RAM) lets you create RAM users for your employees and grant each user only the permissions they need—without exposing your Alibaba Cloud account's AccessKey pair. Only RAM users with the appropriate permissions can access or manage Function Compute resources in the console. All resource usage and costs are billed to the Alibaba Cloud account.
Prerequisites
Before you begin, ensure that you have:
-
An active Alibaba Cloud account with Function Compute enabled
-
RAM administrator access (or Alibaba Cloud account credentials) to the RAM console
Step 1: Create RAM users
-
Log on to the RAM console using your Alibaba Cloud account or a RAM user with administrative rights.
-
In the left-side navigation pane, choose Identities > Users.
-
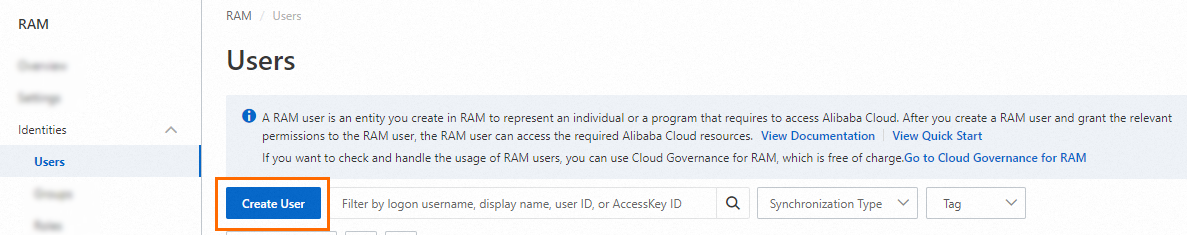
On the Users page, click Create User.
-
In the User Account Information section, configure the following parameters:
To create multiple RAM users at once, click Add User.
Parameter Description Logon Name Up to 64 characters. Allowed characters: letters, digits, periods ( .), hyphens (-), and underscores (_).Display Name Up to 128 characters. Tag Click the  icon, then enter a tag key and value. Tags help you manage and organize RAM users.
-
In the Access Mode section, select one access mode for the RAM user.
Select only one access mode per user to keep individual users separate from programmatic users.
-
Console Access — for employees who need to log on to the Alibaba Cloud Management Console with a username and password. Configure the following options:
Option Description Set Console Password Select Automatically Regenerate Default Password or Reset Custom Password. Custom passwords must meet the complexity requirements. See Configure a password policy for RAM users. Password Reset Specify whether the RAM user must reset the password on next logon. Enable MFA Enable multi-factor authentication (MFA) for additional security. After enabling MFA, bind an MFA device to the RAM user. See Bind an MFA device to a RAM user. -
Using permanent AccessKey to access — for programs that call API operations. The system automatically generates an AccessKey ID and AccessKey secret. See Obtain an AccessKey pair.
The AccessKey secret is shown only once at creation and cannot be retrieved later. Copy and store it securely before closing the page.
-
-
Click OK.
-
Complete the security verification as prompted.
Step 2: Grant permissions to RAM users
-
Log on to the RAM console as a RAM administrator.
-
In the left-side navigation pane, choose Identities > Users.
-
On the Users page, find the RAM user and click Add Permissions in the Actions column.
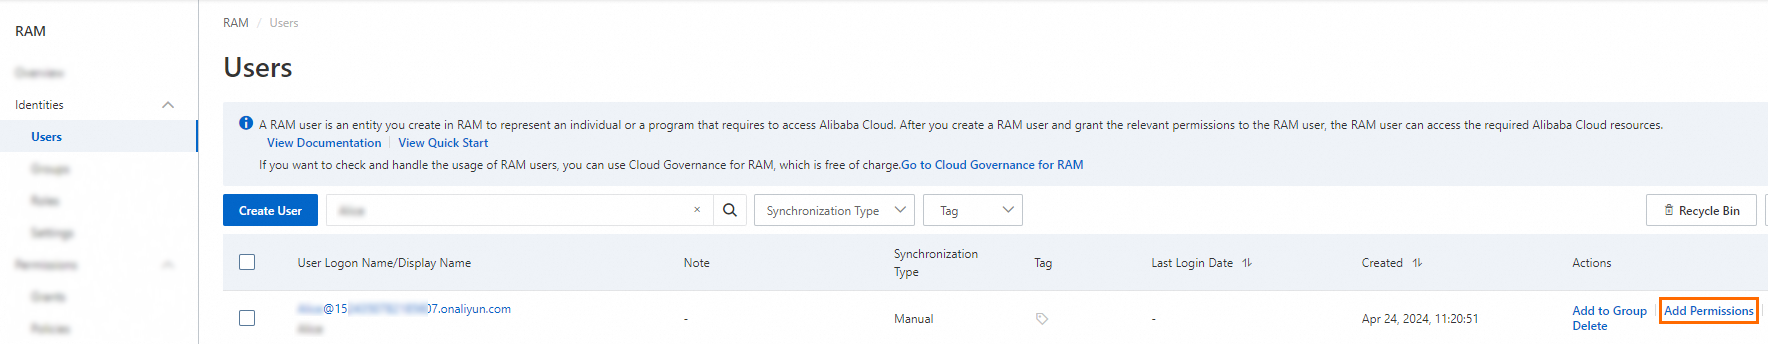
To grant permissions to multiple RAM users at once, select them and click Add Permissions at the bottom of the page.
-
In the Grant Permission panel, configure the following:
-
Resource Scope — defines where the permissions apply:
Option Description Account Permissions take effect on all resources in the current Alibaba Cloud account. Applicable to general scenarios that do not require isolation by resource group. ResourceGroup Permissions take effect only on resources in the specified resource group. Applicable to scenarios in which multiple teams share one Alibaba Cloud account and permissions must be isolated by resource group. If a RAM user is granted resource-group-level permissions, the user must switch the resource scope to the authorized resource group in the top navigation bar after logging on to the console. Otherwise, the user cannot access or manage the resources in that group. Make sure Function Compute supports resource groups before selecting this option. See Services that work with Resource Group and Use a resource group to grant a RAM user the permissions to manage a specific ECS instance. -
Principal — the RAM user that receives the permissions. If you start the authorization from the Users page, the system automatically selects the current RAM user. If you start from the Grants page, you must manually select the RAM users. You can select multiple RAM users at a time.
-
Policy — the set of permissions to grant. Select one or more policies. System policies are created and maintained by Alibaba Cloud and can be searched and selected directly. To locate a policy, search by product name (such as
fcoross), by permission level (such asReadOnlyorFullAccess), or by the full policy name. Fuzzy match is supported. Common Function Compute system policies include:Policy Permissions granted AliyunFCFullAccessFull access to all Function Compute resources and operations. AliyunFCReadOnlyAccessRead-only access to Function Compute resources. If no system policy matches the target product, see Policies and sample policies for the full list, or create a custom policy for finer-grained permission control. Custom policies must be created before they can be attached. See Create a custom policy.
Pagination limit — the policy list is paginated, and the Select All operation takes effect only on the current page. After you go to another page, the policies that you selected remain in the selected list, but the policies on the new page are not automatically selected. Select them page by page.
Quick administrator grant — to grant administrator permissions, search for
AdministratorAccessand select it directly instead of selecting policies page by page. The system automatically flags high-risk system policies, such asAdministratorAccessandAliyunRAMFullAccess, which typically provide full control over all cloud resources or full management permissions on RAM. Selecting such a policy triggers a high-risk alert. Attach them with caution. -
(Optional) Remark — enter the reason or the scenario of the authorization, such as "Dedicated authorization for OSS upload tasks". A remark helps you trace the authorization during later audits.
-
-
Click Grant permissions. After you confirm that the policies are bound to the RAM user, click Close.
Security best practices
Apply these practices to reduce credential exposure and limit blast radius:
-
Separate console users from programmatic users. Assign Console Access to employees and Using permanent AccessKey to access to programs—not both to the same user.
-
Apply least-privilege permissions. Grant only the permissions a user needs. Start with
AliyunFCReadOnlyAccessand escalate if required. -
Enable MFA for console users. MFA adds a second layer of authentication that significantly reduces account compromise risk.
-
Use Security Token Service (STS) tokens instead of permanent AccessKey pairs for programmatic access. STS tokens are short-lived and reduce the impact of credential leaks. See Best practices for using an access credential to call API operations.
-
Revoke permissions and delete RAM users when no longer needed. RAM users and their permissions can be removed at any time without affecting the Alibaba Cloud account.
Next steps
After creating and authorizing RAM users, share their credentials with the relevant employees:
-
Console access — share the logon name and password. The employee logs on at the Alibaba Cloud Management Console. See Log on to the Alibaba Cloud Management Console as a RAM user.
-
API access — share the AccessKey ID and AccessKey secret. The employee uses these credentials in code to call Function Compute API operations.