Jira and Confluence SSO
This guide explains how to configure single sign-on (SSO) for Jira in IDaaS.
Overview
Jira is a project and issue tracking tool developed by Atlassian. It is widely used for bug tracking, customer service, requirements gathering, workflow approvals, task tracking, project management, and agile management. Jira features flexible configuration, comprehensive features, simple deployment, and rich extensibility.
For Jira 7.12 and earlier, you configure SSO from the Authentication methods menu. For Jira 7.13 and later, you use the SSO 2.0 menu. The settings are similar, so you can follow this guide for both versions.
Some versions of Jira do not include a built-in SSO feature. To enable SSO, you must install a plugin from the Atlassian Marketplace. The configuration process is similar for both Jira and Confluence.
The steps in this guide use Jira Server v7.12 as an example.
Procedure
Step 1: Add an application in IDaaS
On the IDaaS console, go to , search for Atlassian Jira, and click Add Application.
After adding the application, you are automatically redirected to the SSO configuration page.
The Application Settings section in IDaaS provides the parameters required for the Jira configuration.

Step 2: Configure Jira
Navigate to the single sign-on settings
In a new browser tab, sign in to the Jira administration console. From the menu in the top-right corner, select System.
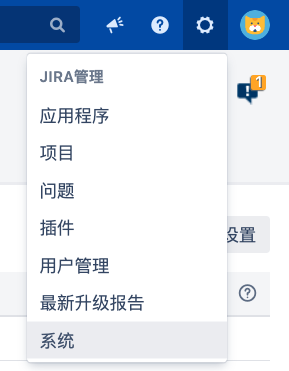
Navigate to .
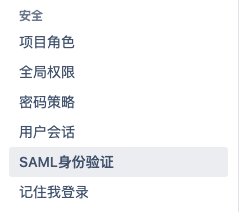
Enable single sign-on.
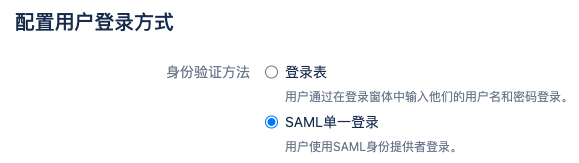
To enable SAML single sign-on, you must first configure HTTPS for your Jira or Confluence environment.
Configure SAML settings
In the SAML SSO 2.0 settings, enter the three parameters from the Application Settings page in IDaaS, and then save the configuration.
Parameter | Alias | Description |
Single sign-on issuer | IdP Entity ID | |
Identity provider single sign-on URL | IdP Sign-in URL, SAML SSO URL | Jira sends SAML requests to this URL to initiate SSO. |
X.509 certificate | Public key certificate |
Sample configuration:
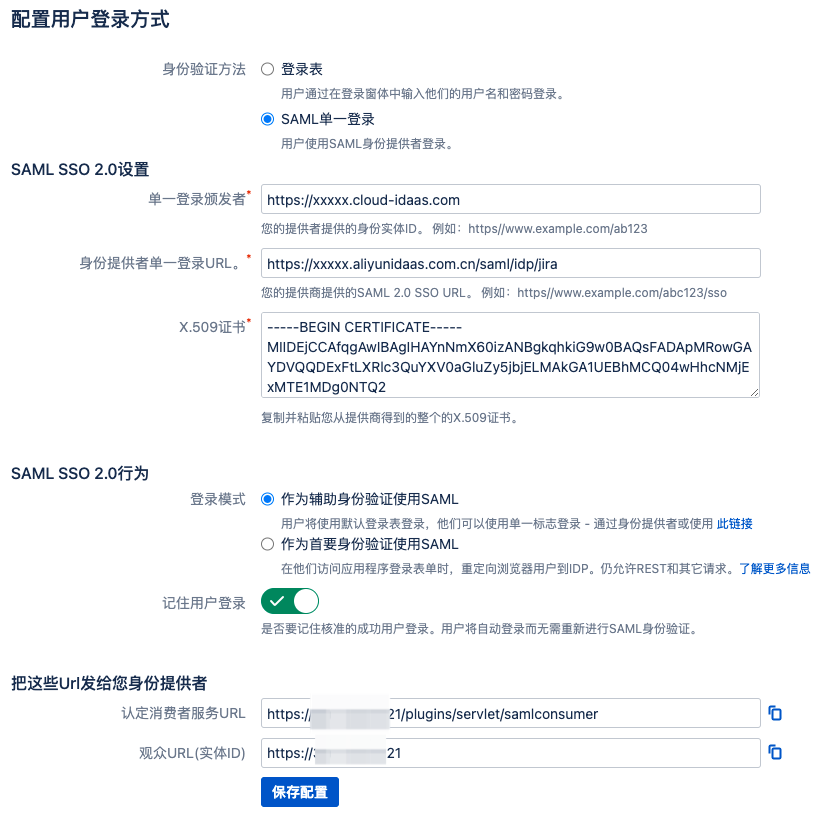
Copy the Assertion Consumer Service URL and Audience URL (Entity ID) displayed at the bottom of the page. You will enter these values in IDaaS in the next step to complete the configuration.
Additionally, if you want users to sign in to Jira directly with their IDaaS accounts and bypass the portal (an SP-initiated SSO flow), copy the logon link from the logon mode section. You can save this link as a bookmark and distribute it to your team.
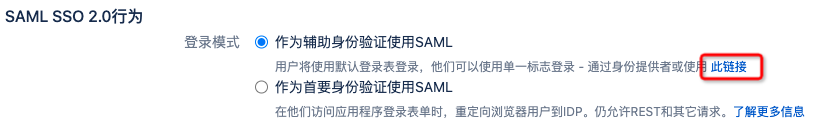
Step 3: Configure SSO in IDaaS
Return to the Jira application's SSO configuration page in IDaaS.
Enter the Assertion Consumer Service URL and Audience URL (Entity ID) that you copied from Jira.

For testing purposes, you can temporarily set the Authorization Scope to All users. Leave the other options at their default settings and click Save to complete the SSO configuration.
Application account: By default, the IDaaS username is used as the login identifier for the application. The username in the application must match the IDaaS username for SSO to succeed. For more flexible configurations, see Configure SAML application accounts.
Authorization scope: By default, the application is available to all users. To specify which IDaaS accounts can access the application, see General SSO configurations.
Step 4: Test SSO
You can now test the Jira SSO connection.
IdP-initiated SSO
Sign in to the IDaaS portal with an authorized account. Click the Jira icon on the portal to initiate SSO and verify the configuration.
SP-initiated SSO
Open the logon link that you copied earlier in a browser. If you are not signed in, you are redirected to the IDaaS sign-in page. After successful authentication, you are redirected to Jira.