Secure tunnel overview
IoT Platform provides the secure tunnel feature to enable remote access, remote diagnosis, and management of devices. This topic describes the concepts and usage of secure tunnels.
The GlobalSign Root R1 certificate, a globally trusted root certificate issued by the third-party certificate authority GlobalSign, is about to expire (this is an industry-planned root certificate rotation, not a unilateral adjustment by Alibaba Cloud). Some applications have already upgraded to the R46 certificate. The IoT Platform server side already supports the R46 certificate, but the device side currently only supports the R1 certificate, which affects the availability of the SSH secure tunnel feature (other features are not affected). You need to perform a device-side upgrade to continue using this feature. For upgrade details, see Root certificate update plan.
What is a secure tunnel
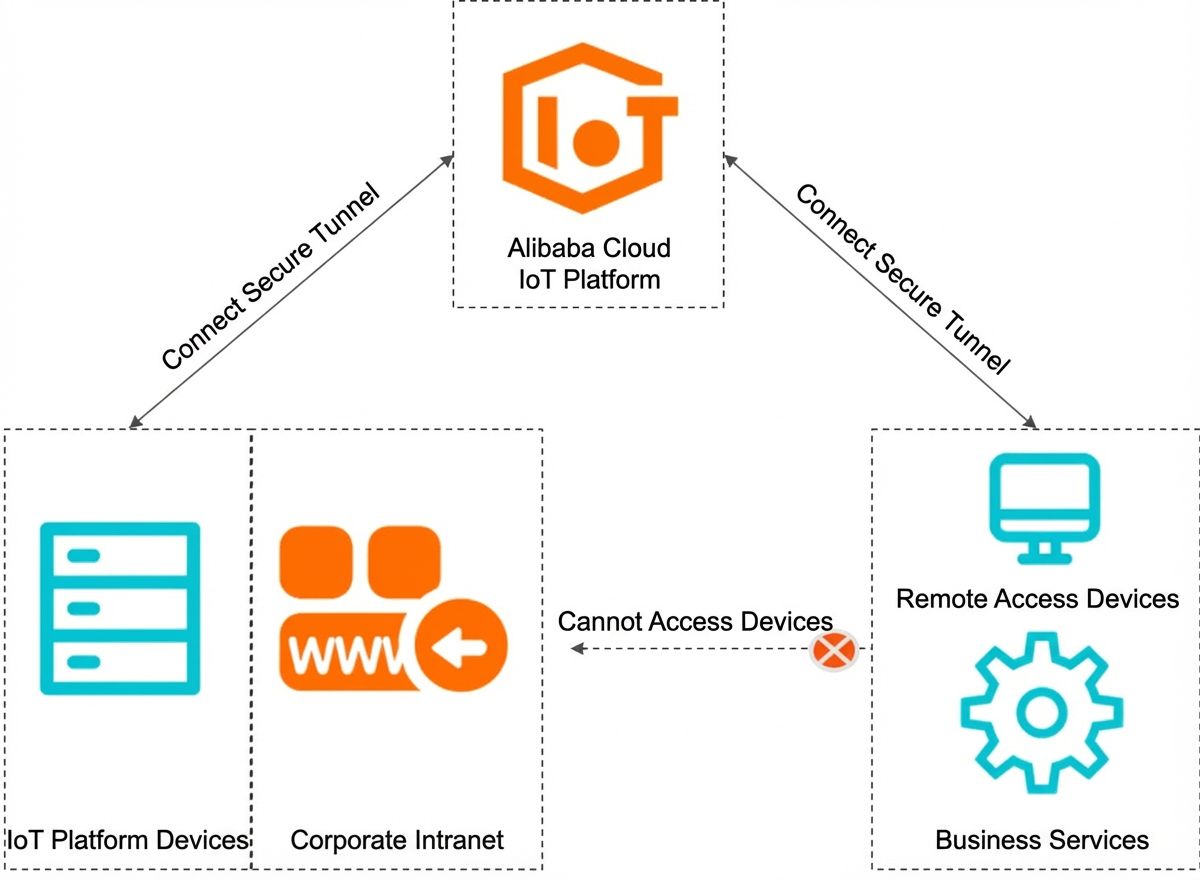
When a device is deployed on an enterprise intranet, you must obtain access permissions and a connection method to access the device remotely. The secure tunnel feature of IoT Platform establishes a WebSocket channel between the access client and the device. This enables you to remotely connect to IoT Platform devices on an enterprise intranet.
After the access client and the device successfully connect to the secure tunnel, you can use the secure tunnel to remotely log on to the device, for example, through the Secure Shell (SSH) service. This lets you perform remote diagnosis, troubleshooting, O&M, configuration updates, and other tasks.
Glossary
| Term | Description |
| Secure tunnel | A secure WebSocket channel established between the device, the access client, and IoT Platform. It serves as a data transmission channel between the access client and the IoT Platform device, providing data pass-through capabilities. |
| Access client | The device or application that remotely accesses an IoT Platform device through a secure tunnel. For example, an O&M engineer's laptop. |
| Device-side proxy (Device Agent) | The proxy software that implements the secure tunnel feature on the device. The device-side Link software development kit (SDK) for IoT Platform provides a software package for secure tunnels. For more information, see Device-side secure tunnel. |
| Device-side target application | The local application on the device that the access client wants to interact with during remote access. For example, the SSHD service in a local device application. |
| Access client URL and token | The unique URL and token generated after a secure tunnel is created. They are used for WebSocket connection establishment and authentication between the access client and IoT Platform. |
| Secure tunnel session | Communication between the access client and the device requires creating a session within the secure tunnel. A single tunnel supports multiple sessions. Each session must specify a service type (service_type) for different device access purposes. For information about session usage and lifecycle, see Session description. |
Limits
| Limit | Description | Limit |
| Secure tunnel | The maximum number of secure tunnels that an instance can have. | 1,000 |
| The maximum number of secure tunnels that a device can have. | 10 | |
| The maximum duration a secure tunnel can remain open after it is created. Note The secure tunnel is forcibly shut down after this period. A shut-down secure tunnel cannot be reopened. |
24 hours | |
| The maximum duration a secure tunnel can be retained after it is created. Note The secure tunnel is automatically deleted by the system after this period. |
30 days | |
| Secure tunnel session | The maximum number of sessions that a secure tunnel can have. | 10 |
| Data transfer rate | The maximum data transfer rate supported by a single secure tunnel. Note Secure tunnels use a traffic shaping mechanism to limit the data transfer rate. When the rate reaches the upper limit, tunnel frames are transmitted with a delay. Control the rate at which you send data. For more information about tunnel frames, see Communication data format. |
100 Kbps |
Device access permissions
Secure tunnels for IoT Platform devices can only be created by your current Alibaba Cloud account. If a third party is the actual user of a device managed by your IoT Platform instance, you must obtain valid and legal authorization from that third party before you create a secure tunnel to access or control the device.
Scenarios
- Remotely log on to a Linux device using the SSH protocol.
- Diagnose and manage a remotely logged-on device from a local computer.
Usage instructions
| Flow | Description | References |
| Develop the device and access clients | Develop the required features for the device and access clients based on the usage method and communication protocol. | |
| Use the secure tunnel |
|
Add a secure tunnel |
Related APIs
API | Description | Support for MQTT instances |
Creates a secure tunnel. | No. | |
Closes an open secure tunnel. | ||
Deletes a closed secure tunnel. | ||
Queries the details of a specific secure tunnel. Details include the associated device, creation time, ID, and connection status. |