Create a custom policy for Managed Service for OpenTelemetry
The system policies provided by Managed Service for OpenTelemetry are coarse-grained. If the system policies cannot meet your requirements, you can create custom policies to implement fine-grained access control. For example, if you need to grant the permissions on a specific application to a RAM user, you must create a custom policy instead.
How policies work
A custom policy is a JSON document with one or more statements. Each statement combines three elements:
| Element | Purpose | Example values |
|---|---|---|
| Effect | Allow or deny access | Allow, Deny |
| Action | The operation to control | xtrace:ReadXtraceApp |
| Resource | The target resource scope | acs:xtrace:cn-hangzhou:*:xtrace/* |
Available actions
| Action | What it controls |
|---|---|
xtrace:Describe* | Coarse-grained read-only permissions. Required for any RAM user who needs to use the Managed Service for OpenTelemetry console. |
xtrace:ReadXtraceApp | Read-only permissions to view applications, application details, and API call details. You can use this action to control RAM permissions on applications and regions. |
xtrace:SaveXtraceAppConfig | Permissions to save application configurations. |
xtrace:DeleteXtraceApp | Permissions to delete applications. |
Resource format
acs:xtrace:<region-id>:*:xtrace/<app-name>| Placeholder | Description | Examples |
|---|---|---|
<region-id> | Region ID, or * for all regions | cn-hangzhou, * |
<app-name> | Application name, * for all applications, or a prefix with wildcard | my-app, *, k8s* |
Prerequisites
Before you begin, make sure that you have:
A basic understanding of RAM policy elements, structure, and syntax. For details, see Policy elements
A RAM user that does not have
AliyunTracingAnalysisFull-AccessorAliyunTracingAnalysisReadOnlyAccessattached
A RAM user cannot have both a system policy and a custom policy for Managed Service for OpenTelemetry at the same time. Remove any existing system policy before you attach a custom policy.
Step 1: Create the policy
Sign in to the RAM console as a RAM user who has administrative rights.
In the left-side navigation pane, choose Permissions > Policies.
On the Policies page, click Create Policy.
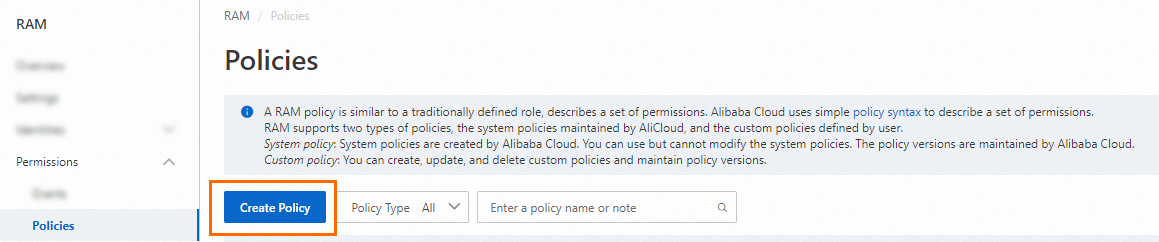
On the Create Policy page, click the JSON tab and enter your policy in the editor.
Example 1: Read-only access to all applications in a single region
This policy grants read access to all applications in the China (Hangzhou) region.
{ "Version": "1", "Statement": [ { "Action": "xtrace:ReadXtraceApp", "Resource": "acs:xtrace:cn-hangzhou:*:xtrace/*", "Effect": "Allow" }, { "Action": "xtrace:Describe*", "Resource": "*", "Effect": "Allow" } ] }xtrace:ReadXtraceAppscoped to all applications (xtrace/*) incn-hangzhouxtrace:Describe*on all resources -- required for console access
Example 2: Read-only access to applications with a name prefix
This policy restricts read access to applications whose names start with "demo" in the China (Hangzhou) region.
{
    "Version": "1",
    "Statement": [
        {
            "Action": "xtrace:ReadXtraceApp",
            "Resource": "acs:xtrace:cn-hangzhou:*:xtrace/demo*",
            "Effect": "Allow"
        },
        {
            "Action": "xtrace:Describe*",
            "Resource": "*",
            "Effect": "Allow"
        }
    ]
}
The only difference from Example 1 is the resource path:
xtrace/demo*limits access to applications with thedemoprefix.Example 3: Read and write access to a specific application
This policy grants read and configuration access to a single application named
prod-paymentin the China (Hangzhou) region, while denying delete access.{ "Version": "1", "Statement": [ { "Action": [ "xtrace:ReadXtraceApp", "xtrace:SaveXtraceAppConfig" ], "Resource": "acs:xtrace:cn-hangzhou:*:xtrace/prod-payment", "Effect": "Allow" }, { "Action": "xtrace:Describe*", "Resource": "*", "Effect": "Allow" }, { "Action": "xtrace:DeleteXtraceApp", "Resource": "*", "Effect": "Deny" } ] }ReadXtraceAppandSaveXtraceAppConfigscoped to a single applicationAn explicit
Denystatement prevents accidental deletion of any application
Click Optional advanced optimize, then click Perform to optimize the policy. The optimization:
Splits resources or conditions that are incompatible with the specified actions
Narrows down resource scopes
Deduplicates and merges statements
Click OK.
In the Create Policy dialog box, enter a Name and Description for the policy, then click OK.
Step 2: Attach the policy to a RAM user
Sign in to the RAM console as a RAM administrator.
In the left-side navigation pane, choose Identities > Users.
On the Users page, find the target RAM user and click Add Permissions in the Actions column. > Tip: To grant permissions to multiple RAM users at once, select the users and click Add Permissions at the bottom of the page.
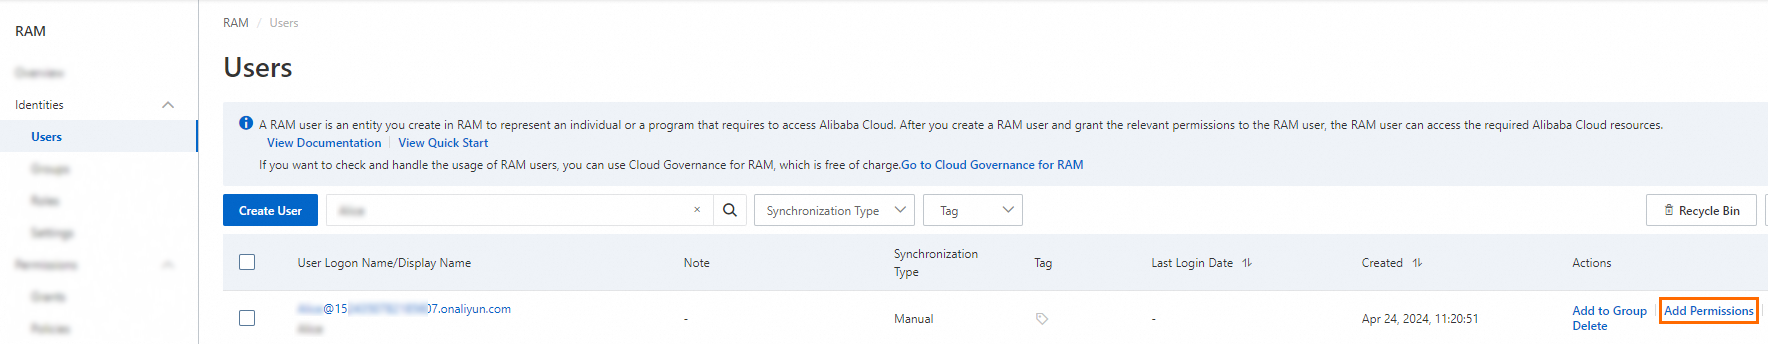
In the Grant Permission panel, configure the following settings:
Resource Scope -- Choose the authorization scope: > Important: If you select ResourceGroup, the target cloud service must support resource groups. For details, see Services that work with Resource Group. For more information about how to grant permissions on a resource group, see Use a resource group to grant a RAM user the permissions to manage a specific ECS instance.
Account: The policy applies to all resources under the current Alibaba Cloud account.
ResourceGroup: The policy applies only to resources in a specific resource group.
Principal -- Verify that the correct RAM user is selected. The current user is pre-selected by default.
Policy -- A policy contains a set of permissions. Policies can be classified into system policies and custom policies. You can select multiple policies at a time. > Note: The system flags high-risk system policies such as
AdministratorAccessandAliyunRAMFullAccess. Avoid attaching these policies unless strictly necessary.System policies: Policies created by Alibaba Cloud. You can use but cannot modify these policies. Version updates are maintained by Alibaba Cloud. For more information, see Services that work with RAM.
Custom policies: You can manage and update custom policies based on your business requirements. You can create, update, and delete custom policies. For more information, see Create a custom policy.
Click Grant permissions.
Click Close.
What's next
Policy elements -- Learn more about policy syntax and advanced features such as conditions.
Create a custom policy -- Explore additional policy authoring methods.
Services that work with RAM -- View the full list of Alibaba Cloud services that support RAM access control.