Grant DTS access to cloud resources
Before you set up a disaster recovery instance group for ApsaraDB RDS for SQL Server for the first time, you must create a RAM role named AliyunDTSDefaultRole and attach the AliyunDTSRolePolicy system policy to the role. This allows DTS to access your ApsaraDB RDS and DTS cloud resources to set up and manage the disaster recovery instance group. This authorization ensures the ApsaraDB RDS disaster recovery feature functions correctly and does not affect the performance of your ApsaraDB RDS instances.
If you log in to the RAM console with your Alibaba Cloud account and find that the required permissions are already granted, you can skip this topic and proceed to set up a disaster recovery instance group.
Prerequisites
-
You have registered an Alibaba Cloud account.
-
You must use an Alibaba Cloud account to perform the authorization.
Permission policy
The AliyunDTSRolePolicy system policy is attached to the AliyunDTSDefaultRole default role and grants management permissions for specific cloud resources such as ApsaraDB for RDS, ECS, PolarDB, ApsaraDB for MongoDB, ApsaraDB for Redis, PolarDB-X, DataHub, and Elasticsearch. For details about this policy, see AliyunDTSRolePolicy.
For more information about permission policies, see Policy syntax and structure.
Method 1: Use the quick authorization link (Recommended)
Log in to the Alibaba Cloud console with your Alibaba Cloud account and visit the quick authorization page for AliyunDTSDefaultRole, and in the dialog box that appears, click Confirm Authorization. A success message indicates that the authorization is complete.
The authorization page uses the AliyunDTSRolePolicy system policy.
Method 2: Authorize in the RAM console
-
Find the default role.
-
Log on to the RAM console with your Alibaba Cloud account.
-
Optional: In the left-side navigation pane, go to .
-
In the search box to the right of Create Role, enter AliyunDTSDefaultRole and search.
NoteIf the AliyunDTSDefaultRole role does not exist, use Method 1.
-
-
In the search results, click AliyunDTSDefaultRole.
-
Grant precise permissions to the target RAM role.
-
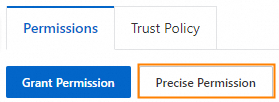
On the Permissions tab, click Precise Permission.
-
Optional: In the Precise Permission panel, set Type to System Policy.

-
In the Policy Name text box, enter AliyunDTSRolePolicy.
-
Click OK.
On the right side of the Permissions tab, click the
 icon to refresh the page and check whether the authorization succeeded.
-
-
After the precise authorization succeeds, click Close.
Verify authorization
You can follow these steps to verify that the default role has the correct permissions.
-
Log on to the RAM console with your Alibaba Cloud account.
-
Optional: In the left-side navigation pane, go to .
-
In the search box to the right of Create Role, enter AliyunDTSDefaultRole and search.
-
In the search results, click AliyunDTSDefaultRole.
-
View the details of the AliyunDTSDefaultRole role.
-
The AliyunDTSDefaultRole role is correctly authorized if it meets the following two conditions:
-
The Trust Policy contains
dts.aliyuncs.com.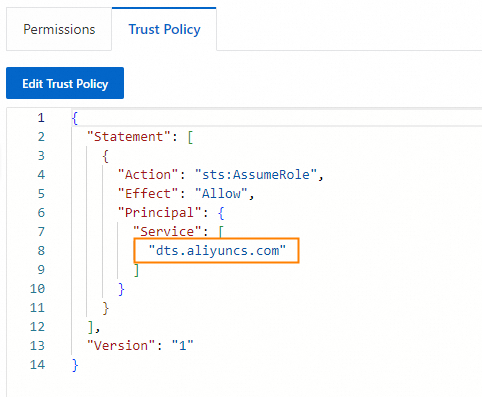
-
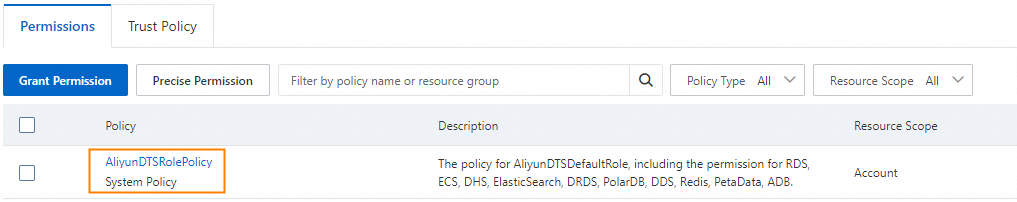
The Permissions tab contains the AliyunDTSRolePolicy system policy.
-
-
If the AliyunDTSDefaultRole role does not meet these conditions, authorization has failed. You must grant the permissions again.
You can delete the AliyunDTSDefaultRole role and grant the permissions again.
Note-
Use Method 1.
-
For information about how to delete a RAM role, see Delete a RAM role.
-
-