Configure multi-account log collection for Log Audit Service
Log Audit Service integrates with Alibaba Cloud Resource Directory to collect logs from Alibaba Cloud services across multiple Alibaba Cloud accounts. This topic describes how to configure multi-account log collection for Log Audit Service using the console and Terraform.
Background information
Resource Directory (RD) is an Alibaba Cloud service that provides multi-level account and resource relationship management for enterprises. Log Audit Service integrates with Resource Directory. You can use a management account or a delegated administrator account to add other Alibaba Cloud accounts in your enterprise as members. This lets you collect logs from Alibaba Cloud services across different accounts. For more information about Resource Directory, see What is Resource Management.
Workflow
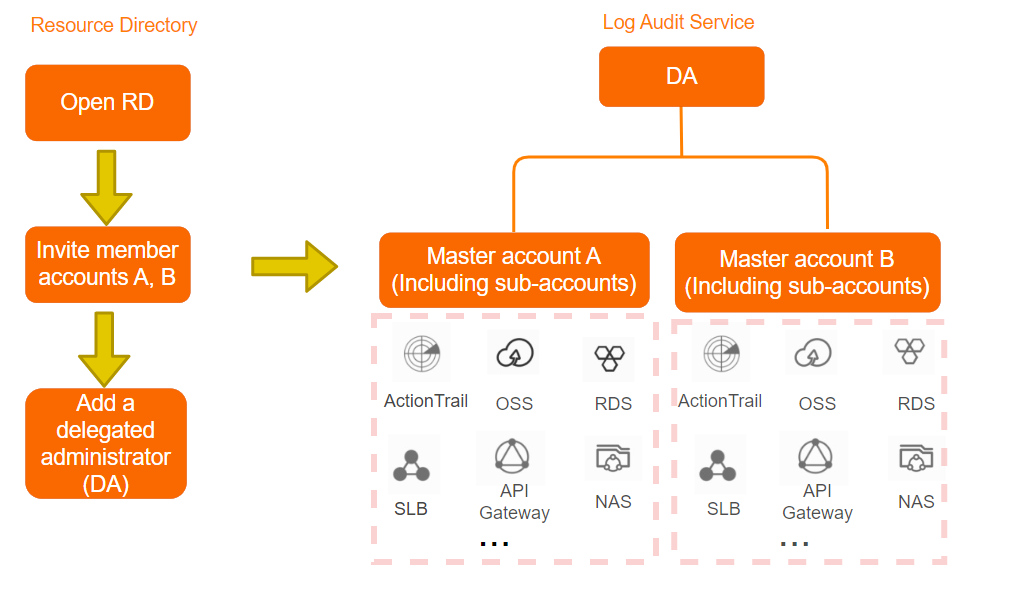
To collect logs from Alibaba Cloud services across multiple accounts, you must perform operations in both Resource Directory and Log Audit Service. This topic focuses on configuring multi-account collection in Log Audit Service. For information about other operations, see the relevant documentation.
Resource Directory
Enable Resource Directory. For more information, see Enable a resource directory.
Invite member accounts. For more information, see Create a member or Invite an Alibaba Cloud account to join a resource directory.
Designate a delegated administrator account. For more information, see Add a delegated administrator account.
Log Audit Service
You can perform the following operations in the Simple Log Service console or using Terraform.
Use a management account or a delegated administrator account to configure multi-account log collection in Log Audit Service.
Enable log collection for the target Alibaba Cloud services. For more information, see Enable and manage log collection.
Benefits
Managing multiple accounts using Resource Directory provides the following benefits.
Establishes trust relationships between accounts.
This feature helps establish trust relationships between Alibaba Cloud accounts for auditing scenarios.
Creates new accounts using the Resource Directory system.
This avoids the complex process of manually creating Alibaba Cloud accounts and completing identity verification.
Invites existing Alibaba Cloud accounts to join the organization.
If your enterprise already has Alibaba Cloud accounts, you can invite them to join your Resource Directory organization.
Builds a directory structure based on your business environment.
This feature enables automatic discovery of multiple accounts within your organization by subscribing to Resource Directory groups.
Builds a tree-like organizational structure for multiple accounts.
You can group and manage accounts by application, environment, team, or any other business unit that is meaningful to your operations to create a tree-like organizational structure.
Creates service-linked roles for integrated products in the member accounts of the organization.
This prevents RAM roles from being modified, whether intentionally or unintentionally.
Supports designating a delegated administrator in the cloud service.
Using a delegated administrator account, you can separate organization management tasks from business management tasks. The management account performs organization management tasks in Resource Directory.
Configure using the console
Log on to the Simple Log Service console using a delegated administrator account or a management account.
Go to the Log Audit Service page.
NoteAs of January 21, 2025, the console entry point for Log Audit Service has been removed. However, it is still visible to existing users who activated the service before January 21, 2025. New users who need to use the old version can access the Log Audit Service (New Version) and use the Back to Old Version feature.
In the Log Application area, on the Audit & Security tab, click Log Audit Service (New Version).
In the upper-right corner of the New Log Audit page, click Back to Old Version to continue using the features of Log Audit (Old Version).
In the navigation pane on the left, choose .
On the Resource Directory Management Mode tab, click Modify.
In the Add Account panel, select the destination accounts and click Confirm.
The Resource Directory management mode supports the All Members and Custom modes. For more information, see Resource Directory management mode (recommended).
Mode
Description
All Members
Log Audit Service automatically adds all members in the Resource Directory to the collection list and collects logs from the Alibaba Cloud services for which log collection is enabled in these member accounts.
When a new member is added to the Resource Directory, the member is automatically added to the collection list.
When a member is removed from the Resource Directory, the member is automatically removed from the collection list.
Custom
You can select specific members to add to the collection list. Log Audit Service collects logs from the Alibaba Cloud services for which log collection is enabled in these member accounts.
When a new member is added to the Resource Directory, the member is not automatically added to the collection list.
When a member is removed from the Resource Directory, if the member is in your collection list, it is automatically removed from the list.
Configure using Terraform
Terraform is an open source tool that you can use to securely and efficiently preview, configure, and manage cloud infrastructure and resources. The Terraform command-line interface (CLI) provides a simple mechanism to deploy configuration files to Alibaba Cloud or any other supported cloud and manage their versions. For more information, see Use Terraform to configure Log Audit Service.
Step 1: Create a working directory and a file
Create a Terraform working directory. For example, you can create a directory named sls.
In the directory that you created, run the following command to initialize the working directory.
terraform initCreate a file named terraform.tf.
Step 2: Configure identity information
When you use Terraform to configure multi-account collection for Resource Directory, you can use several methods for identity authentication, such as environment variables, static AccessKeys, ECS roles, and AssumeRole. For more information, see Authentication.
Method 1: Environment variables
Obtain the AccessKey pair of an Alibaba Cloud account or a RAM user. Then, configure the environment variables with the user identity and the region where the central project for Log Audit Service resides. The following example shows the configuration:
export ALICLOUD_ACCESS_KEY="AccessKey ID"
export ALICLOUD_SECRET_KEY="AccessKey secret"
export ALICLOUD_REGION="cn-huhehaote"
Method 2: Static AccessKey
Obtain the AccessKey pair of an Alibaba Cloud account or a RAM user. Then, configure the provider information in the terraform.tf file.
provider "alicloud" {
  access_key = "AccessKey ID"
  secret_key = "AccessKey secret"
  region     = "cn-huhehaote"
}
Method 3: ECS instance role
Attach a RAM role to an ECS instance. This allows the ECS instance and the applications on it to access other cloud resources based on temporary credentials from the Security Token Service (STS) without exposing your long-term AccessKey.
Create an Alibaba Cloud service role. For more information, see Create a service role.
Grant the created RAM role the permissions to access Simple Log Service. For more information, see Manage the permissions of a RAM role. For the required access policy, see Appendix: Minimum write permissions required for log auditing.
Attach the RAM role to the ECS instance. For more information, see Grant a RAM role to an instance.
Configure the provider information in the
terraform.tffile.provider "alicloud" { ecs_role_name = "your_ram_role_name" region = "cn-huhehaote" }
Method 4: Assume a RAM role
Use an Alibaba Cloud account to grant the AliyunSTSAssumeRoleAccess permission to a RAM user.
Create an Alibaba Cloud service role. For more information, see Create a RAM role for a trusted Alibaba Cloud service.
Grant the created RAM role the permissions to access Simple Log Service. For more information, see Manage the permissions of a RAM role. For the required access policy, see Appendix: Minimum write permissions required for log auditing.
Grant the AssumeRole permission to the RAM user in the trusted account. For more information, see Step 4: Grant permissions to the RAM user of Enterprise B.
Obtain a temporary security token for the RAM role. For more information, see Step 5: Obtain the temporary security token of the RAM role.
Configure the provider information in the terraform.tf file.
provider "alicloud" {
  assume_role {
    role_arn           = "acs:ram::Your_Alibaba_Cloud_Account_UID:role/sls-test"
    session_name       = "AuditRoleSession"
    session_expiration = 999
  }
}
Step 3: Configure multi-account collection
In the terraform.tf file, add the following configuration. For a description of important parameters, see Configure parameters for Log Audit Service.
resource "alicloud_log_audit" "rdtest" {
  display_name = "tf-audit-rd-test"
  aliuid = "1379186349****"
  variable_map = {
    "actiontrail_enabled" = "false",
    "actiontrail_ttl" = "180"
  }
  multi_account = ["1257918632****","1324567349****"]
  resource_directory_type="custom"
}
Step 4: Apply the collection configuration
Run the following command.
terraform applyEnter yes.
If the message
Apply complete!is returned, the collection configuration is applied. Log Audit Service then collects and stores logs based on the configuration.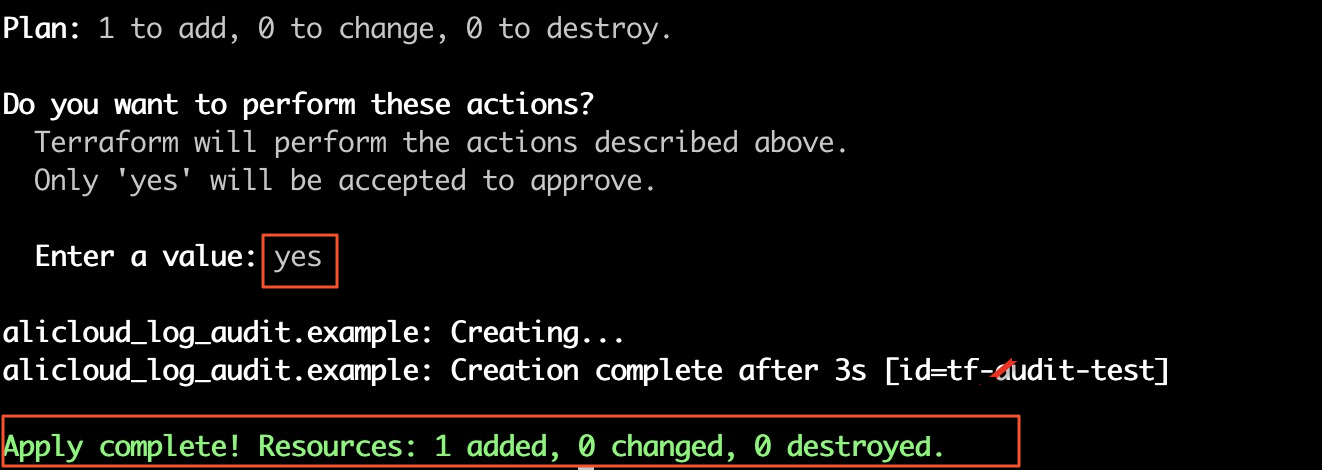
Appendix: Minimum write permissions required for log auditing
The following access policy grants the minimum permissions required to use Log Audit Service.
{
    "Version": "1",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "log:GetApp",
                "log:CreateApp"
            ],
            "Resource": [
                "acs:log:*:*:app/audit"
            ]
        },
        {
            "Effect": "Allow",
            "Action": [
                "log:Get*",
                "log:List*",
                "log:CreateJob",
                "log:UpdateJob",
                "log:CreateProject"
            ],
            "Resource": [
                "acs:log:*:*:project/slsaudit-*"
            ]
        }
    ]
}