Create and authorize a RAM role for an Alibaba Cloud service
A RAM role for an Alibaba Cloud service is used to authorize cross-service access. This topic describes how to create a RAM role for an Alibaba Cloud service and grant permissions to the role.
Step 1: Create a RAM role
Create a Cloud Service RAM role and set the trusted service to Simple Log Service.
Log on to the RAM console as a RAM user who has administrative rights.
In the navigation pane on the left, choose .
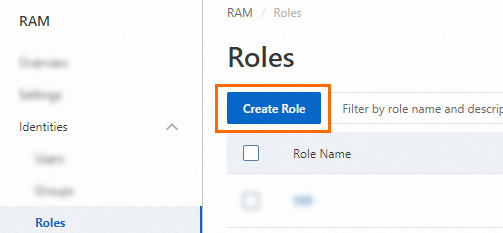
On the Roles page, click Create Role.
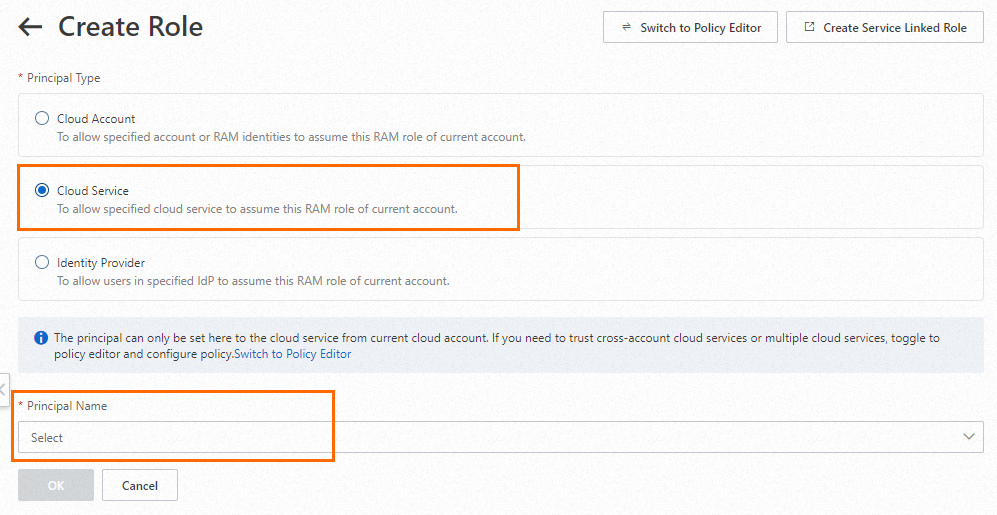
On the Create Role page, set Principal Type to Cloud Service, select an Alibaba Cloud service for the Principal Name parameter, and then click OK.
 Note
Available Alibaba Cloud services for the Principal Name parameter are subject to the RAM console.
Step 2: Grant permissions to the RAM role
A RAM role has no permissions when it is created. You must grant permissions to the role. RAM provides the following two system policies for Simple Log Service. Based on the principle of least privilege, grant only the required permissions to the RAM role.
AliyunLogFullAccess: Grants full permissions to manage Simple Log Service.
AliyunLogReadOnlyAccess: Grants the read-only permissions on Simple Log Service.
If the system policies do not meet your requirements, you can create a custom policy for fine-grained permission management. For more information, see Create a custom policy. For examples of permission policies, see Examples of custom RAM authorization and RAM authorization policies for Simple Log Service.
Log on to the RAM console as a RAM administrator.
In the left-side navigation pane, choose .
On the Roles page, find the RAM role that you want to manage and click Grant Permission in the Actions column.
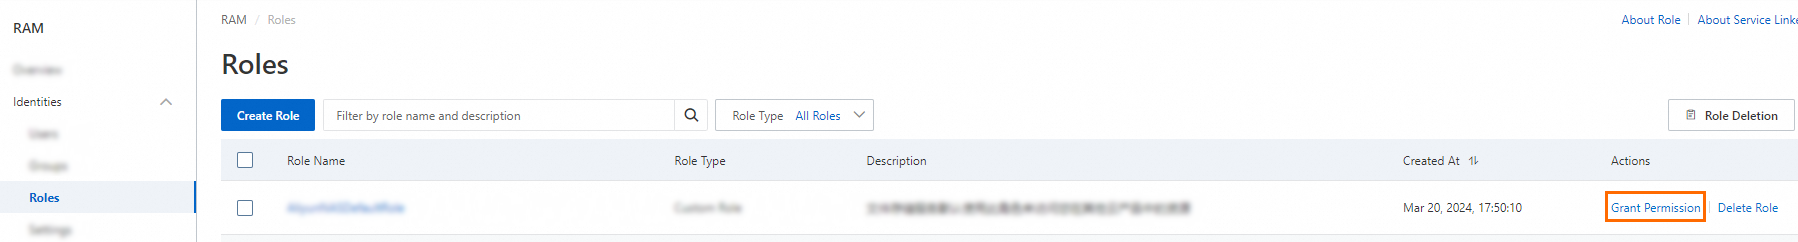
You can also select multiple RAM roles and click Grant Permission in the lower part of the RAM role list to grant permissions to multiple RAM roles at a time.
In the Add Permissions panel, select the target policy, such as AliyunLogReadOnlyAccess, and click OK.
Click Close.