Kubernetes Ingress log center
The Alibaba Cloud Kubernetes Ingress component provides externally accessible URLs, load balancing, Secure Sockets Layer (SSL) connections, and name-based virtual hosts. It also logs all HTTP requests to standard output. Simple Log Service (SLS) provides the Ingress log center feature to help you analyze and monitor services connected to the Ingress backend. This topic describes the features, advantages, assets, billing, and limits of the Ingress log center.
Product trial
The Ingress log center demo in the SLS Playground includes demo data, visualization charts, and other resources. The demo provides a complete environment where you can quickly explore and experience the feature.
Click Ingress log center to try it out.
The data in the SLS Playground is for demonstration only. Do not use it in a production environment.
Features
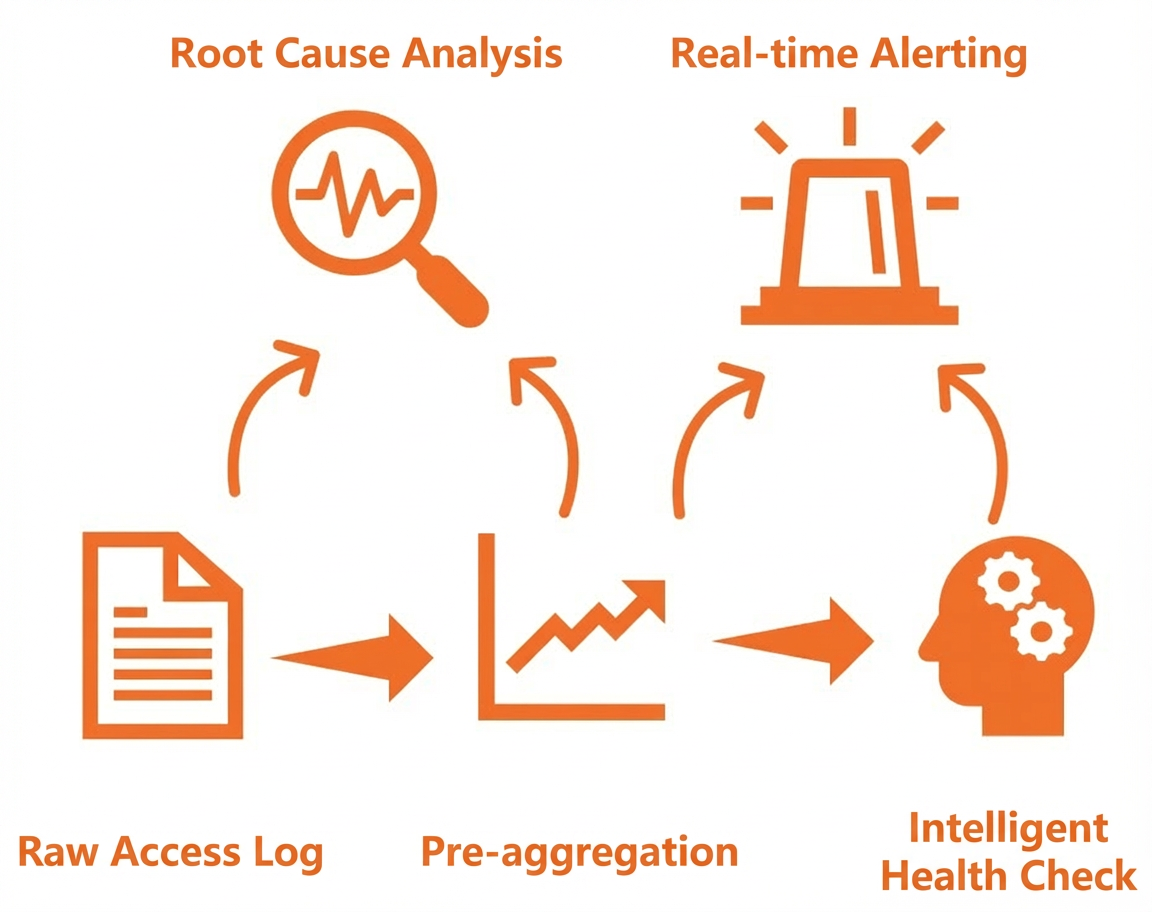
The Ingress log center automatically aggregates real-time access logs and provides features such as intelligent health checks and real-time alerting.
Collects, stores, queries, and analyzes real-time access logs.
Extracts various metrics from raw access logs in real time. These metrics include page views (PV), request success rate, average latency, P50/P99/P9999 latency, and inbound and outbound traffic. It supports aggregation by multiple dimensions, such as host and status.
Provides rich visualization reports, including monitoring dashboards, anomaly reports, and operations dashboards. It supports report subscriptions by email and through DingTalk groups.
Provides an intelligent health check feature that supports global and service-level checks. It also annotates anomalies directly in visualization reports.
Supports custom alert configurations. Alert notifications can be sent to Message Center, email, text messages, voice calls, and DingTalk. It also supports integration with custom webhooks.
Advantages
Simple: Enjoy a one-stop, centralized experience. You do not need to manage log collection, storage, computing, or visualization. This frees developers and O&M engineers from complex log processing, allowing them to focus on business development and technical exploration.
Massive data processing: The volume of access logs is proportional to the Ingress request PV and can be very large. Processing access logs requires you to consider performance and cost. The log center provides a pre-aggregation feature to compute aggregated metrics in real time. The resulting aggregated data is several orders of magnitude smaller, which greatly improves query speed.
Real-time analysis: Scenarios such as DevOps, monitoring, and alerting require real-time log data. The log center uses the powerful big data computing capabilities of SLS to analyze logs in seconds.
Elastic: You can set any log storage period. The Logstore capacity uses dynamic scaling to accommodate business growth.
Intelligent: Based on intelligent AIOps algorithms from Alibaba DAMO Academy, this feature provides automatic health checks for various metrics. This helps you discover and locate issues faster and more accurately.
Assets
The selected project contains the following assets:
Logstore
The access log Logstore stores Kubernetes Ingress access logs. You create this Logstore.
The indexing feature is enabled by default for this Logstore, and indexes are configured for some fields. You can add indexed fields. Changes to indexes take effect only on new data. You can also reindex historical data. For more information, see Reindex logs.
You can change the log storage period. For more information, see Modify Logstore configurations.
The inspection result Logstore stores inspection results. This dedicated Logstore is automatically generated after you enable the log center feature. Its name is access log Logstore name-metrics-result.
ImportantDo not delete the Logstore for Kubernetes Ingress access logs. Otherwise, logs cannot be collected into SLS.
Do not delete the indexes of specific fields in the access log Logstore. If you delete the indexes, metric transformation fails.
Metricstore
The Metricstore stores aggregated metric information. This dedicated Metricstore is automatically generated after you enable the log center feature. Its name is access log Logstore name-metrics.
NoteThe Metricstore stores aggregated metrics. The data volume is greatly reduced compared to raw access logs, making it suitable for long-term storage.
Aggregation rules
Rule name
Time granularity
Aggregation dimension
Generated metrics
total
10 seconds
total
pv
body_bytes_sent_avg
body_bytes_sent_sum
request_length_avg
request_length_sum
upstream_response_time_avg
upstream_response_time_p50
upstream_response_time_p90
upstream_response_time_p99
upstream_response_time_p9999
request_time_avg
request_time_p50
request_time_p90
request_time_p99
request_time_p9999
host
10 seconds
host
pv:host
body_bytes_sent_avg:host
body_bytes_sent_sum:host
request_length_avg:host
request_length_sum:host
upstream_response_time_avg:host
upstream_response_time_p50:host
upstream_response_time_p90:host
upstream_response_time_p99:host
upstream_response_time_p9999:host
request_time_avg:host
request_time_p50:host
request_time_p90:host
request_time_p99:host
request_time_p9999:host
host_status
10 seconds
host+status
pv:host:status
body_bytes_sent_avg:host:status
body_bytes_sent_sum:host:status
request_length_avg:host:status
request_length_sum:host:status
upstream_response_time_avg:host:status
upstream_response_time_p50:host:status
upstream_response_time_p90:host:status
upstream_response_time_p99:host:status
upstream_response_time_p9999:host:status
request_time_avg:host:status
request_time_p50:host:status
request_time_p90:host:status
request_time_p99:host:status
request_time_p9999:host:status
Inspection rules
Rule name
Enabling status
Inspection algorithm
Inspection metrics
total
Enabled by default
Time2Graph
pv
body_bytes_sent_avg
body_bytes_sent_sum
request_length_avg
request_length_sum
upstream_response_time_avg
request_time_avg
host
Enabled by default
Time2Graph
pv:host
body_bytes_sent_avg:host
body_bytes_sent_sum:host
request_length_avg:host
request_length_sum:host
upstream_response_time_avg:host
request_time_avg:host
host_status
Disabled by default
Time2Graph
pv:host:status
body_bytes_sent_avg:host:status
body_bytes_sent_sum:host:status
request_length_avg:host:status
request_length_sum:host:status
upstream_response_time_avg:host:status
request_time_avg:host:status
Dedicated dashboards
Dashboard
Associated Logstore or Metricstore
Description
Operations dashboard
access log Logstore name
Displays information related to user requests, including PV, UV, mobile distribution, and country/province/city distribution.
NoteThis information is calculated based on the full amount of raw access logs. There may be some delay when the data volume is extremely large.
Overview
access log Logstore name-metrics
Displays overall monitoring information of Kubernetes, including PV, failure rate, 5XX ratio, status code distribution, and traffic.
Monitoring dashboard
access log Logstore name-metrics
Supports filtering detailed monitoring information of instances by dimensions such as host and status.
Anomalies
access log Logstore name-metrics
access log Logstore name-metrics-result
Displays service-level anomalous information detected by the stream inspection algorithm, including anomaly statistics and real-time display of specific metrics anomalies.
Billing
SLS charges for storage space, read traffic, the number of requests, data transformation, and data shipping. For more information, see Billable items of pay-by-feature.
Limits
Ingress logs must be successfully parsed before you can configure time series transform rules and inspection rules. For custom Ingress access log formats, you must manually configure parsing rules. The corresponding log field names must follow the default naming convention.
After you configure the log center, the configuration takes effect only on new logs. Existing logs are not converted into metrics.