What is IoT Security Operation Center (This document is no longer maintained)
This topic describes the basic features of IoT Security Operation Center.
Introduction
IoT Security Operation Center (SOC) is a unified security management system for Internet of Things (IoT) assets. It provides features such as network-wide asset mapping, comprehensive security detection, and real-time security protection. This creates a closed-loop security operations cycle that makes IoT assets visible, understandable, and manageable.
Service architecture
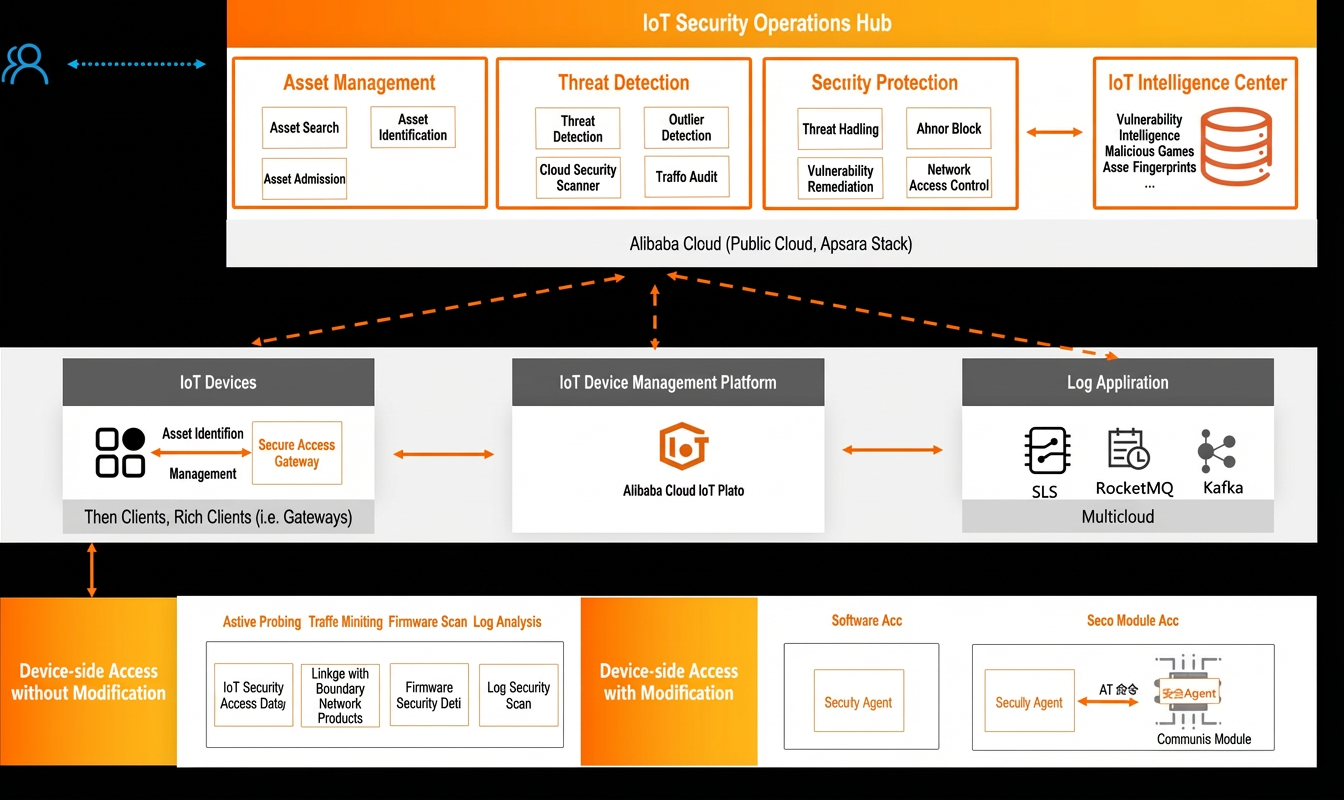
Features
Asset management and control
Comprehensively and accurately discover and identify all types of IoT devices. The service provides network-wide asset mapping to improve the efficiency and accuracy of device asset inventory.
Device asset discovery: Comprehensively and promptly discover device assets through various connection types. This ensures a complete inventory of all assets on your network.
Device asset identification: Quickly and accurately identify device asset information, such as category, manufacturer, and model, based on a powerful Asset Fingerprints library.
Device asset admission: Build a trusted asset checklist to automatically identify and block unauthorized device access.
Security detection
Monitor the security of device assets in real time using a wide range of security risk detection policies.
Security posture: Visualize device security through dashboards and reports. These tools provide information about threats, vulnerabilities, and security statistics to improve administration efficiency.
Threat alerts: Comprehensively discover threats using dozens of detection templates for issues such as identity leaks, malicious files, and high-risk commands.
Abnormal behavior detection: Automatically detect abnormal behaviors related to system objects, processes, and network access.
Vulnerability scan: Identify all vulnerabilities in systems and components based on a powerful IoT vulnerability intelligence database. You can follow the vulnerability remediation guide to fix them.
Firmware detection: Identify various risks in firmware, such as vulnerabilities, configuration risks, and information leaks. The service provides detection reports and recommendations.
Classified protection compliance check: Meet classified protection compliance requirements with specialized checks based on the IoT extension for classified protection.
Security protection
Build security protection policies to protect device assets in real time. This includes capabilities such as blocking abnormal activities, fixing vulnerabilities, and locking down behaviors.
Abnormal activity blocking: Set security policies to prohibit unsafe device behaviors, such as preventing a device from accessing a specific IP address or URL.
Vulnerability remediation: Use the remediation feature to eliminate device vulnerabilities. This prevents attackers from exploiting them to launch attacks.
Threat alerting: Customize threat alert policies to push alert information through email or webhooks.
Continuous upgrades
Receive the latest security intelligence and features to ensure continuous security detection and protection for all device assets within your scope.
Security intelligence upgrades: The intelligence library and Asset Fingerprints library are continuously updated. Security models are also continuously updated through self-learning by an AI engine to improve detection and protection.
Protocol analysis upgrades: The audit and control capabilities for various industry protocols, such as video and industrial control protocols, are continuously enhanced. This continuously improves all types of security detection and protection capabilities.
Security feature upgrades: The latest security features are continuously provided through modular security capabilities.
Benefits
Flexible connection types
The service supports both proxy (for modifiable devices) and proxyless (for non-modifiable devices) connection types. These include various security connection methods such as a security SDK, firmware detection, log ingestion, and probe scanning.
Rich detection capabilities
The service covers a wide range of security detection types, such as vulnerabilities, network access, process behavior, and file anomalies. It supports dozens of major IoT threat models and IoT device classified protection check items. This multi-dimensional, comprehensive detection ensures full coverage for IoT risk detection.
Closed-loop response and handling
Building on comprehensive security detection, the service provides complete handling capabilities, such as abnormal activity blocking, network access control, and threat handling. It also works with security devices such as firewalls to shorten the response and handling cycle, quickly reduce the attack surface, and meet the requirements for closed-loop security management.
Multiple deployment forms
In addition to delivery as a public cloud service or an all-in-one IoT security management appliance, the service also supports on-premises deployment in Apsara Stack, on bare metal servers, or in container environments.
Scenarios
Device asset mapping and security management
Security administrators in an enterprise can obtain a clear overview of device assets in their managed areas. They can fully understand the overall security posture and promptly take security measures to prevent security risk incidents.
Comprehensive identification and risk management for video security terminals
As a key part of digital infrastructure, the security management and control of video security terminals such as IPCs and NVRs are critical. IoT Security Operation Center provides comprehensive protection for these terminals and their corresponding scenarios, such as traffic, traffic police, and campus environments. This enables comprehensive management that is discoverable, identifiable, and detectable.
Full lifecycle protection for consumer terminals
The service provides comprehensive real-time monitoring of the runtime of consumer terminals, such as facial payment terminals and smart POS machines. It detects risky behaviors to prevent financial loss for consumers.
Secure development and security self-checks
Use the security self-check feature provided by IoT Security Center to identify potential security threats, obtain remediation suggestions, and implement security protection.
During device development, developers of IoT devices or gateways can integrate the security SDK to perform security self-checks. After completing firmware and application development, they can also use the firmware security detection feature to perform a security self-check on the IoT device or gateway.