Troubleshoot domain ownership verification issues
After you submit a certificate application, you must cooperate with the Certificate Authority (CA) to complete domain ownership verification. The Apply for Certificate provides an auxiliary domain verification feature that helps you identify and resolve issues during the verification process in advance, reducing the likelihood of CA verification failures. This topic describes common issues and solutions that may occur during domain verification.
Common DV certificate verification issues
DV certificates support three domain verification methods: manual DNS verification, file verification, and automatic verification. You can find the corresponding solution based on the verification method you are using.
Manual DNS verification
How do I check if a DNS record has taken effect?
What should I do if the console displays "No DNS record found."?
What should I do if the console displays "Mismatch found in the DNS record."?
What should I do if the console displays "Verification timed out, please try again"?
File verification
What should I do if the console displays "No file found."?
What should I do if the console displays "Verification timed out, please try again"?
Common causes and solutions are as follows:
-
Port 80 or 443 is not open on the server.
The CA center can only verify the file content by accessing HTTPS Address and HTTP Address (port 443 and port 80, respectively).
Solution 1: Open port 80 or 443.
Linux
Run the following command in the server terminal to check whether port 443 is open:
RHEL/CentOS
command -v nc > /dev/null 2>&1 || sudo yum install -y nc
# Replace <your_server_public_ip_address> with the public IP address of your server.
sudo ss -tlnp | grep -q ':443 ' || sudo nc -l 443 & sleep 1; nc -w 3 -vz <your_server_public_ip_address> 443
If the output contains
Ncat: Connected to <your_server_public_ip_address>:443, port 443 is open. Otherwise, you must open port 443 in the security group and firewall.Debian/Ubuntu
command -v nc > /dev/null 2>&1 || sudo apt-get install -y netcat
# Replace <your_server_public_ip_address> with the public IP address of your server.
sudo ss -tlnp | grep -q ':443 ' || sudo nc -l -p 443 & sleep 1; nc -w 3 -vz <your_server_public_ip_address> 443
If the output contains
Connection to <your_server_public_ip_address> port [tcp/https] succeeded!or[<your_server_public_ip_address>] 443 (https) open, port 443 is open. Otherwise, you must open port 443 in the security group and firewall.Open port 443 in the security group.
ImportantIf your server is deployed on a cloud platform, make sure that its security group allows inbound traffic on TCP port 443. Otherwise, the service is not accessible from the internet. The following operations use an Alibaba Cloud ECS instance as an example. For other cloud platforms, see their official documentation.
Go to the ECS Instances page and click the name of the target instance to go to its details page. For more information, see Add a security group rule. Add a rule to the security group with Action set to Allow, Protocol Type set to TCP, Port Range set to HTTPS(443), and Authorization Object set to Anywhere (0.0.0.0/0).
Open port 443 in the firewall.
Run the following command to identify the current firewall service on your system:
if command -v systemctl >/dev/null 2>&1 && systemctl is-active --quiet firewalld; then
    echo "firewalld"
elif command -v ufw >/dev/null 2>&1 && sudo ufw status | grep -qw active; then
    echo "ufw"
elif command -v nft >/dev/null 2>&1 && sudo nft list ruleset 2>/dev/null | grep -q 'table'; then
    echo "nftables"
elif command -v systemctl >/dev/null 2>&1 && systemctl is-active --quiet iptables; then
    echo "iptables"
elif command -v iptables >/dev/null 2>&1 && sudo iptables -L 2>/dev/null | grep -qE 'REJECT|DROP|ACCEPT'; then
    echo "iptables"
else
    echo "none"
fi
If the output is
none, no further action is required. Otherwise, based on the firewall type (firewalld,ufw,nftables, oriptables), run the corresponding command to open port 443:firewalld
sudo firewall-cmd --permanent --add-port=443/tcp && sudo firewall-cmd --reloadufw
sudo ufw allow 443/tcpnftables
sudo nft add table inet filter 2>/dev/null
sudo nft add chain inet filter input '{ type filter hook input priority 0; }' 2>/dev/null
sudo nft add rule inet filter input tcp dport 443 counter accept 2>/dev/null
iptables
sudo iptables -A INPUT -p tcp --dport 443 -j ACCEPTTo prevent iptables rules from being lost after a system reboot, run the following command to make the rules persistent:
RHEL/CentOS sudo yum install -y iptables-services sudo service iptables saveDebian/Ubuntu sudo apt-get install -y iptables-persistent sudo iptables-save | sudo tee /etc/iptables/rules.v4 >/dev/null
Windows
Log on to your Windows server, click the Start menu, and then open Control Panel.
Go to .
If the firewall is turned off as shown in the following figure, no further action is required.
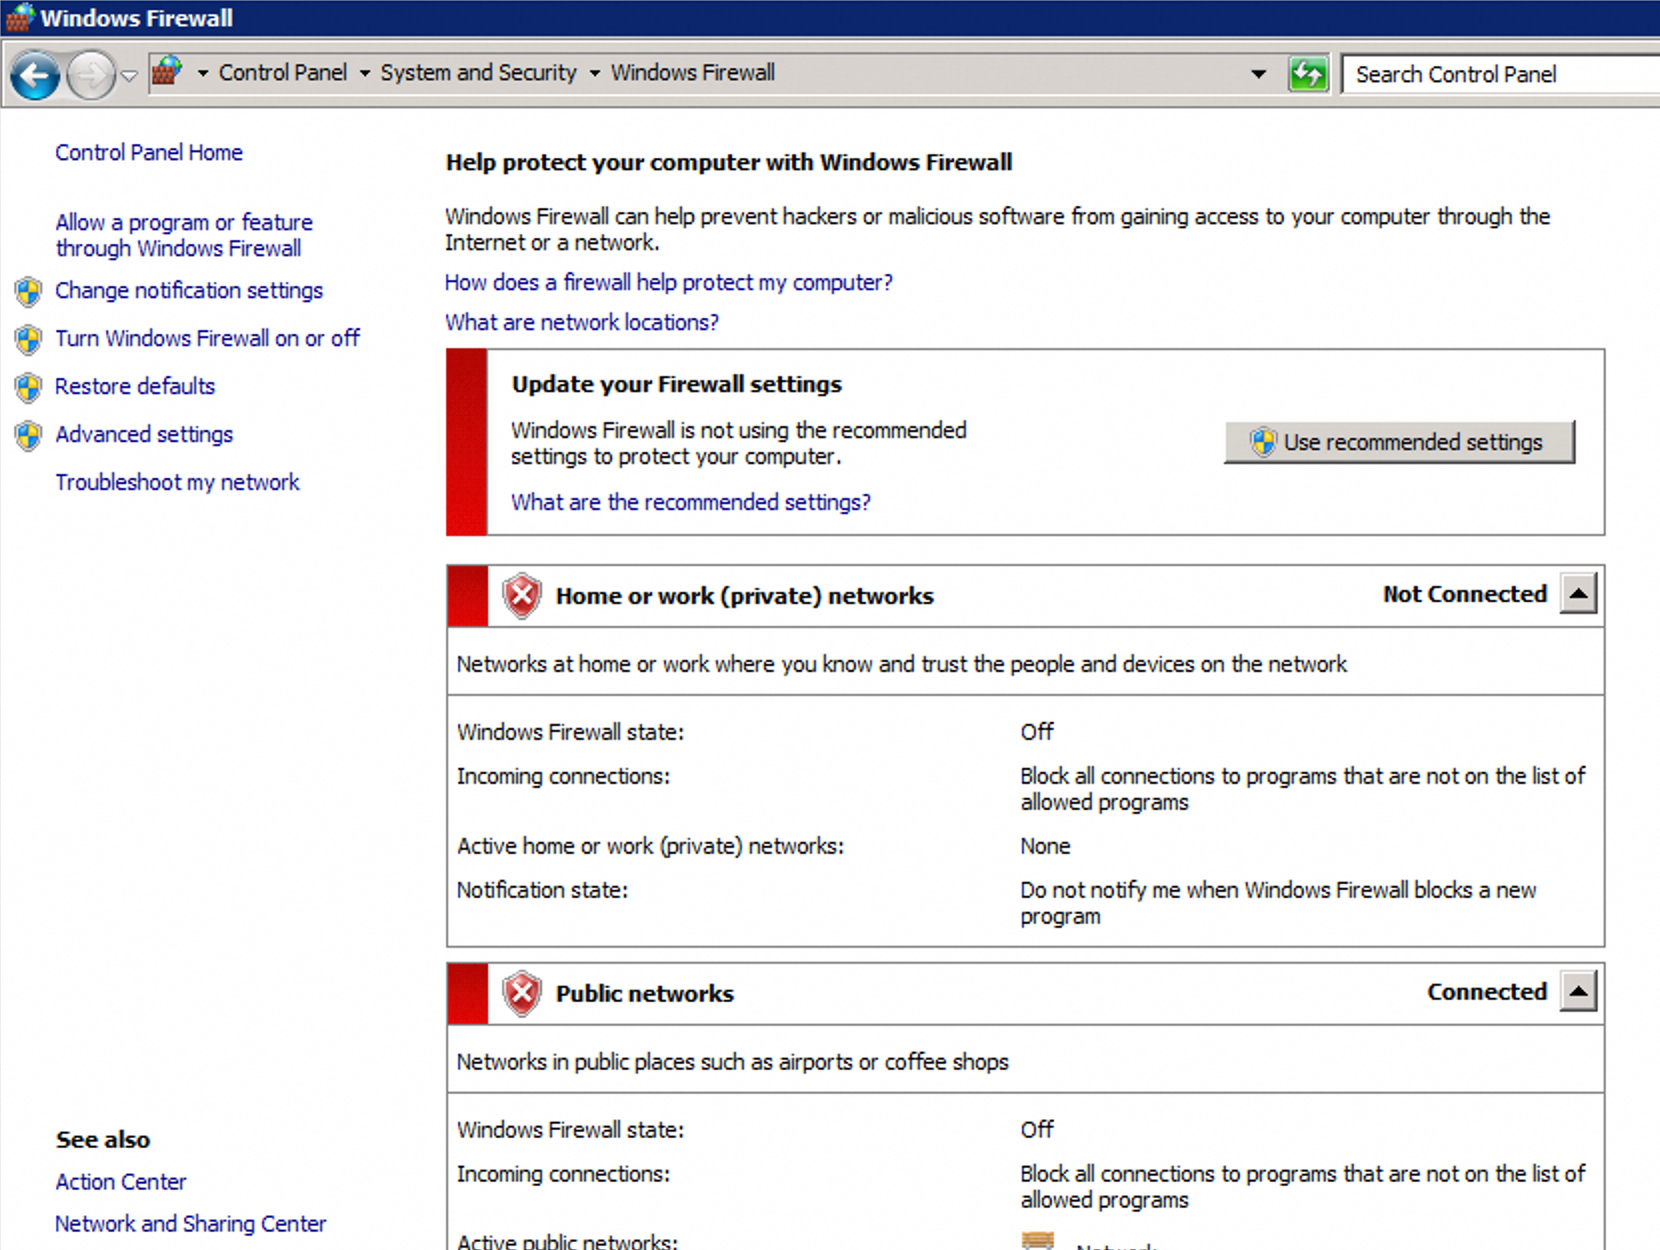
If the firewall is turned on, follow these steps to allow HTTPS traffic.
In the left-side navigation pane, click and check whether an inbound rule exists for which Protocol is TCP, Local Port is 443, and Action is Block.
If such a rule exists, right-click the rule, select Properties, and on the General tab, change the action to Allow the connection. Then, click Apply.
Solution 2: In the Apply for Certificate panel, click Cancel Application, and change the domain verification method to Manual DNS Verification.
-
A 301 or 302 redirect is configured.
-
Use the
wget -S <URL>command to check whether the verification URL has a redirect. If the response isHTTP/1.1 301 Moved PermanentlyorHTTP/1.1 302 Found, a redirect exists.wget -S http://<your_domain>/.well-known/pki-validation/<verification_file_name> -
Remove the redirect configuration. The following examples show 301 and 302 redirect configurations in the Nginx configuration file
nginx.conf.301 redirect
server {
    listen 80;
    server_name <your_root_domain> <your_www_subdomain>;
    return 301 <redirect_domain>$request_uri;
}
302 redirect
location /.well-known/ {
    return 302 <redirect_address>
}
-
-
Overseas CA IP addresses are blocked by a firewall (the website does not support overseas access).
If you apply for an international brand certificate (such as DigiCert or GlobalSign), but the website bound to the certificate domain restricts access from overseas IP addresses, you can temporarily add the CA center's IP addresses to the server whitelist.
Note-
For information about how to obtain the IP addresses of the CA center, see CA IP Addresses, or contact a technical expert. For more information, see one-on-one technical support.
-
After the certificate is issued, we recommend that you remove the configured IP whitelist to avoid issues when applying for certificates in the future.
-
-
A network exception has occurred on the domain name server.
Contact the corresponding domain name provider to check and fix the network issue.
-
The domain name applied for a free test certificate contains sensitive words.
Solution 1: Use a domain name that does not contain sensitive words (such as
edu,gov,org,jpand other country abbreviations, as well aspay,bank,live, andnuclear), and submit the application again.Solution 2: If the domain name cannot be changed, purchase an OV or EV certificate, or a vTrus (a Chinese brand) certificate.
What should I do if the console displays "Incorrect file content"?
Other causes of file verification failure
Is file verification supported for wildcard domain names?
Automatic verification
Can the automatic verification method be changed?
No. If you need to change the verification method, switch to another Alibaba Cloud account to purchase the certificate again. After the purchase, refer to Domain ownership verification to complete the domain ownership verification.
Common OV and EV certificate issues
After the CA center receives your OV or EV certificate application, it sends a domain verification email to the contact email address on file, or calls the contact phone number for verification. The following are common issues:
Can I verify by email only without answering the phone call?
Yes, but you need to reply to the email to explain the situation.
What are the verification emails and who receives them?
The CA center sends a domain verification email and an order confirmation email to the contact email address provided when the certificate was applied. For information about how to manage contacts, see Manage contacts. The email content may vary depending on the certificate brand.
Other issues
The console shows that domain verification has passed, but the certificate has not been issued?
The console verification result is for reference only. A "passed" status in the console does not mean that the CA has completed verification and issued the certificate. The actual verification and issuance result is subject to the CA center's detection. Generally, DV certificates are issued within 1 to 15 minutes, and OV or EV certificates take about 5 calendar days. The following situations may cause the certificate review to take longer:
-
The domain has a CAA record.
Solution 1: Go to the Alibaba Cloud DNS console. On the DNS configuration page for your domain, delete the DNS record with the type "CAA". After that, apply for the certificate again.
Solution 2: Add the CA corresponding to the certificate to the CAA record. After that, apply for the certificate again.
ImportantWhen you use GitHub Pages and CNAME your domain to a
github.iodomain, the CAA policy ofgithub.iois inherited, which can affect certificate issuance. To resolve this, you can pause the CNAME record before the certificate is issued, or addtrust-provider.com,globalsign.com, andsectigo.comto your CAA record. -
The domain contains sensitive words.
When a domain contains sensitive words, it may trigger a manual review mechanism, which extends the review time. Wait patiently for the manual review result. If the review fails, you can change the domain name and apply again.
-
A firewall or other security device affects CA verification.
In environments with high network isolation, such as government agencies and state-owned enterprises, CA domain ownership verification may be restricted by network limitations, causing the certificate to remain in the "reviewing" state for an extended period. To ensure the certificate is issued successfully, you need to configure a CA whitelist in your firewall or other security devices.
-
The root domain and the www subdomain are not covered in both directions.
According to CA verification requirements, regardless of whether you apply for the root domain (such as
example.com) or its www subdomain (such aswww.example.com), the CA checks both addresses simultaneously. Make sure that the verification file is publicly accessible on both domains. Otherwise, the verification will fail.
The DNS record has taken effect, but the console verification still fails?
Whether it is file verification or DNS verification, the console verification result has a certain delay. No other action is required. Wait patiently.
The console shows that domain verification has passed, but the certificate review "failed"?
The console verification result is for reference only. A "passed" status in the console does not mean that the CA has completed verification and issued the certificate. You can refer to Causes and solutions for a failed SSL certificate review for solutions.
Can I apply for an Alibaba Cloud SSL certificate if my DNS provider is not Alibaba Cloud?
Yes. You only need to complete domain ownership verification, which is independent of your DNS provider.
|
Solution |
Procedure |
Advantages |
|
Configure at the current provider |
Log on to your current domain management platform and add the SSL certificate verification record (CNAME/TXT) obtained from Alibaba Cloud. Note
If you have any questions, contact your DNS provider. |
Fast and direct. No domain transfer is required. |
|
Transfer the domain to Alibaba Cloud |
After completing the transfer by referring to Transfer a domain name to Alibaba Cloud, configure DNS resolution in the Alibaba Cloud DNS console. Important
When you transfer a domain, you need to pay a one-year renewal fee. The transfer price is the same as the one-year renewal price. |
Facilitates subsequent certificate renewals and centralized domain management. |
Can an SSL certificate be used in an internal network?
Yes. A newly applied certificate requires the CA center to complete domain ownership verification over the public network. Therefore, you need to enable public network access during the verification process. After the verification is complete, you can disable public network access. There are no restrictions on the usage environment after the certificate is issued, and it can be used normally in an internal network.