Install an SSL certificate on BT-Panel (Linux)
This topic describes how to configure an SSL certificate on BT-Panel and verify the installation. After configuration, you can securely access your application over an encrypted HTTPS channel to ensure data transmission security.
Prerequisites
You have purchased and applied for a certificate by using the SSL Certificates Service, and its Status is Issued. To purchase and apply for a certificate, see Purchase a paid certificate and Apply for a certificate.
Your domain name is correctly resolved to the current server, and you have completed the MIIT ICP filing (for servers in the Chinese mainland).
BT-Panel is installed on the server. If it is not yet installed, see the Install BT-Panel on Linux documentation.
NoteIf your server is an Alibaba Cloud ECS instance, you can quickly install BT-Panel by following the instructions in Deploy BT-Panel.
For more information about installing and using BT-Panel, visit the official BT-Panel website.
Procedure
Step 1: Download the SSL certificate and private key files
On the SSL Certificates page, find the certificate you want to deploy and confirm the following information:
Certificate Status: Make sure that the status is Issued. If the status is About to Expire or Expired, you must renew the SSL certificate.
Bound Domains: Make sure that the certificate covers all domain names that you want to protect. Otherwise, browsers show security warnings when users access unmatched domain names over HTTPS. To add or modify domain names, see Add and replace domain names.
On the Actions column, go to the Download tab, set Server Type to Other, and then click Download.
Decompress the downloaded certificate package.
If the package contains both a certificate file (.pem) and a private key file (.key), securely store both files. You need them for deployment.
If the package contains only a certificate file (.pem) and no private key file (.key), you must deploy the certificate together with the private key file that you saved locally.
NoteIf you generated a certificate signing request (CSR) file by using a tool such as OpenSSL or Keytool when you applied for the certificate, the private key file is stored only on your local machine and the downloaded package does not contain the private key file. If the private key is lost, the certificate becomes unusable. You must purchase a paid certificate and generate a new CSR and private key.
Step 2: Open port 443 in security groups and firewalls
Before you can use an SSL certificate to support HTTPS access, make sure that the HTTPS port (port 443 by default) is open. Otherwise, you cannot access the website over HTTPS.
Open port 443
If you use a non-standard port for HTTPS, open that specific port instead.
Linux
Run the following command in the server terminal to check whether port 443 is open:
RHEL/CentOS
command -v nc > /dev/null 2>&1 || sudo yum install -y nc
# Replace <your_server_public_ip_address> with the public IP address of your server.
sudo ss -tlnp | grep -q ':443 ' || sudo nc -l 443 & sleep 1; nc -w 3 -vz <your_server_public_ip_address> 443
If the output contains
Ncat: Connected to <your_server_public_ip_address>:443, port 443 is open. Otherwise, you must open port 443 in the security group and firewall.Debian/Ubuntu
command -v nc > /dev/null 2>&1 || sudo apt-get install -y netcat
# Replace <your_server_public_ip_address> with the public IP address of your server.
sudo ss -tlnp | grep -q ':443 ' || sudo nc -l -p 443 & sleep 1; nc -w 3 -vz <your_server_public_ip_address> 443
If the output contains
Connection to <your_server_public_ip_address> port [tcp/https] succeeded!or[<your_server_public_ip_address>] 443 (https) open, port 443 is open. Otherwise, you must open port 443 in the security group and firewall.Open port 443 in the security group.
ImportantIf your server is deployed on a cloud platform, make sure that its security group allows inbound traffic on TCP port 443. Otherwise, the service is not accessible from the internet. The following operations use an Alibaba Cloud ECS instance as an example. For other cloud platforms, see their official documentation.
Go to the ECS Instances page and click the name of the target instance to go to its details page. For more information, see Add a security group rule. Add a rule to the security group with Action set to Allow, Protocol Type set to TCP, Port Range set to HTTPS(443), and Authorization Object set to Anywhere (0.0.0.0/0).
Open port 443 in the firewall.
Run the following command to identify the current firewall service on your system:
if command -v systemctl >/dev/null 2>&1 && systemctl is-active --quiet firewalld; then
    echo "firewalld"
elif command -v ufw >/dev/null 2>&1 && sudo ufw status | grep -qw active; then
    echo "ufw"
elif command -v nft >/dev/null 2>&1 && sudo nft list ruleset 2>/dev/null | grep -q 'table'; then
    echo "nftables"
elif command -v systemctl >/dev/null 2>&1 && systemctl is-active --quiet iptables; then
    echo "iptables"
elif command -v iptables >/dev/null 2>&1 && sudo iptables -L 2>/dev/null | grep -qE 'REJECT|DROP|ACCEPT'; then
    echo "iptables"
else
    echo "none"
fi
If the output is
none, no further action is required. Otherwise, based on the firewall type (firewalld,ufw,nftables, oriptables), run the corresponding command to open port 443:firewalld
sudo firewall-cmd --permanent --add-port=443/tcp && sudo firewall-cmd --reloadufw
sudo ufw allow 443/tcpnftables
sudo nft add table inet filter 2>/dev/null
sudo nft add chain inet filter input '{ type filter hook input priority 0; }' 2>/dev/null
sudo nft add rule inet filter input tcp dport 443 counter accept 2>/dev/null
iptables
sudo iptables -A INPUT -p tcp --dport 443 -j ACCEPTTo prevent iptables rules from being lost after a system reboot, run the following command to make the rules persistent:
RHEL/CentOS sudo yum install -y iptables-services sudo service iptables saveDebian/Ubuntu sudo apt-get install -y iptables-persistent sudo iptables-save | sudo tee /etc/iptables/rules.v4 >/dev/null
Windows
Log on to your Windows server, click the Start menu, and then open Control Panel.
Go to .
If the firewall is turned off as shown in the following figure, no further action is required.
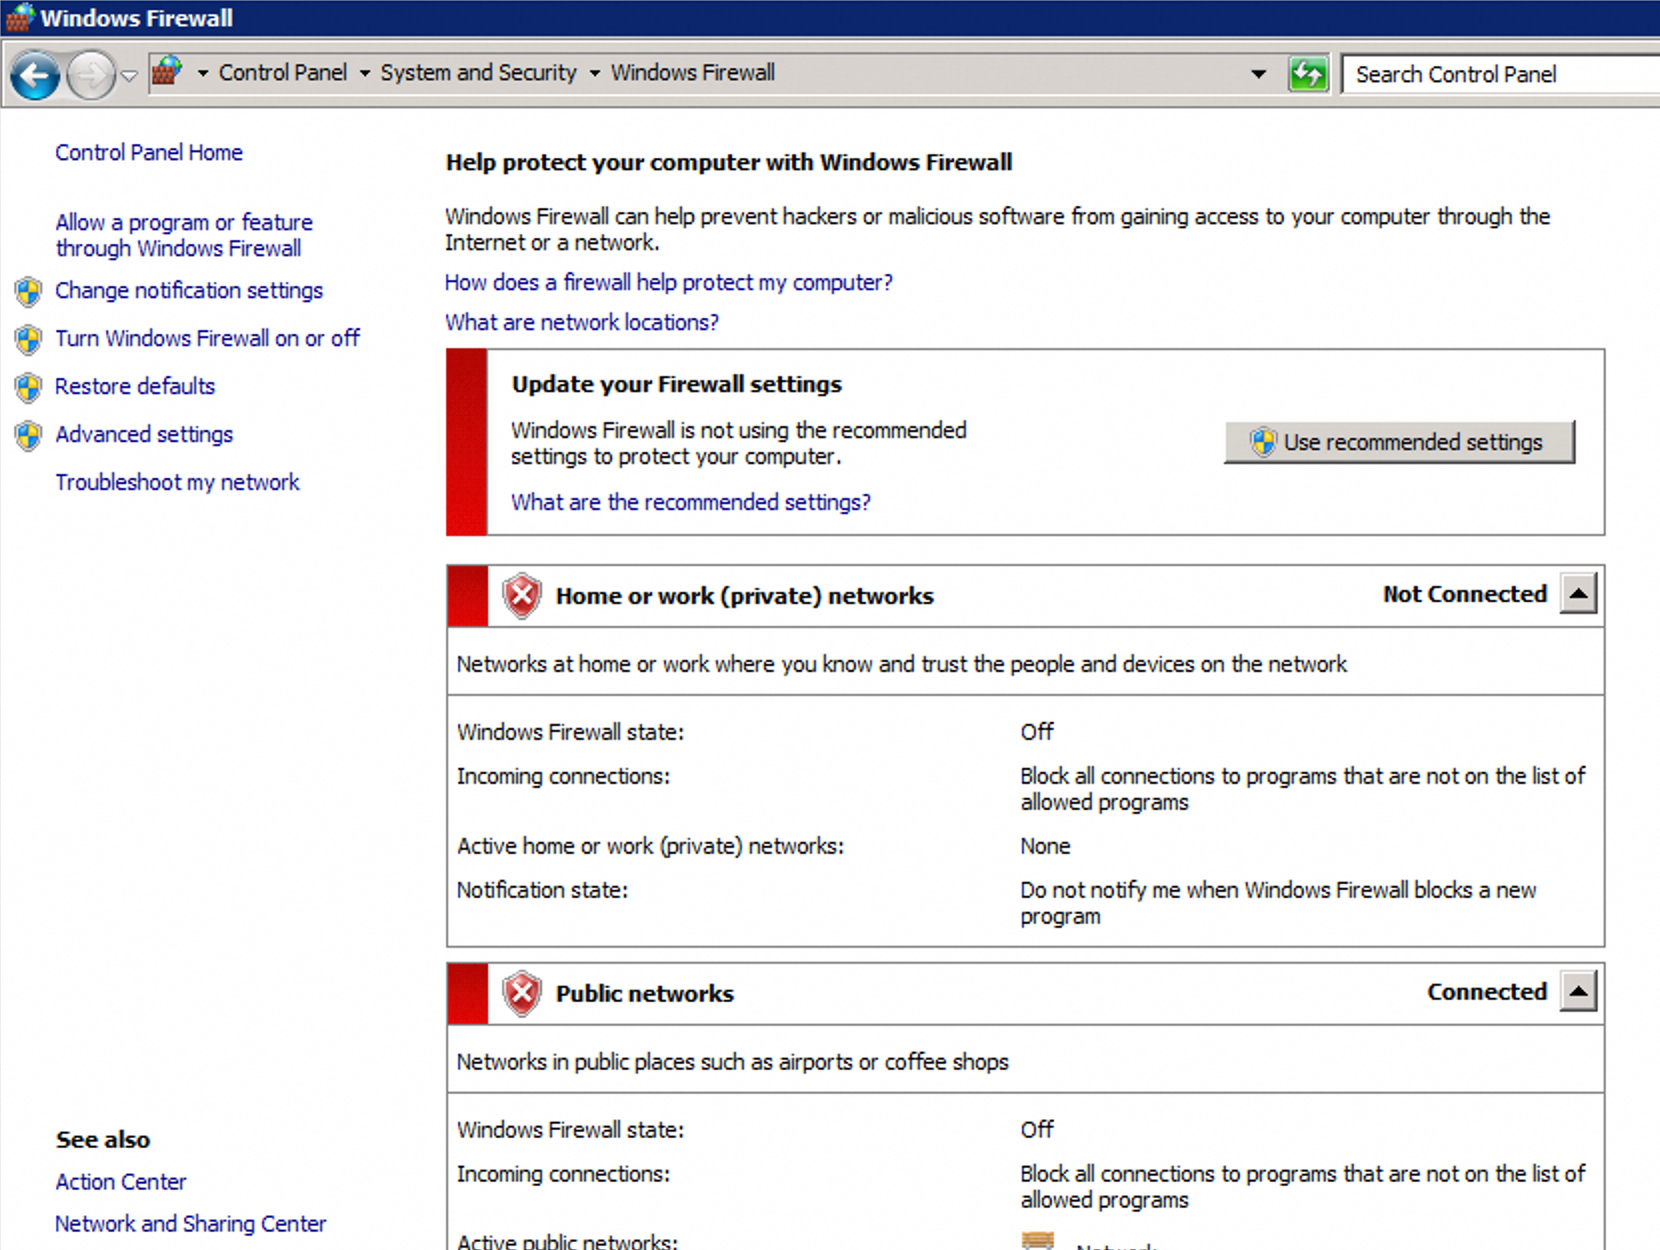
If the firewall is turned on, follow these steps to allow HTTPS traffic.
In the left-side navigation pane, click and check whether an inbound rule exists for which Protocol is TCP, Local Port is 443, and Action is Block.
If such a rule exists, right-click the rule, select Properties, and on the General tab, change the action to Allow the connection. Then, click Apply.
Step 3: Log on to BT-Panel to install the SSL certificate
Log on to BT-Panel in your browser.
NoteIf you cannot log on to BT-Panel, see Failed to log on to the tower panel console for an ECS instance for solutions.
If you have forgotten the BT-Panel URL, username, or password, you can retrieve them by using one of the following methods:
After you log on, click Websites in the left-side navigation pane. Find the target website and click Not Deployed in the SSL Certificate column.
Use a local text editor to open the certificate file (
.pem) and private key file (.key) that you saved in Step 1. Copy the full content of each file and paste it into the corresponding input field.(Optional) Enable Force HTTPS: On the configuration page in Step 3, turn on the Force HTTPS switch.
After you bind a certificate to a website, the HTTP access channel is retained by default. Directly removing HTTP access may prevent users that rely on HTTP from accessing the website normally. After Force HTTPS is enabled, all HTTP requests are automatically redirected to HTTPS, which ensures both access continuity and communication security.
Click Save and Enable Certificate. After the operation is complete, the page displays the validity period of the certificate.
Step 4: Verify whether the SSL certificate is installed
Access the domain bound with the certificate over HTTPS. For example, enter
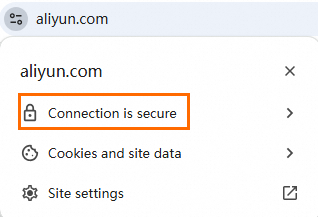
https://yourdomain.com(replaceyourdomain.comwith your actual domain name).If a padlock icon appears in the browser address bar, the certificate is successfully deployed. If you encounter access issues or the padlock icon does not appear, clear the browser cache or try again in incognito (private) mode. If the issue persists, see the FAQ section for troubleshooting.
 Note
Starting from Chrome 117, the padlock icon
 in the address bar is replaced by a new tune icon
 . Click this icon to view the security lock information.
Next steps (Optional)
Enable domain monitoring
After the certificate is deployed, we recommend that you enable domain name monitoring. The system automatically checks the validity period of the certificate and sends reminders before the certificate expires. This helps you renew the certificate in a timely manner to prevent service interruptions. For more information, see Purchase and enable public domain name monitoring.
FAQ
The certificate does not take effect or HTTPS is inaccessible after installation or update
Common causes include:
Browser cache: Clear the browser cache or use incognito or private mode to access the website.
The domain name has not completed ICP filing. See How to check DNS resolution records and ICP filing information.
Port 443 is not open in the server security group or firewall. See Open port 443 in security groups and firewalls.
The Bound Domains of the certificate does not include the domain name that you are accessing. See Check whether the bound domains cover all the domains that you want to protect.
The domain name is integrated with cloud services such as CDN, SLB, or WAF, but the certificate is not installed on the corresponding service. For more information, see Certificate deployment location when traffic passes through multiple cloud services.
The domain name resolves to multiple servers, but the certificate is installed on only some of them. You must install the certificate on each server.
For further troubleshooting, see Troubleshoot certificate deployment issues based on browser errors and SSL certificate deployment troubleshooting guide.
How do I update (replace) an SSL certificate in BT-Panel?
Download the new SSL certificate (
.pemfile) and private key (.keyfile) to your local machine.In the left-side navigation pane of BT-Panel, click Websites. Find the target website and click Settings in the Actions column.
In the website settings dialog box, click SSL in the left-side navigation pane.
In the certificate content section, paste the new certificate content to overwrite the existing content in the corresponding text box.
Copy the content from the
.keyfile and paste it into the Key (KEY) text box in BT-Panel to replace the existing content.Copy the content from the
.pemfile and paste it into the Certificate (PEM format) text box in BT-Panel to replace the existing content.
Click Save.