Enable HTTPS access for websites using personal test certificates (Free Edition)
If you own a domain name with an ICP filing, you can apply for a free personal test certificate before your website goes live and deploy it to your web server to enable HTTPS access for security verification in test environments.
Process overview
Deploy a personal test certificate to your server in three steps:
-
Obtain a personal test certificate: Obtain eligibility to use a personal test certificate.
-
Submit a certificate request: Fill in the certificate information and submit it for review.
-
Deploy the certificate: Deploy the issued certificate to your web server.
Prerequisites
-
Real-name verification has been completed. For more information, see Individual Real-name Verification or Enterprise Real-name Verification.
Port 443, the standard port for HTTPS communication, is open on the web server.
If you use an Alibaba Cloud ECS instance, make sure that an inbound security group rule is configured to allow TCP access on port 443. For more information, see Manage security group rules.
If you use a server from another cloud provider or a local server, make sure that TCP port 443 is open in the firewall or security group.
-
You own a domain name that has an ICP filing.
-
You have DNS resolution management permissions for the domain name.
Port 443 is the default port for HTTPS. You can also customize a port number based on your actual requirements.
Step 1: Obtain a personal test certificate (Free Edition)
-
Log on to the Certificate Management console or . In the left-side navigation pane, choose Certificate Management > SSL Certificate Management V2.0. On the Individual Test Certificate (Formerly Free Certificate) tab, click Purchase Certificate.
-
On the Purchase Certificate page, specify the Purchase Quantity, keep other settings at their default values, select Certificate Management Service Terms of Service and Technical Support Agreement for Certificate Management Service, and then click Buy Now to complete the payment.
Note-
If you do not meet the rules for obtaining a personal test certificate (Free Edition), see Purchase a personal test certificate (Pro).
-
A personal test certificate (Free Edition) cannot be canceled after it is obtained. If it remains unused within 3 months of being obtained, the quota for that year is automatically returned.
-
Step 2: Submit a certificate request
-
On the Individual Test Certificate (Formerly Free Certificate) tab, find the target Certificate Instance, and click Certificate Application in the Actions column.
-
In the certificate request dialog box, fill in the following information, and then click Submit after confirming that the information is correct.
-
Domains to Bind: Enter the domain name to be bound to the certificate. Example domain name:
www.aliyun.com. -
CSR Generation: Select Automatic.
-
Location: Select the province, city, and district where the applicant is located.
-
Contact: Select a contact person for this certificate request.
-
Encryption Algorithm: Select based on your requirements. A longer key length provides higher encryption strength. RSA_2048 indicates the RSA algorithm with a 2048-bit key.
-
Domain Verification Method: We recommend that you select Automatic DNS Verification. When the domain name DNS is different from the current Alibaba Cloud account, you can select Manual DNS validation or File validation. The following table compares the three validation methods:
Validation Method
Description
Recommended Scenario
Automatic DNS Verification
The system automatically adds a DNS resolution record to complete validation. This method is available only when the DNS service for the domain name is under the same Alibaba Cloud account.
Recommended. This is the easiest method.
Manual DNS Verification
Manually add a CNAME or TXT DNS resolution record at the DNS provider for your domain name.
Use when the DNS service for the domain name is under a different Alibaba Cloud account.
File Verification
Create a specific file on the web application server associated with your domain name to verify domain ownership.
Use when you cannot manage DNS resolution.
-
After confirming that the information is correct, click Submit.
-
-
Complete domain validation. On the Individual Test Certificate (Formerly Free Certificate) tab, find the target certificate instance, and click Verify in the Actions column. Follow the instructions to complete domain ownership validation.
After domain ownership validation succeeds, the certificate is typically issued within 1 to 15 minutes. After issuance, the Status changes to Issued. If the certificate is not issued after a long wait, check whether the DNS validation configuration is correct.
Note-
The certificate takes effect from the date of issuance and is valid for 90 days.
-
If validation fails to pass for an extended period, for example, due to incorrect file content, mismatched DNS record values, or DNS validation timeout, see FAQ for domain ownership validation for solutions.
-
Step 3: Deploy the certificate to the web server
The following procedure uses CentOS 8.0 64-bit and Nginx 1.14.2 as an example. The procedure may differ for other operating systems or web servers such as Apache, Tomcat, and IIS. For more information, see Deploy an SSL certificate to a server.
-
Download the certificate files.
-
On the Individual Test Certificate (Formerly Free Certificate) tab, find the issued certificate, and click Download in the Actions column.
-
Select the certificate format that corresponds to your web server type (for example, Nginx), and click Download in the Actions column to download the compressed certificate file package.
-
-
Upload the certificate files to your server.
-
In the Nginx conf directory, create a directory to store the certificates.
ImportantIn this example, the Nginx configuration directory is
/usr/local/nginx/conf. If you are unsure about the Nginx configuration directory, you can runnginx -tto check.# Go to the default Nginx configuration directory. cd /usr/local/nginx/conf # Create a certificate directory named cert. mkdir cert -
Upload the extracted certificate files to the Nginx server. The extracted certificate files usually include:
-
Certificate file (for example:
example.com.pem) -
Private key file (for example:
example.com.key)
NoteYou can use the local file upload feature of a remote logon tool to upload files. Examples of such tools include PuTTY, Xshell, or WinSCP. If you use an Alibaba Cloud Elastic Compute Service instance, see Upload or download files for more information.
-
-
-
Configure the web server: Edit the Nginx configuration file
nginx.confand modify the certificate-related settings.ImportantIn this example, the Nginx configuration directory is
/usr/local/nginx/conf. If you are unsure about the location ofnginx.conf, you can runnginx -tto check.-
Run the following command to open the configuration file.
sudo vim /usr/local/nginx/conf/nginx.conf -
In
nginx.conf, find the HTTPS server block configuration.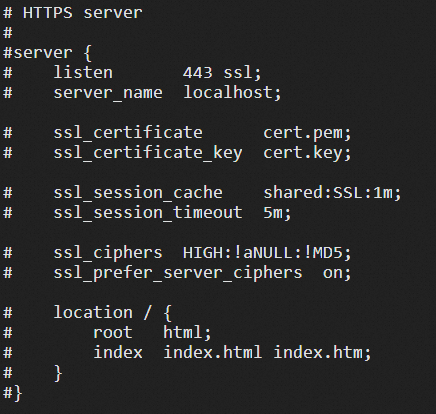 Note
If the server block shown in the preceding figure does not exist in
nginx.confor in any file referenced by an include directive, manually add it. -
Remove the # comment symbol from the beginning of each line, and adjust the configuration based on the following example.
NoteThe insecure TLSv1.1 protocol has been removed from the following example (see RFC 8996), and only TLSv1.2 and TLSv1.3 are retained.
After the modification is complete, press the
Esckey to enter command mode, type:wq, and then press theEnterkey to save and exit.server { # Default HTTPS port is 443. # If you do not configure the default HTTPS port here, Nginx may fail to start. listen 443 ssl; # Enter the domain name bound to the certificate. server_name <YOURDOMAIN>; # Enter the absolute path to the certificate file. ssl_certificate cert/<cert-file-name>.pem; # Enter the absolute path to the certificate private key file. ssl_certificate_key cert/<cert-file-name>.key; ssl_session_cache shared:SSL:1m; ssl_session_timeout 5m; # Customize the TLS protocol versions and cipher suites to use (the following is an example configuration; assess whether you need to configure them). # Higher TLS protocol versions provide more secure HTTPS communication, but higher versions have poorer browser compatibility. ssl_ciphers ECDHE-RSA-AES128-GCM-SHA256:ECDHE:ECDH:AES:HIGH:!NULL:!aNULL:!MD5:!ADH:!RC4; ssl_protocols TLSv1.2 TLSv1.3; # Prefer server cipher suites. Enabled by default. ssl_prefer_server_ciphers on; location / { root html; index index.html index.htm; } } -
Run the following commands to reload the configuration.
# Go to the executable directory of the Nginx service.
cd /usr/local/nginx/sbin
# Reload the configuration.
./nginx -s reload
-
-
Verify the deployment.
After the certificate is deployed, you can verify the deployment by accessing the domain name that is bound to the certificate.
https://yourdomain #Replace yourdomain with your domain name.-
If a
 icon appears in the browser address bar, the certificate is installed successfully.
-
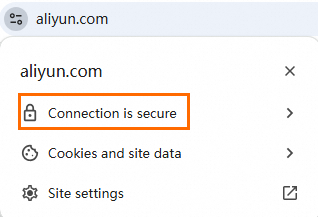
Starting from Chrome version 117, Chrome replaces the
icon for HTTPS in the address bar with an  icon. Click the icon. When you see a
 mark as shown in the following example, the certificate is installed successfully.

-
FAQ
What do I do if domain validation does not pass for an extended period?
-
Check whether the DNS resolution record is correctly added, and ensure that the record type (CNAME or TXT) and the record value match those shown in the console.
-
DNS resolution records take some time to take effect. Validation typically succeeds within a few minutes but may take up to 30 minutes.
-
If you selected file validation, ensure that the validation file is placed in the correct path on the server associated with your domain name and is publicly accessible.
What do I do if the website becomes inaccessible after running nginx -s reload?
-
Run
nginx -tto check whether the configuration file syntax is correct. -
Check whether the certificate file paths are correct, and ensure that the files specified by
ssl_certificateandssl_certificate_keyexist and use absolute paths. -
Check the Nginx error log (default path:
/usr/local/nginx/logs/error.log) and troubleshoot based on the error message. -
For troubleshooting, see Troubleshoot certificate deployment issues based on browser error messages and Self-service troubleshooting guide for SSL certificate deployment faults.
What do I do if the browser shows "Not Secure" after certificate deployment?
-
Confirm that the certificate status is Issued and has not expired.
-
Confirm that the domain name you are accessing matches the domain name bound to the certificate.
-
Clear the browser cache and try accessing the site again.