Configure an H3C firewall
This topic explains how to configure an H3C firewall to establish an IPsec-VPN connection between your data center and a virtual private cloud (VPC) on Alibaba Cloud. It covers both dual-tunnel mode and single-tunnel mode.
We recommend that you use dual-tunnel mode whenever possible. For information about dual-tunnel mode, see Associate with a VPN gateway.
Dual-tunnel mode (recommended)
Scenario

In the preceding scenario:
A company has a data center on premises. The CIDR block in the data center that must communicate with Alibaba Cloud is 10.34.0.0/24.
The company has a virtual private cloud (VPC) on Alibaba Cloud. The VPC CIDR block is 192.168.0.0/16, and application services are deployed on Elastic Compute Service (ECS) instances in the VPC.
The company plans to establish a dual-tunnel mode IPsec-VPN connection between the data center and the VPC on the cloud to enable mutual access to resources.
IP address plan
Based on the number of Internet egresses of the H3C device, this topic provides two scenarios:
single egress: The H3C device is configured with only one Internet egress, and therefore has only one public IP address.
dual egresses: The H3C device is configured with two Internet egresses, which correspond to two public IP addresses.
You can view the corresponding IP address plan based on the actual conditions of your on-premises device.
Single egress
The following table describes the IP address plan.
Location | Configuration item | Example value |
On-premises data center | H3C device addresses | GE2 (Internet egress): 10.32.0.175 Next hop: 10.32.0.173 Mapped public IP address: 8.XX.XX.3 |
GE4 (private interface): 10.34.0.20 | ||
Private CIDR block | 10.34.0.0/24 | |
Server IP address | 10.34.0.21 | |
Alibaba Cloud | VPN gateway address | Active tunnel: 39.XX.XX.17 Standby tunnel: 39.XX.XX.10 |
VPC CIDR block | 192.168.0.0/16 | |
vSwitch CIDR block | Zone J: 192.168.1.0/24 Zone K: 192.168.2.0/24 | |
ECS address | 192.168.1.11 |
Dual egresses
The IP address plan is as follows.
Location | Configuration item | Example value |
Data center | H3C device address | GE2 (Internet egress 1): 10.32.0.175 Next hop: 10.32.0.173 Mapped public IP address: 8.XX.XX.3 |
GE3 (Internet egress 2): 10.33.0.238 Next hop: 10.33.0.236 Mapped public IP address: 116.XX.XX.68 | ||
GE4 (private interface): 10.34.0.20 | ||
Private CIDR block | 10.34.0.0/24 | |
Server IP address | 10.34.0.21 | |
Alibaba Cloud | VPN gateway address | Active tunnel: 39.XX.XX.17 Standby tunnel: 39.XX.XX.10 |
VPC CIDR block | 192.168.0.0/16 | |
vSwitch CIDR block | Zone J: 192.168.1.0/24 Zone K: 192.168.2.0/24 | |
ECS address | 192.168.1.11 |
BGP plan
This topic describes how to configure an H3C firewall for an IPsec-VPN connection that uses static routing and BGP dynamic routing. If you do not need to use BGP dynamic routing, you can ignore this section. The following is the BGP CIDR block plan in this topic.
Resource | Tunnel | BGP tunnel CIDR block | BGP IP address | BGP local ASN |
Alibaba Cloud VPN gateway | Tunnel 1 | 169.254.10.0/30 Note Within a VPN gateway instance, the CIDR block of each tunnel must be unique. | 169.254.10.1 | 65535 |
Tunnel 2 | 169.254.20.0/30 | 169.254.20.1 | ||
H3C firewall | Tunnel 1 | 169.254.10.0/30 | 169.254.10.2 | 65500 |
Tunnel 2 | 169.254.20.0/30 | 169.254.20.2 |
IPsec-VPN connection configuration plan
In dual-tunnel mode, Tunnel 1 (active tunnel) and Tunnel 2 (standby tunnel) use the same example values.
For each tunnel, the IPsec-VPN connection configuration on the Alibaba Cloud side and the H3C firewall side must be the same.
Configuration item | Example value | |
Pre-shared key | ChangeMe**** | |
IKE | Version | ikev2 |
Negotiation mode | main | |
Encryption algorithm | aes256 | |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
IPsec | Encryption algorithm | aes256 |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
Prerequisites
Before you configure the H3C device, complete the following tasks on the Alibaba Cloud side: create a VPN gateway instance, create a customer gateway, create an IPsec-VPN connection, and configure the routing of the VPN gateway.
For static routing, see Standard VPN Gateway quick start.
For BGP dynamic routing, see Dual-tunnel mode with BGP.
The customer gateway configurations differ between single egress and dual egresses scenarios:
Single egress: You need to create only one customer gateway. When you establish the IPsec-VPN connection, both tunnels use the same customer gateway.
Dual egresses: You need to create two customer gateways. When you establish the IPsec-VPN connection, the two tunnels use their respective customer gateways.
Procedure
This topic uses the vFW1k E1185 version of H3C as a configuration example. Configurations may vary for firewalls of different models and versions. You can refer to the corresponding documentation or consult the firewall vendor to perform the configuration based on the version that you actually use.
This topic provides configuration examples for four scenarios. You can view the corresponding configuration steps based on the actual conditions of your on-premises device.
Single egress + static routing
In the single-egress scenario with a single public IP address, you can bind the single egress of the H3C device to two Tunnel interfaces and configure different IPsec profiles for the interfaces to connect to the active tunnel and standby tunnel on Alibaba Cloud.
Step 1: Interface and networking configuration
Configure IP addresses and security zones for the public interface and the private interface of the H3C device, and then configure routes.
# Configure a public interface.
interface GigabitEthernet 2/0
 ip addr 10.32.0.175 24
 quit

# Configure a private interface.
interface GigabitEthernet 4/0
 ip addr 10.34.0.10 24
 quit

# Add the public and private interfaces to their respective security zone.
security-zone name Untrust
 import interface GigabitEthernet 2/0
 quit
security-zone name Trust
 import interface GigabitEthernet 4/0
 quit

# Configure a route for peer VPN gateway public IP (Internet egress).
ip route-static 39.XX.XX.17 32 10.32.0.173
ip route-static 39.XX.XX.10 32 10.32.0.173
ip route-static 10.0.0.0 8 10.34.0.253
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Tunnel configuration
Create two tunnel interfaces to connect to the active tunnel and the standby tunnel on the cloud.
# Configure the tunnel interfaces and apply IPsec to the tunnel interfaces.
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit

# Add the tunnel interfaces to the Untrust security zone.
security-zone name Untrust
 import interface Tunnel 1
 import interface Tunnel 2
 quit
Step 3: IPsec transform set and policy configuration
Configure IPsec and IKE. Make sure that the configurations are the same as those on the Alibaba Cloud side.
# Configure the IPsec transform set
ipsec transform-set to-ali-trans
 encapsulation-mode tunnel
 protocol esp
 esp authentication-algorithm sha256
 esp encryption-algorithm aes-cbc-256
 pfs dh-group14
 quit

# Configure the IKEv2 proposal and the IKE security policy
ikev2 proposal to-ali-prop
 dh group14
 encryption aes-cbc-256
 integrity sha256
 prf sha256
 quit
ikev2 policy to-ali-policy
 priority 1
 proposal to-ali-prop
 quit

# Configure the IKE keychain. The two peers correspond to the two tunnels on Alibaba Cloud, and address specifies the public IP address on Alibaba Cloud.
ikev2 keychain to_ali_key1
 peer to-ali-peer1
  address 39.XX.XX.17 32
  identity address 39.XX.XX.17
  pre-shared-key plaintext ChangeMe****
  quit
 quit
ikev2 keychain to_ali_key2
 peer to-ali-peer2
  address 39.XX.XX.10 32
  identity address 39.XX.XX.10
  pre-shared-key plaintext ChangeMe****
  quit
 quit

# Configure the IKEv2 profile. The two peers correspond to the two tunnels on Alibaba Cloud.
ikev2 profile to-ali-profile1
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key1
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.17 32
 sa duration 86400
 dpd interval 30 periodic
 quit

ikev2 profile to-ali-profile2
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key2
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.10 32
 sa duration 86400
 dpd interval 30 periodic
 quit


# Configure the IPsec profile, which references the IKEv2 profile created above.
# We recommend that you use only the time-based mode for the SA duration. If you need to configure the traffic-based mode, set the traffic-based value to the maximum.
ipsec profile to-ali-profile1 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile1
 sa duration time-based 86400
 quit

ipsec profile to-ali-profile2 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile2
 sa duration time-based 86400
 quit

# Configure the tunnel interface and apply the IPsec policy to the tunnel interface.
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile1
 source 10.32.0.175
 destination 39.XX.XX.17
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile2
 source 10.32.0.175
 destination 39.XX.XX.10
 quit

# Configure a route to the private CIDR block of the peer to point to the tunnel interface. tunnel1 is the active tunnel and has a higher route priority.
ip route-static 192.168.0.0 16 Tunnel 1 preference 10
ip route-static 192.168.0.0 16 Tunnel 2 preference 20
Step 4: Security policy configuration
Configure an access control list (ACL) to permit IKE negotiation and IPsec data traffic.
The example here is a simplified configuration. Add fine-grained rules based on your actual needs.
If multiple CIDR blocks in the data center need to communicate with the VPC, we recommend that you use destination-based routing mode to connect to the H3C device. For more information, see Recommended configuration solutions for multiple CIDR blocks.
# Configure an ACL to allow IKE negotiation packets and IPsec data packets between the Untrust security zone and any other zone. In this example, the configurations are simplified. You can configure a fine-grained ACL based on your business requirements.
acl advanced 3001
 rule 0 permit ip
 quit
zone-pair security source any destination any
 packet-filter 3001
 quit
Step 5: Verify results
On the data center side, after you configure routes from the data center server to the H3C device, you can start to test the network connectivity between the data center and the Alibaba Cloud VPC and verify failover.
Test the connectivity between the data center and the VPC: Log on to an ECS instance in the VPC, run
ping <private IP address of the data center server>. If a reply packet from the data center server is received, the communication is normal.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC and run
ping <private IP address of the data center server> -c 10000to continuously send access packets to the data center.Interrupt the active tunnel of the IPsec-VPN connection: You can modify the pre-shared key of the active tunnel of the IPsec-VPN connection. The active tunnel is then interrupted because the pre-shared keys on the two ends are inconsistent.
After the active tunnel is interrupted, observe the communication status of the ECS instance in the VPC: If the traffic recovers after a brief interruption, it indicates that after the active tunnel is interrupted, the traffic automatically communicates through the standby tunnel.
Single egress + BGP routing
In a scenario with a single public IP address and a single egress, you can bind the single egress of the H3C device to two Tunnel interfaces and configure a different IPsec profile for each interface, so that the H3C device is connected to the active tunnel and standby tunnel of Alibaba Cloud.
Step 1: Interface and networking configuration
Configure IP addresses and security zones for the public interface and the private interface of the H3C device, and then configure routes.
#Public interface
interface GigabitEthernet 2/0
 ip addr 10.32.0.175 24
 quit

#Private interface
interface GigabitEthernet 4/0
 ip addr 10.34.0.10 24
 quit

#Add the interfaces to security zones
security-zone name Untrust
 import interface GigabitEthernet 2/0
 quit
security-zone name Trust
 import interface GigabitEthernet 4/0
 quit

#Configure the route to the public IP address of the peer Alibaba Cloud, with the next hop pointing to the Internet
ip route-static 39.XX.XX.17 32 10.32.0.173
ip route-static 39.XX.XX.10 32 10.32.0.173
#Configure the route to the internal CIDR block on the local side, with the next hop pointing to the private network
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Tunnel configuration
Create two Tunnel interfaces to connect to the active tunnel and standby tunnel on the cloud.
#Configure the Tunnel interfaces and apply the IPsec security framework to the Tunnel interfaces
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit

# Add the tunnel interface to a security zone
security-zone name Untrust
 import interface Tunnel 1
 import interface Tunnel 2
 quit
Step 3: IPsec transform set and policy configuration
Configure IPsec and IKE. Make sure the settings are consistent with those on the Alibaba Cloud side.
# Configure the IPsec transform set
ipsec transform-set to-ali-trans
 encapsulation-mode tunnel
 protocol esp
 esp authentication-algorithm sha256
 esp encryption-algorithm aes-cbc-256
 pfs dh-group14
 quit

# Configure the IKEv2 proposal and IKE security policy
ikev2 proposal to-ali-prop
 dh group14
 encryption aes-cbc-256
 integrity sha256
 prf sha256
 quit
ikev2 policy to-ali-policy
 priority 1
 proposal to-ali-prop
 quit

# Configure the IKE keychain. The two peers correspond to the two tunnels on Alibaba Cloud, and address is the public IP address on Alibaba Cloud.
ikev2 keychain to_ali_key1
 peer to-ali-peer1
  address 39.XX.XX.17 32
  identity address 39.XX.XX.17
  pre-shared-key plaintext ChangeMe****
  quit
 quit
ikev2 keychain to_ali_key2
 peer to-ali-peer2
  address 39.XX.XX.10 32
  identity address 39.XX.XX.10
  pre-shared-key plaintext ChangeMe****
  quit
 quit

# Configure the IKEv2 profile. The two peers correspond to the two tunnels on Alibaba Cloud.
ikev2 profile to-ali-profile1
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key1
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.17 32
 sa duration 86400
 dpd interval 30 periodic
 quit

ikev2 profile to-ali-profile2
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key2
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.10 32
 sa duration 86400
 dpd interval 30 periodic
 quit


# Configure the IPsec profile and reference the IKEv2 profile created above
# We recommend that you use only time-based SA duration. If you need to configure traffic-based SA duration, set the traffic-based value to the maximum.
ipsec profile to-ali-profile1 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile1
 sa duration time-based 86400
 quit

ipsec profile to-ali-profile2 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile2
 sa duration time-based 86400
 quit

# Configure the tunnel interface and apply the IPsec policy to the tunnel interface
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile1
 source 10.32.0.175
 destination 39.XX.XX.17
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile2
 source 10.32.0.175
 destination 39.XX.XX.10
 quit

# Configure routes to the peer private CIDR blocks to point to the tunnel interfaces. tunnel1 is the active tunnel and has a higher route priority.
ip route-static 192.168.0.0 16 Tunnel 1 preference 10
ip route-static 192.168.0.0 16 Tunnel 2 preference 20
Step 4: Security policy configuration
Configure a security policy to allow IKE protocol traffic and IPsec data traffic to pass through.
The example here is a simplified configuration. Add fine-grained rules as needed based on your actual requirements.
If multiple CIDR blocks on the on-premises IDC side need to communicate with the VPC, we recommend that you use destination-based routing mode to connect with the H3C device. For more information, see Recommended configuration solutions for multiple CIDR blocks.
#Configure the security zone to allow IKE negotiation packets and IPsec data packets. The configuration here is simplified. Add fine-grained rules as needed.
acl advanced 3001
 rule 0 permit ip
 quit
zone-pair security source any destination any
 packet-filter 3001
 quit
Step 5: BGP dynamic routing configuration
# Configure IP addresses for the tunnel interfaces to establish BGP peering with the VPN gateway on Alibaba Cloud.
interface tunnel 1 mode ipsec
 ip address 169.254.10.2 30
 quit
interface tunnel 2 mode ipsec
 ip address 169.254.20.2 30
 quit

# Delete the static routes that point to the tunnels in the static routing scenario.
undo ip route-static 192.168.0.0 16 Tunnel 1 preference 10
undo ip route-static 192.168.0.0 16 Tunnel 2 preference 20

# Configure BGP dynamic routing. The H3C firewall advertises 10.0.0.0/8 to the VPN gateway on Alibaba Cloud.
bgp 65500
peer 169.254.10.1 as-number 65535
peer 169.254.20.1 as-number 65535
address-family ipv4 unicast
peer 169.254.10.1 enable
peer 169.254.20.1 enable
network 10.0.0.0 8  # Advertise the CIDR block 10.0.0.0/8.
After the configuration is complete, view the BGP connection:
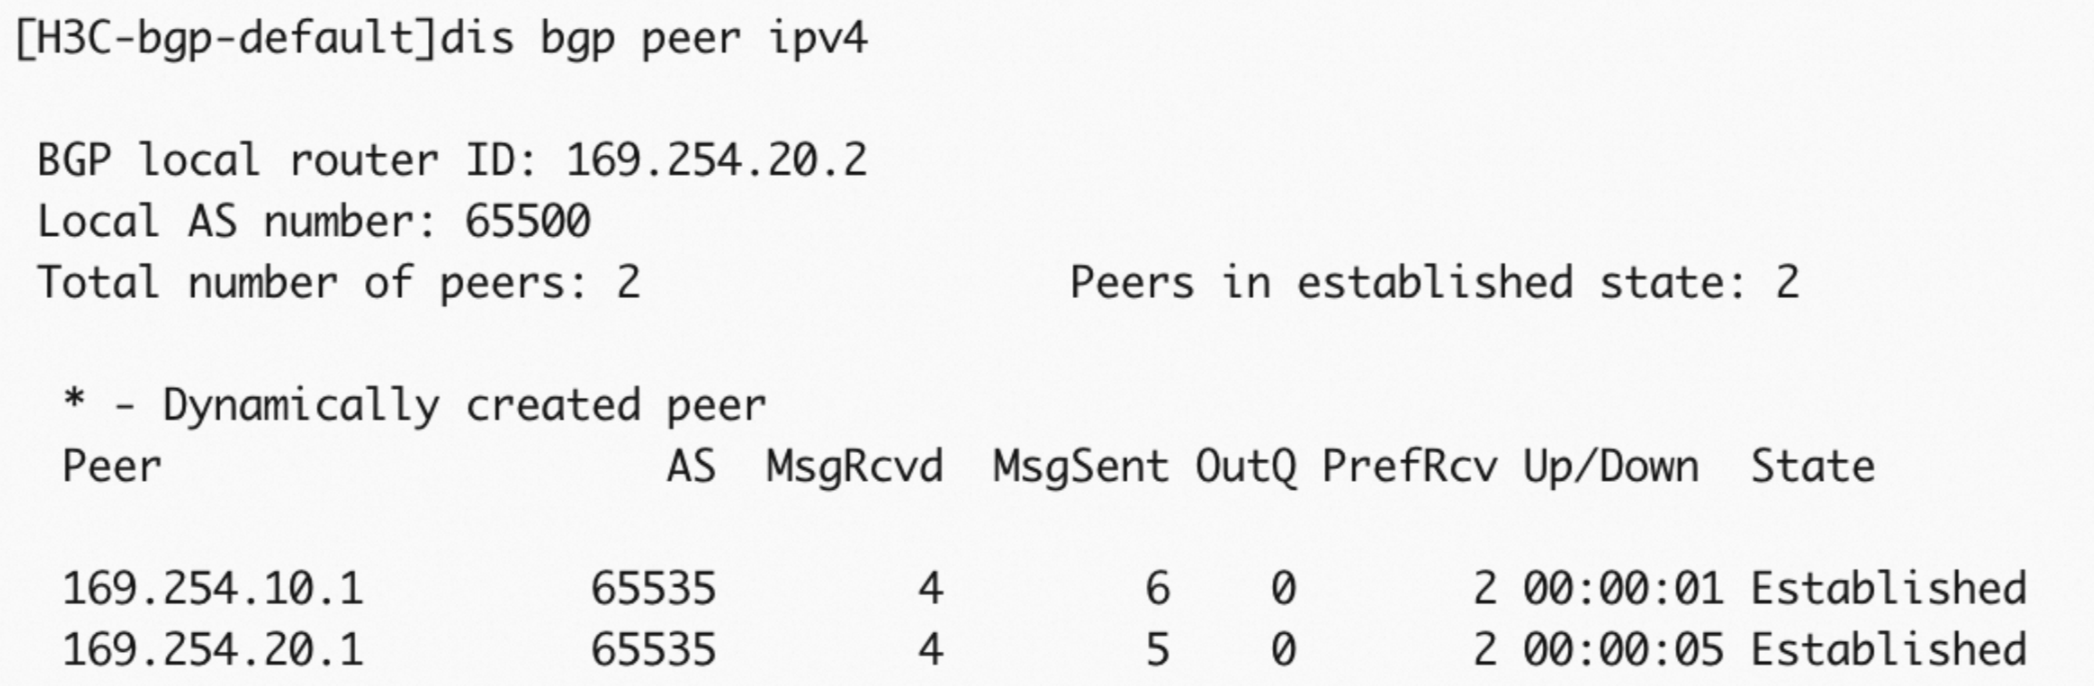
View the BGP routes:
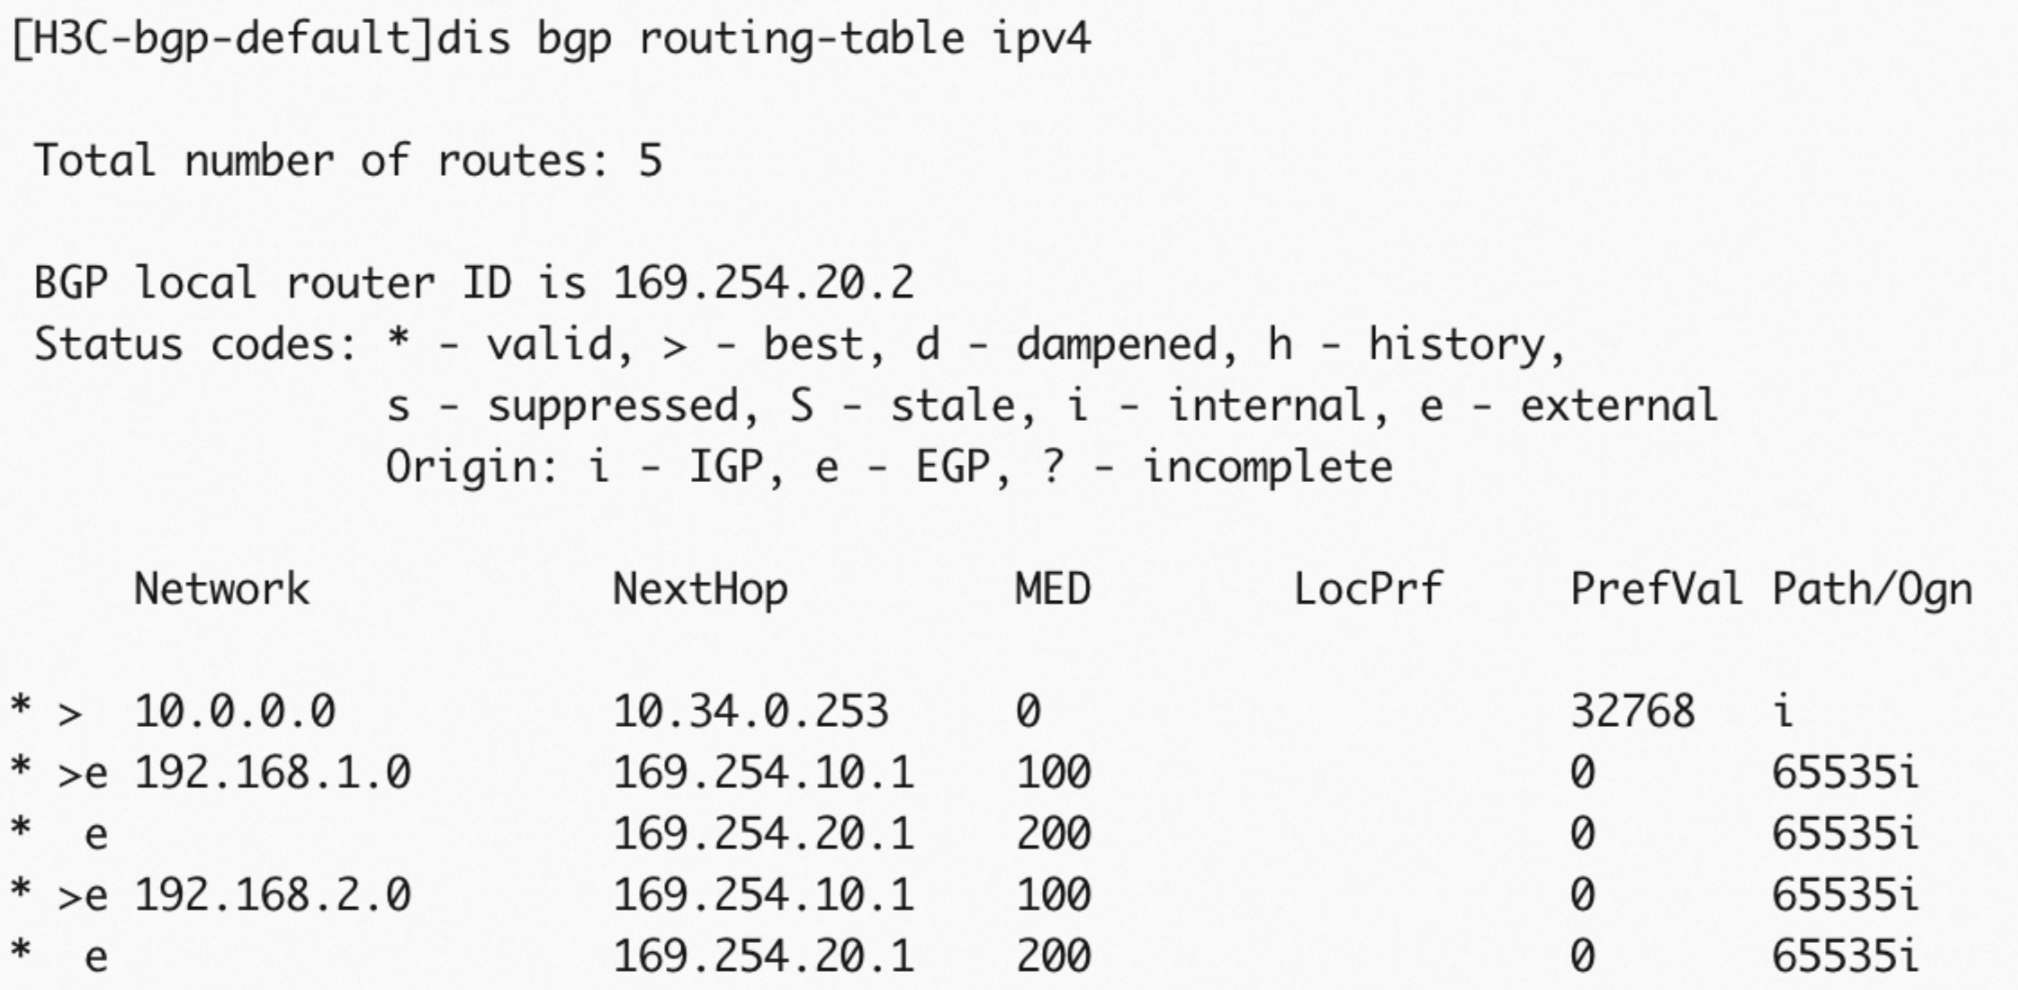
View the routing table:
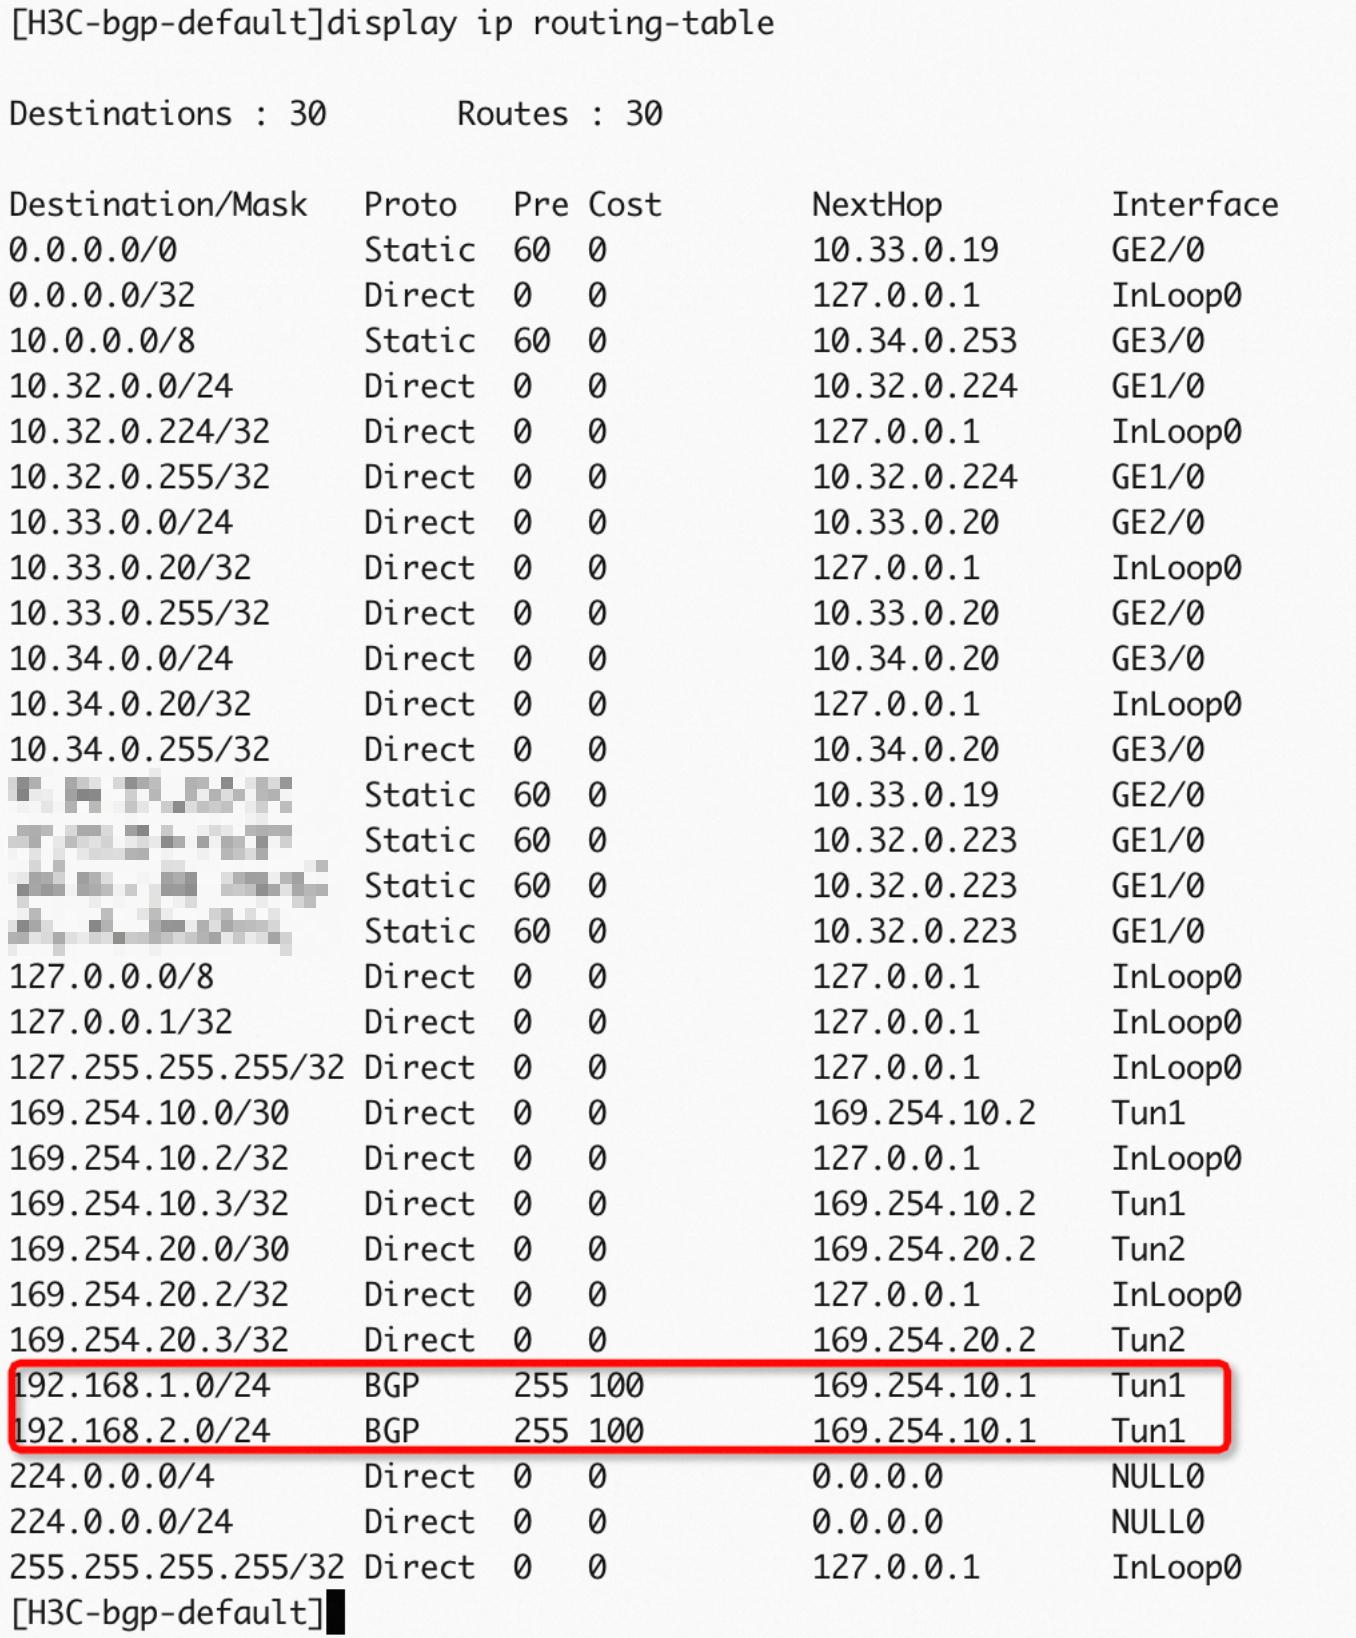
Step 6: Verify results
On the data center side, after you configure the route from the data center client to the H3C device, you can start to test the network connectivity between the data center and the Alibaba Cloud VPC, and verify failover.
Test the connectivity between the data center and the VPC: Log on to an ECS instance in the VPC, run
ping <private IP address of the data center server>. If a reply packet from the data center server is received, the communication is normal.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC and run
ping <private IP address of the data center server> -c 10000to continuously send access packets to the data center.Interrupt the active tunnel of the IPsec-VPN connection: You can modify the pre-shared key of the active tunnel of the IPsec-VPN connection. The active tunnel is then interrupted because the pre-shared keys on the two ends are inconsistent.
After the active tunnel is interrupted, observe the communication status of the ECS instance in the VPC: If the traffic recovers after a brief interruption, it indicates that after the active tunnel is interrupted, the traffic automatically communicates through the standby tunnel.
Dual egresses + static routing
In a scenario with dual public IP addresses and dual egresses, you can bind the two egresses of the H3C device to two Tunnel interfaces respectively, and configure different IPsec profiles for them to connect to the active and standby tunnels of Alibaba Cloud.
Step 1: Configure interfaces and networking
Configure the IP address and security zone for the Internet-facing interface and the private interface respectively, and configure routes.
# Configure Public Interface 1.
interface GigabitEthernet 2/0
 ip addr 10.32.0.175 24
 quit

# Configure Public Interface 2.
interface GigabitEthernet 3/0
 ip addr 10.33.0.238 24
 quit

# Configure a private interface.
interface GigabitEthernet 4/0
 ip addr 10.34.0.10 24
 quit

# Add the public and private interfaces to their respective security zone.
security-zone name Untrust
 import interface GigabitEthernet 2/0
 import interface GigabitEthernet 3/0
 quit
security-zone name Trust
 import interface GigabitEthernet 4/0
 quit

# Configure 32-bit routes for peer VPN gateway public IPs (Internet).
ip route-static 39.XX.XX.17 32 10.32.0.173
ip route-static 39.XX.XX.10 32 10.33.0.236
# Configure a route for the local internal network CIDR block.
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Tunnel configuration
Create two Tunnel interfaces to connect to the active and standby tunnels on the cloud.
#Configure the tunnel interface and apply the IPsec security framework to the tunnel interface
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 3/0
 quit

#Add the tunnel interface to the security zone
security-zone name Untrust
 import interface Tunnel 1
 import interface Tunnel 2
 quit
Step 3: IPsec transform set and policy configuration
Configure IPsec and IKE settings, and make sure they are consistent with the Alibaba Cloud side.
#Configure the IPsec transform set
ipsec transform-set to-ali-trans
 encapsulation-mode tunnel
 protocol esp
 esp authentication-algorithm sha256
 esp encryption-algorithm aes-cbc-256
 pfs dh-group14
 quit

#Configure the IKEv2 proposal and IKE security policy
ikev2 proposal to-ali-prop
 dh group14
 encryption aes-cbc-256
 integrity sha256
 prf sha256
 quit
ikev2 policy to-ali-policy
 priority 1
 proposal to-ali-prop
 quit

#Configure the IKE keychain. The two peers correspond to the two tunnels on Alibaba Cloud, and address is the public IP address on Alibaba Cloud
ikev2 keychain to_ali_key1
 peer to-ali-peer1
  address 39.XX.XX.17 32
  identity address 39.XX.XX.17
  pre-shared-key plaintext ChangeMe****
  quit
 quit
ikev2 keychain to_ali_key2
 peer to-ali-peer2
  address 39.XX.XX.10 32
  identity address 39.XX.XX.10
  pre-shared-key plaintext ChangeMe****
  quit
 quit

#Configure the IKEv2 profile. The two peers correspond to the two tunnels on Alibaba Cloud
ikev2 profile to-ali-profile1
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key1
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.17 32
 sa duration 86400
 dpd interval 30 periodic
 quit

ikev2 profile to-ali-profile2
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key2
 identity local address 116.XX.XX.68
 match remote identity address 39.XX.XX.10 32
 sa duration 86400
 dpd interval 30 periodic
 quit


#Configure the IPsec profile and reference the IKEv2 profile created above
#We recommend that you use only time-based SA duration. If you need to set a traffic-based value, set the traffic-based value to the maximum
ipsec profile to-ali-profile1 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile1
 sa duration time-based 86400
 quit

ipsec profile to-ali-profile2 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile2
 sa duration time-based 86400
 quit

#Configure the tunnel interface and apply the IPsec policy to the tunnel interface
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile1
 source 10.32.0.175
 destination 39.XX.XX.17
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 3/0
 tunnel protection ipsec profile to-ali-profile2
 source 10.33.0.238
 destination 39.XX.XX.10
 quit

#Configure a route for the peer private CIDR block to point to the tunnel interface. tunnel1 is the active tunnel and has a higher route priority
ip route-static 192.168.0.0 16 Tunnel 1 preference 10
ip route-static 192.168.0.0 16 Tunnel 2 preference 20
Step 4: Security policy configuration
Configure a security policy to allow IKE protocol traffic and IPsec data traffic to pass through.
The configuration in this example is simplified. Add fine-grained rules as needed.
If multiple CIDR blocks on the on-premises IDC side need to communicate with the VPC, we recommend that you use destination-based routing mode to connect to the H3C device. For more information, see Recommended configuration solutions for multiple CIDR blocks.
#Configure the security zone to allow IKE negotiation packets and IPsec data packets. The configuration is simplified here. If you need fine-grained rules, add them as needed.
acl advanced 3001
 rule 0 permit ip
 quit
zone-pair security source any destination any
 packet-filter 3001
 quit
Step 5: Verify results
On the data center side, after you configure the route from the data center client to the H3C device, you can start testing the network connectivity between the data center and the Alibaba Cloud VPC, and verify failover.
Test the connectivity between the data center and the VPC: Log on to an ECS instance in the VPC, run
ping <private IP address of the data center server>. If a reply packet from the data center server is received, the communication is normal.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC and run
ping <private IP address of the data center server> -c 10000to continuously send access packets to the data center.Interrupt the active tunnel of the IPsec-VPN connection: You can modify the pre-shared key of the active tunnel of the IPsec-VPN connection. The active tunnel is then interrupted because the pre-shared keys on the two ends are inconsistent.
After the active tunnel is interrupted, observe the communication status of the ECS instance in the VPC: If the traffic recovers after a brief interruption, it indicates that after the active tunnel is interrupted, the traffic automatically communicates through the standby tunnel.
Dual egresses + BGP routing
In a dual public IP and dual egresses scenario, you can bind the two egresses of the H3C device to two Tunnel interfaces respectively, and configure different IPsec profiles for them, to connect to the active and standby tunnels of Alibaba Cloud.
Step 1: Configure interfaces and networking
Configure IP addresses and security zones for the public interface and the private interface respectively, and configure routes.
# Configure Public Interface 1.
interface GigabitEthernet 2/0
 ip addr 10.32.0.175 24
 quit

# Configure Public Interface 2.
interface GigabitEthernet 3/0
 ip addr 10.33.0.238 24
 quit

# Configure a private interface.
interface GigabitEthernet 4/0
 ip addr 10.34.0.10 24
 quit

# Add the public and private interfaces to their respective security zone.
security-zone name Untrust
 import interface GigabitEthernet 2/0
 import interface GigabitEthernet 3/0
 quit
security-zone name Trust
 import interface GigabitEthernet 4/0
 quit

# Configure 32-bit routes for peer VPN gateway public IPs (Internet).
ip route-static 39.XX.XX.17 32 10.32.0.173
ip route-static 39.XX.XX.10 32 10.33.0.236
# Configure a route for the local internal network CIDR block.
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Tunnel configuration
Create two Tunnel interfaces to connect to the active and standby tunnels on the cloud.
# Configure the tunnel interfaces and apply IPsec to the tunnel interfaces.
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 3/0
 quit

# Add the tunnel interfaces to the Untrust security zone.
security-zone name Untrust
 import interface Tunnel 1
 import interface Tunnel 2
 quit
Step 3: IPsec transform set and policy configuration
Configure IPsec and IKE, and make sure the configuration is consistent with the Alibaba Cloud side.
#Configure the IPsec transform set
ipsec transform-set to-ali-trans
 encapsulation-mode tunnel
 protocol esp
 esp authentication-algorithm sha256
 esp encryption-algorithm aes-cbc-256
 pfs dh-group14
 quit

#Configure the IKEv2 proposal and IKE security policy
ikev2 proposal to-ali-prop
 dh group14
 encryption aes-cbc-256
 integrity sha256
 prf sha256
 quit
ikev2 policy to-ali-policy
 priority 1
 proposal to-ali-prop
 quit

#Configure the IKE keychain. The two peers correspond to the two tunnels on Alibaba Cloud respectively, and the address is the public IP address on Alibaba Cloud
ikev2 keychain to_ali_key1
 peer to-ali-peer1
  address 39.XX.XX.17 32
  identity address 39.XX.XX.17
  pre-shared-key plaintext ChangeMe****
  quit
 quit
ikev2 keychain to_ali_key2
 peer to-ali-peer2
  address 39.XX.XX.10 32
  identity address 39.XX.XX.10
  pre-shared-key plaintext ChangeMe****
  quit
 quit

#Configure the IKEv2 profile. The two peers correspond to the two tunnels on Alibaba Cloud respectively
ikev2 profile to-ali-profile1
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key1
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.17 32
 sa duration 86400
 dpd interval 30 periodic
 quit

ikev2 profile to-ali-profile2
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key2
 identity local address 116.XX.XX.68
 match remote identity address 39.XX.XX.10 32
 sa duration 86400
 dpd interval 30 periodic
 quit


#Configure the IPsec profile and reference the IKEv2 profile created above
#We recommend that you use only time-based SA duration. If you need to configure traffic-based duration, set the traffic-based value to the maximum
ipsec profile to-ali-profile1 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile1
 sa duration time-based 86400
 quit

ipsec profile to-ali-profile2 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile2
 sa duration time-based 86400
 quit

#Configure the tunnel interface and apply the IPsec policy to the tunnel interface
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile1
 source 10.32.0.175
 destination 39.XX.XX.17
 quit
interface tunnel 2 mode ipsec
 ip address unnumbered interface GigabitEthernet 3/0
 tunnel protection ipsec profile to-ali-profile2
 source 10.33.0.238
 destination 39.XX.XX.10
 quit

#Configure a route for the peer intranet CIDR block that points to the tunnel interface. Tunnel1 is the active tunnel and has a higher route priority
ip route-static 192.168.0.0 16 Tunnel 1 preference 10
ip route-static 192.168.0.0 16 Tunnel 2 preference 20
Step 4: Security policy configuration
Configure a security policy to allow IKE protocol traffic and IPsec data traffic to pass through.
The example here is a simplified configuration. Add fine-grained rules as needed based on your actual requirements.
If multiple CIDR blocks on the on-premises IDC side need to communicate with the VPC, we recommend that you use Destination-based routing mode to connect to the H3C device. For more information, see Recommended configuration solutions for multiple CIDR blocks.
#Configure the security zone to allow IKE negotiation packets and IPsec data packets. The configuration here is simplified. Add fine-grained rules as needed
acl advanced 3001
 rule 0 permit ip
 quit
zone-pair security source any destination any
 packet-filter 3001
 quit
Step 5: BGP dynamic routing configuration
# Configure IP addresses for the tunnel interfaces to establish BGP peering with the VPN gateway on Alibaba Cloud.
interface tunnel 1 mode ipsec
 ip address 169.254.10.2 30
 quit
interface tunnel 2 mode ipsec
 ip address 169.254.20.2 30
 quit

# Delete the static routes that point to the tunnels in the static routing scenario.
undo ip route-static 192.168.0.0 16 Tunnel 1 preference 10
undo ip route-static 192.168.0.0 16 Tunnel 2 preference 20

# Configure BGP dynamic routing. The H3C firewall advertises 10.0.0.0/8 to the VPN gateway on Alibaba Cloud.
bgp 65500
peer 169.254.10.1 as-number 65535
peer 169.254.20.1 as-number 65535
address-family ipv4 unicast
peer 169.254.10.1 enable
peer 169.254.20.1 enable
network 10.0.0.0 8  # Advertise the CIDR block 10.0.0.0/8.
After the configuration is complete, view the BGP connection:
Check the BGP dynamic routing.
Check the route table.
Step 6: Verify results
On the data center side, after configuring the route from the data center client to the H3C device, you can start to test the network connectivity between the data center and the Alibaba Cloud VPC, and verify failover.
Test the connectivity between the data center and the VPC: Log on to an ECS instance in the VPC, run
ping <private IP address of the data center server>. If a reply packet from the data center server is received, the communication is normal.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC and run
ping <private IP address of the data center server> -c 10000to continuously send access packets to the data center.Interrupt the active tunnel of the IPsec-VPN connection: You can modify the pre-shared key of the active tunnel of the IPsec-VPN connection. The active tunnel is then interrupted because the pre-shared keys on the two ends are inconsistent.
After the active tunnel is interrupted, observe the communication status of the ECS instance in the VPC: If the traffic recovers after a brief interruption, it indicates that after the active tunnel is interrupted, the traffic automatically communicates through the standby tunnel.
Single-tunnel mode
Scenario

Take the scenario shown in the preceding figure as an example:
A company has a data center on-premises. The CIDR block that needs to communicate with Alibaba Cloud in the data center is 10.34.0.0/24.
The company has a virtual private cloud (VPC) on Alibaba Cloud. The VPC CIDR block is 192.168.0.0/16, and application services are deployed in the VPC by using Elastic Compute Service (ECS).
The company plans to establish single-tunnel mode IPsec-VPN connections between the data center and the VPC in the cloud to enable mutual resource access.
For single-tunnel mode, this topic provides only a configuration example for static routing.
IP address plan
For details about the network configuration involved in this example, see the following table.
Location | Configuration item | Example value |
Data center | H3C device address | GE2 (Internet egress): 10.32.0.175/24 Next hop: 10.32.0.173 Mapped public IP address: 8.XX.XX.3 |
GE4 (private interface): 10.34.0.20/24 | ||
Server IP | 10.34.0.21 | |
Alibaba Cloud | VPN gateway address | 39.XX.XX.17 |
VPC CIDR block | 192.168.0.0/16 | |
vSwitch CIDR block | 192.168.1.0/24 | |
ECS IP address | 192.168.1.11 |
IPsec-VPN connection configuration plan
The IPsec-VPN connection configuration on the Alibaba Cloud side and the H3C firewall side must be the same.
Configuration item | Example value | |
Pre-shared key | ChangeMe**** | |
IKE | Version | ikev2 |
Negotiation mode | main | |
Encryption algorithm | aes256 | |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
IPsec | Encryption algorithm | aes256 |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
Prerequisites
You have created a VPN gateway, created a customer gateway, created an IPsec-VPN connection, and configured routes for the VPN gateway on the Alibaba Cloud side. For more information, see Single-tunnel mode.
Procedure
This topic uses the H3C vFW1k E1185 version for the configuration example. The firewall configuration may vary depending on the model and version. You can perform the configuration by referring to the corresponding documentation or consulting the firewall vendor based on the version that you actually use.
Static routing
Step 1: Configure interfaces and networking
Configure IP addresses and security zones for the Internet-facing interface and the private interface of the H3C device, and configure routes.
# Configure a public interface.
interface GigabitEthernet 2/0
 ip addr 10.32.0.175 24
 quit

# Configure a private interface.
interface GigabitEthernet 4/0
 ip addr 10.34.0.10 24
 quit

# Add the public and private interfaces to their respective security zone.
security-zone name Untrust
 import interface GigabitEthernet 2/0
 quit
security-zone name Trust
 import interface GigabitEthernet 4/0
 quit

# Configure routes for peer VPN gateway public IPs (Internet egress).
ip route-static 39.XX.XX.17 32 10.32.0.173
ip route-static 39.XX.XX.10 32 10.32.0.173
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Tunnel configuration
Create a tunnel interface to connect to the tunnel on the cloud side.
# Configure the tunnel interface and apply IPsec to the tunnel interface.
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 quit

# Add the tunnel interface to the Untrust security zone.
security-zone name Untrust
 import interface Tunnel 1
 quit
Step 3: IPsec transform set and policy configuration
Configure IPsec and IKE. Make sure the configurations are consistent with those on the Alibaba Cloud side.
# Configure an IPsec transform set.
ipsec transform-set to-ali-trans
 encapsulation-mode tunnel
 protocol esp
 esp authentication-algorithm sha256
 esp encryption-algorithm aes-cbc-256
 pfs dh-group14
 quit

# Configure an IKEv2 proposal and policy.
ikev2 proposal to-ali-prop
 dh group14
 encryption aes-cbc-256
 integrity sha256
 prf sha256
 quit
ikev2 policy to-ali-policy
 priority 1
 proposal to-ali-prop
 quit

# Configure IKEv2 keychains — one per tunnel, pointing to the active and standby tunnel IPs.
ikev2 keychain to_ali_key1
 peer to-ali-peer1
  address 39.XX.XX.17 32
  identity address 39.XX.XX.17
  pre-shared-key plaintext ChangeMe****
  quit
 quit

 peer to-ali-peer2
ikev2 profile to-ali-profile1
 authentication-method local pre-share
 authentication-method remote pre-share
 keychain to_ali_key1
 identity local address 8.XX.XX.3
 match remote identity address 39.XX.XX.17 32
 sa duration 86400
 dpd interval 30 periodic
 quit

 keychain to_ali_key1
ipsec profile to-ali-profile1 isakmp
 transform-set to-ali-trans
 ikev2-profile to-ali-profile1
 dpd interval 30 periodic
 sa duration time-based 86400
 quit

 authentication-method local pre-share
interface tunnel 1 mode ipsec
 ip address unnumbered interface GigabitEthernet 2/0
 tunnel protection ipsec profile to-ali-profile1
 source 10.32.0.175
 destination 39.XX.XX.17
 quit

#Configure a route for the peer intranet CIDR block to point to the tunnel interface
ip route-static 192.168.0.0 16 Tunnel 1 preference 10
Step 4: Security policy configuration
Configure a security policy to allow IKE protocol traffic and IPsec data traffic to pass through.
The example here is a simplified configuration. Add fine-grained rules as needed.
If multiple CIDR blocks on the on-premises data center side need to communicate with the VPC, we recommend that you use Destination-based routing mode to connect to the H3C firewall. For more information, see Recommended configuration solutions for multiple CIDR blocks.
# Configure an ACL to allow IKE negotiation packets and IPsec data packets between the Untrust security zone and any other zone. In this example, the configurations are simplified. You can configure a fine-grained ACL based on your business requirements.
acl advanced 3001
 rule 0 permit ip
 quit
zone-pair security source any destination any
 packet-filter 3001
 quit
Step 5: Verify results
On the data center side, after you configure routes from the data center servers to the H3C device, you can start to test the network connectivity between the data center and the Alibaba Cloud VPC.
Log on to an ECS instance that is not assigned a public IP address in the VPC. For more information, see Connection method overview.
Run the ping command to ping a server in the data center to test the network connectivity.
If you can receive echo reply packets, the connection is established.