Huawei firewall configuration examples
To connect an on-premises data center to an Alibaba Cloud virtual private cloud (VPC) using an IPsec-VPN connection, you must configure your on-premises gateway device after you configure the VPN Gateway on Alibaba Cloud. This topic uses a Huawei firewall as an example to describe how to add VPN configurations to an on-premises gateway device.
In the scenario described in this topic, a Huawei firewall in an on-premises data center uses two public IP addresses to establish a dual-tunnel IPsec-VPN connection with Alibaba Cloud. If the VPN Gateway that you created supports only single-tunnel IPsec-VPN connections, see the Single-tunnel mode configuration example section at the end of this topic.
We recommend that you upgrade your IPsec-VPN connection to dual-tunnel mode. A dual-tunnel IPsec-VPN connection supports zone-disaster recovery and provides high availability.
Dual-tunnel mode
Scenario

For example, consider the scenario in the graph above:
A company has an on-premises data center. The CIDR block of the data center that needs to communicate with Alibaba Cloud is 10.34.0.0/24.
The company has a VPC on Alibaba Cloud. The CIDR block of the VPC is 192.168.0.0/16. Applications are deployed on Elastic Compute Service (ECS) instances in the VPC.
The company wants to establish a dual-tunnel IPsec-VPN connection between the on-premises data center and the VPC to allow resource access.
Address planning
This topic provides two scenario examples based on the number of public egresses on the Huawei firewall:
Single egress: The Huawei firewall is configured with one public egress that corresponds to one public IP address.
Dual egress: The Huawei firewall is configured with two public egresses that correspond to two public IP addresses.
You can view the address planning for your Huawei firewall based on its configuration.
Single egress
The following describes the address planning.
Location | Configuration item | Example value |
On-premises data center | Huawei firewall interface address | GE1/0/0 (public egress) address: 10.32.0.174 Egress next hop: 10.32.0.173 Mapped public IP address: 1.1.XX.XX |
GE1/0/2 (private interface): 10.34.0.9 | ||
Private CIDR block | 10.34.0.0/24 | |
Server IP | 10.34.0.1 | |
Alibaba Cloud | VPN Gateway address | Primary tunnel: 3.3.XX.XX Standby tunnel: 4.4.XX.XX |
VPC CIDR block | 192.168.0.0/16 | |
vSwitch CIDR block | Zone J: 192.168.1.0/24 Zone K: 192.168.2.0/24 | |
ECS address | 192.168.1.1 |
Dual egress
The following describes the address planning.
Location | Configuration item | Example value |
On-premises data center | Huawei firewall interface address | GE1/0/0 (public egress 1): 10.32.0.174 Egress next hop: 10.32.0.173 Mapped public IP address: 1.1.XX.XX |
GE1/0/1 (public egress 2): 10.33.0.237 Egress next hop: 10.33.0.236 Mapped public IP address: 2.2.XX.XX | ||
GE1/0/2 (private interface): 10.34.0.9 | ||
Private CIDR block | 10.34.0.0/24 | |
Server IP | 10.34.0.1 | |
Alibaba Cloud | VPN Gateway address | Active tunnel: 3.3.XX.XX Standby tunnel: 4.4.XX.XX |
VPC CIDR block | 192.168.0.0/16 | |
vSwitch CIDR block | Zone J: 192.168.1.0/24 Zone K: 192.168.2.0/24 | |
ECS address | 192.168.1.1 |
BGP planning
This topic describes how to configure a Huawei firewall for an IPsec-VPN connection that uses static routes or BGP dynamic routing. If you do not need to use BGP dynamic routing, you can skip this section. The following table describes the BGP address plan used in this topic.
Resource | Tunnel | BGP tunnel CIDR block | BGP IP address | BGP AS number (local autonomous system number) |
Alibaba Cloud VPN Gateway | Tunnel 1 | 169.254.10.0/30 Note The CIDR block of each tunnel must be unique within a VPN gateway instance. | 169.254.10.1 | 45104 |
Tunnel 2 | 169.254.20.0/30 | 169.254.20.1 | ||
Huawei firewall | Tunnel 1 | 169.254.10.0/30 | 169.254.10.2 | 45001 |
Tunnel 2 | 169.254.20.0/30 | 169.254.20.2 |
IPsec connection configuration planning
In dual-tunnel mode, Tunnel 1 (active tunnel) and Tunnel 2 (standby tunnel) use the same example values.
For each tunnel, the IPsec connection configurations on the Alibaba Cloud side and the Huawei firewall side must be the same.
Configuration item | Example value | |
Pre-shared key | ChangeMe**** | |
IKE | Version | ikev2 |
Negotiation mode | main | |
Encryption algorithm | aes256 | |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
IPsec | Encryption algorithm | aes256 |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
Prerequisites
Before you configure the Huawei firewall, you must create a VPN Gateway, a customer gateway, and an IPsec-VPN connection, and then configure routes for the VPN Gateway on Alibaba Cloud.
For static routes, see Establish a connection between a VPC and an on-premises data center (dual-tunnel mode).
For BGP dynamic routing, see Establish a connection between a VPC and an on-premises data center (dual-tunnel mode and BGP routes).
The customer gateway configuration varies based on your scenario:
Single egress: Create one customer gateway. When you create the IPsec-VPN connection, select the same customer gateway for both tunnels.
Dual egress: Create two customer gateways. When you create the IPsec-VPN connection, select the corresponding customer gateway for each tunnel.
Procedure
This topic uses a Huawei USG6000V2 firewall for demonstration. The configurations may vary based on the model and version of your firewall. Configure your firewall based on the documentation for your firewall version or contact the firewall vendor.
This topic provides configuration examples for four scenarios. Select the tab that applies to your scenario to view the configuration steps.
Single egress with static routes
In a single-egress scenario that uses a single public IP address, you can bind the single egress of the Huawei firewall to two tunnel interfaces and configure a different IPsec policy for each interface. This allows the firewall to connect to the active and standby tunnels on Alibaba Cloud. The route injection feature of the IPsec policy automatically generates routes that point to the tunnels and switches traffic based on the IPsec tunnel negotiation status.
Step 1: Configure the network interfaces
Configure IP addresses and security domains for the public and private interfaces of the Huawei firewall, and configure routes.
#Public interface
interface GigabitEthernet1/0/0
 ip addr 10.32.0.174 24
 service-manage ping permit
 quit

#Private interface
interface GigabitEthernet1/0/2
 ip addr 10.34.0.9 24
 service-manage ping permit
 quit

#Add the public and private interfaces to security domains
firewall zone untrust
 add interface GigabitEthernet 1/0/0
 quit
firewall zone trust
 add interface GigabitEthernet 1/0/2
 quit

#Configure 32-bit routes that point to the public IP addresses of the peer VPN gateway
ip route-static 3.3.XX.XX 32 10.32.0.174
ip route-static 4.4.XX.XX 32 10.32.0.174
#Configure a route that points from the on-premises CIDR block to the private network
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Configure the tunnels
Create two tunnel interfaces to connect to the active and standby tunnels on the cloud.
#Configure tunnel interfaces and apply the IPsec security framework to the tunnel interfaces
interface tunnel 1
 tunnel-protocol ipsec
 ip address unnumbered interface GigabitEthernet1/0/0
 service-manage ping permit
 quit
interface tunnel 2
 tunnel-protocol ipsec
 ip address unnumbered interface GigabitEthernet1/0/0
 service-manage ping permit
 quit

#Add the tunnel interfaces to a security domain
firewall zone untrust
 add interface Tunnel 1
 add interface Tunnel 2
 quit
Step 3: Configure IPsec proposals and policies
Configure IPsec and IKE. Make sure that the configurations are consistent with the configurations on the Alibaba Cloud side.
#Configure an IPsec proposal
ipsec proposal to-ali-prop
 encapsulation-mode tunnel
 esp authentication-algorithm sha2-256
 esp encryption-algorithm aes-256
 quit

#Configure an IKE proposal
ike proposal 1
 dh group14
 authentication-method pre-share
 encryption-algorithm aes-256
 integrity-algorithm hmac-sha2-256
 prf hmac-sha2-256
 sa duration 86400
 quit

#Configure IKE peers. The two peers correspond to the two tunnels on Alibaba Cloud. The remote-address is the public IP address on Alibaba Cloud.
ike peer to-ali-peer1
 version 2
 ike-proposal 1
 remote-address 3.3.XX.XX
 pre-shared-key ChangeMe****
 remote-id-type none
 local-id 1.1.XX.XX
 dpd type periodic
 quit
ike peer to-ali-peer2
 version 2
 ike-proposal 1
 remote-address 4.4.XX.XX
 pre-shared-key ChangeMe****
 remote-id-type none
 local-id 1.1.XX.XX
 dpd type periodic
 quit

#Configure the traffic selector. In this example, an address set is used.
ip address-set to-ali-subnets type group
 address 0 192.168.0.0 mask 16
 quit
ip address-set local-subnets type group
 address 0 10.34.0.0 mask 16
 quit
acl number 3000
 rule 5 permit ip source address-set local-subnets destination address-set to-ali-subnets
 quit

#Configure an IPsec policy, reference the created ACL, IKE peer, and IPsec proposal, and set the priority for routes that are automatically generated by the route injection feature. In this example, you only need to set the priority of Tunnel1 higher than that of Tunnel2. The specific values depend on your network plan.
ipsec policy to-ali-policy1 1 isakmp
 security acl 3000
 pfs dh-group14
 ike-peer to-ali-peer1
 proposal to-ali-prop
 tunnel local applied-interface
 sa duration traffic-based 0
 sa duration time-based 86400
 route inject dynamic preference 100
 quit
ipsec policy to-ali-policy2 1 isakmp
 security acl 3000
 pfs dh-group14
 ike-peer to-ali-peer2
 proposal to-ali-prop
 tunnel local applied-interface
 sa duration traffic-based 0
 sa duration time-based 86400
 route inject dynamic preference 120
 quit

#Configure the tunnel interfaces and apply the IPsec policies to the tunnel interfaces
interface tunnel 1
 ip address unnumbered interface GigabitEthernet1/0/0
 tunnel-protocol ipsec
 service-manage ping permit
 ipsec policy to-ali-policy1
 quit
interface tunnel 2
 ip address unnumbered interface GigabitEthernet1/0/0
 tunnel-protocol ipsec
 service-manage ping permit
 ipsec policy to-ali-policy2
 quit
Step 4: Configure security policies
Configure security policies to allow IKE protocol traffic and IPsec data traffic.
The following configurations are for demonstration purposes only. Add fine-grained rules as needed.
If multiple CIDR blocks in the on-premises data center need to communicate with the VPC, we recommend that you use destination-based routes to connect to the Huawei firewall. For more information, see Recommended configurations for multiple CIDR blocks.
#Configure an inter-domain security policy between the Local and Untrust domains to allow IKE negotiation messages
security-policy
rule name policy1
source-zone local
source-address 10.32.0.174 32
destination-zone untrust
destination-address 3.3.XX.XX 32
destination-address 4.4.XX.XX 32
action permit
quit
rule name policy2
source-zone untrust
source-address 3.3.XX.XX 32
source-address 4.4.XX.XX 32
destination-zone local
destination-address 10.32.0.174 32
action permit
quit
quit

#Configure an inter-domain security policy between the Trust and Untrust domains to allow data datagrams
security-policy
rule name policy3
source-zone trust
source-address 10.0.0.0 8
destination-zone untrust
destination-address 192.168.0.0 16
action permit
quit
rule name policy4
source-zone untrust
source-address 192.168.0.0 16
destination-zone trust
destination-address 10.0.0.0 8
action permit
quit
quit
Step 5: Verify the results
After you configure a route from the on-premises server to the Huawei firewall, you can test the network connectivity between the on-premises data center and the Alibaba Cloud VPC and verify the active/standby switchover.
Test the connectivity between the data center and the VPC. To do this, log on to an ECS instance in the VPC and run the
ping <private IP address of a server in the data center>command. If you receive a reply message from the server in the data center, the connection is established.Test the high availability of the IPsec-VPN connection.
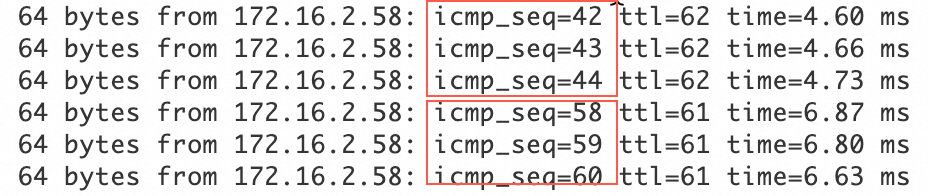
Log on to an ECS instance in the VPC. Run the
ping <private IP address of a server in the data center> -c 10000command to continuously send ping requests to the data center.Disconnect the active tunnel of the IPsec-VPN connection. You can do this by modifying the pre-shared key of the active tunnel. The tunnel disconnects because the pre-shared keys at the two ends of the tunnel no longer match.
After the active tunnel is disconnected, check the communication status of the ECS instance in the VPC. If traffic is briefly interrupted and then resumes, this indicates that traffic is automatically switched to the standby tunnel.
Single egress with BGP routes
In this example, the following configurations are added to the configurations in the "Single egress with static routes" scenario.
Step 1: Configure BGP
After you complete Step 1 to Step 4 in the "Single egress with static routes" scenario, perform the following configurations.
#Disable route injection
ipsec policy to-ali-policy1 1 isakmp
 undo route inject
 sa trigger-mode auto
quit

ipsec policy to-ali-policy2 1 isakmp
 undo route inject
 sa trigger-mode auto
quit

#Set the source and destination of the traffic selector to any
acl number 3000
 undo rule 5
 rule 10 permit ip
 quit

#Change the IP addresses of the tunnel interfaces to 169.254.X.X addresses. The IP addresses must be in the same CIDR block as the BGP IP addresses on Alibaba Cloud.
interface Tunnel1
 ip address 169.254.10.2 30
 quit
interface Tunnel2
 ip address 169.254.20.2 30
 quit

#Change the tunnel local address of the IPsec policy to the public interface address
ipsec policy to-ali-policy1 1 isakmp
 tunnel local 10.32.0.174
 quit
ipsec policy to-ali-policy2 1 isakmp
 tunnel local 10.32.0.174
 quit

#Configure the local and peer BGP settings
bgp 45001
 router-id 169.254.10.2
 peer 169.254.10.1 as-number 45104
 peer 169.254.20.1 as-number 45104
 ipv4-family unicast
  undo synchronization
  network 10.34.0.0 255.255.255.0
  peer 169.254.10.1 enable
  peer 169.254.20.1 enable

#Add a security policy
security-policy
 rule name policy1
  source-address 169.254.0.0 16
 quit
 rule name policy2
  destination-address 169.254.0.0 16
 quit
quit
Step 2: Verify the results
You can test the network connectivity between the on-premises data center and the Alibaba Cloud VPC and verify the active/standby switchover.
Test the connectivity between the data center and the VPC. To do this, log on to an ECS instance in the VPC and run the
ping <private IP address of a server in the data center>command. If you receive a reply message from the server in the data center, the connection is established.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC. Run the
ping <private IP address of a server in the data center> -c 10000command to continuously send ping requests to the data center.Disconnect the active tunnel of the IPsec-VPN connection. You can do this by modifying the pre-shared key of the active tunnel. The tunnel disconnects because the pre-shared keys at the two ends of the tunnel no longer match.
After the active tunnel is disconnected, check the communication status of the ECS instance in the VPC. If traffic is briefly interrupted and then resumes, this indicates that traffic is automatically switched to the standby tunnel.
Dual egress with static routes
In a dual-egress scenario that uses two public IP addresses, you can bind the two egresses of the Huawei firewall to two tunnel interfaces and configure a different IPsec policy for each interface. This allows the firewall to connect to the active and standby tunnels on Alibaba Cloud. The route injection feature of the IPsec policy automatically generates routes that point to the tunnels and switches traffic based on the IPsec tunnel negotiation status.
Step 1: Configure the network interfaces
Configure IP addresses and security domains for the public and private interfaces, and configure routes.
#Public interface 1
interface GigabitEthernet1/0/0
 ip addr 10.32.0.174 24
 service-manage ping permit
 quit

#Public interface 2
interface GigabitEthernet1/0/1
 ip addr 10.33.0.237 24
 service-manage ping permit
 quit

#Private interface
interface GigabitEthernet1/0/2
 ip addr 10.34.0.9 24
 service-manage ping permit
 quit

#Add the public and private interfaces to security domains
firewall zone untrust
 add interface GigabitEthernet 1/0/0
 add interface GigabitEthernet 1/0/1
 quit
firewall zone trust
 add interface GigabitEthernet 1/0/2
 quit

#Configure 32-bit routes that point to the public IP addresses of the peer VPN gateway
ip route-static 3.3.XX.XX 32 10.32.0.174
ip route-static 4.4.XX.XX 32 10.33.0.237
#Configure a route that points from the on-premises CIDR block to the private network
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Configure the tunnels
Create two tunnel interfaces to connect to the active and standby tunnels on the cloud.
#Configure tunnel interfaces and apply the IPsec security framework to the tunnel interfaces
interface tunnel 1
 tunnel-protocol ipsec
 ip address unnumbered interface GigabitEthernet1/0/0
 service-manage ping permit
 quit
interface tunnel 2
 tunnel-protocol ipsec
 ip address unnumbered interface GigabitEthernet1/0/1
 service-manage ping permit
 quit

#Add the tunnel interfaces to a security domain
firewall zone untrust
 add interface Tunnel 1
 add interface Tunnel 2
 quit
Step 3: Configure IPsec proposals and policies
Configure IPsec and IKE. Make sure that the configurations are consistent with the configurations on the Alibaba Cloud side.
#Configure an IPsec proposal
ipsec proposal to-ali-prop
 encapsulation-mode tunnel
 esp authentication-algorithm sha2-256
 esp encryption-algorithm aes-256
 quit

#Configure an IKE proposal
ike proposal 1
 dh group14
 authentication-method pre-share
 encryption-algorithm aes-256
 integrity-algorithm hmac-sha2-256
 prf hmac-sha2-256
 sa duration 86400
 quit

#Configure IKE peers. The two peers correspond to the two tunnels on Alibaba Cloud. The remote-address is the public IP address on Alibaba Cloud.
ike peer to-ali-peer1
 version 2
 ike-proposal 1
 remote-address 3.3.XX.XX
 pre-shared-key ChangeMe****
 remote-id-type none
 local-id 1.1.XX.XX
 dpd type periodic
 quit
ike peer to-ali-peer2
 version 2
 ike-proposal 1
 remote-address 4.4.XX.XX
 pre-shared-key ChangeMe****
 remote-id-type none
 local-id 2.2.XX.XX
 dpd type periodic
 quit

#Configure the traffic selector. In this example, an address set is used.
ip address-set to-ali-subnets type group
 address 0 192.168.0.0 mask 16
 quit
ip address-set local-subnets type group
 address 0 10.34.0.0 mask 16
 quit
acl number 3000
 rule 5 permit ip source address-set local-subnets destination address-set to-ali-subnets
 quit

#Configure an IPsec policy, reference the created ACL, IKE peer, and IPsec proposal, and set the priority for routes that are automatically generated by the route injection feature. In this example, you only need to set the priority of Tunnel1 higher than that of Tunnel2. The specific values depend on your network plan.
ipsec policy to-ali-policy1 1 isakmp
 security acl 3000
 pfs dh-group14
 ike-peer to-ali-peer1
 proposal to-ali-prop
 tunnel local applied-interface
 sa duration traffic-based 0
 sa duration time-based 86400
 route inject dynamic preference 100
 quit
ipsec policy to-ali-policy2 1 isakmp
 security acl 3000
 pfs dh-group14
 ike-peer to-ali-peer2
 proposal to-ali-prop
 tunnel local applied-interface
 sa duration traffic-based 0
 sa duration time-based 86400
 route inject dynamic preference 120
 quit

#Configure the tunnel interfaces and apply the IPsec policies to the tunnel interfaces
interface tunnel 1
 ip address unnumbered interface GigabitEthernet1/0/0
 tunnel-protocol ipsec
 service-manage ping permit
 ipsec policy to-ali-policy1
 quit
interface tunnel 2
 ip address unnumbered interface GigabitEthernet1/0/1
 tunnel-protocol ipsec
 service-manage ping permit
 ipsec policy to-ali-policy2
 quit
Step 4: Configure security policies
Configure security policies to allow IKE protocol traffic and IPsec data traffic.
The following configurations are for demonstration purposes only. Add fine-grained rules as needed.
If multiple CIDR blocks in the on-premises data center need to communicate with the VPC, we recommend that you use destination-based routes to connect to the Huawei firewall. For more information, see Recommended configurations for multiple CIDR blocks.
#Configure an inter-domain security policy between the Local and Untrust domains to allow IKE negotiation messages
security-policy
rule name policy1
source-zone local
source-address 10.32.0.174 32
source-address 10.33.0.237 32
destination-zone untrust
destination-address 3.3.XX.XX 32
destination-address 4.4.XX.XX 32
action permit
quit
rule name policy2
source-zone untrust
source-address 3.3.XX.XX 32
source-address 4.4.XX.XX 32
destination-zone local
destination-address 10.32.0.174 32
destination-address 10.33.0.237 32
action permit
quit
quit

#Configure an inter-domain security policy between the Trust and Untrust domains to allow data datagrams
security-policy
rule name policy3
source-zone trust
source-address 10.0.0.0 8
destination-zone untrust
destination-address 192.168.0.0 16
action permit
quit
rule name policy4
source-zone untrust
source-address 192.168.0.0 16
destination-zone trust
destination-address 10.0.0.0 8
action permit
quit
quit
Step 5: Verify the results
After you configure a route from the on-premises client to the Huawei firewall, you can test the network connectivity between the on-premises data center and the Alibaba Cloud VPC and verify the active/standby switchover.
Test the connectivity between the data center and the VPC. To do this, log on to an ECS instance in the VPC and run the
ping <private IP address of a server in the data center>command. If you receive a reply message from the server in the data center, the connection is established.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC. Run the
ping <private IP address of a server in the data center> -c 10000command to continuously send ping requests to the data center.Disconnect the active tunnel of the IPsec-VPN connection. You can do this by modifying the pre-shared key of the active tunnel. The tunnel disconnects because the pre-shared keys at the two ends of the tunnel no longer match.
After the active tunnel is disconnected, check the communication status of the ECS instance in the VPC. If traffic is briefly interrupted and then resumes, this indicates that traffic is automatically switched to the standby tunnel.
Dual egress with BGP routes
In this example, the following configurations are added to the configurations in the "Dual egress with static routes" scenario.
Step 1: Configure BGP
After you complete Step 1 to Step 4 in the "Dual egress with static routes" scenario, perform the following configurations.
#Disable route injection
ipsec policy to-ali-policy1 1 isakmp
 undo route inject
 sa trigger-mode auto
quit

ipsec policy to-ali-policy2 1 isakmp
 undo route inject
 sa trigger-mode auto
quit

#Set the source and destination of the traffic selector to any
acl number 3000
 undo rule 5
 rule 10 permit ip
 quit

#Change the IP addresses of the tunnel interfaces to 169.254.X.X addresses. The IP addresses must be in the same CIDR block as the BGP IP addresses on Alibaba Cloud.
interface Tunnel1
 ip address 169.254.10.2 30
 quit
interface Tunnel2
 ip address 169.254.20.2 30
 quit

#Change the tunnel local address of the IPsec policy to the public interface address
ipsec policy to-ali-policy1 1 isakmp
 tunnel local 10.32.0.174
 quit
ipsec policy to-ali-policy2 1 isakmp
 tunnel local 10.33.0.237
 quit

#Configure the local and peer BGP settings
bgp 45001
 router-id 169.254.10.2
 peer 169.254.10.1 as-number 45104
 peer 169.254.20.1 as-number 45104
 ipv4-family unicast
  undo synchronization
  network 10.34.0.0 255.255.255.0
  peer 169.254.10.1 enable
  peer 169.254.20.1 enable

#Add a security policy
security-policy
 rule name policy1
  source-address 169.254.0.0 16
 quit
 rule name policy2
  destination-address 169.254.0.0 16
 quit
quit
Step 2: Verify the results
You can test the network connectivity between the on-premises data center and the Alibaba Cloud VPC and verify the active/standby switchover.
Test the connectivity between the data center and the VPC. To do this, log on to an ECS instance in the VPC and run the
ping <private IP address of a server in the data center>command. If you receive a reply message from the server in the data center, the connection is established.Test the high availability of the IPsec-VPN connection.
Log on to an ECS instance in the VPC. Run the
ping <private IP address of a server in the data center> -c 10000command to continuously send ping requests to the data center.Disconnect the active tunnel of the IPsec-VPN connection. You can do this by modifying the pre-shared key of the active tunnel. The tunnel disconnects because the pre-shared keys at the two ends of the tunnel no longer match.
After the active tunnel is disconnected, check the communication status of the ECS instance in the VPC. If traffic is briefly interrupted and then resumes, this indicates that traffic is automatically switched to the standby tunnel.
Single-tunnel mode
Example scenario

The following example is based on the scenario in the preceding graph:
A company has an on-premises data center. The CIDR block of the data center that needs to communicate with Alibaba Cloud is 10.34.0.0/24.
The company has a VPC on Alibaba Cloud. The CIDR block of the VPC is 192.168.0.0/16. Applications are deployed on ECS instances in the VPC.
The company wants to establish a single-tunnel IPsec-VPN connection between the on-premises data center and the VPC to allow resource access.
For single-tunnel mode, this topic provides only a configuration example that uses static routes.
Address planning
The following table describes the network configurations that are used in this example.
Location | Configuration item | Example value |
On-premises data center | Huawei firewall interface address | GE2 (public egress): 10.32.0.174/24 Egress next hop: 10.32.0.173 Mapped public IP address: 8.149.XX.XX |
GE4 (private interface): 10.34.0.9/24 | ||
Private CIDR block | 10.34.0.0/24 | |
Server IP | 10.34.0.1 | |
Alibaba Cloud | VPN Gateway address | 47.103.XX.XX |
VPC CIDR block | 192.168.0.0/16 | |
vSwitch CIDR block | 192.168.0.0/24 | |
ECS address | 192.168.0.1 |
IPsec connection configuration planning
The IPsec connection configurations on the Alibaba Cloud side and the Huawei firewall side must be the same.
Configuration item | Example value | |
Pre-shared key | ChangeMe**** | |
IKE | Version | ikev2 |
Negotiation mode | main | |
Encryption algorithm | aes256 | |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
IPsec | Encryption algorithm | aes256 |
Authentication algorithm | sha256 | |
DH group | group14 | |
SA lifetime (seconds) | 86400 | |
Prerequisites
You have created a VPN Gateway, a customer gateway, and an IPsec-VPN connection, and have configured routes for the VPN Gateway on Alibaba Cloud. For more information, see Establish a connection from a VPC to a data center (single-tunnel mode).
Procedure
This topic uses a Huawei USG6000V2 firewall for demonstration. The configurations may vary based on the model and version of your firewall. Configure your firewall based on the documentation for your firewall version or contact the firewall vendor.
Static routes
Step 1: Configure the network interfaces
Configure IP addresses and security domains for the public and private interfaces of the Huawei firewall, and configure routes.
#Public interface
interface GigabitEthernet1/0/0
 ip addr 10.32.0.174 24
 service-manage ping permit
 quit

#Private interface
interface GigabitEthernet1/0/2
 ip addr 10.34.0.9 24
 service-manage ping permit
 quit

#Add the public and private interfaces to security domains
firewall zone untrust
 add interface GigabitEthernet 1/0/0
 quit
firewall zone trust
 add interface GigabitEthernet 1/0/2
 quit

#Configure a route that points to the public IP address of the peer Alibaba Cloud VPN gateway
ip route-static 47.103.XX.XX 32 10.32.0.173

#Configure a route that points from the on-premises CIDR block to the private network
ip route-static 10.0.0.0 8 10.34.0.253
Step 2: Configure the tunnel
Create one tunnel interface to connect to the tunnel on the cloud.
#Configure a tunnel interface and apply the IPsec security framework to the tunnel interface
interface tunnel 1
 tunnel-protocol ipsec
 ip address unnumbered interface GigabitEthernet1/0/0
 service-manage ping permit
 quit


#Add the tunnel interface to a security domain
firewall zone untrust
 add interface Tunnel 1
 quit
Step 3: Configure IPsec proposals and policies
Configure IPsec and IKE. Make sure that the configurations are consistent with the configurations on the Alibaba Cloud side.
#Configure an IPsec proposal
ipsec proposal to-ali-prop
 encapsulation-mode tunnel
 esp authentication-algorithm sha2-256
 esp encryption-algorithm aes-256
 quit

#Configure an IKE proposal
ike proposal 1
 dh group14
 authentication-method pre-share
 encryption-algorithm aes-256
 integrity-algorithm hmac-sha2-256
 prf hmac-sha2-256
 sa duration 86400
 quit

#Configure an IKE peer. The remote-address is the public IP address of the Alibaba Cloud VPN gateway.
ike peer to-ali-peer1
 version 2
 ike-proposal 1
 remote-address 47.103.XX.XX
 pre-shared-key ChangeMe****
 remote-id-type none
 local-id 8.149.XX.XX
 dpd type periodic
 quit

#Configure the traffic selector. In this example, an address set is used.
ip address-set to-ali-subnets type group
 address 0 192.168.0.0 mask 16
 quit
ip address-set local-subnets type group
 address 0 10.34.0.0 mask 16
 quit
acl number 3000
 rule 5 permit ip source address-set local-subnets destination address-set to-ali-subnets
 quit

#Configure an IPsec policy, reference the created ACL, IKE peer, and IPsec proposal, and set the priority for routes that are automatically generated by the route injection feature. In this example, you only need to set the priority of Tunnel1 higher than that of Tunnel2. The specific values depend on your network plan.
ipsec policy to-ali-policy1 1 isakmp
 security acl 3000
 pfs dh-group14
 ike-peer to-ali-peer1
 proposal to-ali-prop
 tunnel local applied-interface
 sa duration traffic-based 0
 sa duration time-based 86400
 route inject dynamic preference 100
 quit

#Configure the tunnel interface and apply the IPsec policy to the tunnel interface
interface tunnel 1
 ip address unnumbered interface GigabitEthernet1/0/0
 tunnel-protocol ipsec
 service-manage ping permit
 ipsec policy to-ali-policy1
 quit
Step 4: Configure security policies
Configure security policies to allow IKE protocol traffic and IPsec data traffic.
The following configurations are for demonstration purposes only. Add fine-grained rules as needed.
If multiple CIDR blocks in the on-premises data center need to communicate with the VPC, we recommend that you use destination-based routes to connect to the Huawei firewall. For more information, see Recommended configurations for multiple CIDR blocks.
#Configure an inter-domain security policy between the Local and Untrust domains to allow IKE negotiation messages
security-policy
rule name policy1
source-zone local
source-address 10.32.0.174 32
destination-zone untrust
destination-address 47.103.XX.XX 32
action permit
quit
rule name policy2
source-zone untrust
source-address 47.103.XX.XX 32
destination-zone local
destination-address 10.32.0.174 32
action permit
quit
quit

#Configure an inter-domain security policy between the Trust and Untrust domains to allow data datagrams
security-policy
rule name policy3
source-zone trust
source-address 10.0.0.0 8
destination-zone untrust
destination-address 192.168.0.0 16
action permit
quit
rule name policy4
source-zone untrust
source-address 192.168.0.0 16
destination-zone trust
destination-address 10.0.0.0 8
action permit
quit
quit
Step 5: Verify the results
After you configure a route from the on-premises server to the Huawei firewall, you can test the network connectivity between the on-premises data center and the Alibaba Cloud VPC.
Log on to an ECS instance that is not assigned a public IP address in the VPC. For more information, see Connection method overview.
Run the ping command to ping a server in the data center to test the network connectivity.
If you can receive echo reply packets, the connection is established.