Encrypt private traffic over Express Connect with static routing
When an Express Connect circuit connects your data center to Alibaba Cloud, traffic traverses the dedicated link unencrypted by default. To meet security compliance requirements — preventing data breaches and tampering — you can overlay a private IPsec-VPN connection on the circuit and route traffic through encrypted tunnels instead.
Background information
Before you begin, we recommend that you first understand the principles of encrypting private network traffic over Express Connect circuits. For more information, see Encrypt Express Connect traffic.
If the on-premises gateway device supports the BGP dynamic routing protocol, we recommend that both the VBR instance and the private IPsec-VPN connection use the BGP dynamic routing protocol to implement private network traffic encryption over Express Connect circuits. For related tutorials, see Encrypt private traffic over Express Connect with BGP.
Scenario example
This topic uses the scenario shown in the following figure as an example. An enterprise has a data center (IDC, Internet Data Center) in Hangzhou and a VPC in the China (Hangzhou) region on Alibaba Cloud. Related services are deployed in the VPC by using Elastic Compute Service (ECS). As the business grows, the on-premises IDC needs to connect to the cloud. Based on certain security compliance requirements, the enterprise needs to use an Express Connect circuit and a transit router to implement private network communication between the on-premises IDC and the VPC. In addition, to reduce the risk of data leakage and prevent confidential enterprise data from being stolen or tampered with by internal or external personnel, the enterprise wants all traffic transmitted over the Express Connect circuit to be encrypted before being transmitted to Alibaba Cloud.
When the on-premises IDC implements private network communication with the VPC over an Express Connect circuit and a transit router, the enterprise can establish a private IPsec-VPN connection between the on-premises gateway device and the transit router, and use the private IPsec-VPN connection to encrypt the traffic that passes through the Express Connect circuit, meeting the enterprise's high requirements for network security.

Network planning
If you need to plan CIDR blocks for the on-premises IDC and related network instances yourself, ensure that there is no overlap between the CIDR blocks that need to communicate with each other.
Routing mechanism description
To implement private network traffic encryption over Express Connect circuits, you need to ensure that the traffic between the on-premises IDC and the VPC is transmitted preferentially through the private IPsec-VPN connection instead of the Express Connect circuit. This topic achieves this goal by controlling routes:
Traffic from the VPC to the on-premises IDC:
The transit router can learn the routes to the on-premises IDC through the VBR instance and the private IPsec-VPN connection respectively. Based on the route priority of the transit router, the routes learned through the VBR instance are preferred by default. This mechanism causes the traffic from the VPC to the on-premises IDC to be transmitted preferentially over the Express Connect circuit, which makes encryption impossible.
This topic avoids this issue by adding on-premises IDC CIDR blocks with different subnet masks. When you add an on-premises IDC CIDR block to the VBR instance, you must add a large CIDR block (that is, a shorter subnet mask). When you add an on-premises IDC CIDR block to the route table of the private IPsec-VPN connection, you must add a small CIDR block (that is, a longer subnet mask).
For example, if the CIDR block of the on-premises IDC is 192.168.0.0/16 and the CIDR block of the clients in the on-premises IDC that communicate with the VPC is 192.168.20.0/24, add the on-premises IDC CIDR block 192.168.0.0/16 to the VBR instance and add the specific client CIDR block 192.168.20.0/24 to the route table of the private IPsec-VPN connection. This ensures that the route learned through the private IPsec-VPN connection in the transit router is preferred, so that traffic from the VPC to the clients is preferentially encrypted and transmitted through the private IPsec-VPN connection.
Traffic from the on-premises IDC to the VPC:
Add routes to the VPC instance in the on-premises IDC, with the next hops pointing to the Express Connect circuit and the private IPsec-VPN connection respectively. Then, adjust the route priority to ensure that the route pointing to the private IPsec-VPN connection is preferred, so that traffic from the on-premises IDC to the VPC is preferentially encrypted and transmitted through the private IPsec-VPN connection.
The current routing mechanism also ensures that, after the private IPsec-VPN connection is interrupted, the on-premises IDC and the VPC can still achieve private network communication through the Express Connect circuit and the transit router, but the traffic is no longer encrypted.
CIDR block planning
Configuration objectives | CIDR block planning | IP address |
VPC |
|
|
VBR | 10.0.0.0/30 |
|
On-premises IDC | Client CIDR block: 192.168.20.0/24 | Client address: 192.168.20.6 |
On-premises gateway device CIDR block:
|
|
Prerequisites
You have created a VPC in the China (Hangzhou) region of Alibaba Cloud and deployed relevant services by using ECS. For more information, see Create a VPC with an IPv4 CIDR block.
Check the on-premises gateway device to ensure that it supports the standard IKEv1 and IKEv2 protocols so that it can establish a private IPsec-VPN connection with Alibaba Cloud. To confirm whether the on-premises gateway device supports the standard IKEv1 and IKEv2 protocols, consult the vendor of the on-premises gateway device.
Procedure
Step 1: Enable private network communication between the IDC and the VPC through an Express Connect circuit and a transit router
Step 1: Deploy an Express Connect circuit
Deploy an Express Connect circuit to connect the on-premises IDC to Alibaba Cloud.
Create an Express Connect circuit.
Apply for an Express Connect circuit in the China (Hangzhou) region. For more information, see Apply for Classic Mode or Shared circuit access process. In this topic, Dedicated Physical Connection is selected.
Create a VBR instance.
Log on to the Express Connect console.
In the left-side navigation pane, click Virtual Border Router (VBR).
In the top menu bar, select the China (Hangzhou) region.
The region of the VBR instance must be the same as the region to which the Express Connect circuit belongs.
On the Virtual Border Router (VBR) page, click Create VBR.
On the Create VBR panel, configure based on the following information, and then click OK.
The following lists only the configuration items that are strongly related to this topic. Keep the default settings for other configuration items. For more information, see Create and manage VBRs.
Configuration item
Description
Name
In this topic, enter VBR.
Physical Connection
In this topic, select the Dedicated Express Connect Circuits type, and then select the created Express Connect circuit interface.
VLAN ID
In this topic, enter 0.
IPv4 Address of Gateway at Alibaba Cloud Side
In this topic, enter 10.0.0.1.
IPv4 Address of Gateway at Customer Side
In this example, enter 10.0.0.2.
Subnet Mask (IPv4 Address)
In this example, enter 255.255.255.252.
Add a route destined for the on-premises IDC in the VBR instance.
On the Virtual Border Router (VBR) page, click the VBR instance ID.
Click the Route tab, and then click Add Route Entry under the Custom Route Entry tab.
On the Add Route Entry panel, configure based on the following information, and then click OK.
Configuration item
Route entry
Next Hop Type
Select Express Connect Circuit.
Destination CIDR Block
Enter the CIDR block 192.168.0.0/16 of the on-premises IDC.
Next Hop
Select the Express Connect circuit that you created.
ImportantWhen you add a route to the data center (IDC) in the VBR instance, we recommend that you add a large CIDR block to ensure that the routes to the data center (IDC) that the transit router subsequently learns over the private IPsec-VPN connection are more specific than the current routes and have a higher route priority.
Add a route to the VPC on the on-premises gateway device.
NoteIn this example, the software Adaptive Security Appliance (ASA) 9.19.1 is used to describe how to configure a Cisco firewall. The commands may vary with software versions. Consult the documentation or your vendor based on your actual environment during operations. For more information, see Configure local gateways.
The following content contains third-party product information, which is only for reference. Alibaba Cloud does not make guarantees or other forms of commitments for the performance and reliability of third-party products, or the potential impacts of operations performed by using these products.
ciscoasa> enable
Password: ********             # Enter the enable mode password.
ciscoasa# configure terminal   # Enter configuration mode.
ciscoasa(config)#
#The interface configuration on the Cisco firewall is complete and the interfaces are enabled. The following section provides an example of the interface configuration used in this topic.
ciscoasa(config)# show running-config interface
!
interface GigabitEthernet0/0                #The interface that connects to the VBR.
 nameif VBR                                 #The name of the GigabitEthernet0/0 interface.
 security-level 0
 ip address 10.0.0.1 255.255.255.252        #The IP address configured on the GigabitEthernet0/0 interface.
!
interface GigabitEthernet0/2                #The interface that connects to the data center (IDC).
 nameif private                             #The name of the GigabitEthernet0/2 interface.
 security-level 100                         #Specifies that the security-level of the interface that connects to the data center (IDC) is lower than that of the interface that connects to Alibaba Cloud.
 ip address 192.168.50.215 255.255.255.0    #The IP address configured on the GigabitEthernet0/2 interface.
!
interface GigabitEthernet0/3                #The interface connecting to private IPsec-VPN tunnel 1.
 nameif VPN-IP1                             #The name of the GigabitEthernet0/3 interface.
 security-level 0
 ip address 192.168.10.136 255.255.255.0    #The private IP address configured for the GigabitEthernet0/3 interface.
!
interface GigabitEthernet0/4                #The interface connecting to private IPsec-VPN tunnel 2.
 nameif VPN-IP2                             #The name of the GigabitEthernet0/4 interface.
 security-level 0
 ip address 192.168.40.159  255.255.255.0   #The private IP address configured for the GigabitEthernet0/4 interface.
!
#Configure a static route to the Alibaba Cloud VPC (172.16.0.0/16).
route VBR 172.16.0.0 255.255.0.0 10.0.0.2
#Configure a route to the on-premises IDC clients.
route private 192.168.0.0 255.255.0.0 192.168.50.216
Step 2: Configure a transit router
After the on-premises IDC is connected to Alibaba Cloud over an Express Connect circuit, start configuring the transit router to enable private network communication between the on-premises IDC and the VPC through the transit router.
In the Create a CEN instance. dialog box, select Create CEN Only, then customize the Cloud Enterprise Network (CEN) instance name and keep the other configuration items at their default values.
Create a transit router instance in the China (Hangzhou) region to connect the VBR instance and the VPC instance. Keep the default settings for the other configuration items.
Create a VPC connection.
On the tab of the CEN instance details page, find the transit router instance in the China (Hangzhou) region and click Create Connection in the Actions column.
On the Connection with Peer Network Instance page, configure the settings based on the following information, and then click OK to connect the VPC instance to the transit router.
The following section describes only the configuration items that are closely related to this topic. Keep the default settings for the other configuration items. For more information, see Procedure.
Configuration item
Description
Instance Type
Select Virtual Private Cloud (VPC).
Region
Select China (Hangzhou).
Attachment Name
Set a custom name to VPC-Attachment.
Network Instance
Select VPC.
VSwitch
Select a vSwitch instance in a zone supported by the transit router.
In this topic, vSwitch 2 and vSwitch 3 are selected. In a region that supports multiple zones, you must select one vSwitch instance in each of at least two zones. We recommend that you use vSwitches that do not carry workloads to create the VPC connection.
Advanced Settings
Use the default route configuration, which means enabling all three advanced configurations.
Click Create More Connections to return to the Connection with Peer Network Instance page.
Create a VBR connection.
On the Connection with Peer Network Instance page, configure the connection based on the following information, and then click OK to connect the VBR instance to the transit router. Only the configuration items that are strongly related to this topic are listed below. Keep the other configuration items at their default values. For more information, see Connect a VBR to a transit router.
Configuration item
Description
Instance Type
Select Virtual Border Router (VBR).
Region
Select China (Hangzhou).
Attachment Name
Set the custom name to VBR-Attachment.
Network Instance
Select VBR.
Advanced Settings
Use the default route configuration, that is, enable all three advanced configurations.
Step 3: Test private network connectivity
After you complete the preceding configurations, private network communication between the data center (IDC) and the VPC is established. You can perform the following steps to test private network connectivity.
Make sure that you understand the security group rules applied to the ECS instances in the VPC and the access control rules applied to the clients in the data center (IDC), and make sure that the security group rules of the ECS instances and the access control rules of the clients in the data center (IDC) allow the clients in the data center (IDC) to communicate with the ECS instances in the VPC. For more information, see View security group rules and Add a security group rule.
In this step, the access control rules of the data center (IDC) must allow the ICMP protocol and the VPC CIDR block, and the security group rules of the ECS instances must allow the ICMP protocol and the data center (IDC) CIDR block.
Log on to the ECS1 instance in the VPC. For more information, see Connection method overview.
Run the ping command to access any client in the data center (IDC) CIDR block.
ping <the IP address of a client in the data center>[root@iZr***viZ ~]# ping 192.168.20.6 PING 192.168.20.6 (192.168.20.6) 56(84) bytes of data. 64 bytes from 192.168.20.6: icmp_seq=1 ttl=60 time=153 ms 64 bytes from 192.168.20.6: icmp_seq=2 ttl=60 time=152 ms 64 bytes from 192.168.20.6: icmp_seq=3 ttl=60 time=152 ms 64 bytes from 192.168.20.6: icmp_seq=4 ttl=60 time=152 ms 64 bytes from 192.168.20.6: icmp_seq=5 ttl=60 time=152 ms 64 bytes from 192.168.20.6: icmp_seq=6 ttl=60 time=152 ms ^Z [1]+ Stopped ping 192.168.20.6As shown in the preceding output, if ECS1 can receive response packets, private network communication between the on-premises IDC and the VPC is established.
Step 2: Encrypt private network traffic over Express Connect circuits
After private network communication between the data center (IDC) and the VPC is established, you can establish an IPsec-VPN connection of the private network type between the on-premises gateway device and the transit router. Then, you can use route configuration to direct traffic between the data center (IDC) and the VPC to be transmitted over the private IPsec-VPN connection, which encrypts private network traffic over the Express Connect circuit.
Step 1: Establish a private IPsec-VPN connection
Add a transit router CIDR block 10.10.10.0/24 to the transit router. For more information, see Add a CIDR block to an existing router.
The transit router CIDR block is used to assign gateway IP addresses to the IPsec connection so that a private IPsec-VPN connection can be established. The transit router CIDR block cannot conflict with the CIDR blocks in the data center (IDC) and the VPC that need to participate in network communication.
Create two customer gateways to register the two VPN IP addresses of the on-premises gateway device with Alibaba Cloud.
- Log on to the VPN gateway console.
In the left-side navigation pane, choose Interconnections - VPN - Customer Gateways.
On the Customer Gateway page, click Create Customer Gateway.
On the Create Customer Gateway panel, configure the parameters based on the following information, and then click OK.
This section only lists the configuration items that are closely related to this topic. Keep the default settings for the other configuration items. For more information, see Customer Gateway.
Customer gateway 1
Name: Set the customer gateway name to Customer-Gateway1.
IP Address: Enter VPN IP address 1 of the on-premises gateway device 192.168.10.136.
Customer gateway 2
Name: Set the customer gateway name to Customer-Gateway2.
IP Address: Enter VPN IP address 2 of the on-premises gateway device 192.168.40.159.
Create a VPC connection.
In the left navigation pane, choose .
On the IPsec Connections page, click Bind CEN.
On the Create IPsec-VPN Connection page, configure the IPsec connection based on the following information, and then click OK.
The following section lists only the configuration items strongly related to this topic. Keep the default values for other configuration items. For more information, see IPsec-VPN connection (attached to a TR).
Configuration item
IPsec connection
Name
Set the value to IPsec connection.
Region
Select the region where the transit router is deployed.
The ipsec-vpn connection is created in the same region as the transit router.
Gateway Type
Select Private.
Bind CEN
Select Same Account.
CEN Instance ID
Select the Cloud Enterprise Network (CEN) instance created in Step 2.
The console displays the ID and CIDR block of the transit router that is created for the CEN instance in the current region. The ipsec-vpn connection will be attached to this transit router.
Routing Mode
This topic uses Destination Routing Mode, and the transmitted traffic is subsequently controlled by routes.
Tunnel 1
Customer Gateway
Associate Customer-Gateway1.
Pre-Shared Key
fddsFF111****.
ImportantThe pre-shared key of the IPsec-VPN connection must be the same as the pre-shared key of the peer gateway device. Otherwise, the IPsec-VPN connection cannot be established.
Encryption Configuration
Except for the following parameters, keep the default values for the remaining configuration items.
For DH Group (Perfect Forward Secrecy) of IKE Configurations, select group14.
For DH Group (Perfect Forward Secrecy) of IPsec Configurations, select group14.
NoteYou need to select encryption parameters based on the on-premises gateway device to ensure that the encryption configurations for the IPsec connection are the same as those for the on-premises gateway device.
Tunnel 2
Customer Gateway
Associate Customer-Gateway2.
Pre-Shared Key
fddsFF222****.
Encryption Configuration
Retain the default values for the configuration items other than those described in the following table.
Set DH Group (Perfect Forward Secrecy) of IKE Configurations to group14.
Set DH Group (Perfect Forward Secrecy) of IPsec Configurations to group14.
NoteYou need to select encryption parameters based on the on-premises gateway device to ensure that the encryption configurations for the IPsec connection are the same as those for the on-premises gateway device.
Advanced Settings
Use the default route configuration, that is, enable all advanced configuration options.
After the IPsec connection is created, you can view the gateway IP addresses of the IPsec connection on the IPsec connection details page. The IPsec connection uses these two gateway IP addresses to establish a private IPsec-VPN connection with the on-premises gateway device. After the IPsec connection is created, click the Tunnel tab on the IPsec connection details page to view the gateway IP addresses of the two tunnels: the gateway IP address of Tunnel 1 is
10.10.10.49and the gateway IP address of Tunnel 2 is10.10.10.50. The connection status of both tunnels is Phase 2 negotiation succeeded and the status is Normal.
Return to the IPsec-VPN connection page, find the created IPsec connection, and click Generate Peer Configuration in the Actions column.
The peer configuration is the VPN configuration that you must add to the peer of the IPsec connection. In the scenario described in this topic, you must add these configurations to the on-premises gateway device.
In the IPsec-VPN Connection Configuration dialog box, copy the configuration and save it locally for subsequent configuration of the on-premises gateway device.
Configure the customer gateway device.
After you create the IPsec connection, you must add the VPN configuration to the on-premises gateway device so that a private IPsec-VPN connection can be established between the on-premises gateway device and Alibaba Cloud.
After completing the above configuration, the data center (IDC) can successfully establish a private IPsec-VPN connection with Alibaba Cloud. You can view the status of the private IPsec-VPN connection on the details page of the IPsec connection instance in Alibaba Cloud. If the private IPsec-VPN connection is not established successfully in your environment, try to troubleshoot the issue by yourself. For more information, see Self-service diagnostics. After the configuration is complete, you can view the connection status of the two tunnels on the Tunnel tab of the VPN gateway. Both Tunnel 1 (gateway IP address
10.10.10.49) and Tunnel 2 (gateway IP address10.10.10.50) display Phase 2 negotiation succeeded, and the status is Normal, which indicates that the private IPsec-VPN connection is established successfully.
Step 2: Configure routes
After the private IPsec-VPN connection is created, traffic between the data center (IDC) and the VPC is still transmitted over the Express Connect circuit and is not encrypted. You need to add related routes so that traffic between the data center (IDC) and the VPC is transmitted over the private IPsec-VPN connection.
Modify the route configuration on the on-premises gateway device.
#Configure a route to the VPC so that traffic is transmitted over the private IPsec-VPN connection route ALIYUN1 172.16.0.0 255.255.0.0 10.10.10.49 4 route ALIYUN2 172.16.0.0 255.255.0.0 10.10.10.50 5 #Modify the priority of the static route pointing to the Express Connect circuit so that its priority is lower than that of the static route pointing to the private IPsec-VPN connection. route VBR 172.16.0.0 255.255.0.0 10.0.0.2 10ImportantIn this scenario, traffic from the data center (IDC) to the VPC is preferentially transmitted over Tunnel 1. When Tunnel 1 is interrupted, the traffic is automatically transmitted over Tunnel 2. Traffic from the VPC to the data center (IDC) is randomly transmitted over the two tunnels.
Add a route entry for the data center (IDC) to the IPsec connection.
Log on to the VPN Gateway console.
In the left-side navigation pane, choose Interconnections- VPN - IPsec Connections.
In the top status bar, select the China (Hangzhou) region.
On the IPsec Connections page, find the target IPsec connection instance and click the ID of the IPsec connection instance.
-
On the Destination-based Route Table tab, click Add Route Entry.
On the Add Route Entry panel, configure the destination route based on the following information, and then click OK.
ImportantWhen you add a route to the data center (IDC), make sure that the destination CIDR block is more specific than the CIDR block added to the VBR instance, so that the route to the data center (IDC) that the transit router learns over the private IPsec-VPN connection is preferred.
Configuration item
CIDR block 1
CIDR block 2
CIDR block 3
Destination CIDR Block
Enter 192.168.10.0/24.
Enter 192.168.20.0/24.
Enter 192.168.40.0/24.
Next Hop Type
Select IPsec-VPN connection.
Next Hop
Select the IPsec connection that you created.
Add a custom route entry for the transit router.
After the preceding route configuration is complete, the private IPsec-VPN connection is interrupted. You must add a specific route destined for the VPN IP address of the on-premises gateway device to the route table of the transit router, with the next hop pointing to the VBR instance, to re-establish the private IPsec-VPN connection.
Stay on the Route Table tab, click the Route tab, and then click Create Route.
In the Add Route Entry dialog box, configure the route entry information, and then click OK.
Parameter
CIDR block 1
CIDR block 2
Destination CIDR
Enter VPN IP address 1 of the on-premises gateway device 192.168.10.136/32.
Enter VPN IP address 2 of the on-premises gateway device 192.168.40.159/32.
Blackhole Route?
Select No.
Next Hop Connection
Select VBR-Attachment.
Step 3: Verify the encryption effect
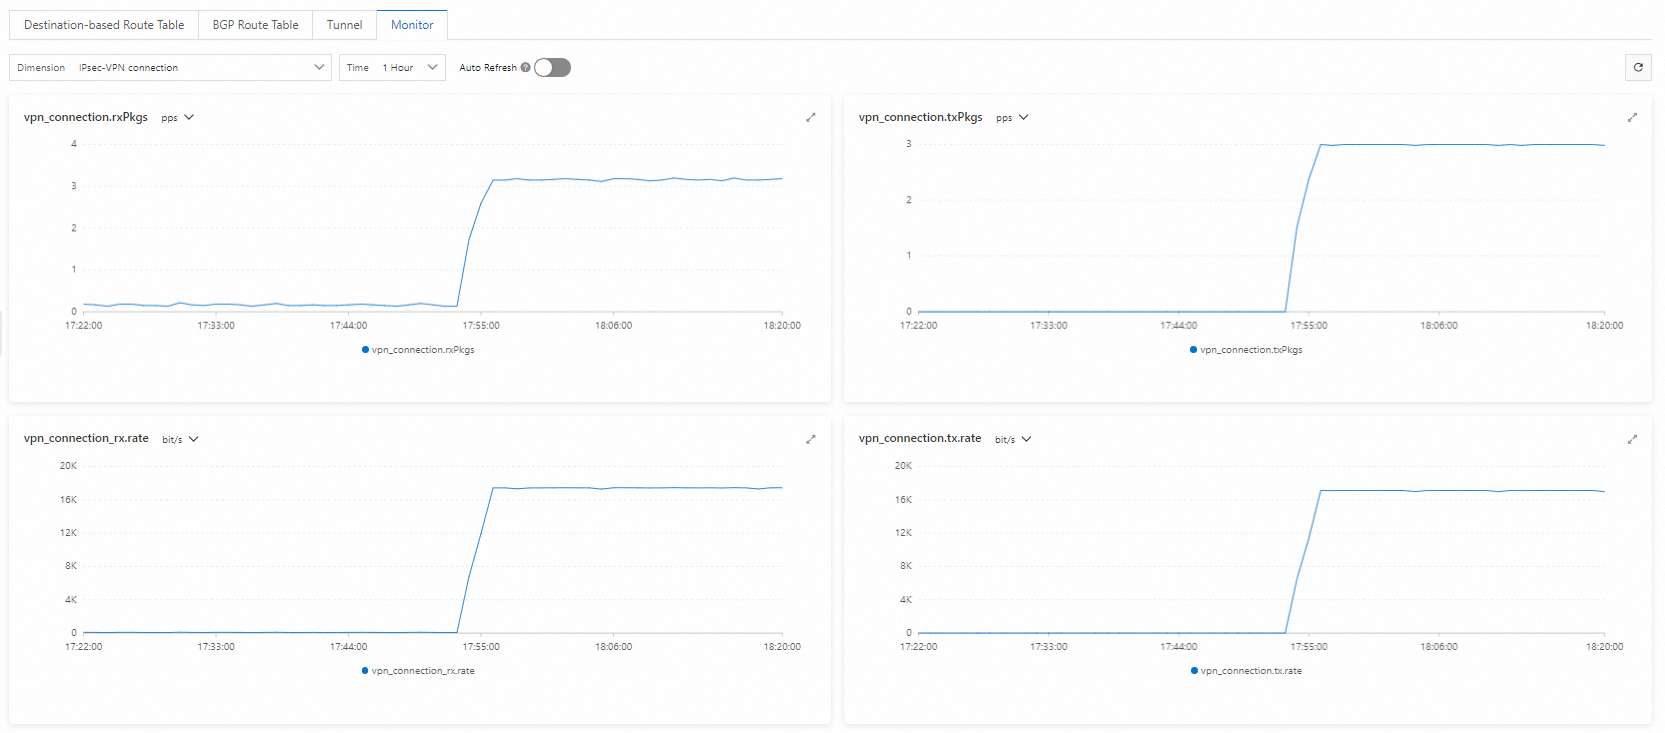
After you complete the preceding configurations, if you can view traffic transmission monitoring data on the details page of the IPsec connection, the private network traffic over the Express Connect circuit is encrypted.
Log on to the ECS1 instance in the VPC. Run the ping command to continuously access any client in the on-premises IDC CIDR block.
ping <IP address of a client in the data center> -s 1000 -c 10000-s 1000: specifies to send 1000-byte packets.-c 10000: continuously sends 10000 request packets.
Log on to the VPN Gateway console.
In the top navigation bar, select the China (Hangzhou) region.
In the left-side navigation pane, choose Interconnections - VPN - IPsec Connections.
On the IPsec-VPN connection page, find the created IPsec connection and click the IPsec connection ID.
View the traffic transmission monitoring data on the IPsec connection details page.