WAF plans and editions
Web Application Firewall (WAF) supports subscription and pay-as-you-go billing methods. Available editions vary by billing method. This topic describes the business scales and protection features offered by different editions.
WAF plans and editions
WAF offers two subscription deployment plans: On-cloud WAF and Hybrid Cloud WAF. On-cloud WAF instances are available in Pro, Enterprise, Ultimate, and Exclusive (sales suspended) editions, which vary by business scale and protection features. Hybrid Cloud WAF instances are available only in the Exclusive edition.
For pay-as-you-go, WAF instances are available only in the Pay-as-you-go V2.0 edition.
Edition specifications and use cases
The following table outlines the recommended use cases and specifications for each WAF edition. For medium-sized enterprise websites, we recommend the On-cloud WAF Business or On-cloud WAF Enterprise edition.
Specification | On-cloud WAF Pro | On-cloud WAF Business | On-cloud WAF Enterprise | On-cloud WAF Exclusive (No longer available for purchase) | Hybrid Cloud WAF Exclusive |
Website scale | Designed for small to medium-sized websites with basic security needs. | Ideal for medium-sized enterprise websites and public services that require high standards of data security. | For medium- to large-scale enterprise websites or those with custom security requirements. | Tailored for large-scale enterprise websites that require highly customized security configurations to meet specific business needs. | For medium to large enterprises with on-premises services or web traffic that cannot be protected by On-cloud WAF. This edition provides the same high standard of web security as On-cloud WAF. |
peak queries per second (QPS) | 2,000 QPS | 5,000 QPS | Over 10,000 QPS | 5,000 QPS | 0 QPS (scalable) |
Number of nodes in an on-premises protection cluster and peak QPS | Not supported | Available for an additional fee. | Available for an additional fee. | Available for an additional fee. | 2 nodes, 10,000 QPS |
Maximum bandwidth (Mbit/s) for origin servers on Alibaba Cloud | 50 Mbps | 100 Mbps | 200 Mbps | 100 Mbps | 0 Mbps (scalable) |
Maximum bandwidth (Mbit/s) for origin servers outside Alibaba Cloud | 10 Mbps | 30 Mbps | 50 Mbps | 30 Mbps | |
Default number of protected second-level domains | 1 | 1 | 1 | 1,000 | 200 domains (of any level). The limit increases by 100 for each additional node. |
Total protected domains (includes wildcard domains) | 10 | 10 | 10 | 1,000 |
Features by edition (Chinese mainland)
This table lists the features of WAF subscription and pay-as-you-go instances in the Chinese mainland region. For more details, see the WAF Product Pricing Page.
Legend:
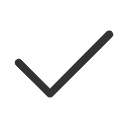 : Supported in the current version.
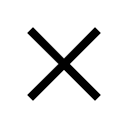 : Not supported in the current version.
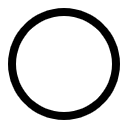
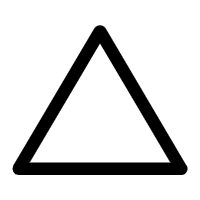 : A value-added service that requires an additional fee. You can enable this service when purchasing a WAF instance or later using the upgrade feature.
- : Available only after activating pay-as-you-go WAF. You can enable it through the Bill and Plan Center.
Feature module | Description | WAF Advanced edition | WAF Enterprise edition | WAF Ultimate edition | WAF Exclusive edition (Unavailable for purchase) | Hybrid Cloud WAF Exclusive edition | Pay-as-you-go V2.0 edition |
Website access | |||||||
Enables site-wide HTTPS protection with a single click. |
|
|
|
|
|
| |
Proactively discovers and manages website assets, which you can add to WAF for one-click protection. |
|
|
|
|
|
| |
Directs traffic from origin servers, such as SLB instances and ECS instances, to WAF for protection. |
|
|
|
|
|
| |
Protects websites that use the HTTP/2 protocol. |
|
|
|
|
|
| |
Protects services on non-standard ports other than 80, 8080, 443, and 8443. |
|
|
|
|
|
| |
Inspects and protects IPv6 traffic. |
|
|
|
|
|
| |
Offers customized access and protection, including custom default SNI certificates and service ports. |
|
|
|
|
|
| |
Protects web traffic that does not pass through Alibaba Cloud by deploying a WAF protection cluster to an on-premises data center, |
|
|
|
|
|
| |
Provides automatic scheduling and disaster recovery for your origin server across multiple nodes and lines. |
|
|
|
|
|
| |
Provides dedicated IPs for your domain names. |
|
|
|
|
|
| |
Website Protection | |||||||
Protects against common web attacks, such as SQL injection and XSS. |
|
|
|
|
|
| |
Automatically updates protection rules for zero-day vulnerabilities. |
|
|
|
|
|
| |
Protects against common CC attacks using built-in rules and an emergency mode. |
|
|
|
|
|
| |
Locks website pages to prevent malicious tampering. |
|
|
|
|
|
| |
Prevents leakage of sensitive data, such as phone numbers, ID card numbers, and bank card numbers. |
|
|
|
|
|
| |
Detects security risks on account-related endpoints, such as login and registration pages. These risks include credential stuffing, brute-force attacks, spam registration, credential sniffing, and SMS abuse. |
|
|
|
|
|
| |
DDoS protection | Mitigates DDoS attacks at no extra cost. For more information about the protection capabilities, see Anti-DDoS Origin Basic blackhole thresholds. |
|
|
|
|
|
|
Blocks access from specified IP addresses and CIDR blocks. |
|
|
|
|
|
| |
Also blocks access from specified geographic locations. |
|
|
|
|
|
| |
Blocks high-frequency web attacks and directory traversal attempts using default rules. Also provides scanner blocking and collaborative defense. |
|
|
|
|
|
| |
Includes the preceding features and allows you to create custom rules to block high-frequency web attacks and directory traversal attempts. |
|
|
|
|
|
| |
Basic access control: Creates access control list (ACL) rules based on common request fields, including IP, URL, Referer, User-Agent, and Params. |
|
|
|
|
|
| |
Advanced access control: In addition to common fields, supports rules based on advanced request fields such as Cookie, Content-Type, Header, and HTTP Method. |
|
|
|
|
|
| |
Supports rate limiting by IP address and session. You can define precise match conditions and rate limits to filter malicious requests. |
|
|
|
|
|
| |
Supports rate limiting based on custom fields in addition to IP addresses and sessions. |
|
|
|
|
|
| |
Supports custom protection rule groups. |
|
|
|
|
|
| |
Proactively defends your website by using deep learning to analyze traffic. |
|
|
|
|
|
| |
Protects against bot-driven fraud on critical business endpoints, such as registration, login, promotion, and forum pages. |
|
|
|
|
|
| |
Maintains a whitelist of legitimate search engine bots to ensure they can access your site. |
|
|
|
|
|
| |
Provides multi-dimensional bot threat intelligence rules. These rules are based on sources like dial-up IPs, data center IPs, malicious scanners, and a real-time, cloud-generated bot library. Use these rules to block malicious bot requests for an entire domain or for specific paths. |
|
|
|
|
|
| |
Secures native apps with features like trusted communication and anti-bot scripting. It also identifies requests from proxies, emulators, and illegally signed apps. |
|
|
|
|
|
| |
Protects and detects vulnerabilities in the APIs of your WAF-protected services. |
|
|
|
|
|
| |
Security analytics and support | |||||||
Integrates with CloudMonitor to provide configurable, threshold-based alerts for WAF events. |
|
|
|
|
|
| |
Collects and stores all WAF logs in Log Service, providing near real-time query and analysis capabilities and online reports. |
|
|
|
|
|
| |
Provides a dashboard to visualize and analyze your website's overall traffic and security status. |
|
|
|
|
|
| |
Features by edition (Regions outside Mainland China)
The following table lists the features of different editions of subscription Web Application Firewall (WAF) instances in Regions Outside Chinese Mainland. For more information about the features of each edition, see the Web Application Firewall pricing page.
Legend:
 : Supported in the current version.
- : Not supported in the current version.
- : A value-added service that requires an additional fee. You can enable this service when purchasing a WAF instance or later using the upgrade feature.
- : Available only after activating pay-as-you-go WAF. You can enable it through the Bill and Plan Center.
The pay-as-you-go billing method is not supported for WAF instances in Regions Outside Chinese Mainland.
Feature module | Description | WAF Advanced | WAF Enterprise | WAF Ultimate | WAF Exclusive (No longer available for purchase) | Hybrid Cloud WAF Exclusive |
Website onboarding | ||||||
Enables site-wide HTTPS protection with one click. |
|
|
|
|
| |
Directs traffic from your origin server, such as an SLB or ECS instance, to WAF for protection. |
|
|
|
|
| |
Protects websites that use the HTTP/2 protocol. |
|
|
|
|
| |
Protects services that run on specific non-standard ports other than 80, 8080, 443, and 8443. |
|
|
|
|
| |
Provides custom onboarding and protection capabilities. |
|
|
|
|
| |
Detects and protects against threats in IPv6 traffic. |
|
|
|
|
| |
Proactively discovers and manages website assets, letting you add them to WAF for protection with a single click. |
|
|
|
|
| |
Enables dedicated IP protection for your domain names. |
|
|
|
|
| |
You can deploy a WAF protection cluster in on-premises data centers to protect web traffic that does not pass through Alibaba Cloud. |
|
|
|
|
| |
Provides automated scheduling and disaster recovery for your origin server by using intelligent multi-node and multi-line access. |
|
|
|
|
| |
Website Protection | ||||||
Defends against common web attacks, such as SQL injection and XSS. |
|
|
|
|
| |
Automatically updates protection rules to defend against zero-day vulnerability exploits. |
|
|
|
|
| |
Detects security risks, such as credential stuffing, brute-force attacks, spam registration, credential sniffing, and SMS abuse, on account-related endpoints like registration and login pages. |
|
|
|
|
| |
Defends against common CC attacks using standard and emergency protection modes. |
|
|
|
|
| |
Blocks access from specified IP addresses and CIDR blocks. |
|
|
|
|
| |
Includes the preceding features and allows you to block access from specified geographic locations with one click. |
|
|
|
|
| |
Supports high-frequency web attack blocking (default rules), directory traversal blocking (default rules), scan tool blocking, and collaborative defense. |
|
|
|
|
| |
Includes the preceding features and allows you to create custom rules to block high-frequency web attacks and directory traversal attempts. |
|
|
|
|
| |
Basic fine-grained access control: Creates access control list (ACL) rules based on basic fields such as IP, URL, Referer, User-Agent, and Params. |
|
|
|
|
| |
Advanced fine-grained access control: Includes all basic fields and supports advanced fields such as Cookie, Content-Type, Header, and Http-Method. |
|
|
|
|
| |
Supports rate limiting based on IP addresses and sessions, allowing you to create custom CC attack protection rules with precise match conditions and rate limits to accurately filter malicious requests. |
|
|
|
|
| |
Supports rate limiting based on custom fields, in addition to IP addresses and sessions. |
|
|
|
|
| |
Locks website pages to prevent malicious tampering. |
|
|
|
|
| |
Prevents the leakage of sensitive data, such as phone numbers, ID card numbers, and bank card numbers. |
|
|
|
|
| |
Supports custom rule groups. |
|
|
|
|
| |
Provides proactive defense based on a deep learning analysis of your website traffic. |
|
|
|
|
| |
Defends against bot-driven fraud on critical business endpoints, such as registration, login, promotion, and forum pages. |
|
|
|
|
| |
DDoS attack protection | Provides basic DDoS attack protection. For details on the protection capabilities, see Anti-DDoS Origin Basic blackhole thresholds. |
|
|
|
|
|
Provides a whitelist of legitimate search engine crawlers to allow their access requests for your domain. |
|
|
|
|
| |
Provides multi-dimensional bot threat intelligence rules based on dial-up IP addresses, data center IP addresses, malicious scanner IP addresses, and a real-time malicious bot library generated by a cloud-based model to block malicious bot requests for your entire domain or specific paths. |
|
|
|
|
| |
Protects native apps by identifying requests from proxies, emulators, and illegally signed apps, and provides features such as trusted communication and anti-bot scripting. |
|
|
|
|
| |
Security analytics and support | ||||||
Lets you configure WAF event monitoring and threshold-based alert rules by using CloudMonitor. |
|
|
|
|
| |
Collects and stores all WAF logs in Log Service, providing near real-time query and analytics capabilities and online reports. |
|
|
|
|
| |
Provides a data visualization dashboard to display the overall traffic and security status of your website. |
|
|
|
|
| |