Role authorization for data transmission and migration
This topic describes how to grant Alibaba Cloud accounts and Resource Access Management (RAM) users permissions to access Data Transmission Service.
Background information
Data Transmission Service uses the same logon system as Alibaba Cloud, which lets you log on with an Alibaba Cloud account or a Resource Access Management (RAM) user. For more information, see the official Resource Access Management (RAM) documentation.
An Alibaba Cloud account is the basic entity that owns cloud resources and is responsible for billing. An Alibaba Cloud account can create, manage, and grant permissions to RAM users within an organization.
A RAM user is created and managed by an Alibaba Cloud account in the RAM system. A RAM user does not own resources or have separate billing. The associated Alibaba Cloud account controls and pays for the resources that the RAM user uses.
Grant permissions to an Alibaba Cloud account for data transmission and migration
Data Transmission Service requires permissions to access cloud resources. If you log on with an Alibaba Cloud account that has not been granted permissions, you must go to the Alibaba Cloud Management Console to authorize the data transmission and migration role.
Log on to the OceanBase Management Console with your Alibaba Cloud account.
In the navigation pane on the left, expand Data Transmission and select a page.
In the authorization prompt, click Go to RAM Role Authorization.
Confirm the information on the page and click Agree to Authorization.
Return to the Data Transmission Service page and refresh it.
Grant permissions to a RAM user for data transmission and migration
Data Transmission Service requires permissions to access cloud resources. If you log on with a RAM user that has not been granted permissions, you must go to the Alibaba Cloud Management Console to authorize the data transmission and migration role.
Log on to the OceanBase Management Console as a RAM user.
In the navigation pane on the left, expand Data Transmission and select a page.
In the authorization prompt, click Go to RAM Role Authorization.
You can also click Switch to Alibaba Cloud Account Logon to access Data Transmission Service.
Confirm the information on the page and click Agree to Authorization.
Return to the Data Transmission Service page and refresh it.
If the RAM user authorization fails, you can perform one of the following operations:
Log on to the console with your Alibaba Cloud account.
Have the owner of the Alibaba Cloud account grant the RAM authorization permission to the current RAM user.
Log on to the RAM console with your Alibaba Cloud account.
In the left navigation pane, click Identity Management > Users.
On the Users page, find the target RAM user, and in the Actions column, click Add Permissions.
In the Add Permissions dialog box, on the System Policy tab, search for and select the AliyunRAMFullAccess policy. The policy is then added to the Selected list on the right.
After the RAM authorization permission is granted to the RAM user, authorize the data transmission and migration role again.
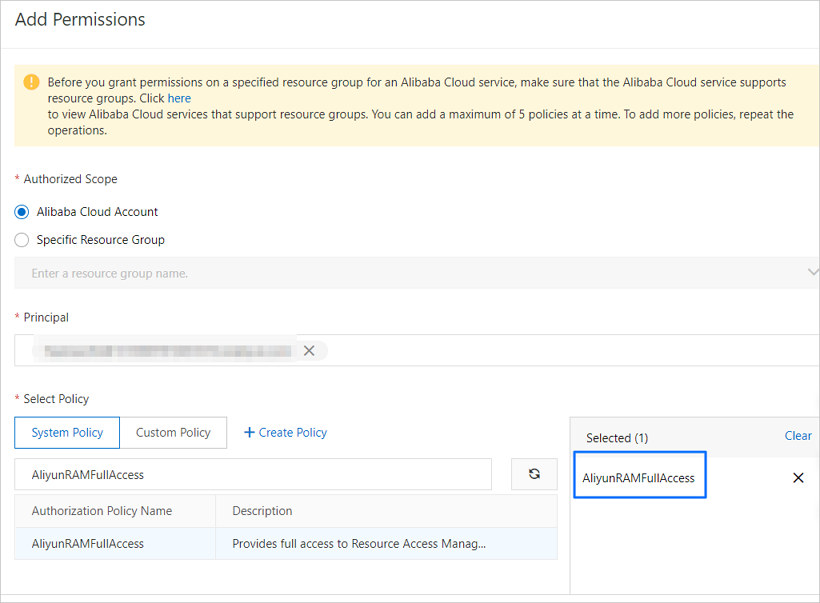
Click OK.
Click Complete.
Log on to the console as another RAM user who has the permission to authorize the data transmission and migration role.
(Optional) Switch to an Alibaba Cloud account to log on to the console
If you are logged on to the console as a RAM user, you can follow these steps to switch to an Alibaba Cloud account. You can also skip this procedure and log on to the console directly with an Alibaba Cloud account.
Log on to the OceanBase Management Console as a RAM user.
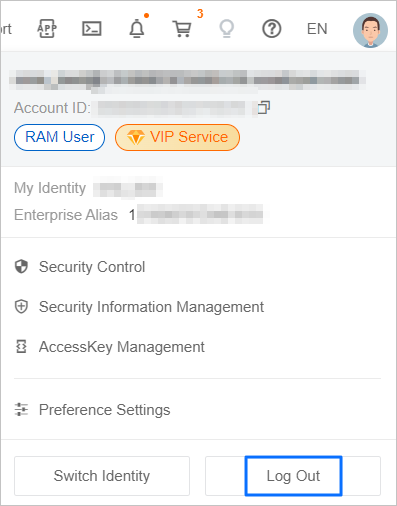
In the upper-right corner of the page, click Log Out in the personal center to log out of the current RAM user.
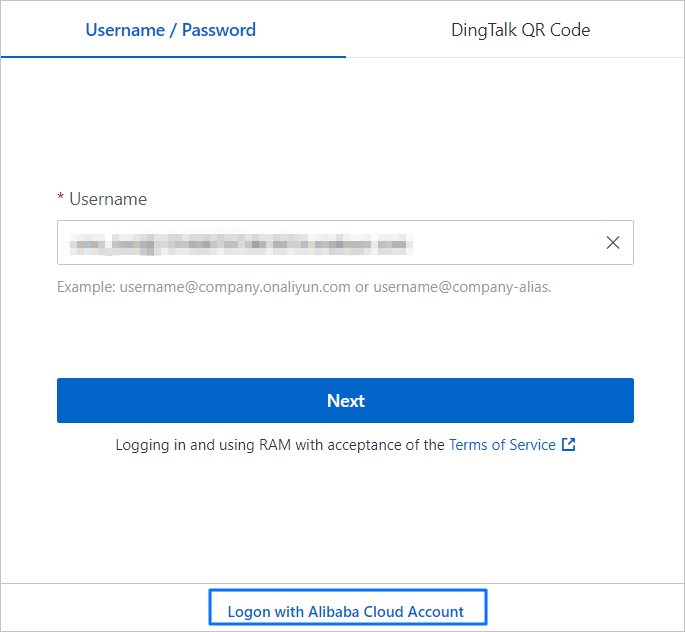
On the logon page, click Root Account Logon.
(Optional) Use an Alibaba Cloud account to grant a RAM user permissions to authorize the data transmission and migration role
A RAM user must have the AliyunOceanbaseMigrationServiceRolePolicy for the data transmission and migration role to access Data Transmission Service. If the RAM user does not have this role, the Alibaba Cloud account must first log on to the RAM console and manually grant permissions for the data transmission and migration role.
Log on to the RAM console with your Alibaba Cloud account.
Create the data transmission and migration role.
In the left navigation pane, click Identity Management > Roles.
On the Roles page, click Create Role.
In the Create Role dialog box, select Alibaba Cloud Account as the trusted entity type and click Next.
On the Configure Role page, set the parameters.
Parameter
Description
Role Name
Enter AliyunOceanbaseMigrationServiceRole.
Note (Optional)
Enter a note for the role.
You can select a trusted Alibaba Cloud account.
Current Alibaba Cloud Account: Select this option if you want to allow RAM users of the current Alibaba Cloud account to assume this RAM role.
Other Alibaba Cloud Account: Select this option if you want to allow RAM users of another Alibaba Cloud account to assume this RAM role. Then, enter the ID of the other Alibaba Cloud account. This option is mainly used for cross-account resource access authorization.
Click Complete.
Create a permission policy for Data Transmission Service to retrieve ApsaraDB RDS information.
Return to the Roles page and then click Add Permissions for the new role.
In the Add Permissions dialog box, under Select Permissions, click Create Policy.
On the Create Policy page, click the Script Editor tab and enter the following policy statement.
{
    "Statement": [
        {
            "Action": [
                "rds:DescribeDBInstances",
                "rds:DescribeDBInstanceNetInfo",
                "rds:DescribeDBInstanceIPArrayList",
                "rds:ModifySecurityIps"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "vpc:DescribeVpcs",
                "vpc:DescribeVSwitches"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "polardb:DescribeDBClusterIPArrayList",
                "polardb:DescribeDBClusterNetInfo",
                "polardb:DescribeDBClusters",
                "polardb:DescribeRegions",
                "polardb:DescribeDBClusterEndpoints",
                "polardb:DescribeDBClusterAccessWhitelist",
                "polardb:ModifyDBClusterAccessWhitelist"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "dg:GetUserGatewayInstances",
                "dg:GetUserGateways",
                "dg:GetUserDatabases",
                "dg:ListDatabaseAccessPoint",
                "dg:DescribeRegions",
                "dg:FindUserGatewayById"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "adb:DescribeDBClusters",
                "adb:DescribeDBClusterAttribute",
                "adb:DescribeAutoRenewAttribute",
                "adb:DescribeAvailableResource",
                "adb:DescribeDBResourcePool",
                "adb:DescribeElasticDailyPlan",
                "adb:DescribeElasticPlan",
                "adb:DescribeTables",
                "adb:DescribeAllDataSource",
                "adb:DescribeSchemas",
                "adb:DescribeColumns",
                "adb:DescribeTablePartitionDiagnose",
                "adb:DescribeRegions",
                "adb:DescribeDBClusterNetInfo",
                "adb:DescribeDBClusterAccessWhiteList",
                "adb:ModifyDBClusterAccessWhiteList"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "dms:ListUsers",
                "dms:ListUserTenants",
                "dms:ListColumns",
                "dms:ListIndexes",
                "dms:ListDatabases",
                "dms:ListLogicDatabases",
                "dms:ListTables",
                "dms:ListLogicTables",
                "dms:ListInstances",
                "dms:GetUserActiveTenant",
                "dms:GetTableDBTopology",
                "dms:SearchDatabase",
                "dms:SearchTable"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "cms:DescribeContactList",
                "cms:DescribeMonitorGroups",
                "cms:DescribeMonitorGroupInstances",
                "cms:DescribeCustomMetricList",
                "cms:DescribeSystemEventMetaList",
                "cms:DescribeSystemEventCount",
                "cms:DescribeSystemEventAttribute",
                "cms:DescribeSystemEventHistogram",
                "cms:DescribeCustomEventCount",
                "cms:DescribeCustomEventAttribute",
                "cms:DescribeCustomEventHistogram",
                "cms:CreateMonitorGroup",
                "cms:PutCustomEvent",
                "cms:PutCustomMetric",
                "cms:PutContactGroup",
                "cms:PutCustomMetricRule"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Action": [
                "alikafka:ListInstance",
                "alikafka:UpdateInstance",
                "alikafka:ReadOnly"
            ],
            "Resource": "*",
            "Effect": "Allow"
        },
        {
            "Effect": "Allow",
            "Action": [
                "ecs:DescribeVSwitches",
                "ecs:DescribeSecurityGroups",
                "ecs:CreateSecurityGroup",
                "ecs:DeleteSecurityGroup",
                "ecs:CreateNetworkInterface",
                "ecs:DescribeNetworkInterfaces",
                "ecs:CreateNetworkInterfacePermission",
                "ecs:DescribeNetworkInterfacePermissions",
                "ecs:DeleteNetworkInterface"
            ],
            "Resource": "*"
        }
    ],
    "Version": "1"
}
Click Next: Edit Basic Information.
Enter a Name for the policy and click OK.
Add permissions to the RAM role.
Return to the Roles page and click Add Permissions for the new role.
In the Add Permissions dialog box, under Select Permissions, click the Custom Policy tab.
Search for and select the policy you created. The policy appears in the Selected list on the right.
Click OK.