Recommended architecture for Finance Cloud (VPC)
Alibaba Finance Cloud VPC clusters are deployed in three regions: China (Hangzhou), China (Shanghai), and China (Shenzhen). When you use a virtual private cloud (VPC), build your Finance Cloud environment based on the following recommended architectures.
Recommended architecture
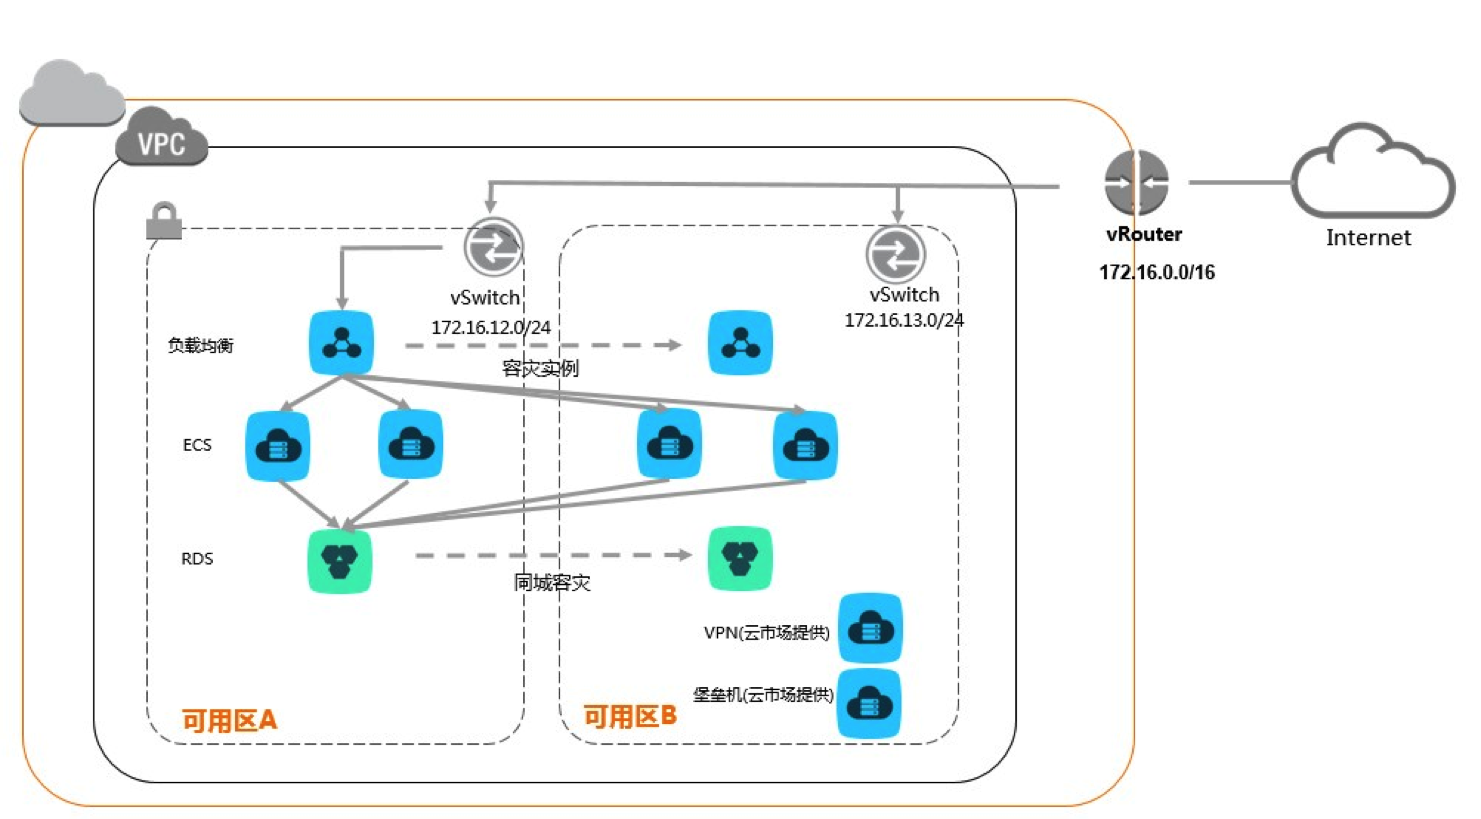
- Network isolation:
- Create a VPC. Configure a vRouter and vSwitches to completely isolate the network of this environment from other environments.
- After you create the VPC, attach elastic IP addresses (EIPs) to backend ECS instances or use Server Load Balancer (SLB) directly to allow access from the Internet.
- Create a vSwitch in each of the two zones to isolate the network of each zone.
- High availability across zones:
- When you create an SLB instance, select a multi-zone instance to ensure high availability across zones.
- Purchase an equal number of ECS instances in each of the two zones. Assign each ECS instance to the vSwitch in its corresponding zone.
- When you create an RDS instance, select a multi-zone instance. RDS automatically maintains two identical data replicas across the two zones. This provides excellent performance and reliability. Use RDS MySQL or RDS SQL Server services instead of building your own database servers. When you create the RDS instance, you can assign it to a specific vSwitch.
- Security domains: Use a Virtual Private Network (VPN) and Bastionhost, and configure security groups. Use a multi-level jump server policy with security groups to ensure O&M security.
Recommended architecture for high security requirements
For finance customers with high security requirements, use the following architecture to build your Finance Cloud environment.
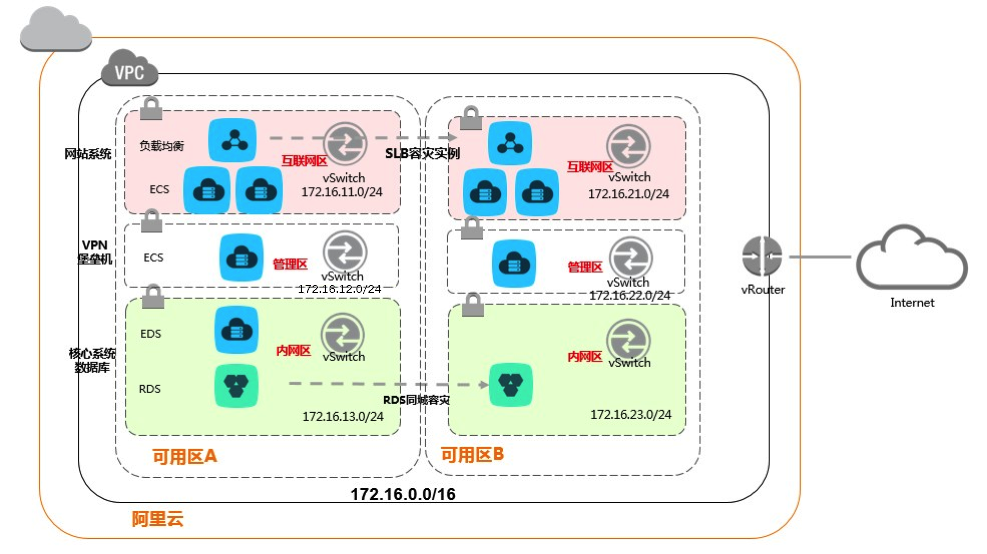
- Use vSwitch routing policies and security groups to isolate networks with different security levels.
- Divide the network into different security domains based on security levels. Use different vSwitches for each domain, such as an Internet zone (demilitarized zone or DMZ), a management zone, and a private network zone.
- Configure the Internet zone to be the only zone that can access the Internet and receive user traffic.
- Install the VPN and jump servers in the management zone.
- The deployment of other network elements is the same as that in the Recommended architecture.
FAQ
Q: What is the difference between a VPC and a classic network?
A: Cloud products in a classic network are deployed in Alibaba Cloud's public basic network. Alibaba Cloud is responsible for network planning and management. This option is suitable for customers who prioritize ease of use. A VPC is a custom, isolated network that you create within the Alibaba Cloud basic network. You can define the network topology and IP addresses for your VPC. Compared to a classic network, a VPC is better for customers who have the capability and requirement to manage their own network.
Q: Do I have to build my application based on this architecture?
A: Alibaba Finance Cloud recommends that you follow the principles of this architecture to build your system. This lets you achieve high availability across two data centers at a low cost. If one data center fails, it does not cause a service interruption. The key principles are to use SLB for access, use multiple low-specification ECS instances distributed across different zones, and use the RDS service instead of building your own database.
Q: Are Bastionhost or jump servers required?
A: No, they are not. However, using Bastionhost to manage servers provides better security and is strongly recommended.