Type 2: Tag-based authorization
When your organization has many members, use user tag-based authorization instead of granting permissions to individual users or user groups. This method lets you authorize all users at once, simplifying administration. This topic describes how to configure tag-based authorization.
Scenarios
This method uses a user-level permission strategy to personalize data access. For example, users responsible for different regions can view only the data for their assigned regions.
Prerequisites
You have created a dataset. For more information, see Create a dataset.
Precautions
This topic applies only to users who purchased or started a trial of Quick BI on or after June 3, 2021. If you do not meet this requirement, you must first upgrade from the legacy row-level permissions to the new version before you proceed.
Limits
You can configure row-level permissions only in Advanced Edition and Quick BI Enterprise Standard.
Only dataset owners and workspace administrators can configure row-level permissions.
NoteA workspace developer can configure row-level permissions only for the datasets they create, while a workspace administrator can configure them for all datasets.
Procedure
Log on to the Quick BI console. You can configure row-level permissions for a dataset from the workbench or the dataset editing page.
Entry points
Entry point 1
Configure row-level permissions for a dataset from the workbench.
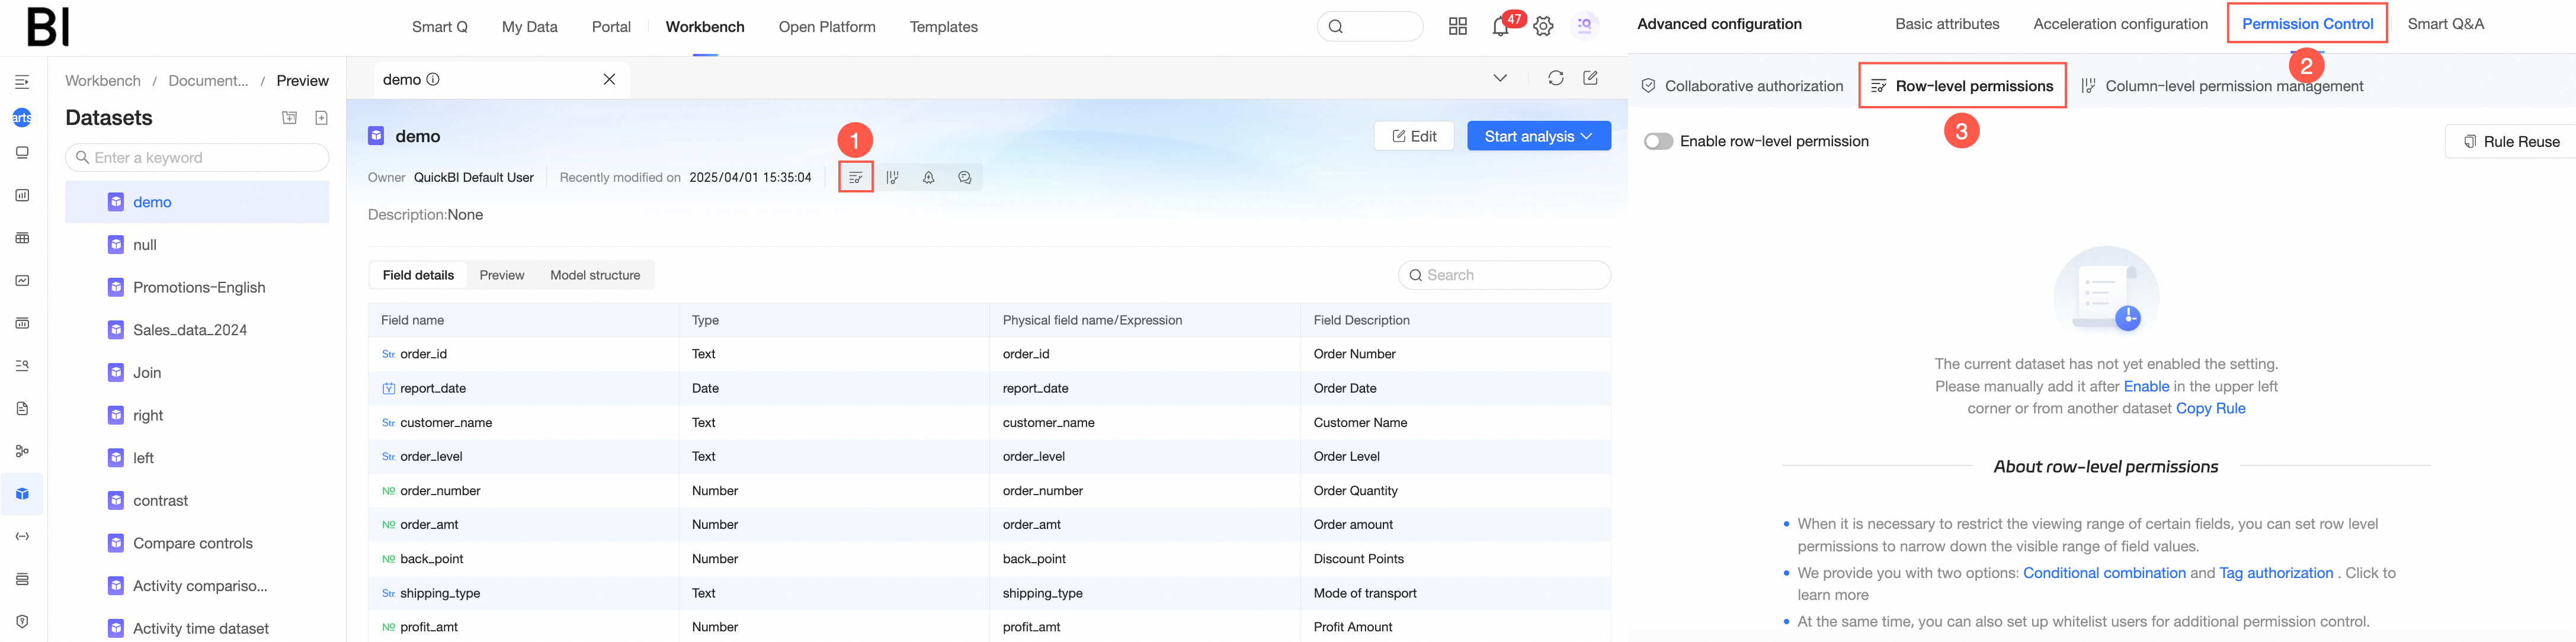
Follow the steps in the figure to go to the Row-level Permissions settings page.

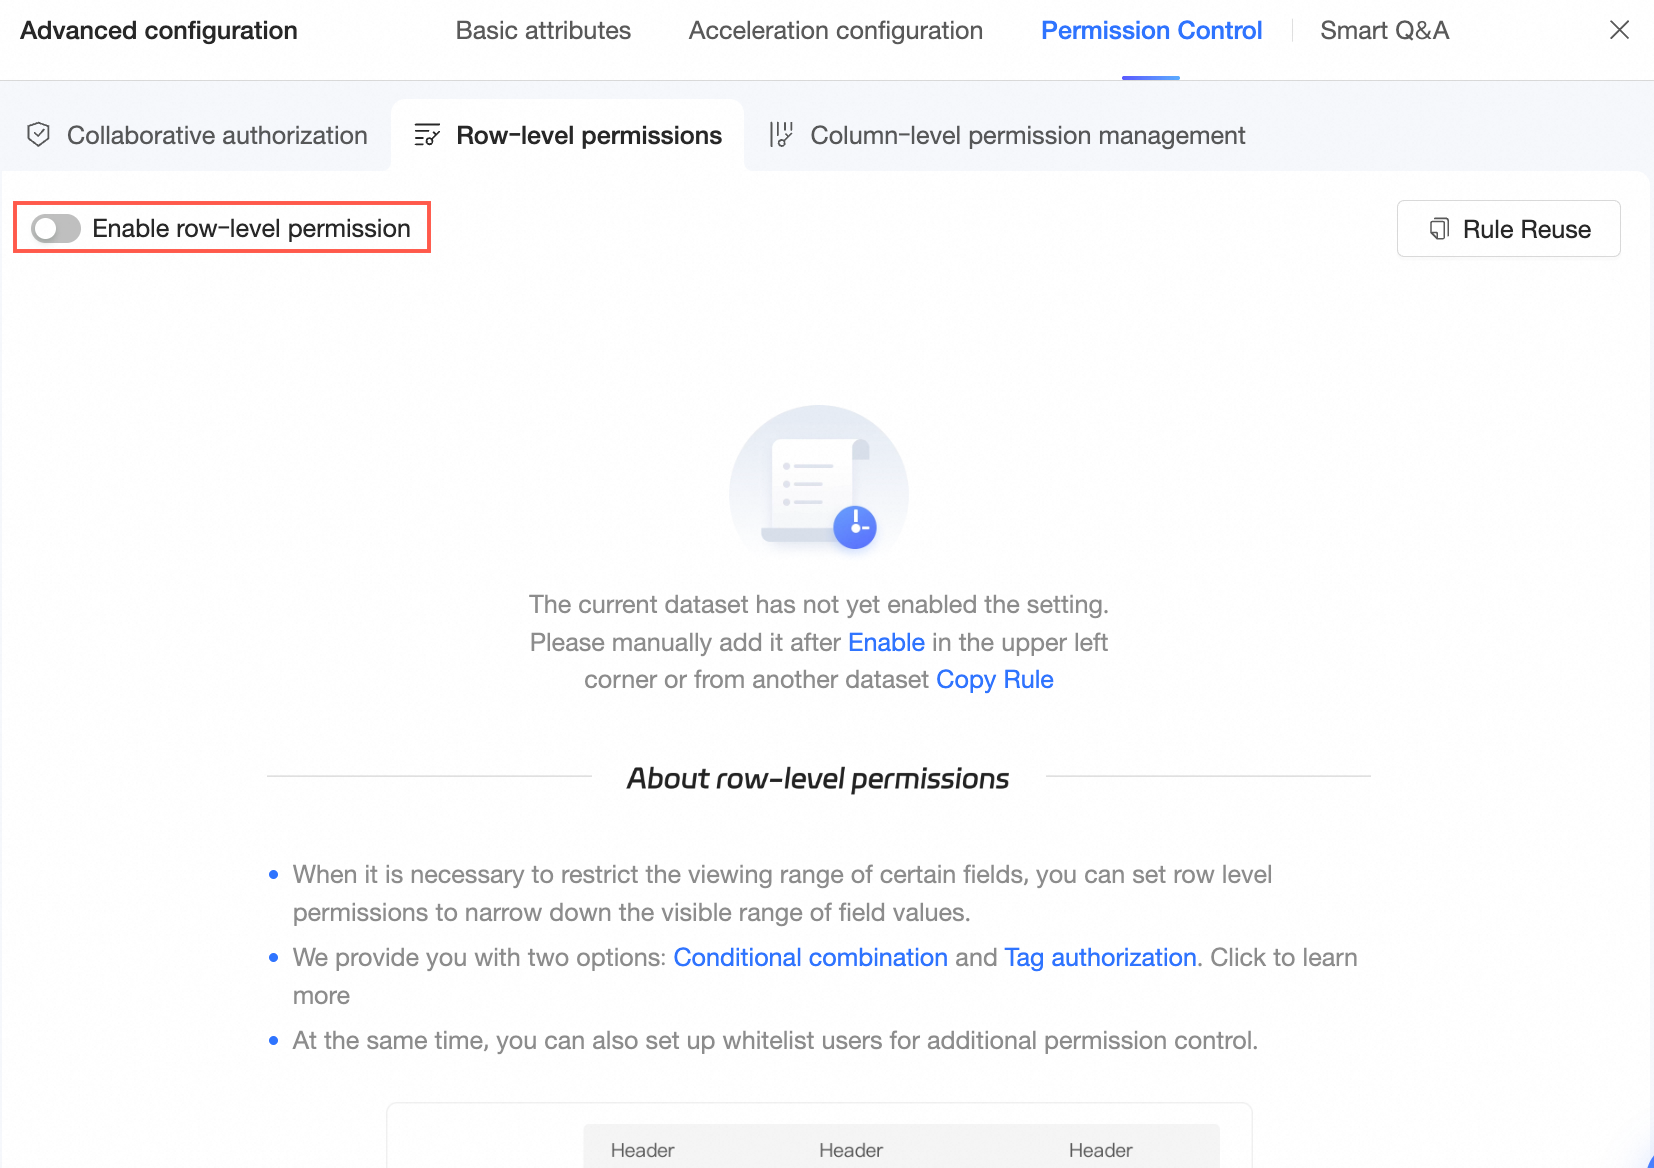
Turn on Enable Row-level Permissions.
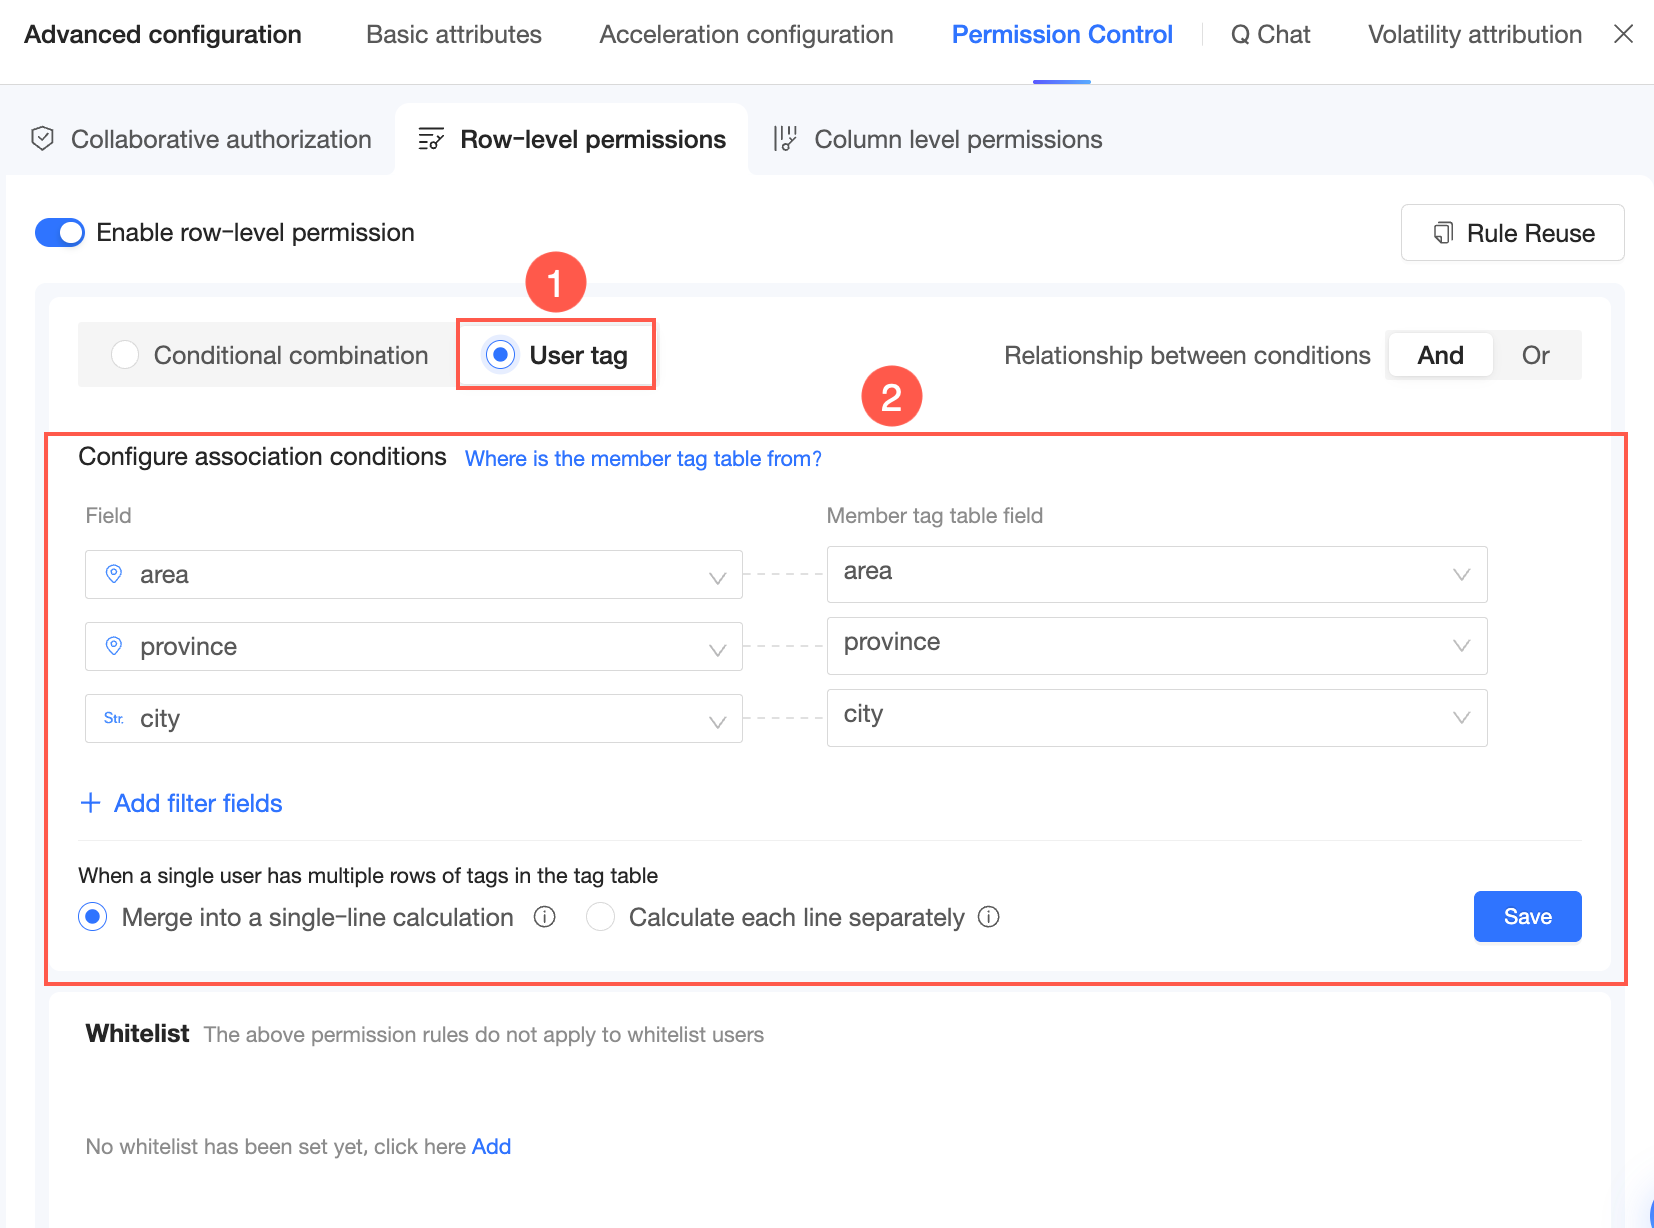
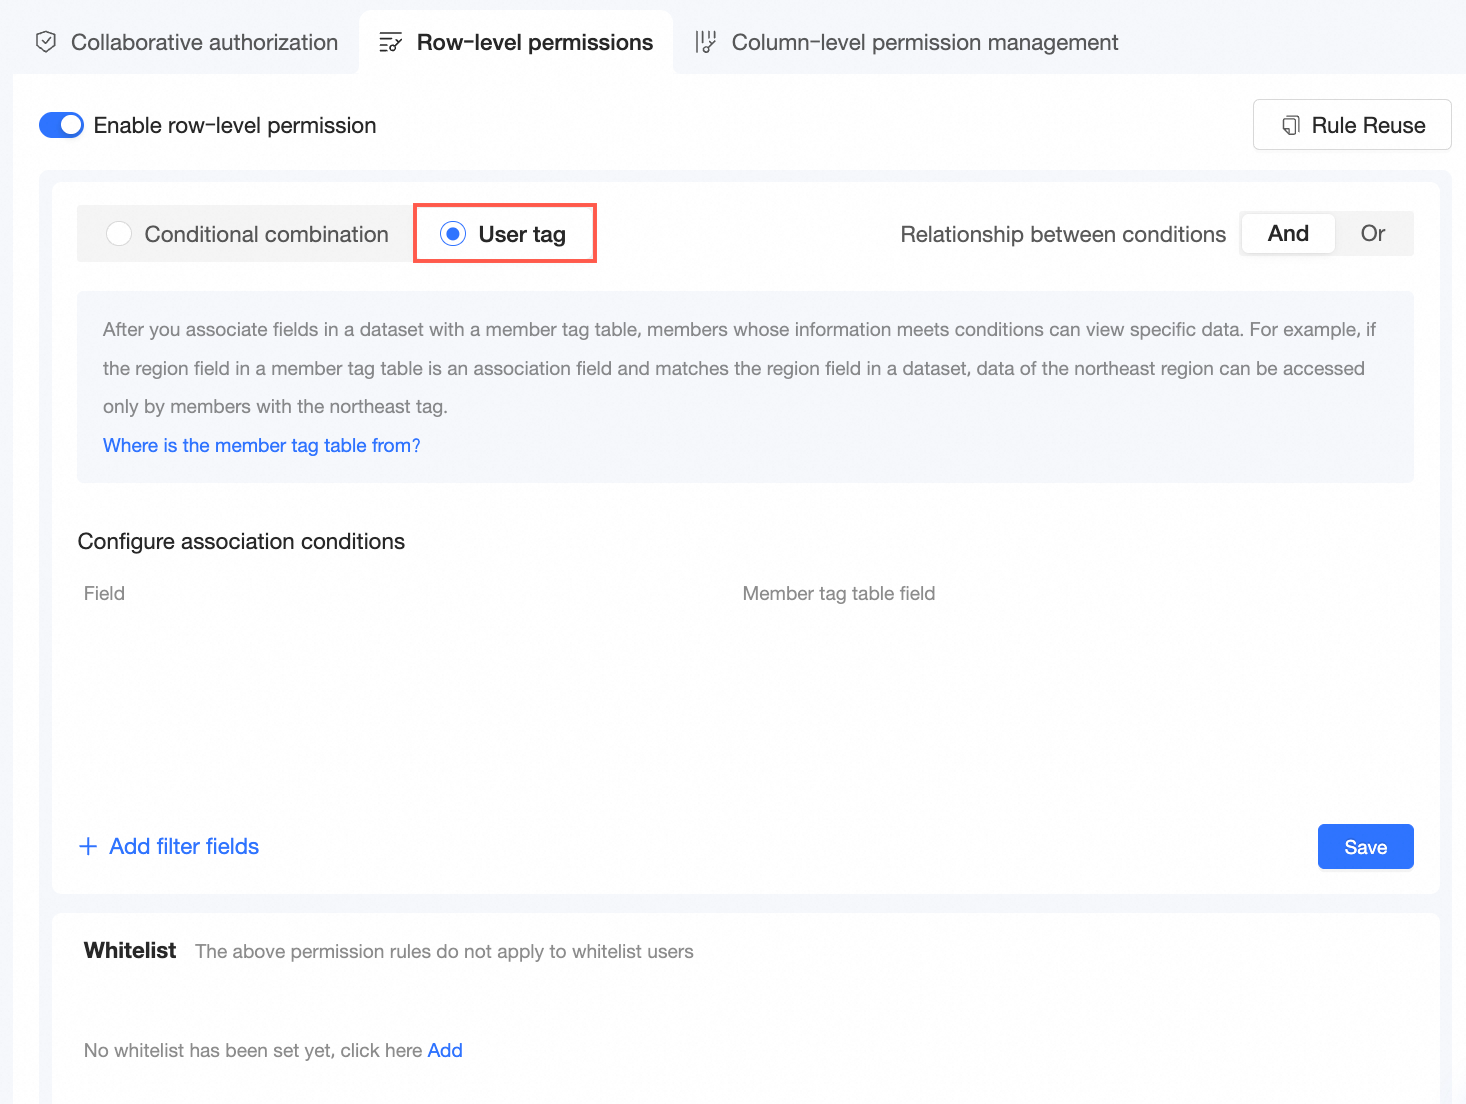
On the Row-level Permissions configuration page, select User Tag-based Authorization and configure association conditions.
Click Save.
Entry point 2
Configure row-level permissions for a dataset from the dataset editing page.
In the top toolbar, click Advanced Configurations and select Permission Control > Row-level Permissions.
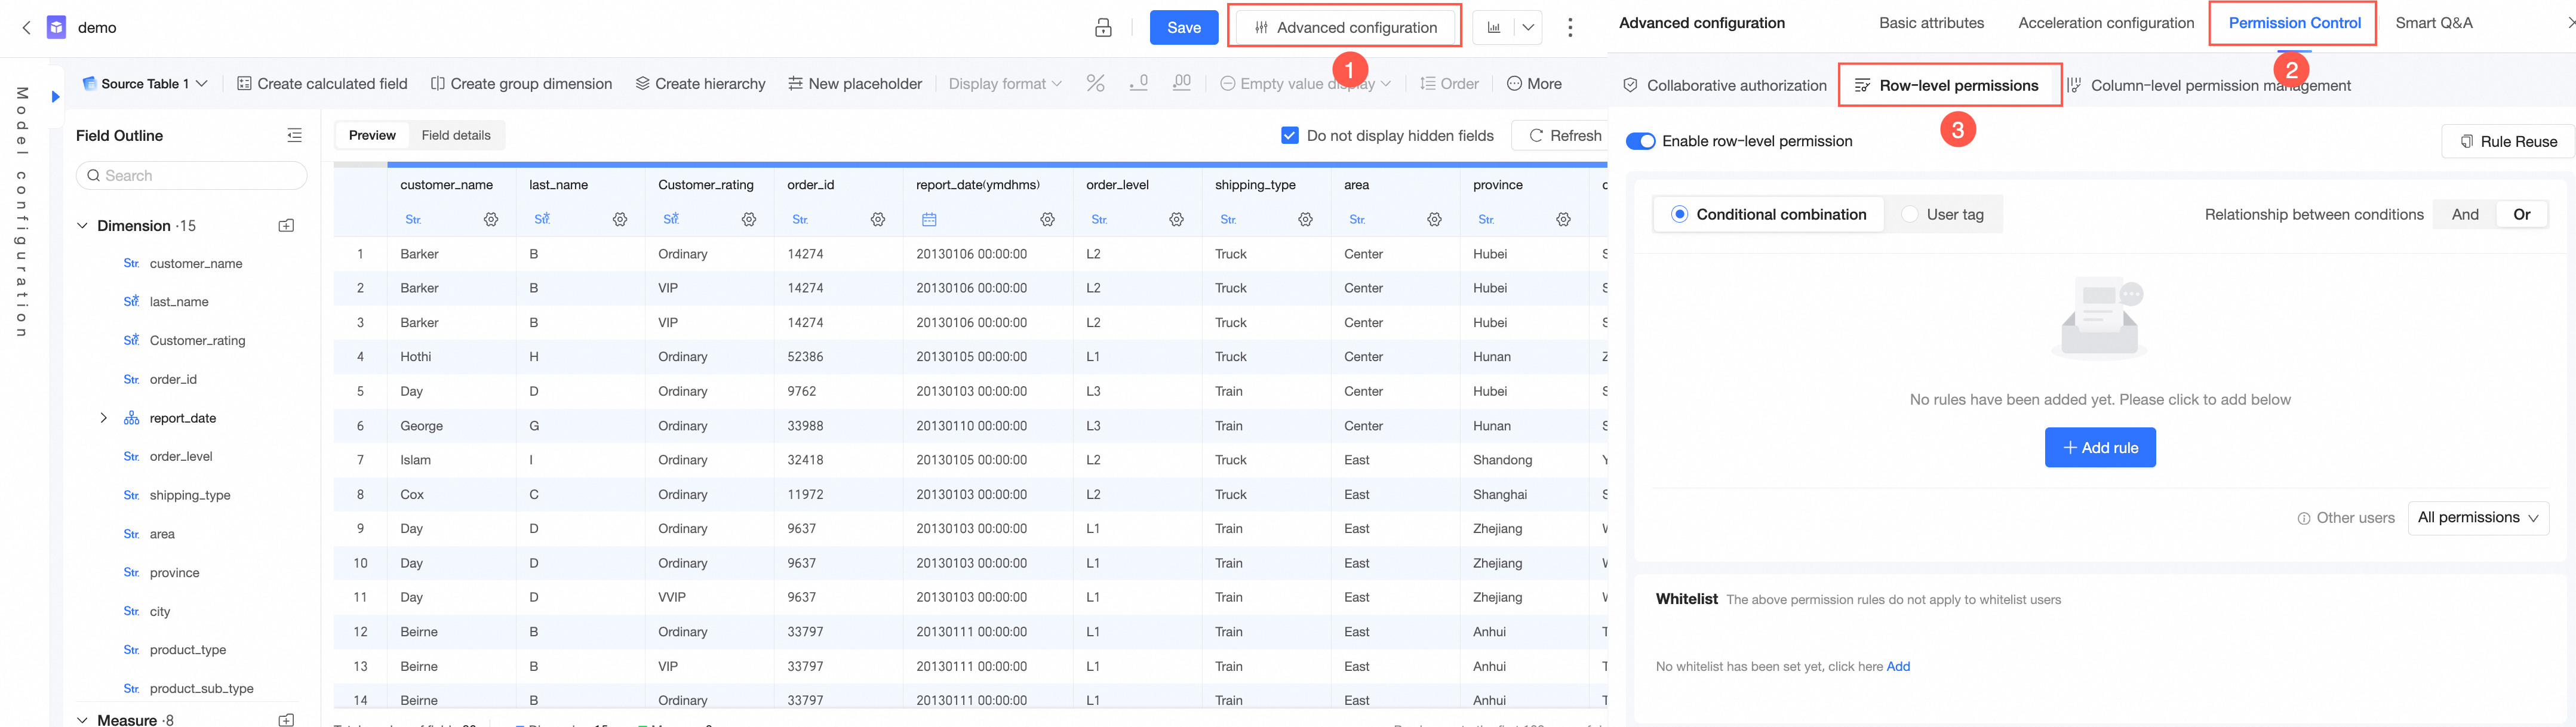
Turn on Enable Row-level Permissions.
On the Row-level Permissions configuration page, select User Tag-based Authorization and configure association conditions.
Click Save.
Entry point 3
Configure row-level permissions while you create a dataset.
On the dataset preview page, click the
 icon to go to the Row-level Permissions configuration page.

Turn on Enable Row-level Permissions.
On the Row-level Permissions configuration page, select User Tag-based Authorization and configure association conditions.
Click Save.
Configure association conditions
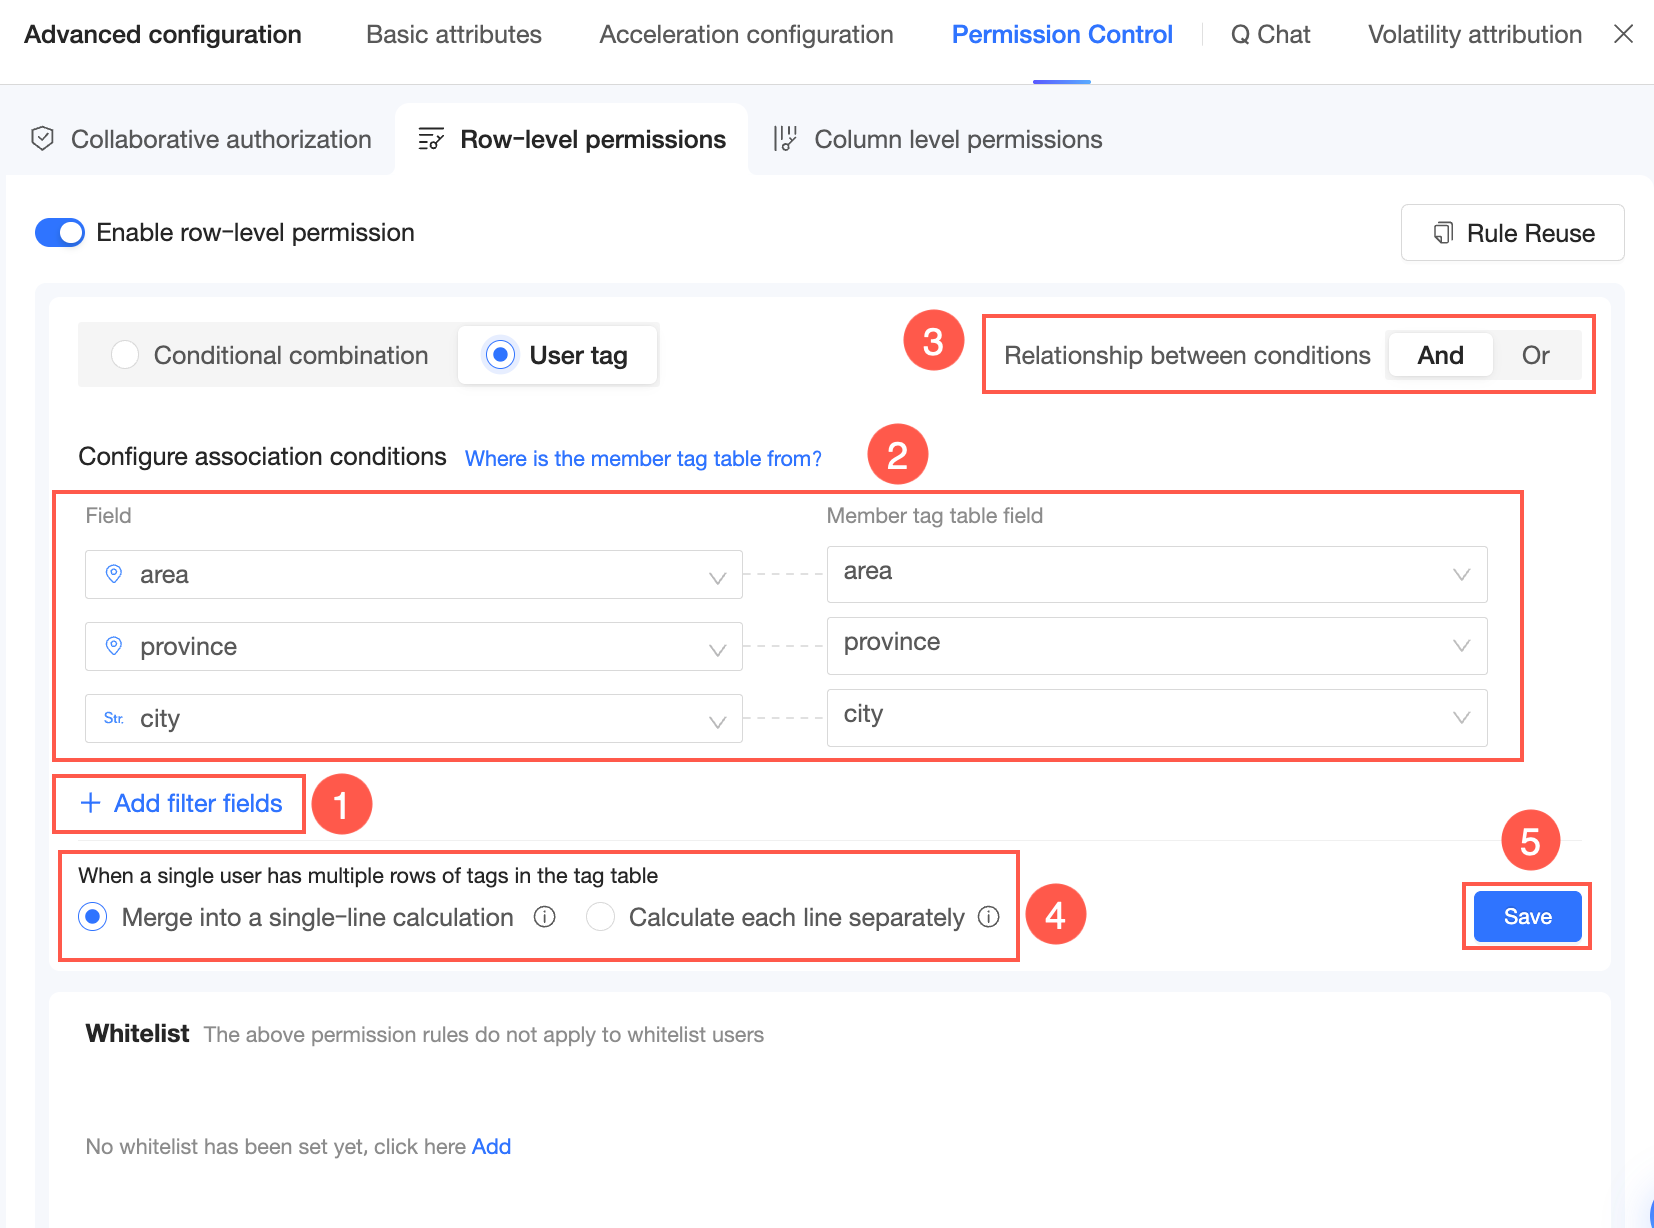
Click Add Controlled Field.
Select a controlled field and a user tag table field.
When adding multiple association conditions, select either AND or OR logic. AND requires all rules to be met, while OR requires only one rule to be met.
If the user tag table contains multiple tag rows for the same user, you can choose to merge rows for calculation or calculate rows separately.
Merge rows for calculation: Values from all tag rows are unioned and merged into a single row to verify permissions.
For example, the following is a user tag table:
User
Region
Province
City
user1
Northeast
$ALL_VALUES$
$ALL_VALUES$
user1
Southeast
Zhejiang
Hangzhou
With AND logic between conditions, the merged calculation logic is:
WHERE Region IN ('Northeast', 'Southeast')
AND 1=1 -- The Province condition is effectively ignored because $ALL_VALUES$ is a union with a specific value.
AND 1=1 -- The City condition is effectively ignored because $ALL_VALUES$ is a union with a specific value.
The effective permissions are equivalent to the following single-row tag:
User
Region
Province
City
user1
Northeast,Southeast
$ALL_VALUES$
$ALL_VALUES$
Calculate rows separately: The final permission is the logical OR of each row's permissions. You can use the calculate rows separately mode only when all user tag table fields are from the same user tag table. For example:
If the logic between conditions is AND, and the user tag table is as follows:
User
Region
Province
City
user1
Northeast
$ALL_VALUES$
$ALL_VALUES$
user1
North China,Southwest
$ALL_MEMBERS$
$ALL_MEMBERS$
user1
Southeast
Zhejiang
Hangzhou
The logic for calculating rows separately is as follows:
WHERE (Region = 'Northeast') -- Province and City conditions are ignored due to $ALL_VALUES$.
OR (Region IN ('North China', 'Southwest')) -- $ALL_MEMBERS$ grants access to all provinces and cities within the specified regions.
OR (Region = 'Southeast' AND Province = 'Zhejiang' AND City = 'Hangzhou')
If the logic between conditions is OR, and the user tag table is as follows:
User
Region
Product Type
user1
Northeast
$ALL_VALUES$
user1
North China,Southwest
$ALL_MEMBERS$
user1
Southeast
Furniture
The logic for calculating rows separately is as follows:
WHERE (Region = 'Northeast' OR 1=1) -- The Product Type condition becomes true due to $ALL_VALUES$.
OR (Region IN ('North China', 'Southwest') OR 1=1) -- The Product Type condition becomes true due to $ALL_MEMBERS$.
OR (Region = 'Southeast' OR Product Type = 'Furniture')
The effective permissions are equivalent to the following single-row tag:
User
Region
Product Type
user1
Northeast,North China,Southwest,Southeast
$ALL_VALUES$
Click Save.
Configure a whitelist
If you want to exempt specific users from the preceding rules, you can add them to the whitelist.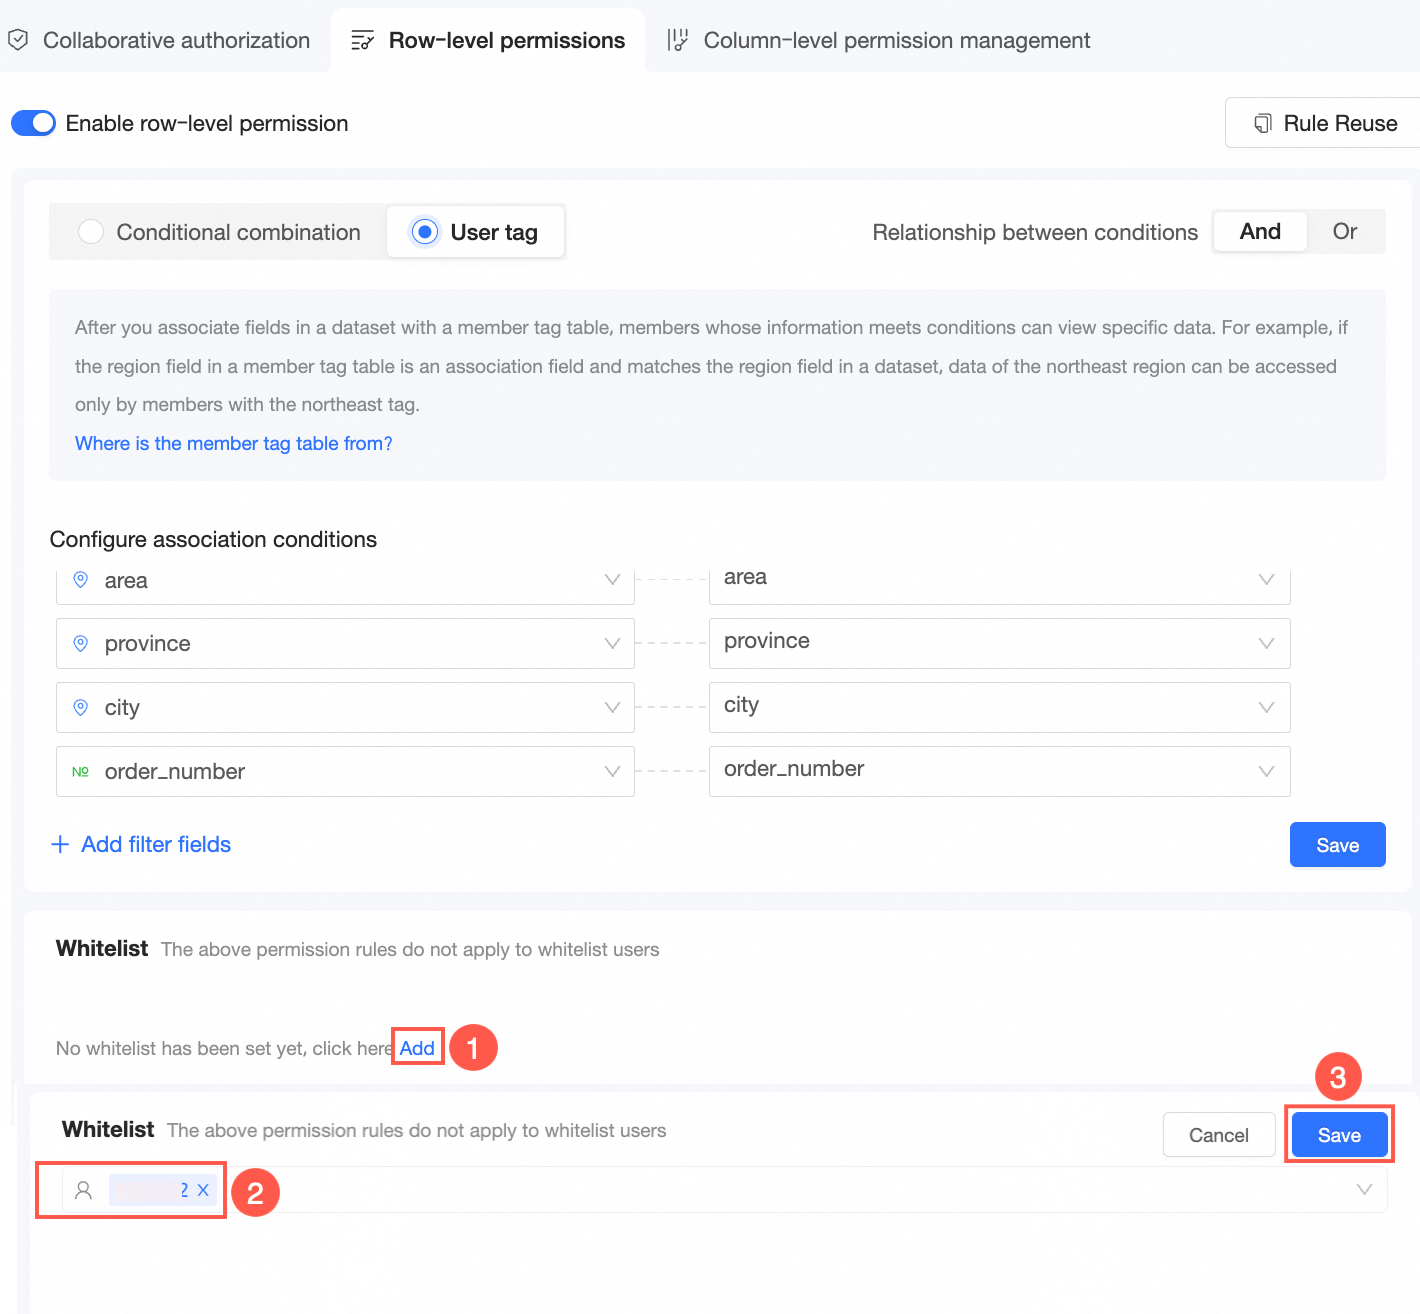
Copy row-level permissions
You can copy row-level permissions from another dataset. For more information, see Copy row-level permissions.
Application scenarios
Tags can originate from a user-managed user tag table or from tags that are manually configured in Quick BI. The following sections describe these two scenarios.
Scenario | Steps |
| |
|
Scenario 1: Bind a user tag table
Create a custom user tag table.
Binding a user tag table from your data source ensures that Quick BI always reads the latest tag information, eliminating manual maintenance.
When you create a custom tag table, make sure that it meets the following requirements:
It must contain at least one of the following fields: Alibaba Cloud account ID (
account_id), Alibaba Cloud account name (account_name), or nickname in the Quick BI organization (nick_name).NoteIf you use an Alibaba Cloud account ID or account name, make sure that the corresponding user already exists in your Quick BI organization.
It must contain at least one tag field, such as area.
If a user has multiple values for a single tag, you can separate the values with a comma (,) in a single row or list them in multiple rows.
The value
$ALL_MEMBERS$grants permissions on all data for that field.
Bind the user tag table.
After you bind the table, one of its fields, such as the Alibaba Cloud account ID, Alibaba Cloud account name, or nickname, is used as a primary key to associate users with members of your Quick BI organization.
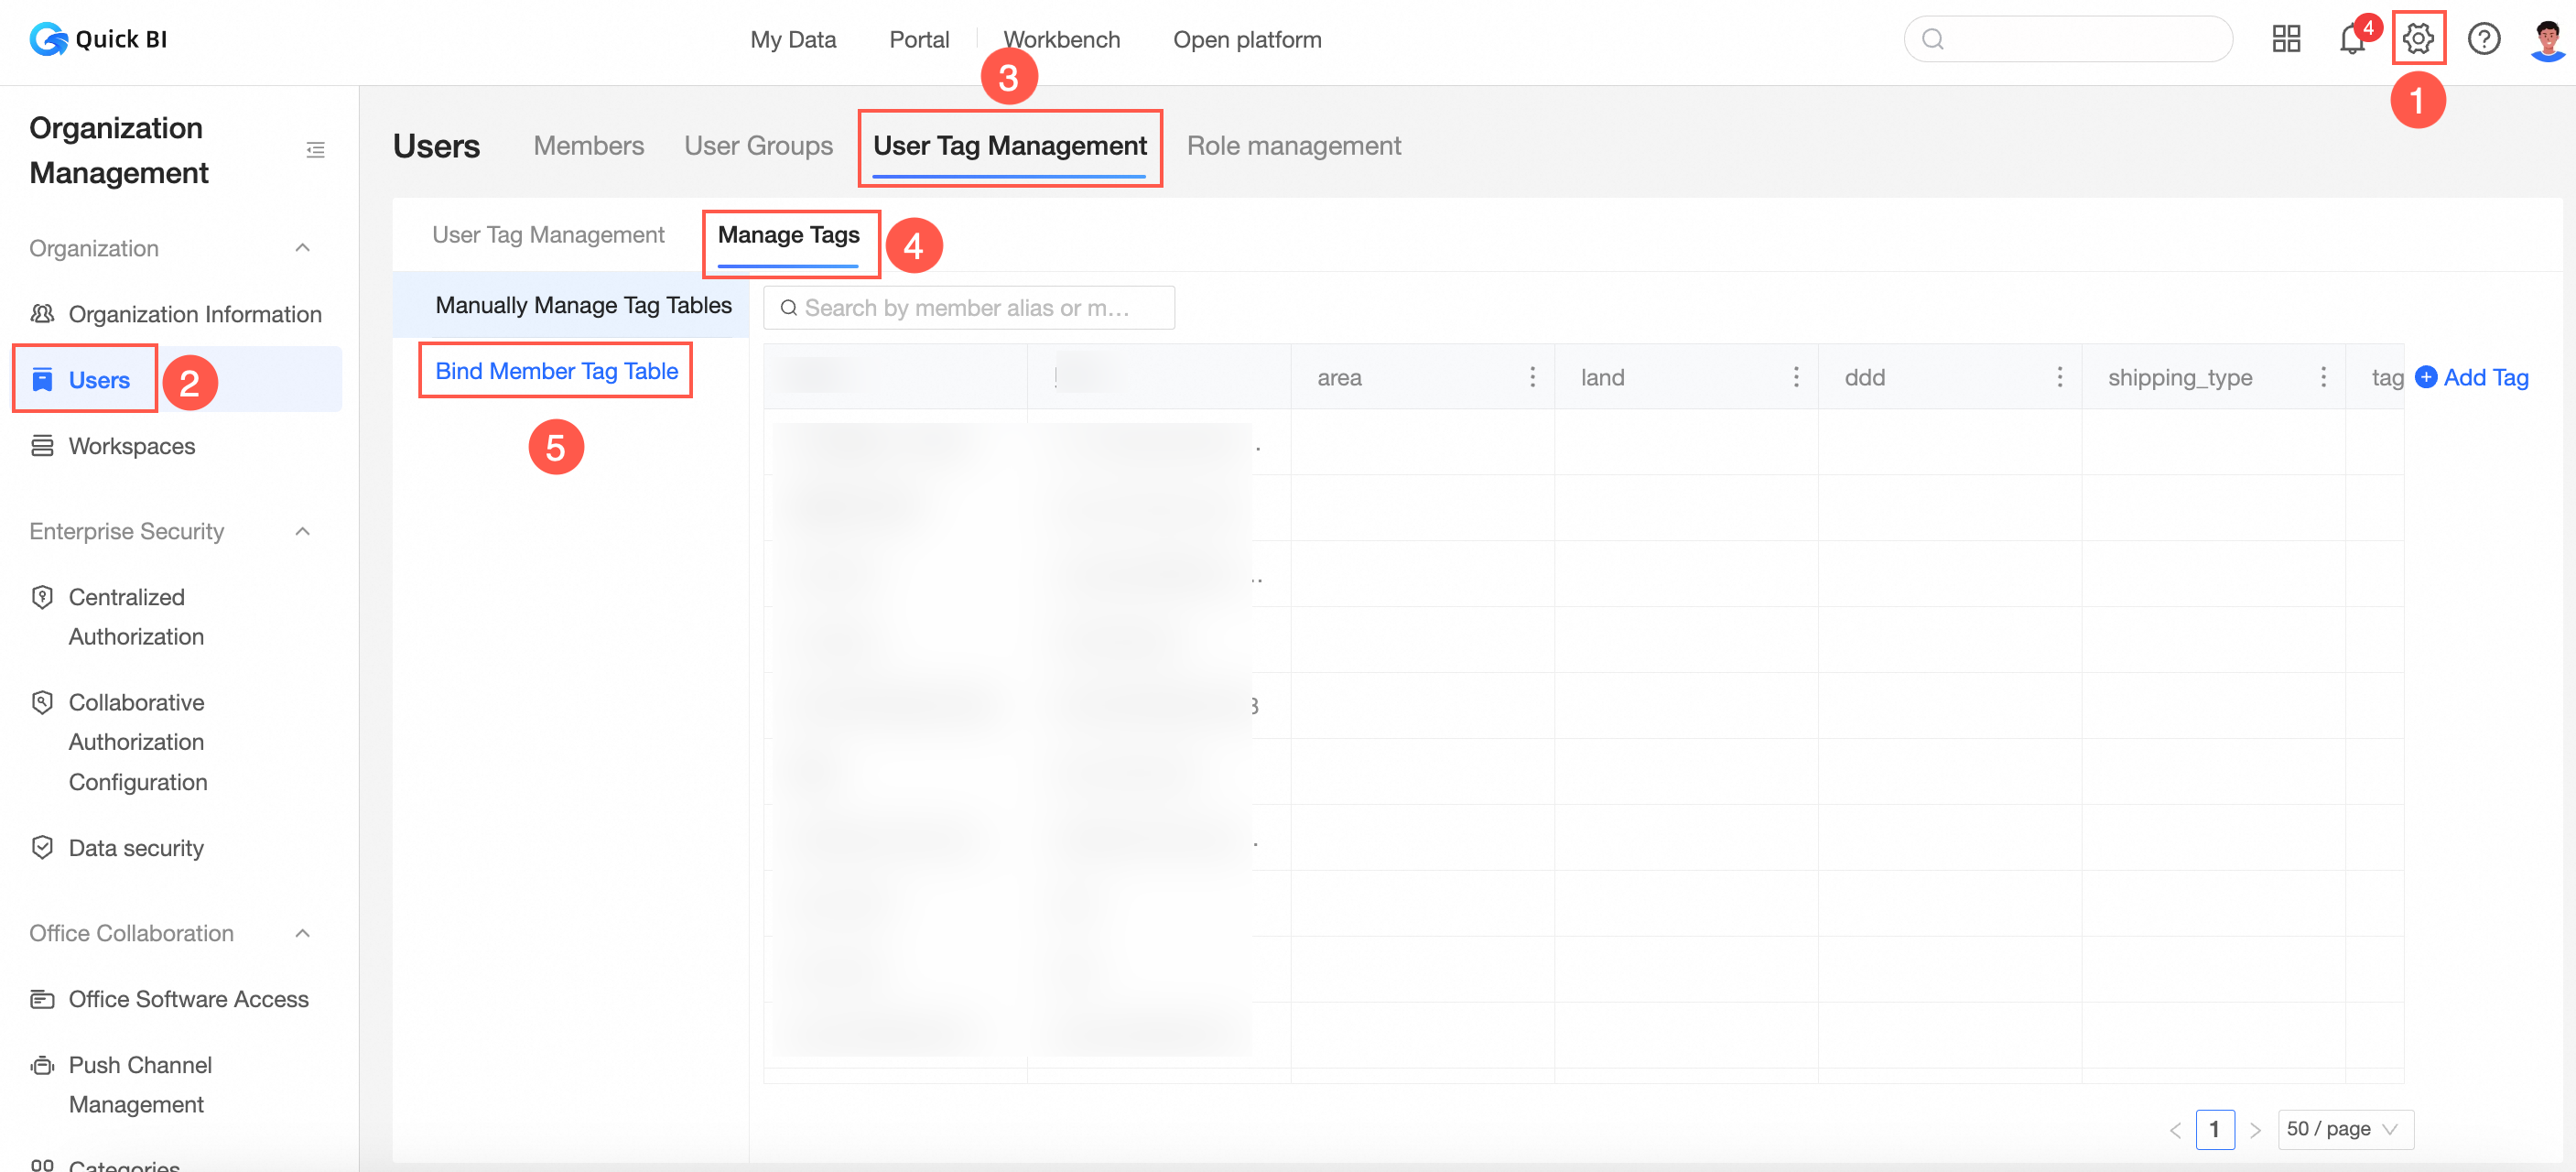
Log on to the Quick BI console.
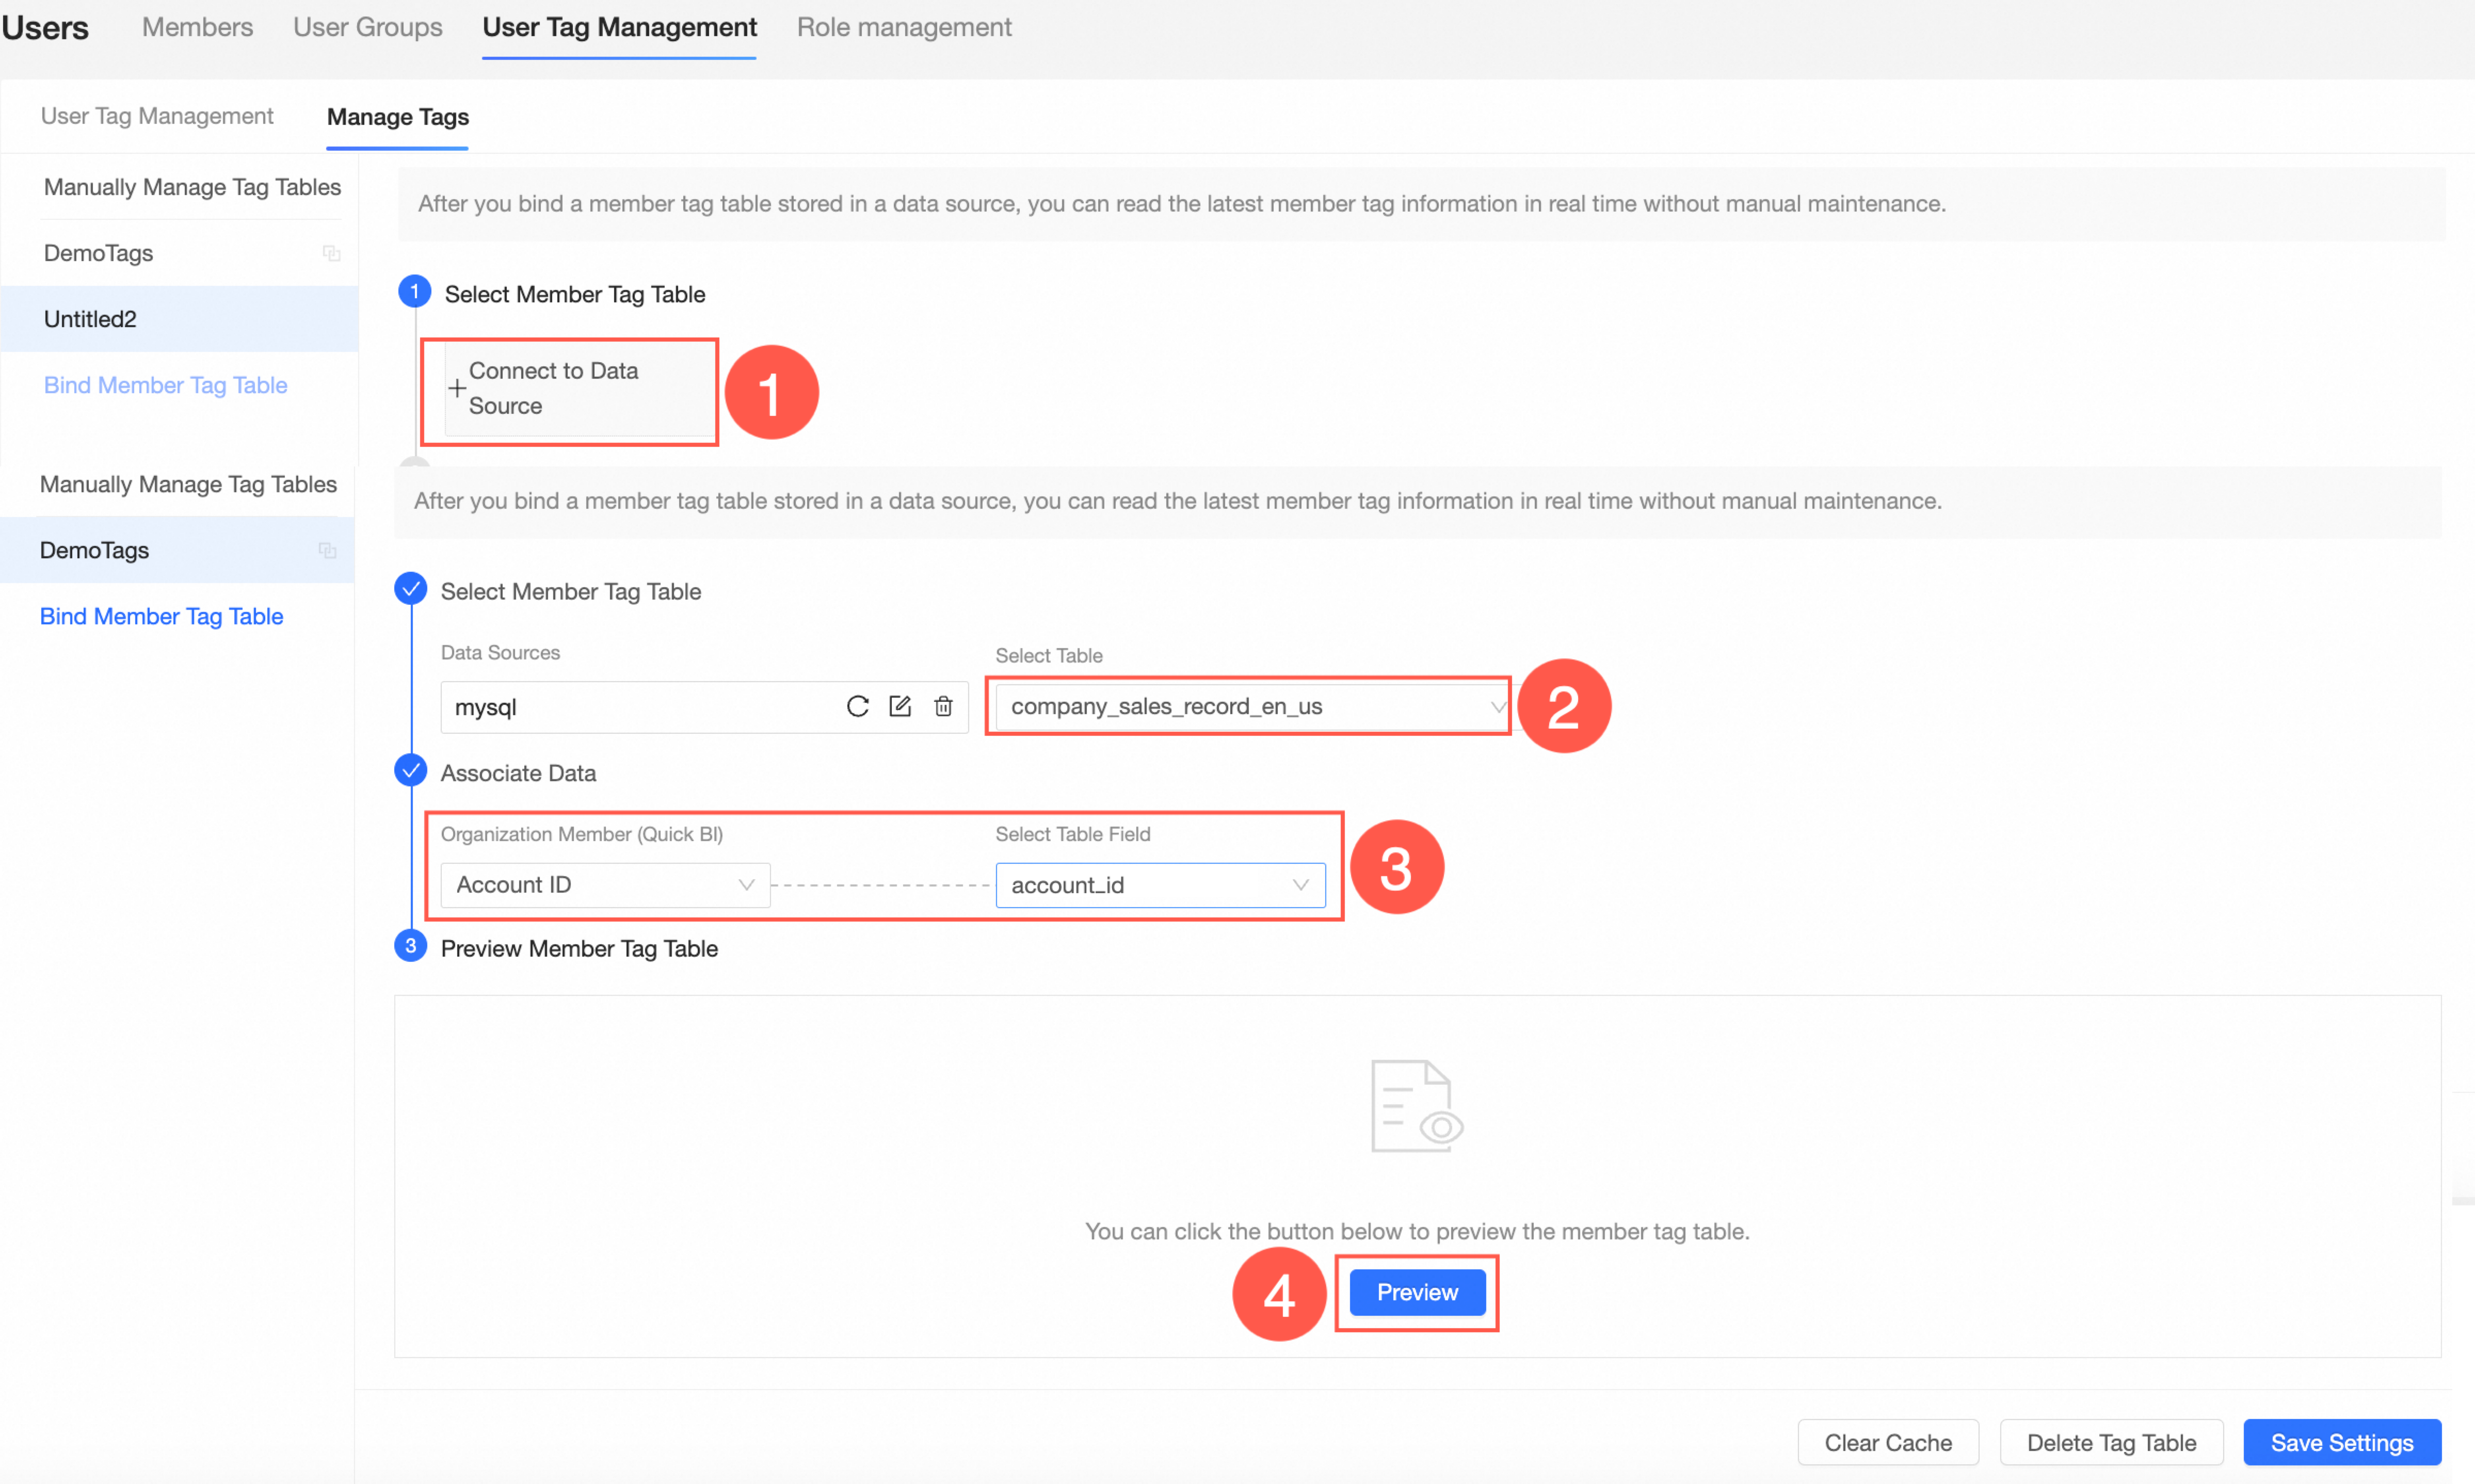
On the Quick BI homepage, follow the steps in the figure to go to the tag table binding page.
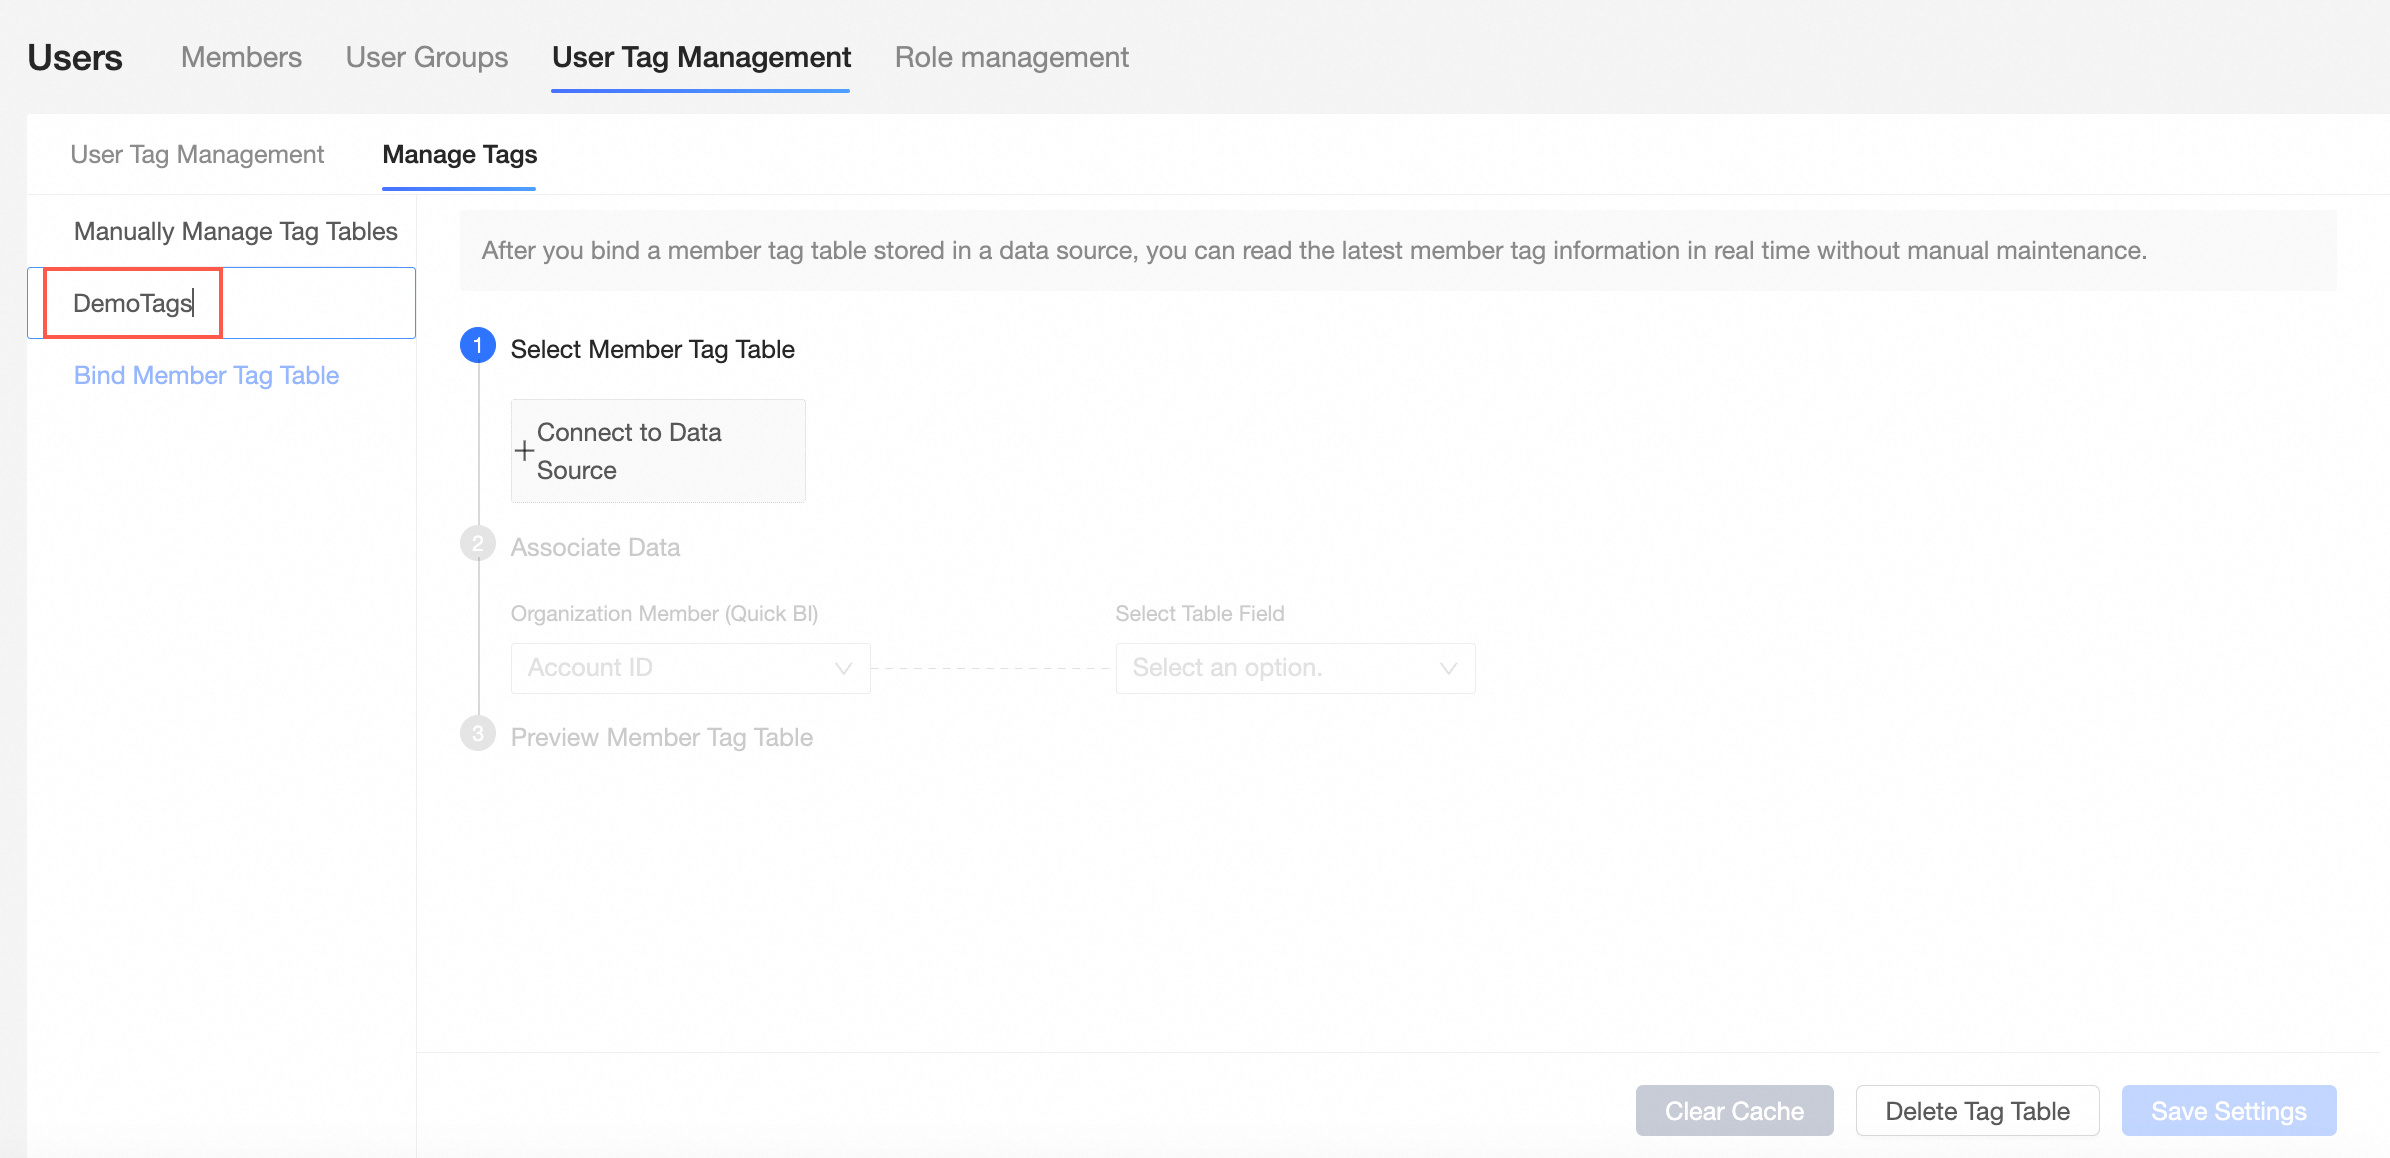
Enter a custom name for the user tag table that you want to bind.
In this example, the user tag table is named Demo Tag Table.
Follow the steps in the figure to configure the user tag table binding.
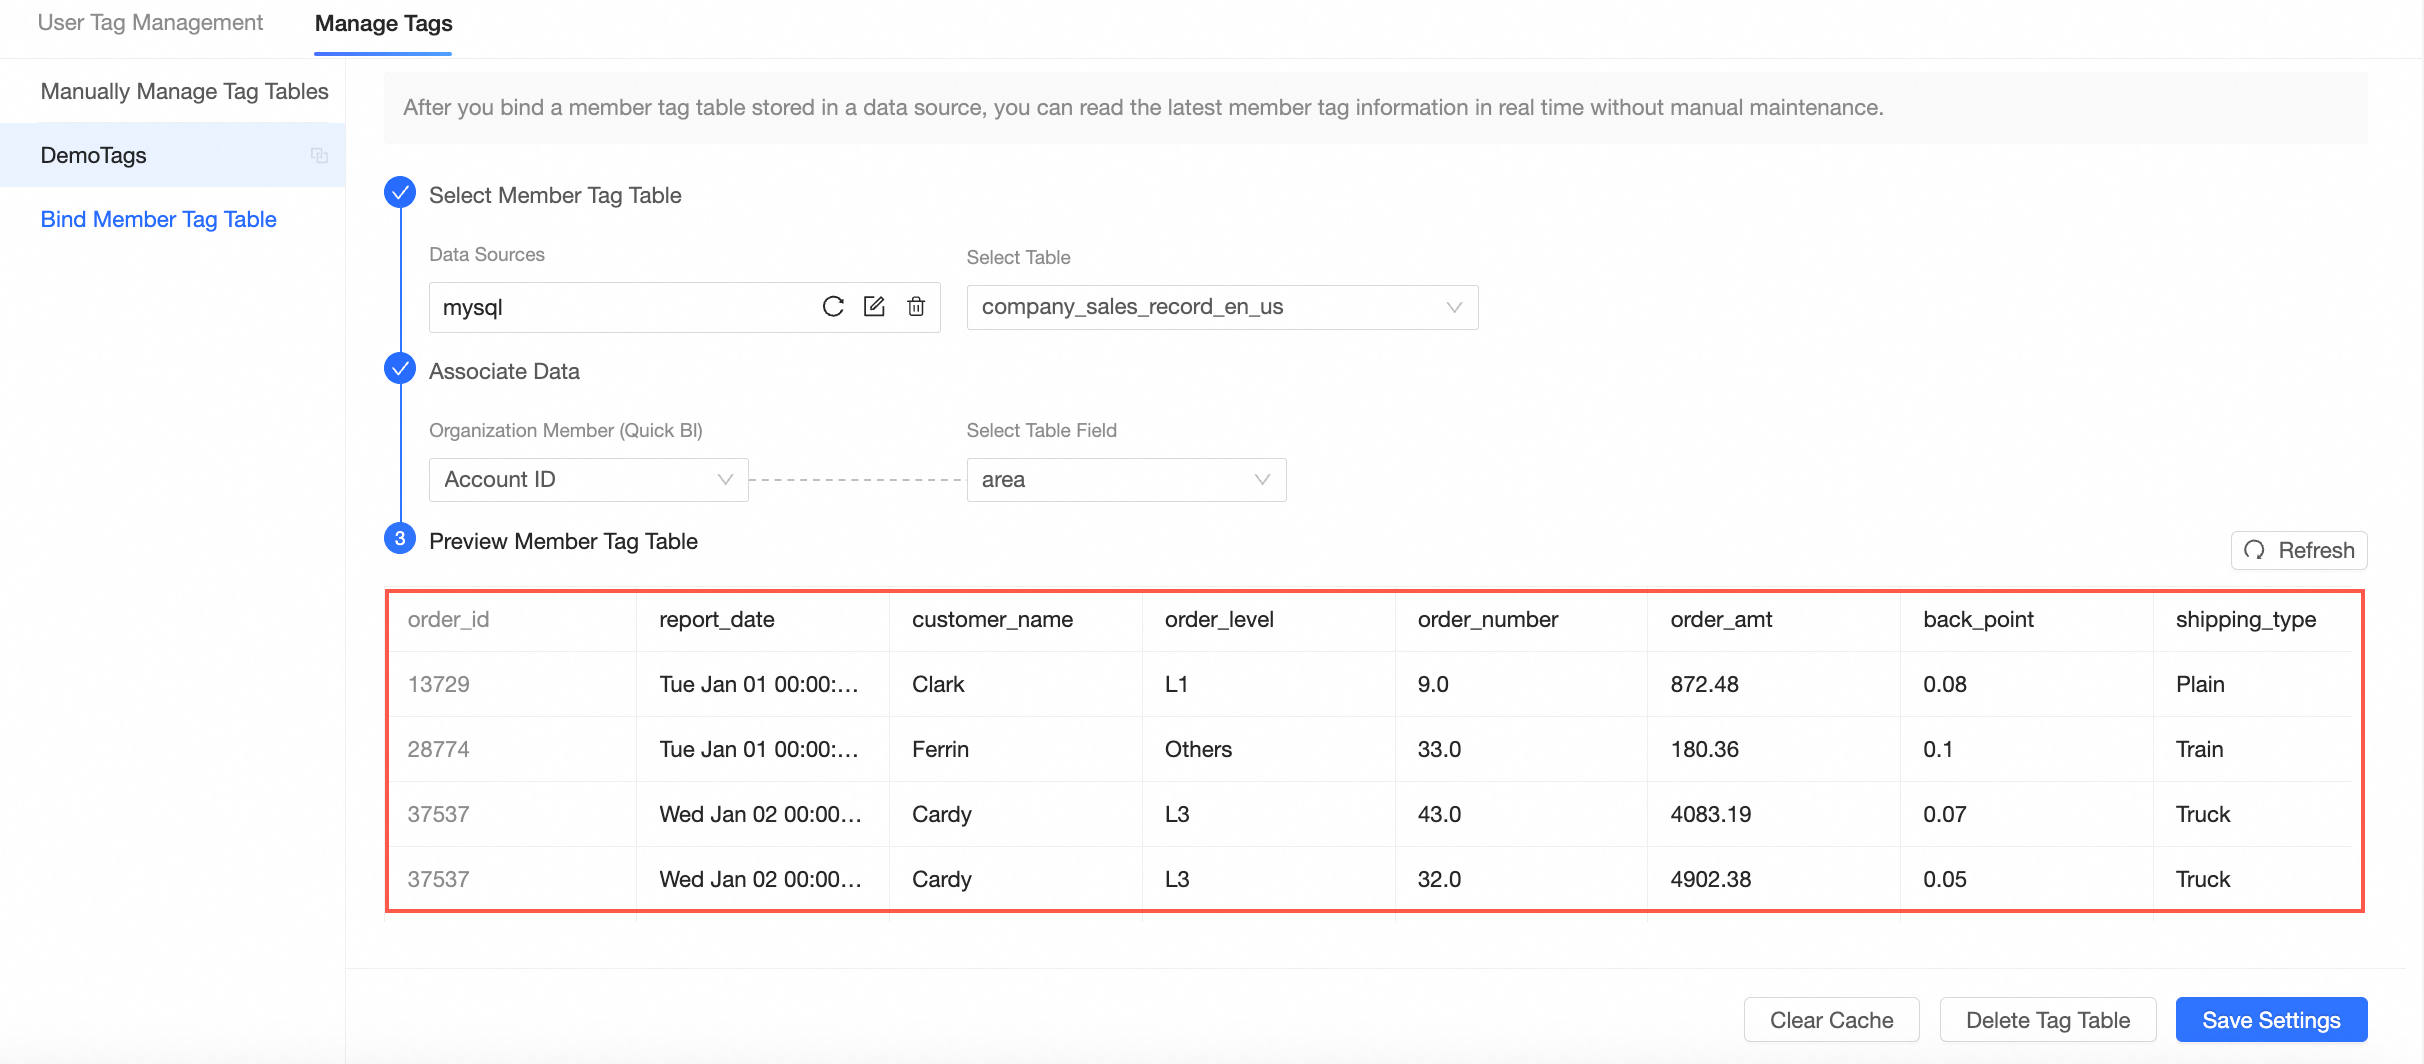
A preview of the user tag table is shown in the following figure.
Add a user tag.
Once associated, Quick BI passes the values from the user tag table to the corresponding user tags.
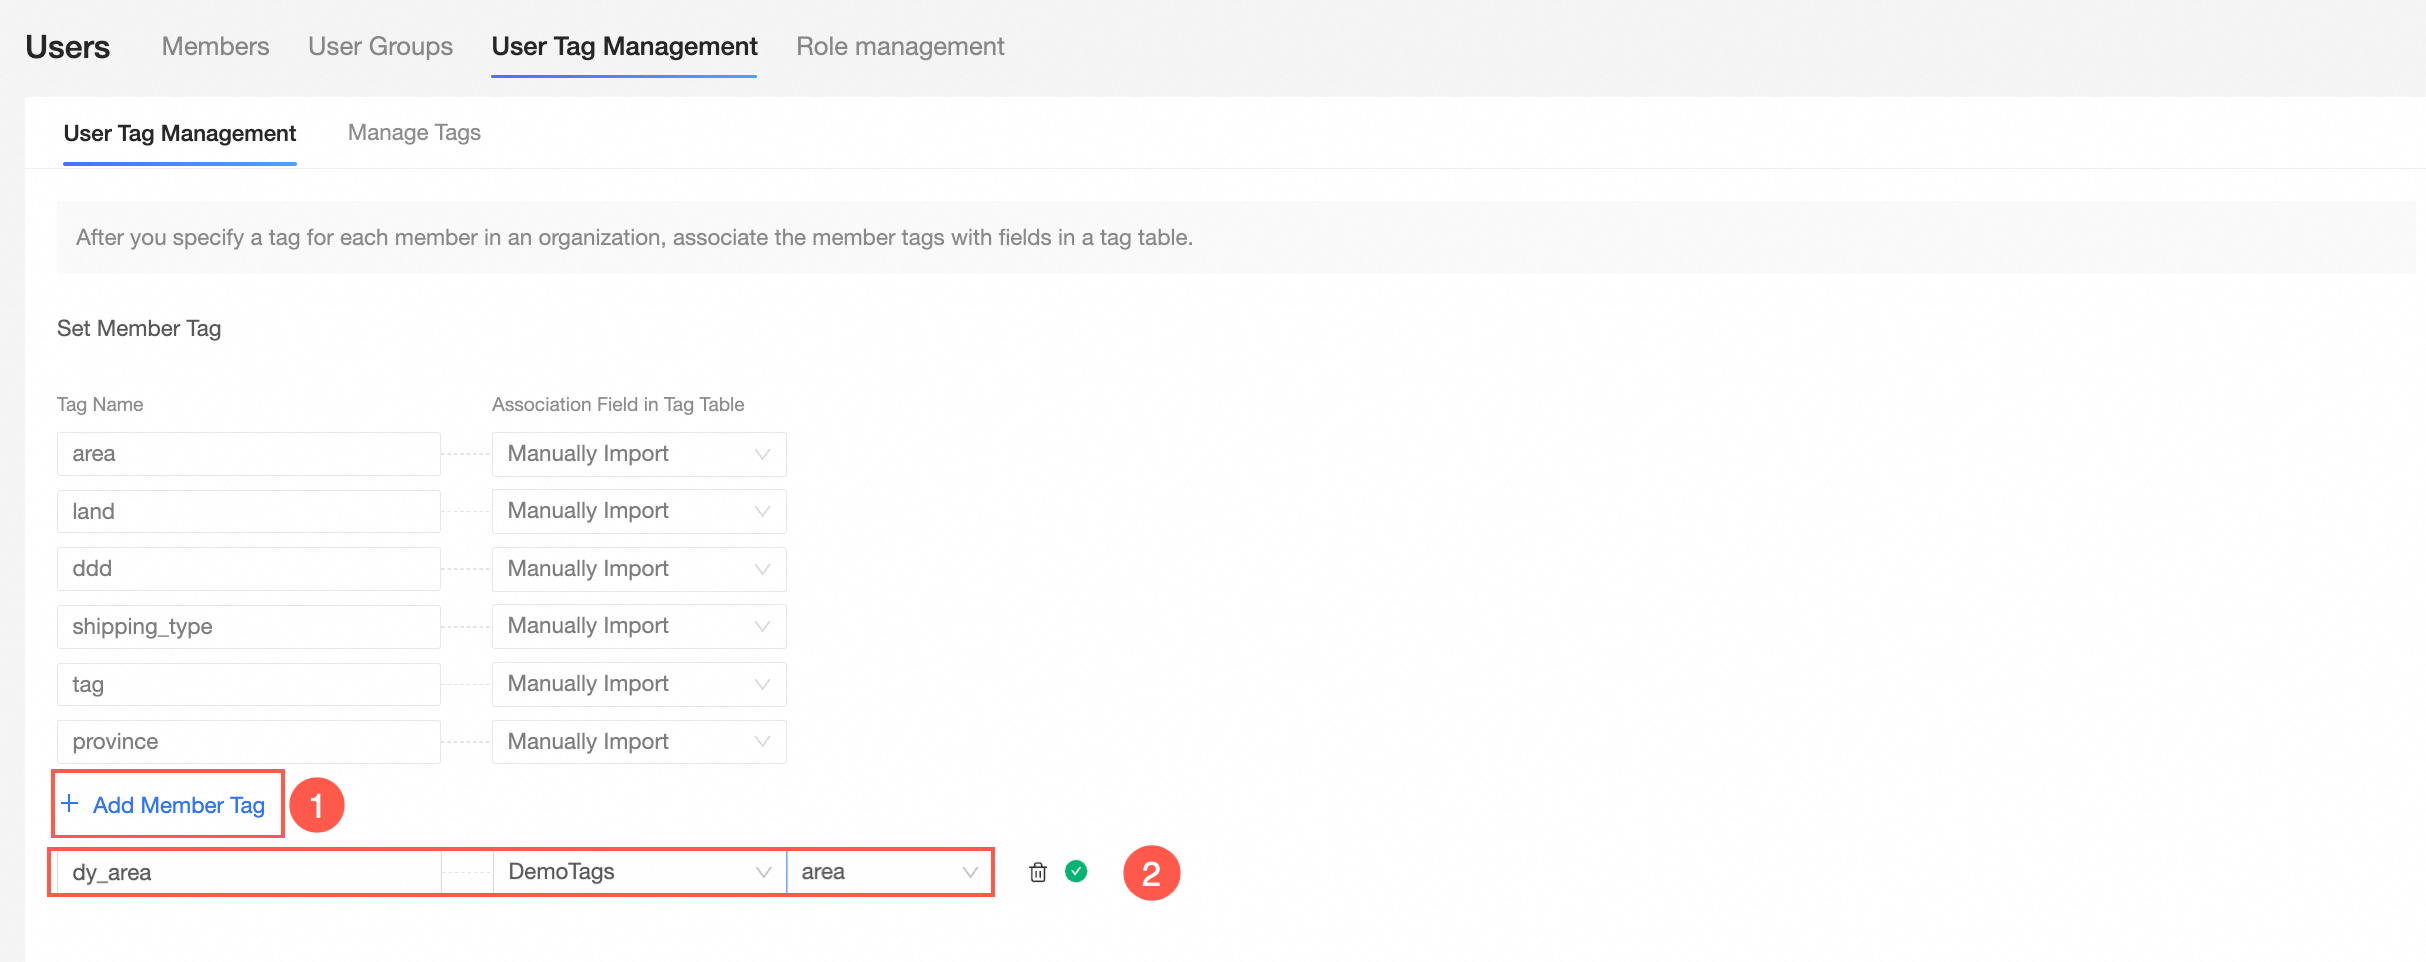
Click the User Tag Management tab and then click Add User Tag.
Enter a Tag Name and select an Associated Tag Table Field. Then, save the configuration.
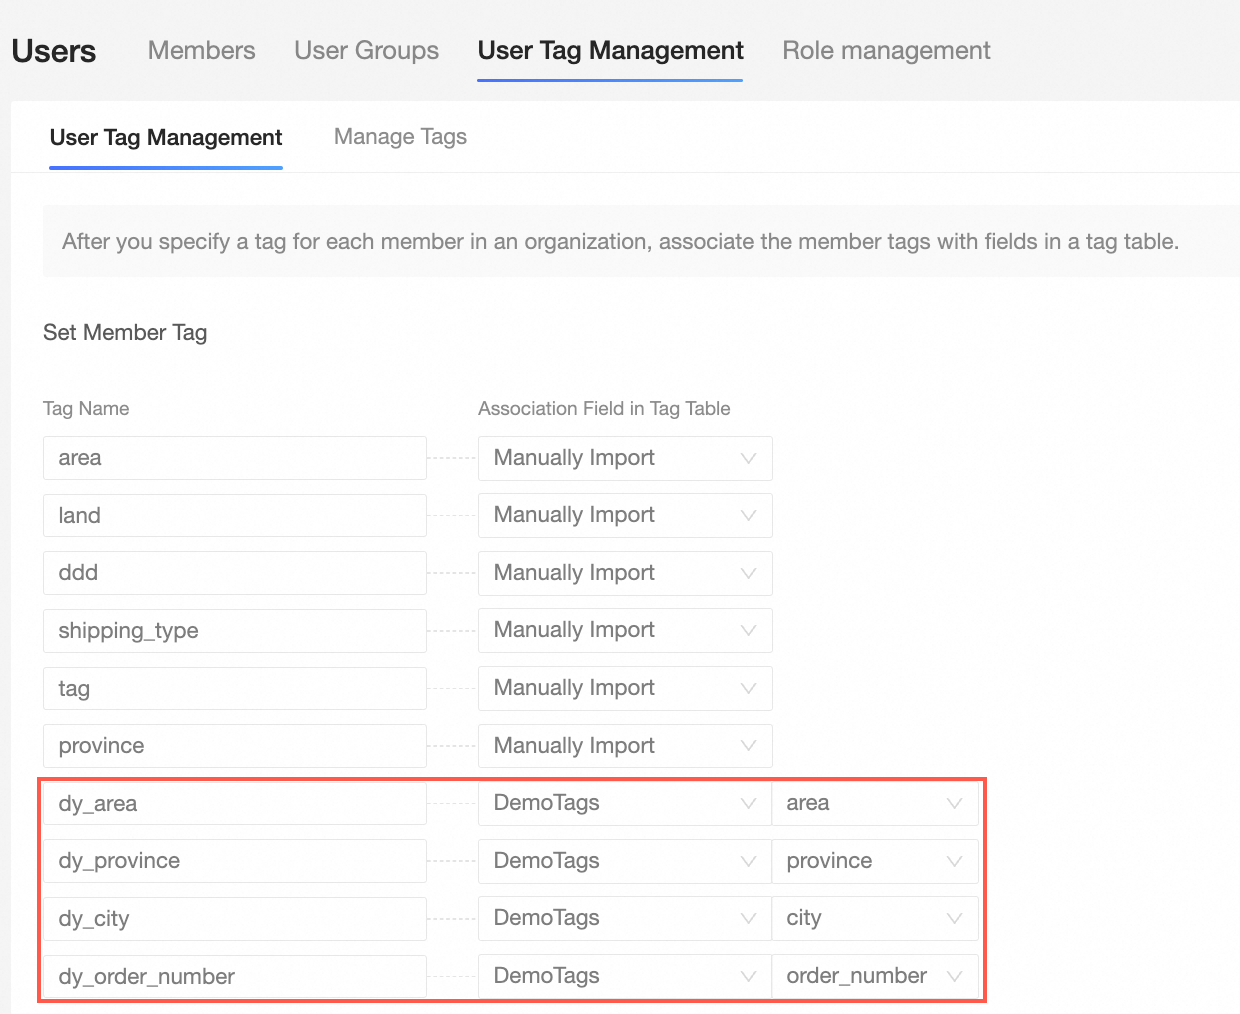
For the association, select Demo Tag Table. Create custom tag names, such as dy_area, dy_province, dy_city, and dy_order_number. Then, bind them to the area, province, city, and order_number fields in the Demo Tag Table.
Use tag-based authorization.
After you grant permissions, these tag values apply to all relevant datasets, ensuring that users can view only data within their permitted scope.
On the Quick BI homepage, follow the steps in the figure to go to the row-level permissions settings page.
Turn on the Enable Row-level Permissions switch and select User Tag-based Authorization for the Authorization Method.
In the Configure Association Conditions section, click Add Controlled Field.
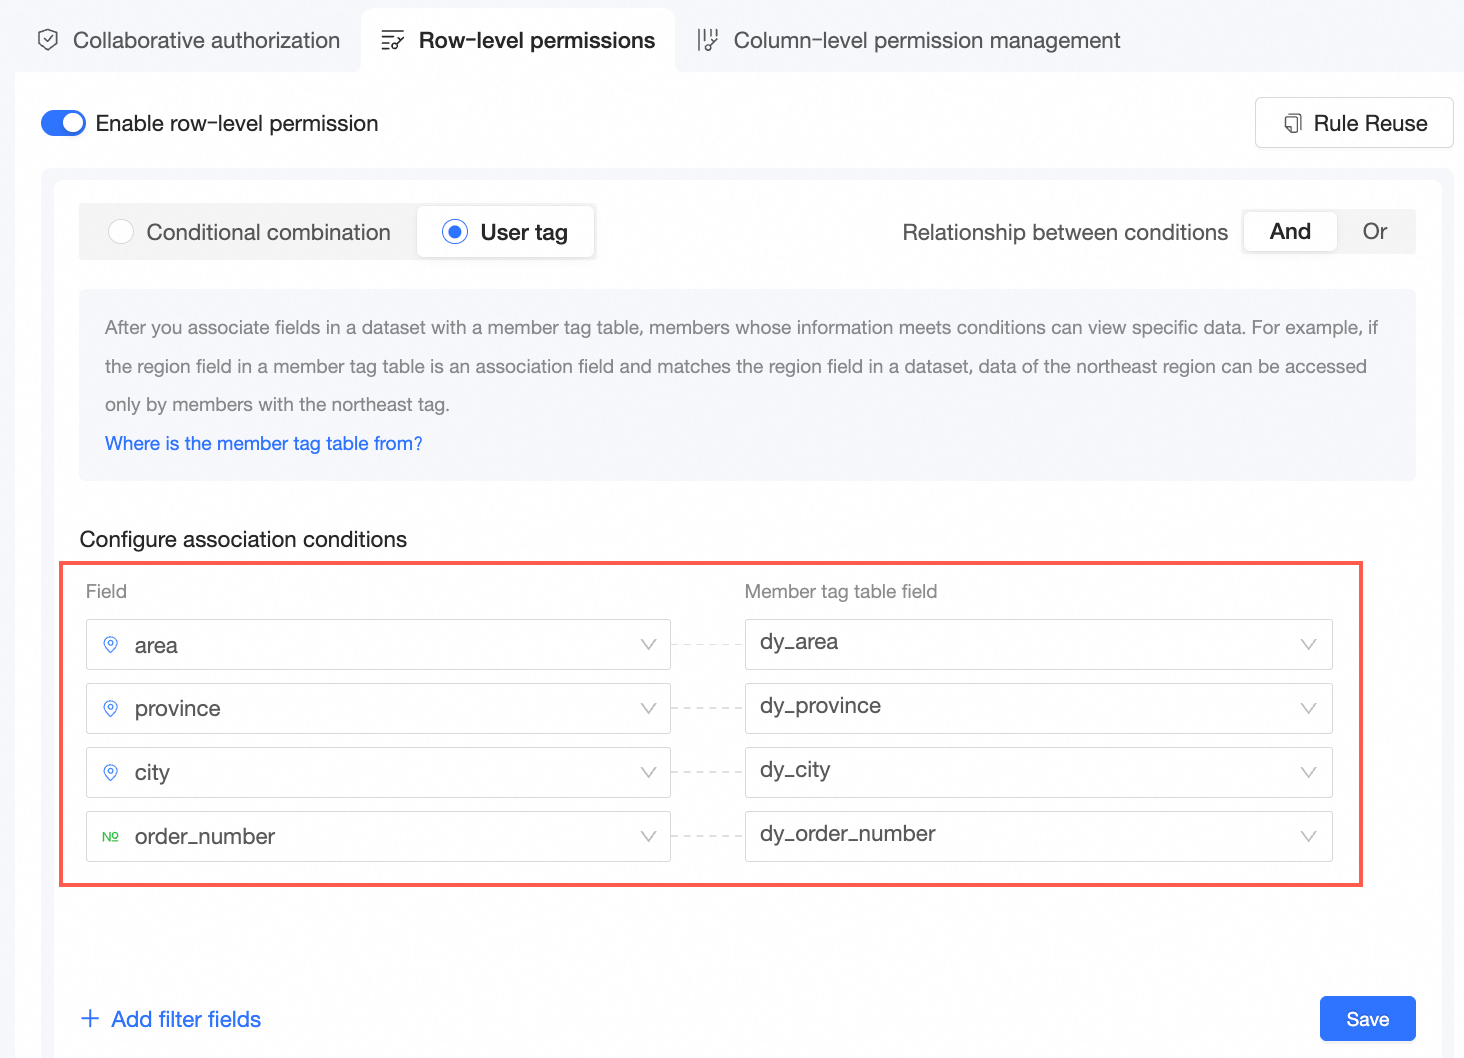
Select a controlled field and bind it to a user tag table field.
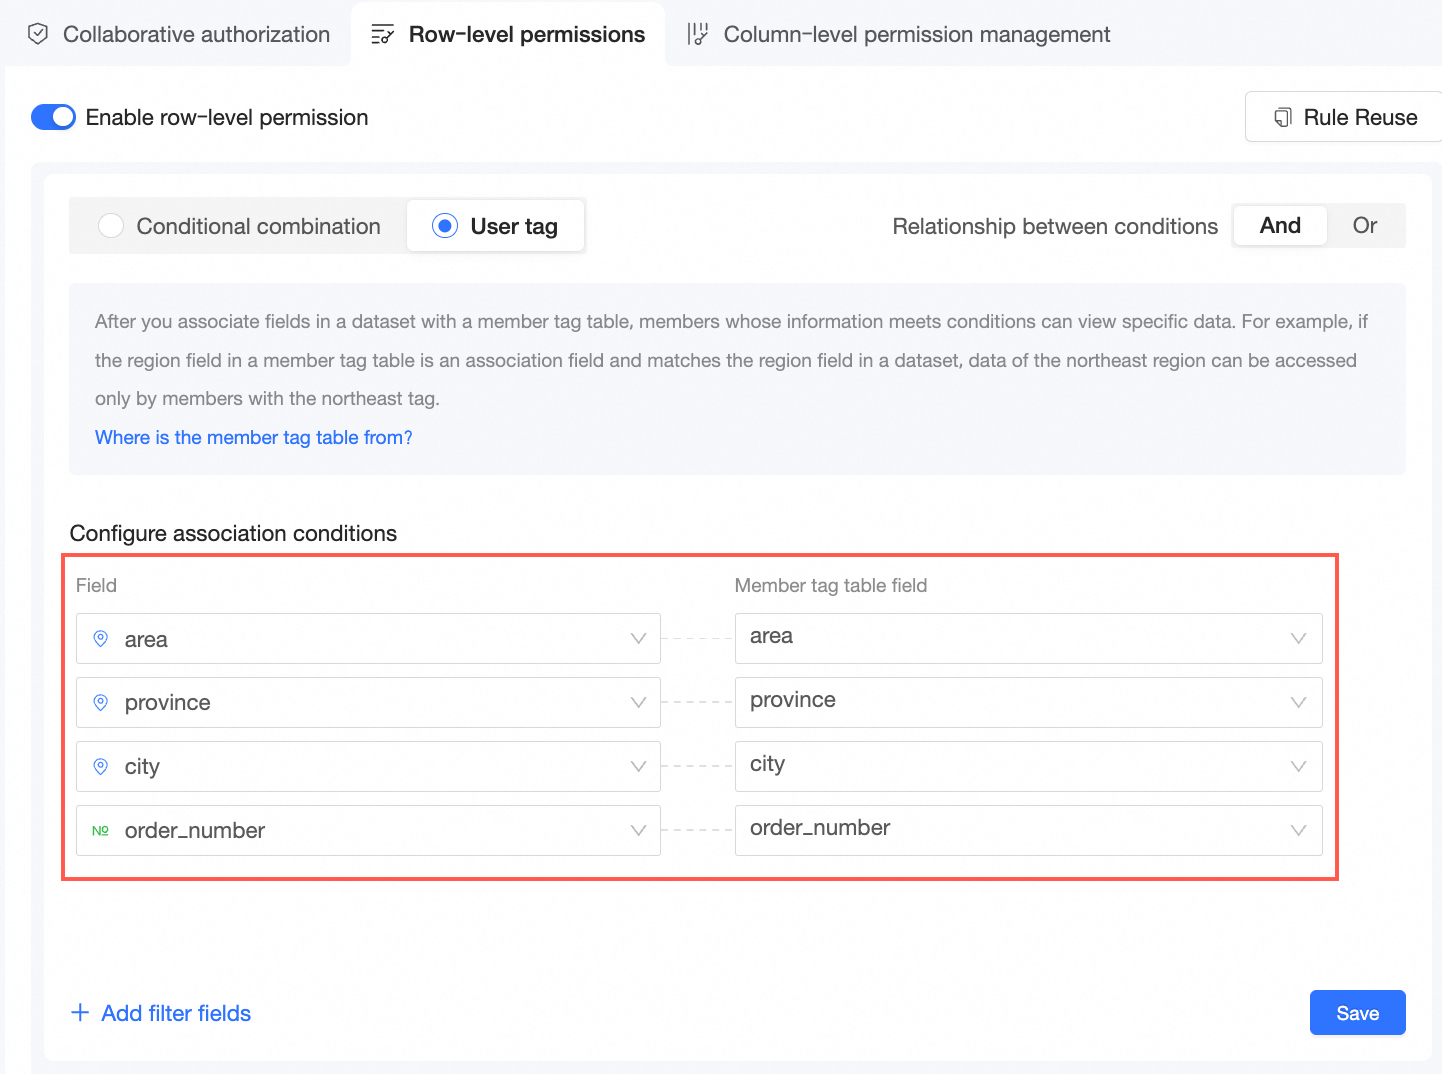
The controlled fields and user tag table fields selected in this example are shown in the following figure.
Click Save.
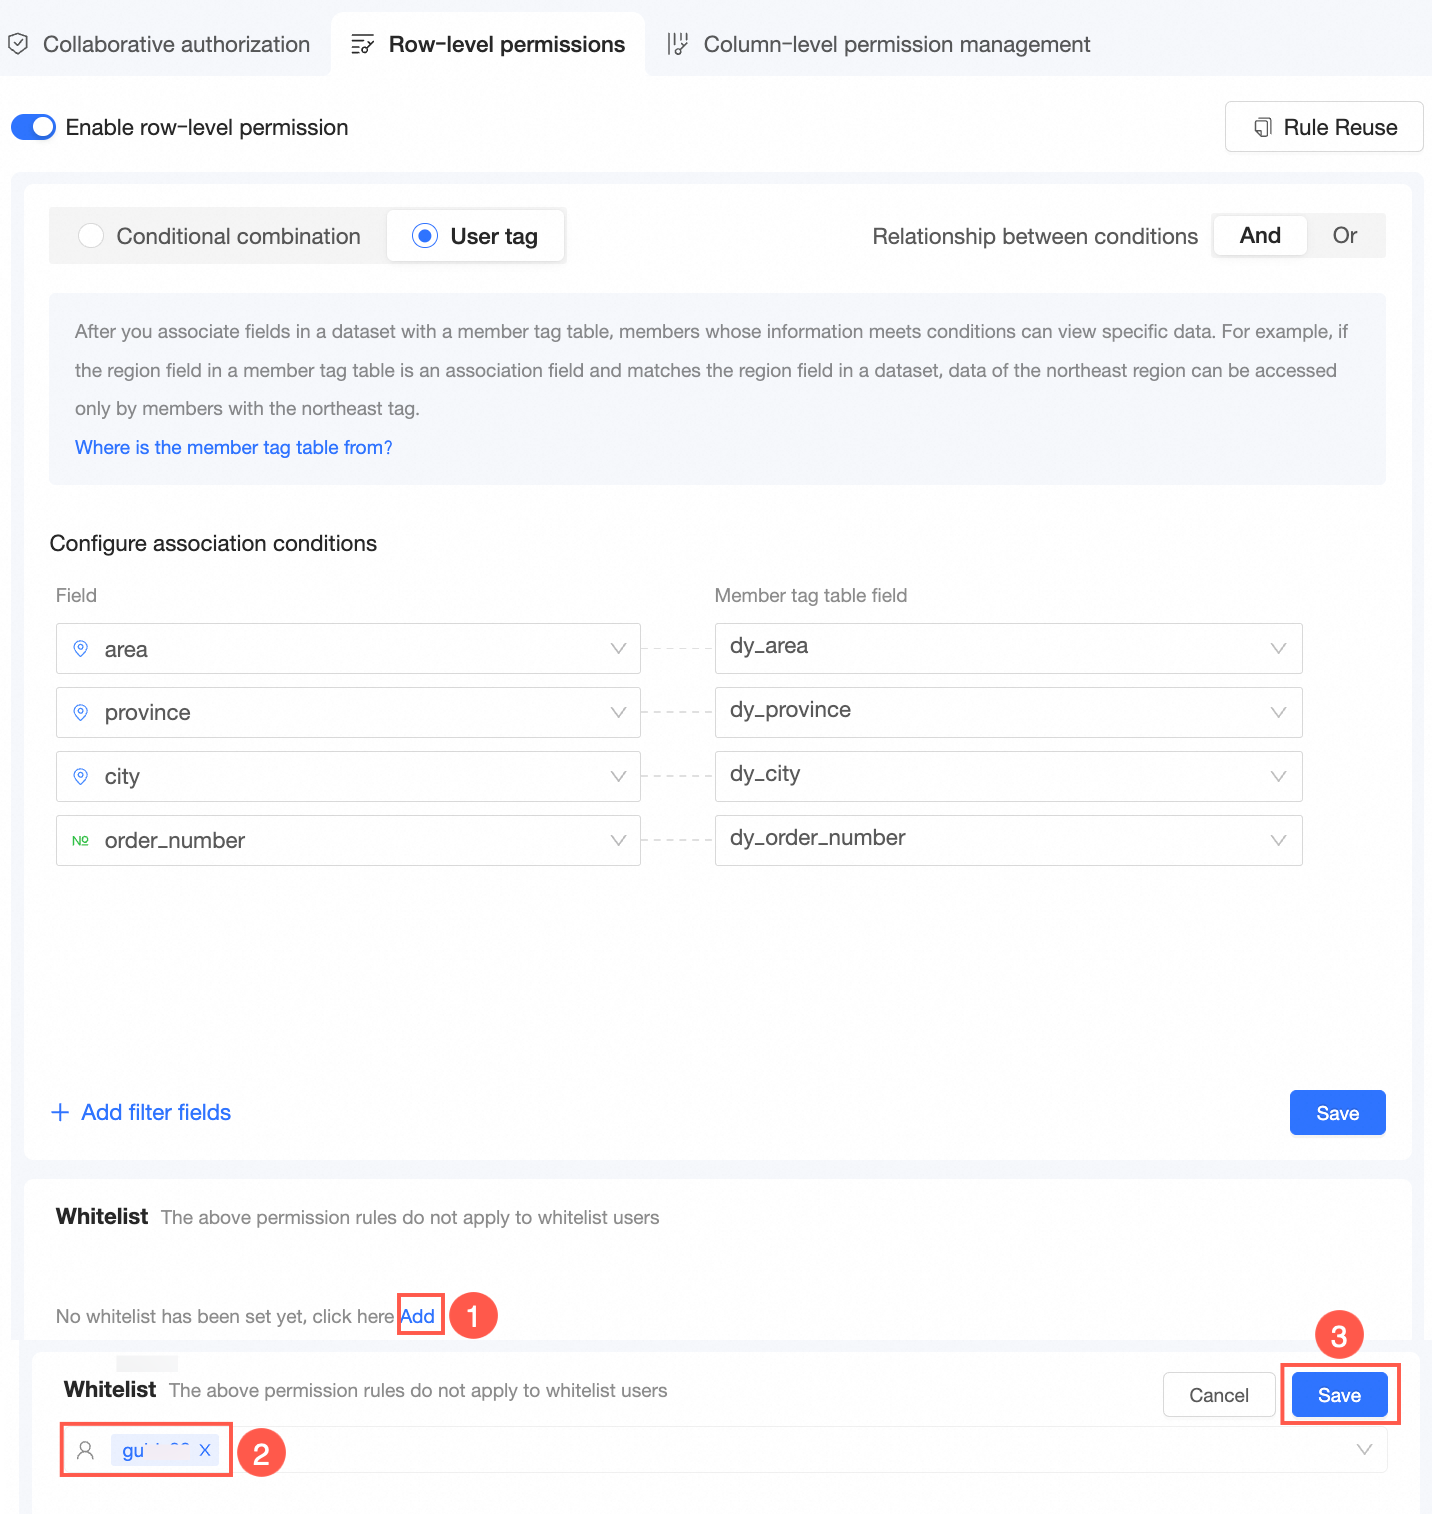
Add users to the whitelist.
If you want to exempt specific users from the preceding rules, you can add them to the whitelist.
Verify the results on a dashboard.
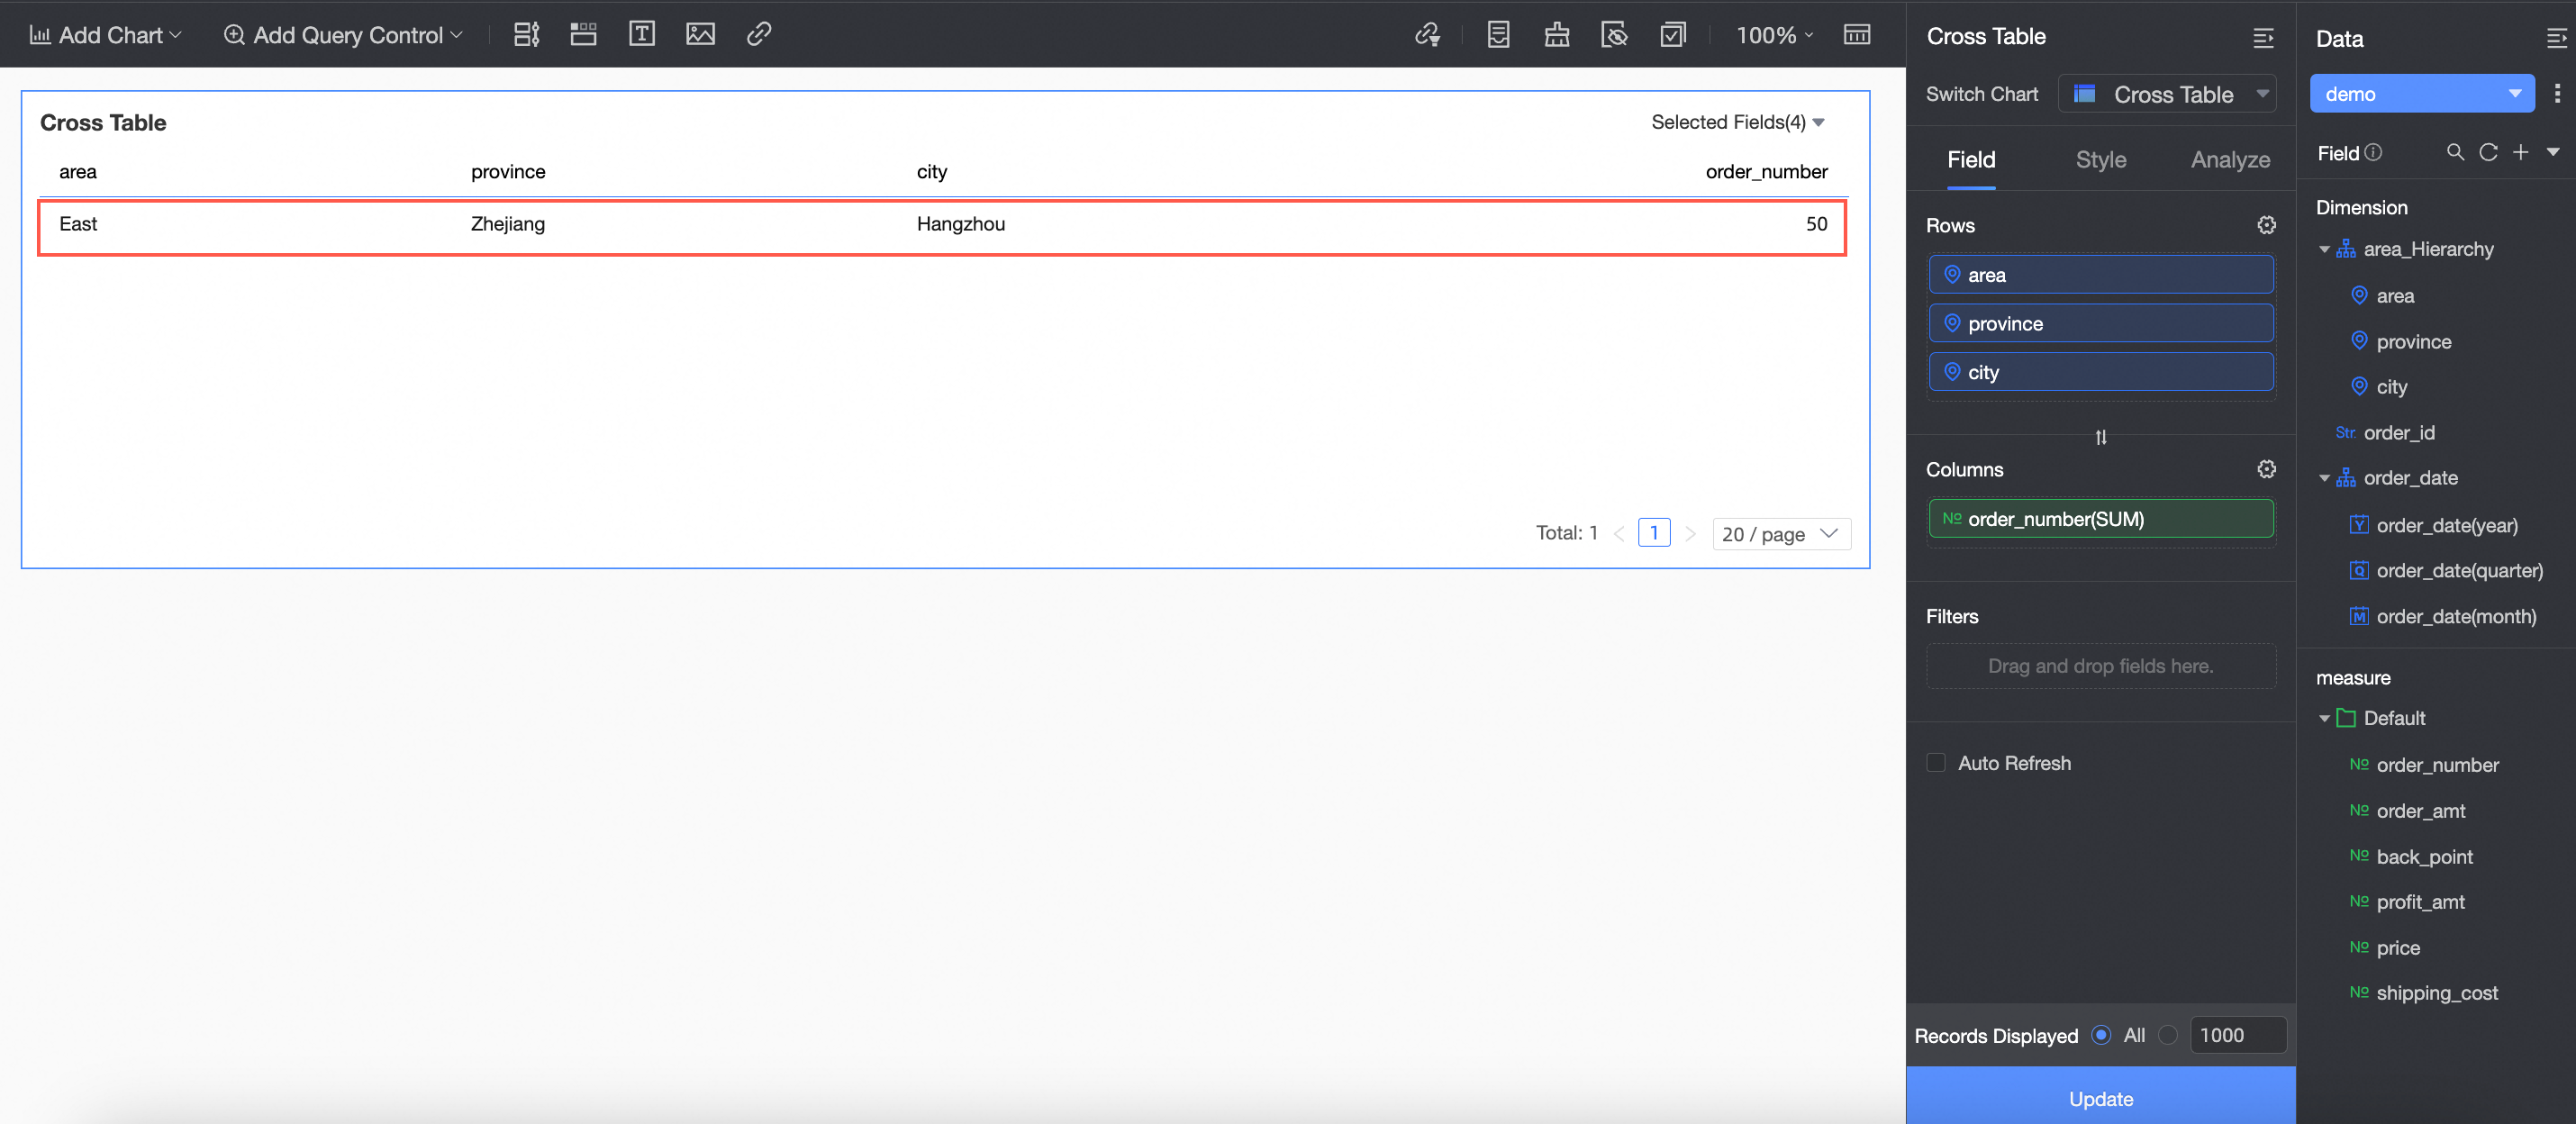
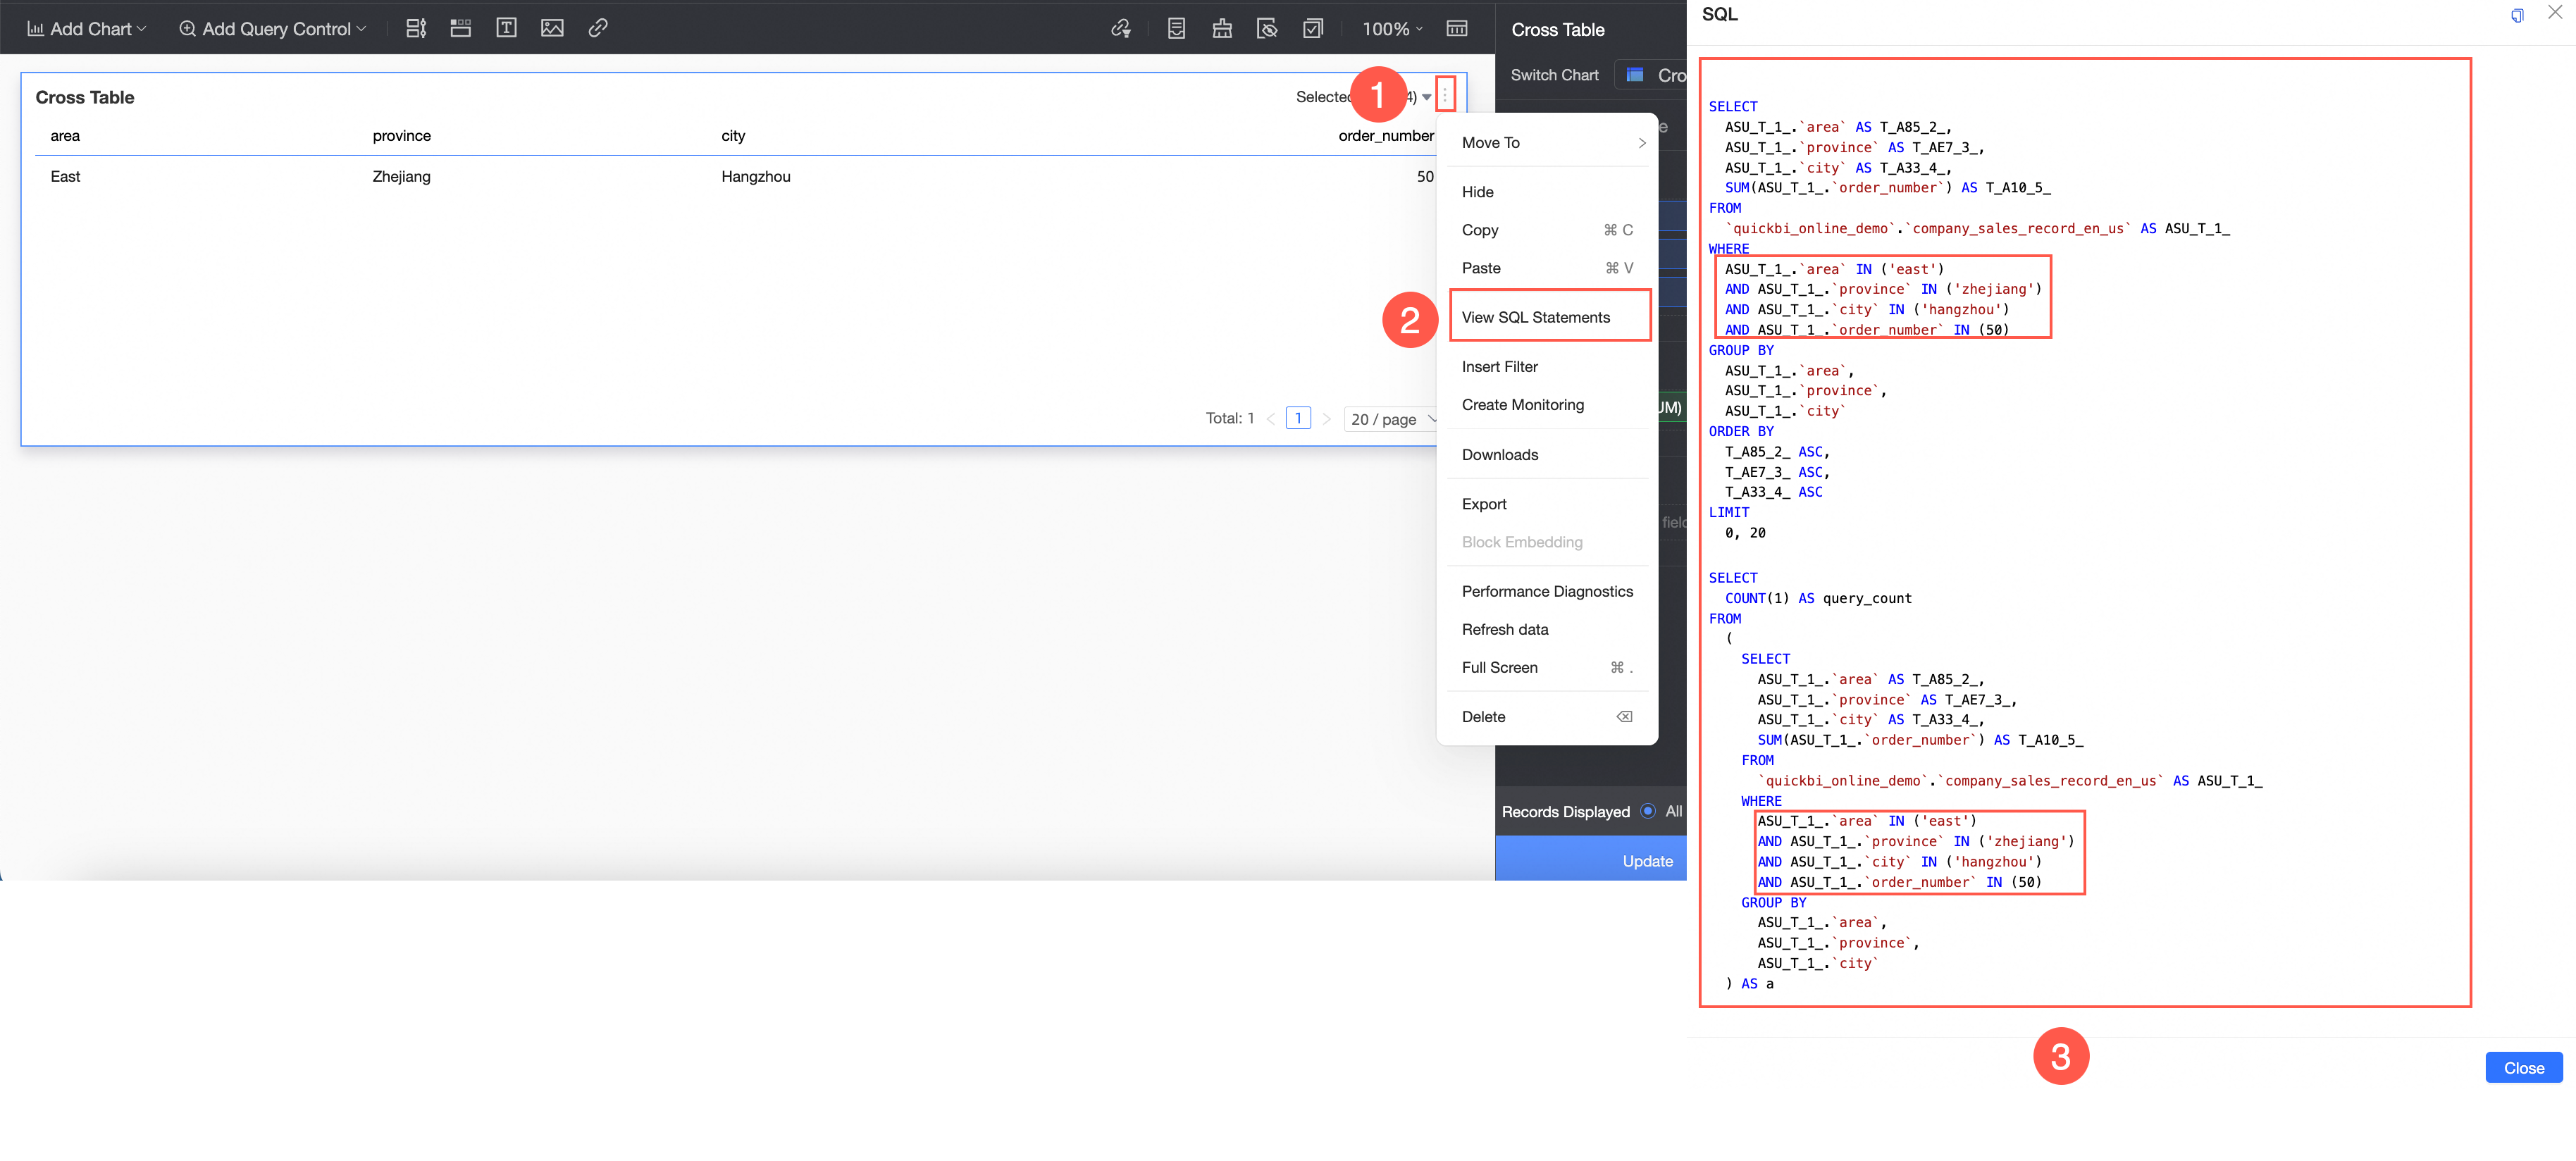
On the dashboard editing page, create a chart and verify the authorization results.
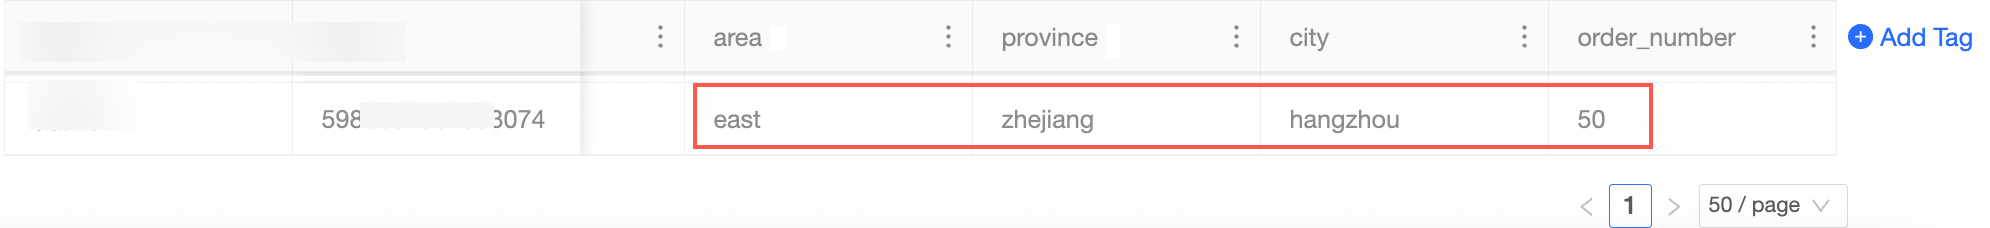
For example, if you create a cross table, you can see the data for Hangzhou where the order count is 50.
View the data retrieval logic in the SQL query.


Scenario 2: Manually manage tags
Log on to the Quick BI console.
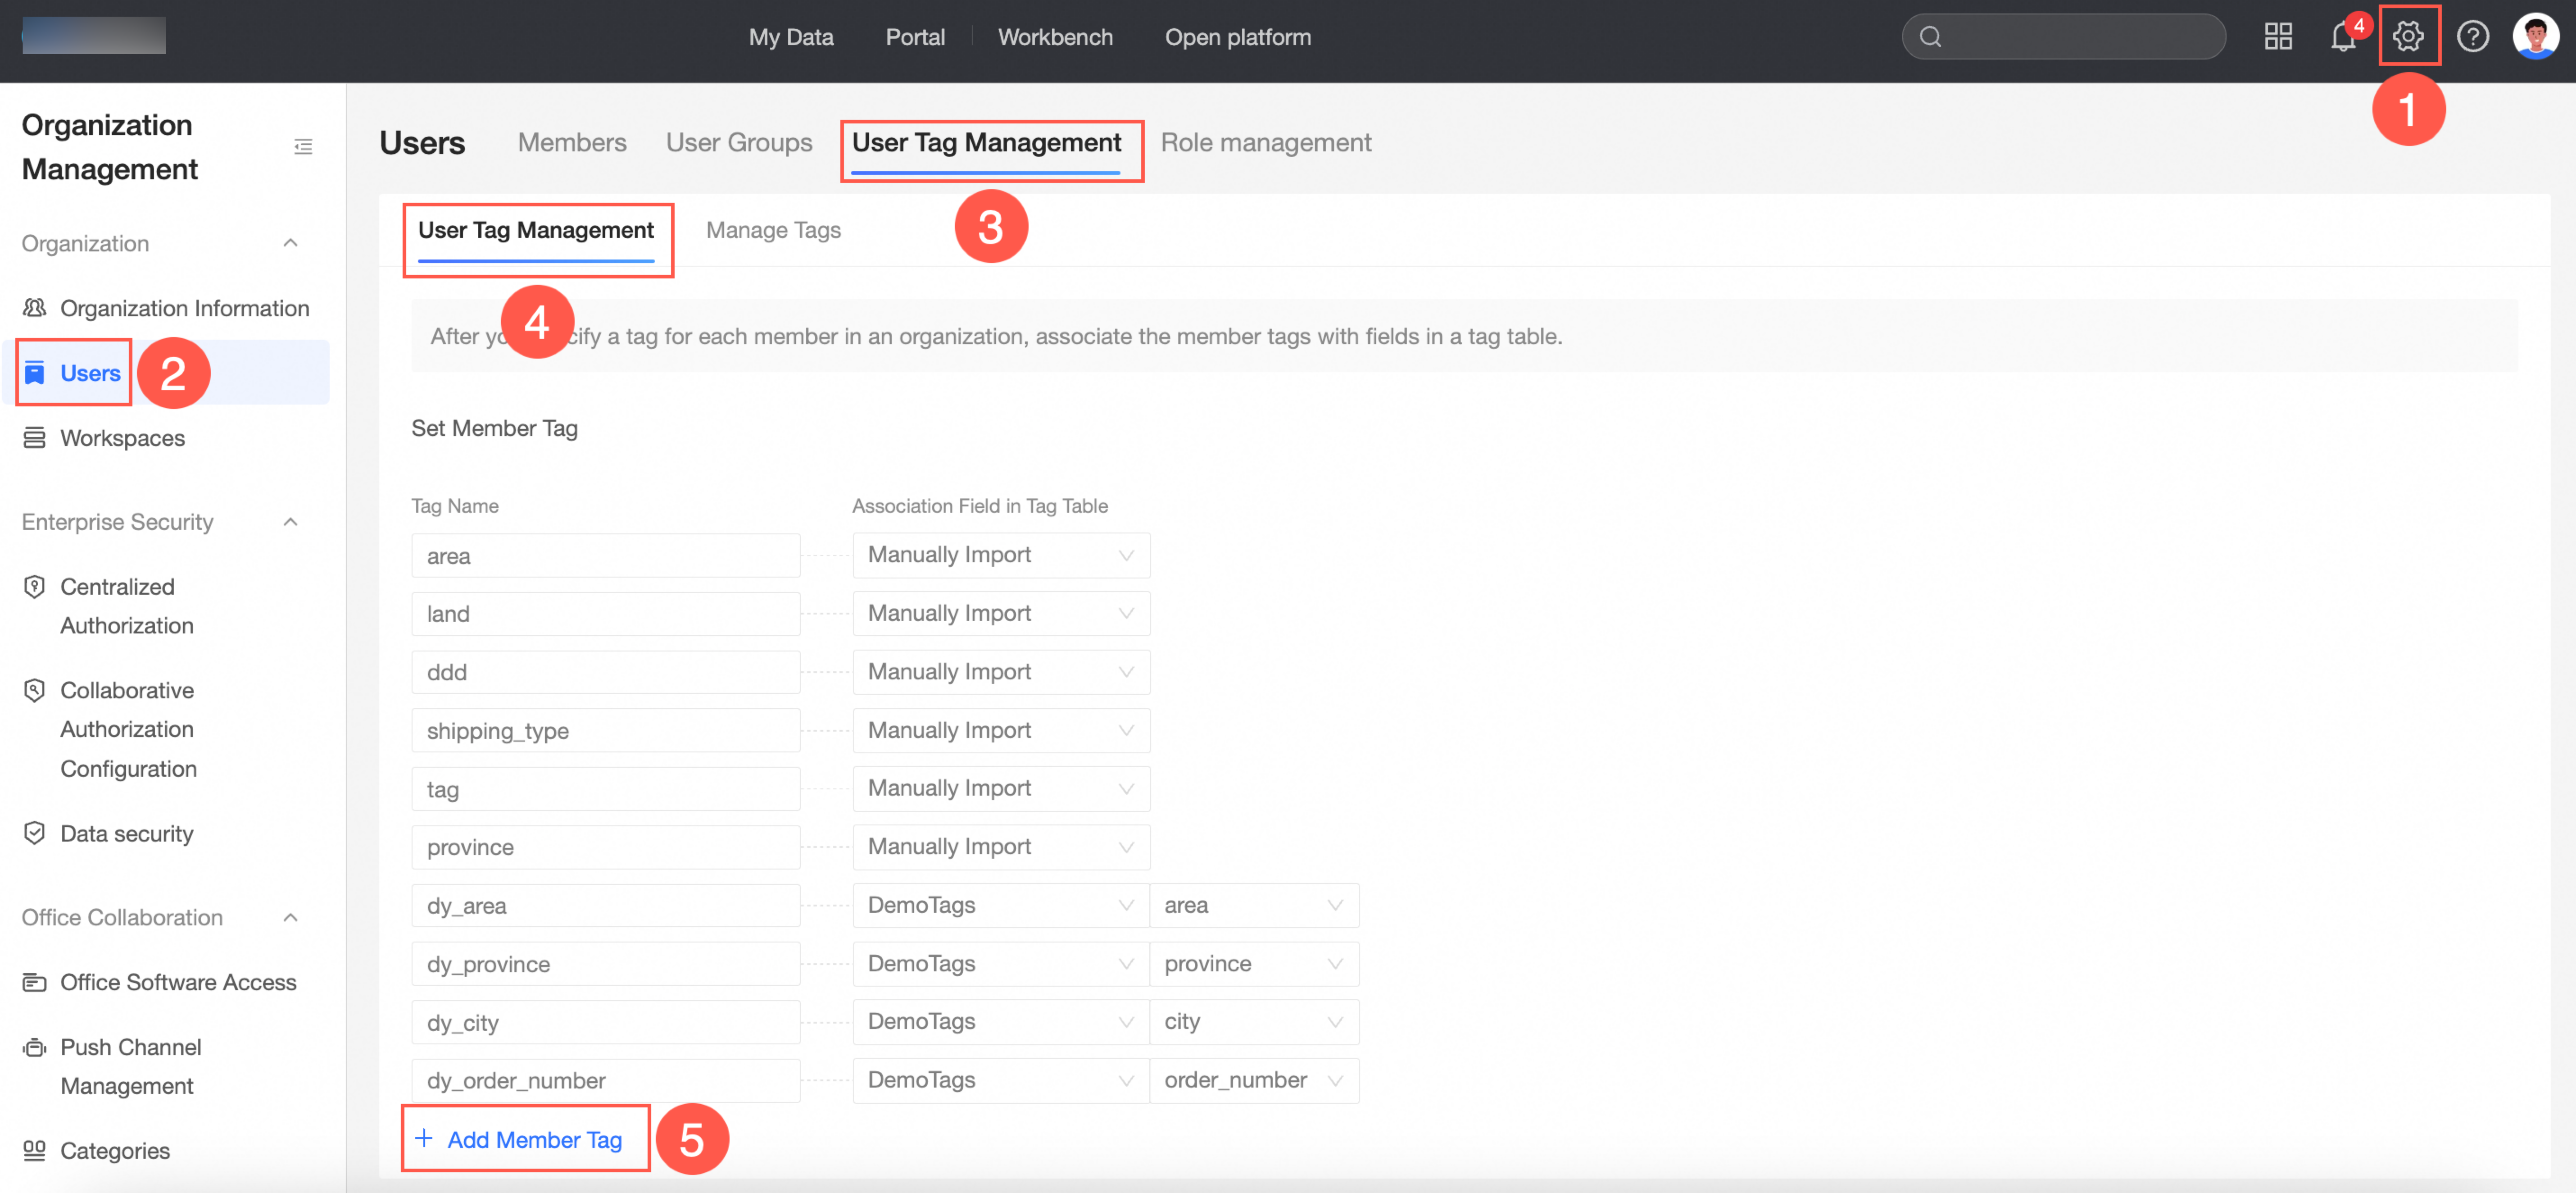
Configure user tags.
The user tags that you add are used to control the scope of data visibility when you configure row-level permissions.
Follow the steps in the figure to add a user tag.
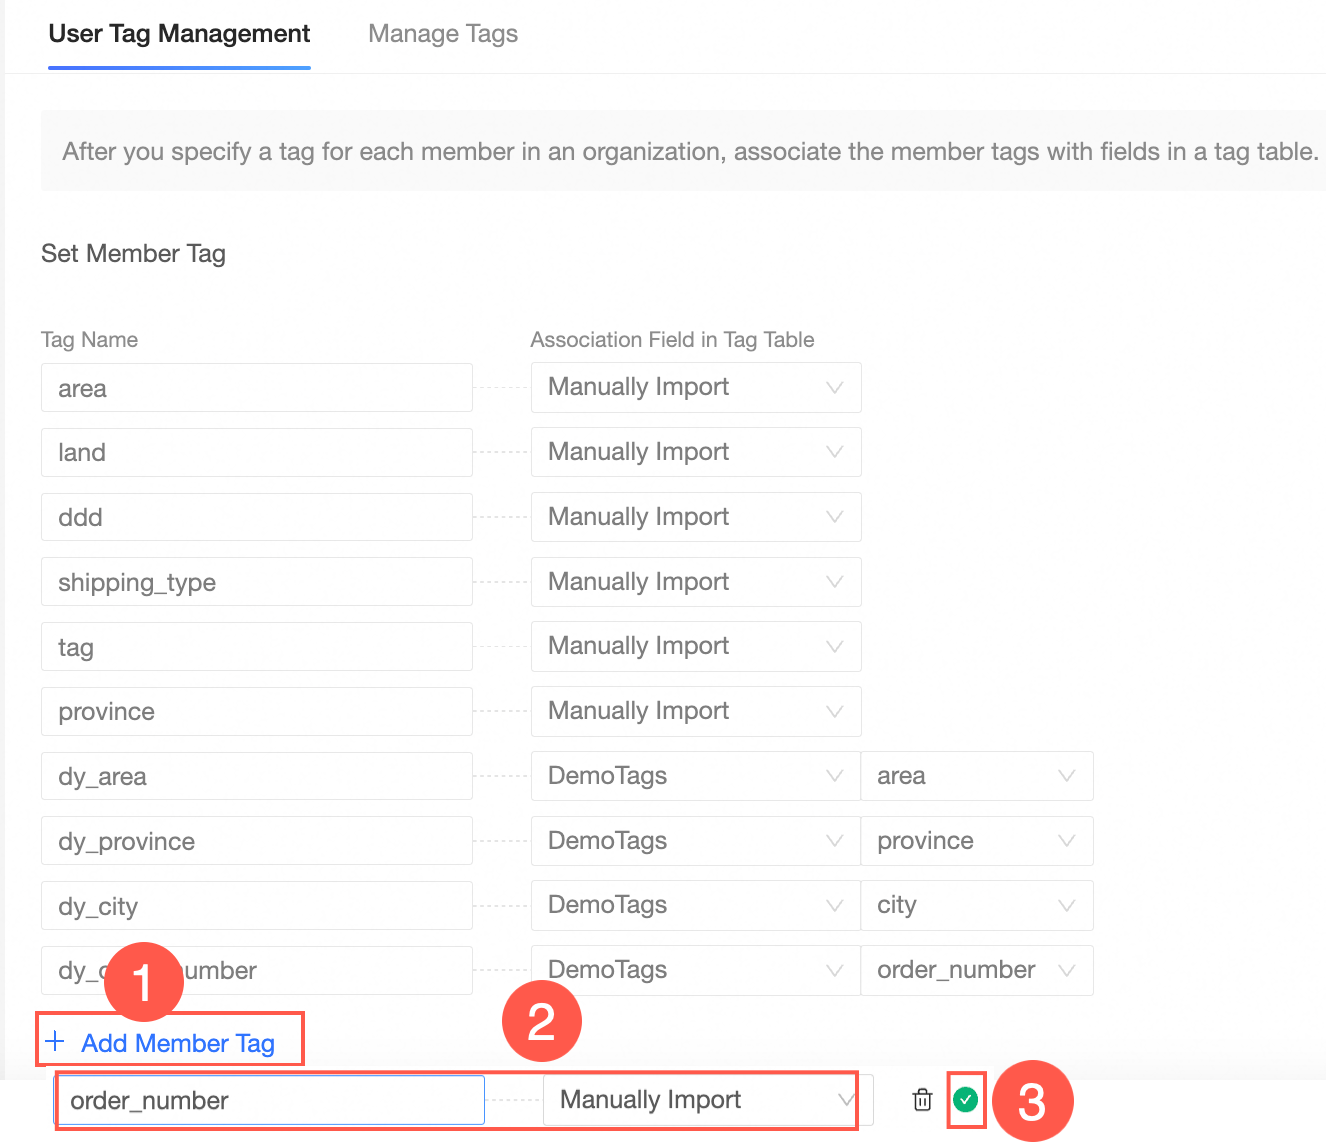
Enter a Tag Name and select an Associated Tag Table Field. Then, save the configuration.
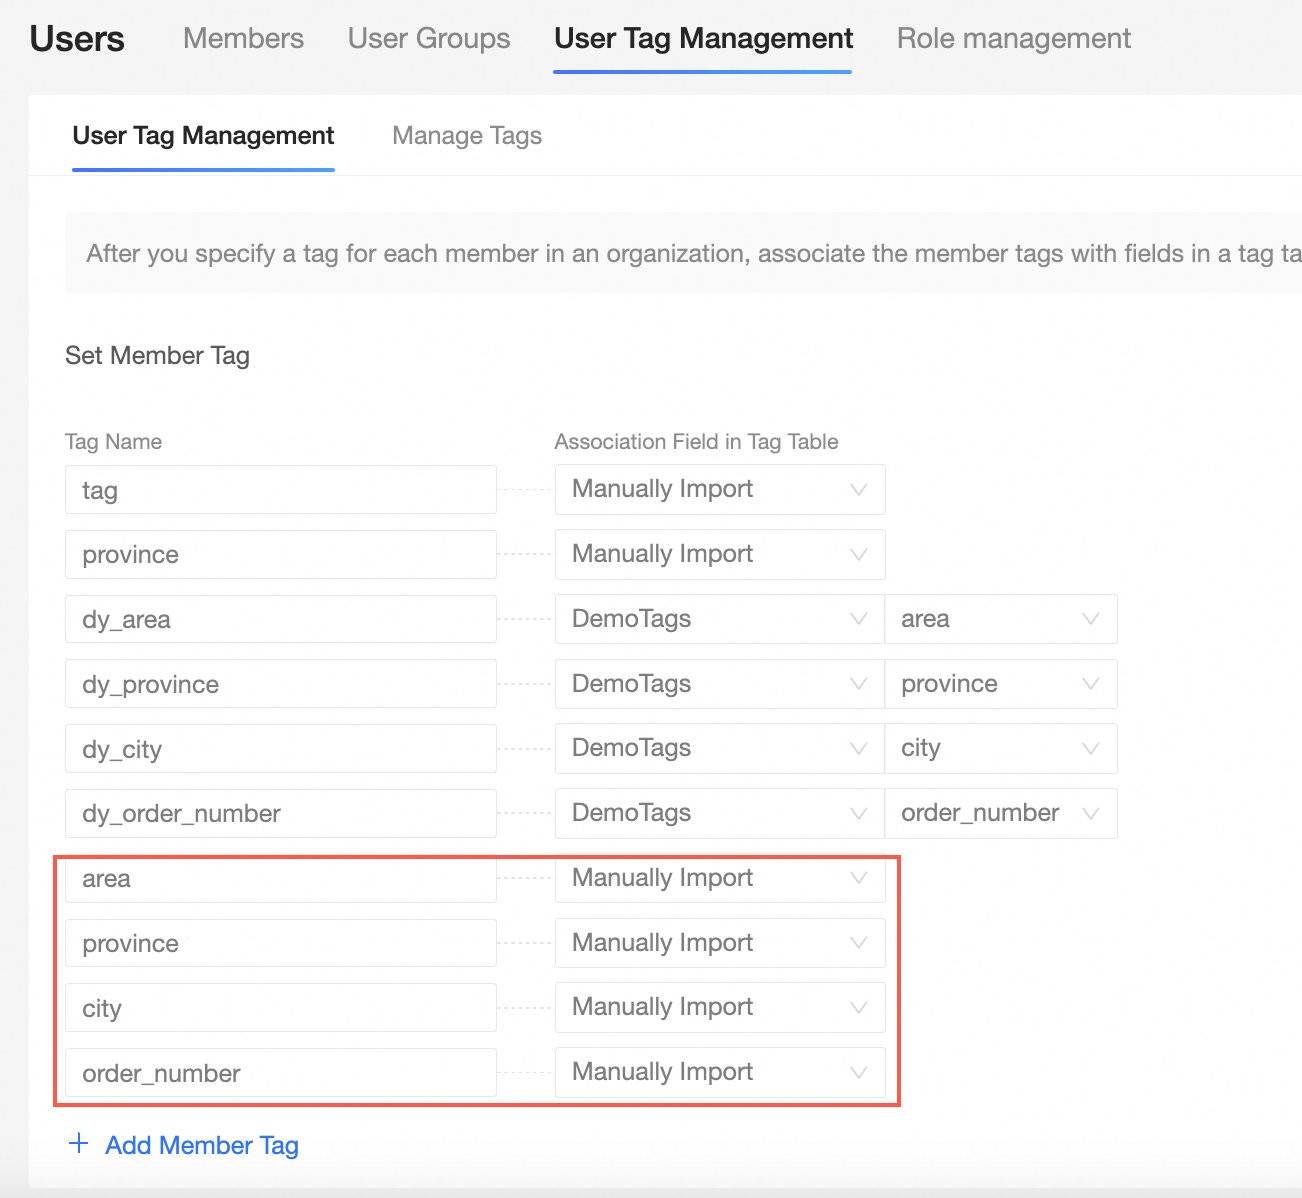
Create custom tag names, such as area, province, city, and order_number. For the Associated Tag Table Field, select manual entry for all tags.
Manually manage the user tag table.
In the manual tag management table, select one or more users and assign values to their tags.
On the Tag Management page, click Manual Management in the left-side navigation pane.
Search for a target user and assign values to the user tags.
The tag assignments in this example are shown in the following figure.
Use tag-based authorization.
After you grant permissions, these tag values apply to all relevant datasets, ensuring that users can view only data within their permitted scope.
On the Quick BI homepage, follow the steps in the figure to go to the row-level permissions settings page.
Turn on the Enable Row-level Permissions switch and select User Tag-based Authorization for the Authorization Method.
In the Configure Association Conditions section, click Add Controlled Field.
Select a controlled field and bind it to a user tag table field.
The controlled fields and user tag table fields selected in this example are shown in the following figure.
Click Save.
Add users to the whitelist.
If you want to exempt specific users from the preceding rules, you can add them to the whitelist.
Verify the results on a dashboard.
On the dashboard editing page, create a chart and verify the authorization results.
For example, if you create a cross table, you can see the data for Hangzhou where the order count is 50.
View the data retrieval logic in the SQL query.
Next steps
After you configure the dataset, you can analyze its data. For more information, see Create a dashboard and Create a chart.