Configure the network for a Dify instance
Enable private and public endpoints for a Dify instance to make it accessible over your internal network or the internet, then restrict access using an IP whitelist.
Prerequisites
Before you begin, ensure that you have:
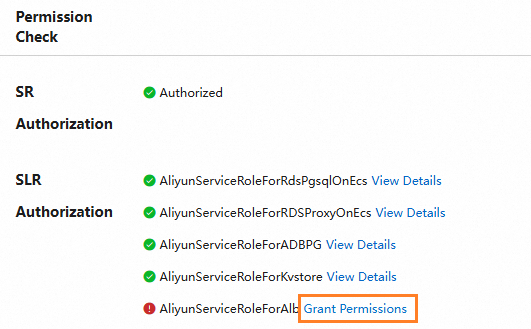
The AliyunServiceRoleForAlb service-linked role on the Alibaba Cloud account you use to log on to Data Management (DMS). To create this role, go to the One-click Deployment page, turn on the Private and Public Network Access Address switch, and click Grant Permissions next to AliyunServiceRoleForAlb in the Permission Check section.
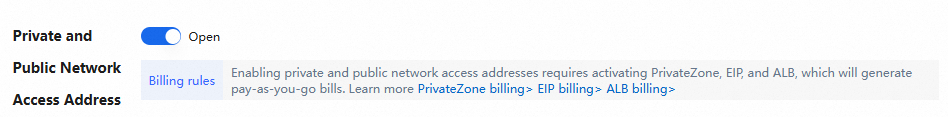
The following services activated: PrivateZone, elastic IP address (EIP), and Application Load Balancer (ALB). When you enable the endpoints, the system automatically purchases and configures instances of these services, which incurs pay-as-you-go fees. For billing details, see PrivateZone billing rules, EIP billing rules, and ALB billing rules.
Limitations
Private and public endpoints must be enabled at the same time. You cannot enable one without the other.
Once enabled, endpoints cannot be manually disabled. They are released automatically when you release the Dify instance resources.
The vSwitch you select for the standby zone must be in a different zone from the Dify instance.
Enable endpoints
During one-click deployment
During a one-click deployment, turn on the Private and Public Network Access Address switch, then complete the deployment.
For an existing instance
Prerequisite: A Dify instance is already deployed. For deployment instructions, see One-click deployment or Manual deployment.
Log on to the .
Go to the Workspace Management page using one of the following methods:
Method 1
Move the pointer over the
 icon in the upper-left corner, then choose .
Note
In normal mode, choose in the top navigation bar.
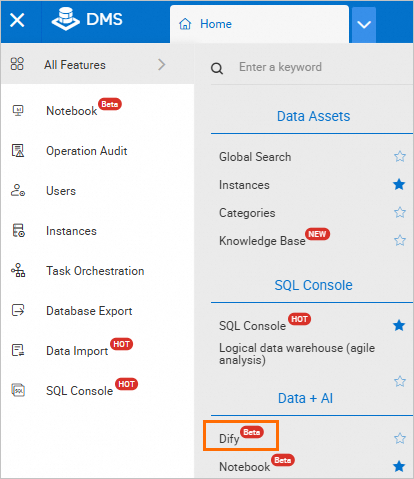
Method 2
In the left-side navigation pane, click the
 icon, then click Workspace.
Note
In normal mode, choose in the top navigation bar.
Click the target workspace name.
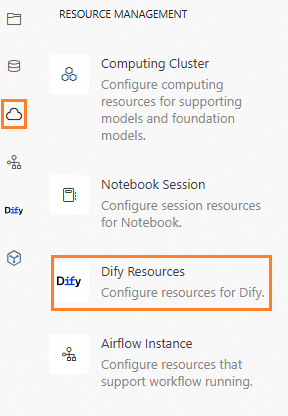
In the navigation pane on the left, choose
 > Dify Resources.
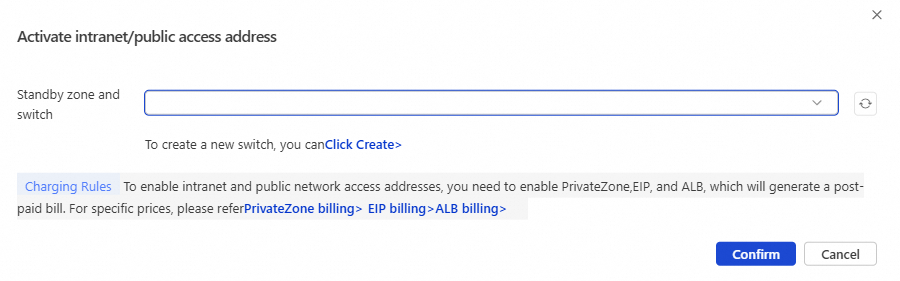
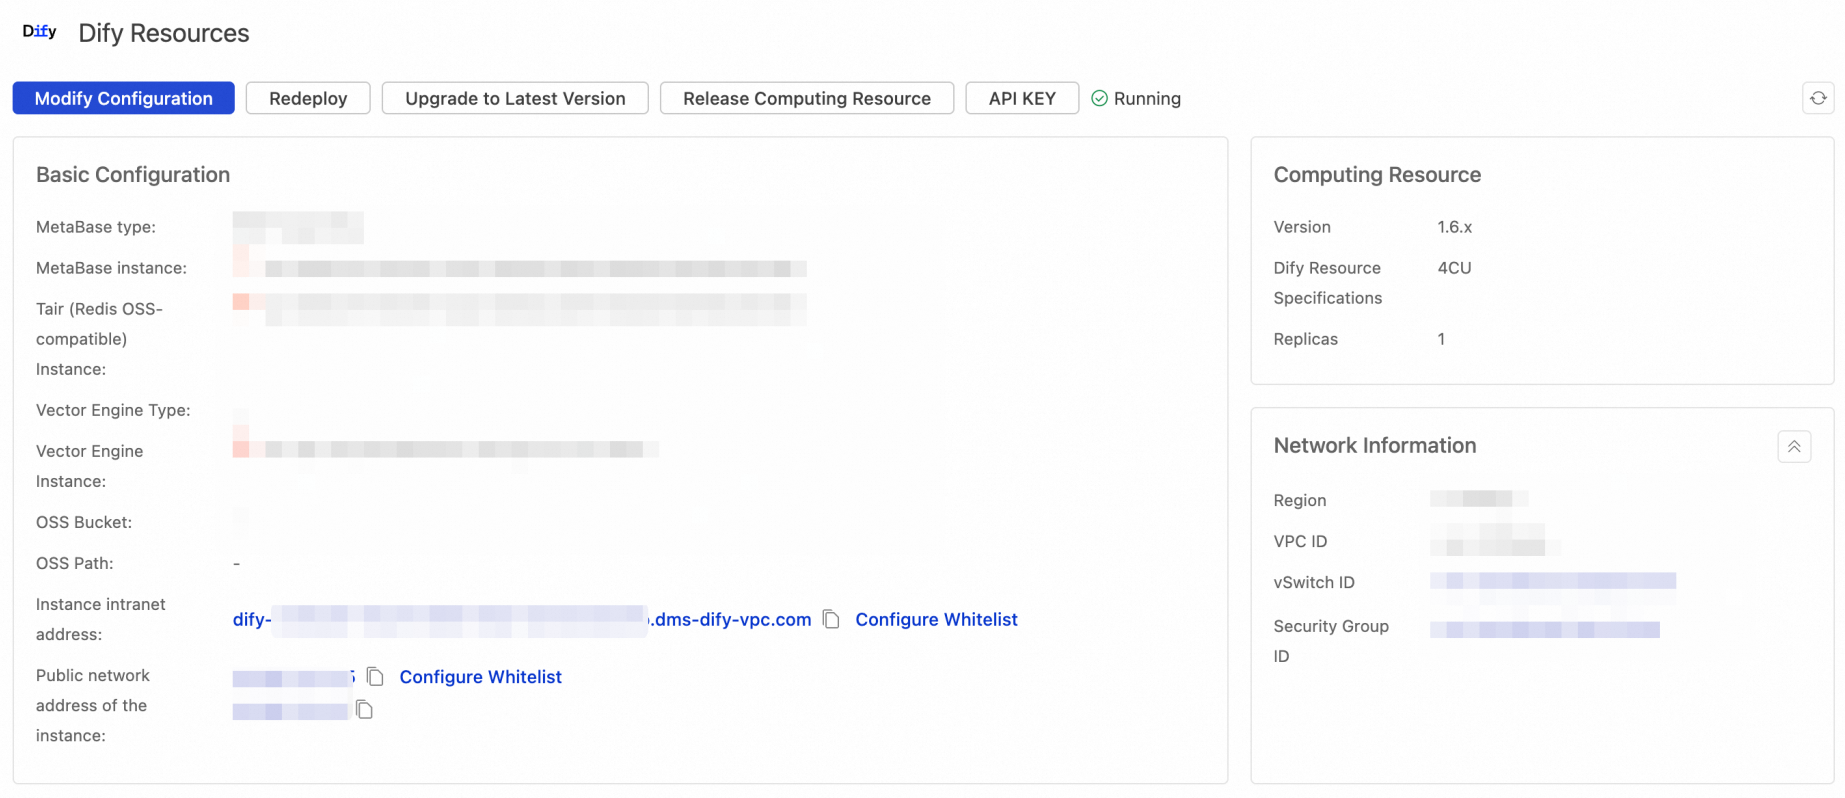
In the Basic Configuration section, click Activate the intranet/public address of the instance next to Instance intranet address.
In the dialog box, select a Standby zone and switch, then click Confirm.
Wait for the endpoints to be enabled.
After the endpoints are enabled, the private and public endpoints appear in the Basic Configuration section.
To access the Dify instance, configure an IP whitelist as described in the next section.
 > Dify Resources
Configure an IP whitelist
After endpoints are enabled, configure an IP whitelist to control which IP addresses can reach the Dify instance.
Entry format
When adding multiple entries in bulk, use the following format:
<IP address or CIDR block>|<description>
Example: 192.168.1.0/24|Office network
Enter one entry per line. Press Enter to start a new line.
Add whitelist entries
In the Basic Configuration section, click Configure Whitelist next to Instance intranet address or Public network address of the instance.
On the page that appears, add entries using one of the following methods:
Add a single entry: Click Add Entry. In the dialog box, enter an IP Address/CIDR Block and a Remarks, and then click Add.
Bulk add entries: Click Add ACL Entries and enter the entries in the following format:
Enter one entry per line. Press the Enter key to start a new line.
Separate the IP address or CIDR block from its description with a vertical bar (|). For example, 192.168.1.0/24|description.
The Dify instance is now accessible from the IP addresses or CIDR blocks you added.